
最新发布第350页

CVE-2023-5003: Active Directory Integration WP Plugin < 4.1.10 - Log Disclosure
漏洞标题 CVE-2023-5003: Active Directory Integration WP Plugin < 4.1.10 - Log Disclosure 漏洞描述 The Active Directory Integration / LDAP Integration WordPress plugin before 4.1...
 2023年11月3日 04:37
CVE-2024-35694: WordPress WPMobile.App >= 11.42 – Cross-Site Scripting
漏洞标题 CVE-2024-35694: Wordpress WPMobile.App >= 11.42 - Cross-Site Scripting 漏洞描述 WPMobile.App versions up to 11.41 contain a reflected cross-site scripting (XSS) caused ...
2024年9月21日 20:20CVE-2022-21587: Oracle E-Business Suite 12.2.3 -12.2.11 – Remote Code Execution
漏洞标题 CVE-2022-21587: Oracle E-Business Suite 12.2.3 -12.2.11 - Remote Code Execution 漏洞描述 Oracle E-Business Suite 12.2.3 through 12.2.11 is susceptible to remote code execu...
2022年10月26日 16:20CVE-2024-51567: CyberPanel v2.3.6 Pre-Auth Remote Code Execution
漏洞标题 CVE-2024-51567: CyberPanel v2.3.6 Pre-Auth Remote Code Execution 漏洞描述 upgrademysqlstatus in databases/views.py in CyberPanel (aka Cyber Panel) before 5b08cd6 allows re...
2024年4月26日 23:48CVE-2021-42670: Engineers Online Portal 1.0 容易受到三种类型的SQL注入攻击
漏洞标题 CVE-2021-42670: Engineers Online Portal 1.0 容易受到三种类型的SQL注入攻击 漏洞描述 Engineers Online Portal 1.0 应用程序中的 id 参数my_classmates.php似乎容易受到三种类型的 ...
2021年2月27日 18:09CVE-2023-28662: WordPress Gift Cards <= 4.3.1 - SQL Injection
漏洞标题 CVE-2023-28662: Wordpress Gift Cards <= 4.3.1 - SQL Injection 漏洞描述 The Gift Cards (Gift Vouchers and Packages) WordPress Plugin, version <= 4.3.1, is affected by...
2023年10月16日 12:34CVE-2023-6977: Mlflow <2.8.0 - Local File Inclusion
漏洞标题 CVE-2023-6977: Mlflow <2.8.0 - Local File Inclusion 漏洞描述 Mlflow before 2.8.0 is susceptible to local file inclusion due to path traversal in GitHub repository mlflo...
2023年9月26日 00:47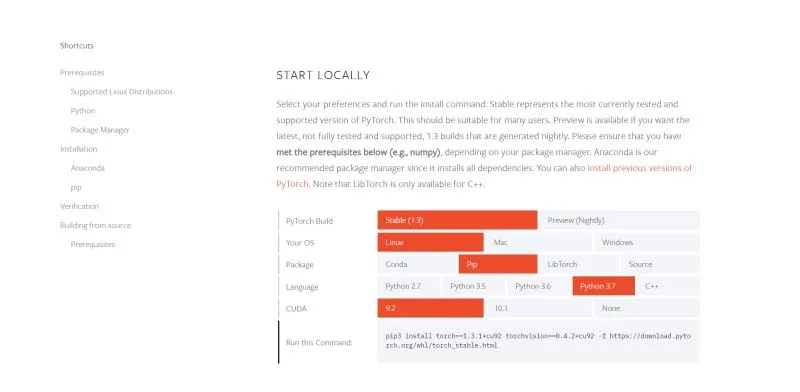
linux或windows环境下pytorch的安装与检查验证(解决runtimeerror问题)_Linux
这篇文章主要介绍了linux或windows环境下pytorch的安装与检查验证(解决runtimeerror问题),需要的朋友可以参考下 1、pytorch官网下载对应安装文件 http://pytorch.org/ 在getstarted处选择对应版...
2026年5月22日 11:45CVE-2020-16952: Microsoft SharePoint – Remote Code Execution
漏洞标题 CVE-2020-16952: Microsoft SharePoint - Remote Code Execution 漏洞描述 Microsoft SharePoint is vulnerable to a remote code execution when the software fails to check the so...
2020年8月29日 09:02
bugbounty技巧聚合20220218
漏洞报告 子域名接管 750$ http://hackerone.com/reports/1474784 挖洞技巧 SSRF读取元数据RCE http://cloud.tencent.com/developer/article/1423222 Zabbix - 不安全会话存储的案例研究 http:/...
2022年3月10日 23:32CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection
漏洞标题 CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection 漏洞描述 The HTML5 Video Player WordPress plugin before 2.5.27 does not sanitize and escape a param...
2024年2月17日 14:01CVE-2023-7164: WordPress BackWPup < 4.0.4 - Backup File Disclosure
漏洞标题 CVE-2023-7164: WordPress BackWPup < 4.0.4 - Backup File Disclosure 漏洞描述 BackWPup WordPress plugin < 4.0.4 contains a directory listing vulnerability caused by la...
2023年1月23日 23:03CVE-2025-53770: Microsoft SharePoint Server – Remote Code Execution (ToolShell)
漏洞标题 CVE-2025-53770: Microsoft SharePoint Server - Remote Code Execution (ToolShell) 漏洞描述 Deserialization of untrusted data in on-premises Microsoft SharePoint Server allow...
2025年2月25日 19:52CVE-2019-12987: Citrix SD-WAN Center – Remote Command Injection
漏洞标题 CVE-2019-12987: Citrix SD-WAN Center - Remote Command Injection 漏洞描述 Citrix SD-WAN Center is susceptible to remote command injection via the apply action in StorageMgm...
2019年9月7日 15:54CVE-2017-5868: OpenVPN Access Server 2.1.4 – CRLF Injection
漏洞标题 CVE-2017-5868: OpenVPN Access Server 2.1.4 - CRLF Injection 漏洞描述 CRLF injection vulnerability in the web interface in OpenVPN Access Server 2.1.4 allows remote attacke...
2017年3月21日 12:15CVE-2024-4358: Progress Telerik Report Server – Authentication Bypass
漏洞标题 CVE-2024-4358: Progress Telerik Report Server - Authentication Bypass 漏洞描述 In Progress Telerik Report Server, version 2024 Q1 (10.0.24.305) or earlier, on IIS, an unau...
2024年11月27日 05:48
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

