
最新发布第353页

CVE-2024-57049: TP-Link Archer C20 – Authentication Bypass
漏洞标题 CVE-2024-57049: TP-Link Archer C20 - Authentication Bypass 漏洞描述 A vulnerability in the TP-Link Archer C20 router with firmware version V6.6_230412 and earlier permits ...
 2024年4月24日 16:44
CVE-2023-1177: MLflow get-artifact 任意文件读取漏洞
漏洞标题 CVE-2023-1177: MLflow get-artifact 任意文件读取漏洞 漏洞描述 使用 MLflow 模型注册表托管 MLflow 开源项目的用户 mlflow server或者 mlflow ui使用早于 MLflow 2.2.1 的 MLflow 版...
2023年6月4日 18:24
docker 内存监控与压测方式_docker
这篇文章主要介绍了docker 内存监控与压测方式,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 一直运行的docker容器显示内存已经耗尽,并且容器内存耗尽也没出现重启情况,...
2022年8月8日 21:03CVE-2016-3510: Oracle WebLogic Server Java Object Deserialization – Remote Code Execution
漏洞标题 CVE-2016-3510: Oracle WebLogic Server Java Object Deserialization - Remote Code Execution 漏洞描述 Unspecified vulnerability in the Oracle WebLogic Server component in Ora...
2016年1月11日 17:40CVE-2012-6499: WordPress Plugin Age Verification v0.4 – Open Redirect
漏洞标题 CVE-2012-6499: WordPress Plugin Age Verification v0.4 - Open Redirect 漏洞描述 Open redirect vulnerability in age-verification.php in the Age Verification plugin 0.4 and e...
2012年11月26日 05:38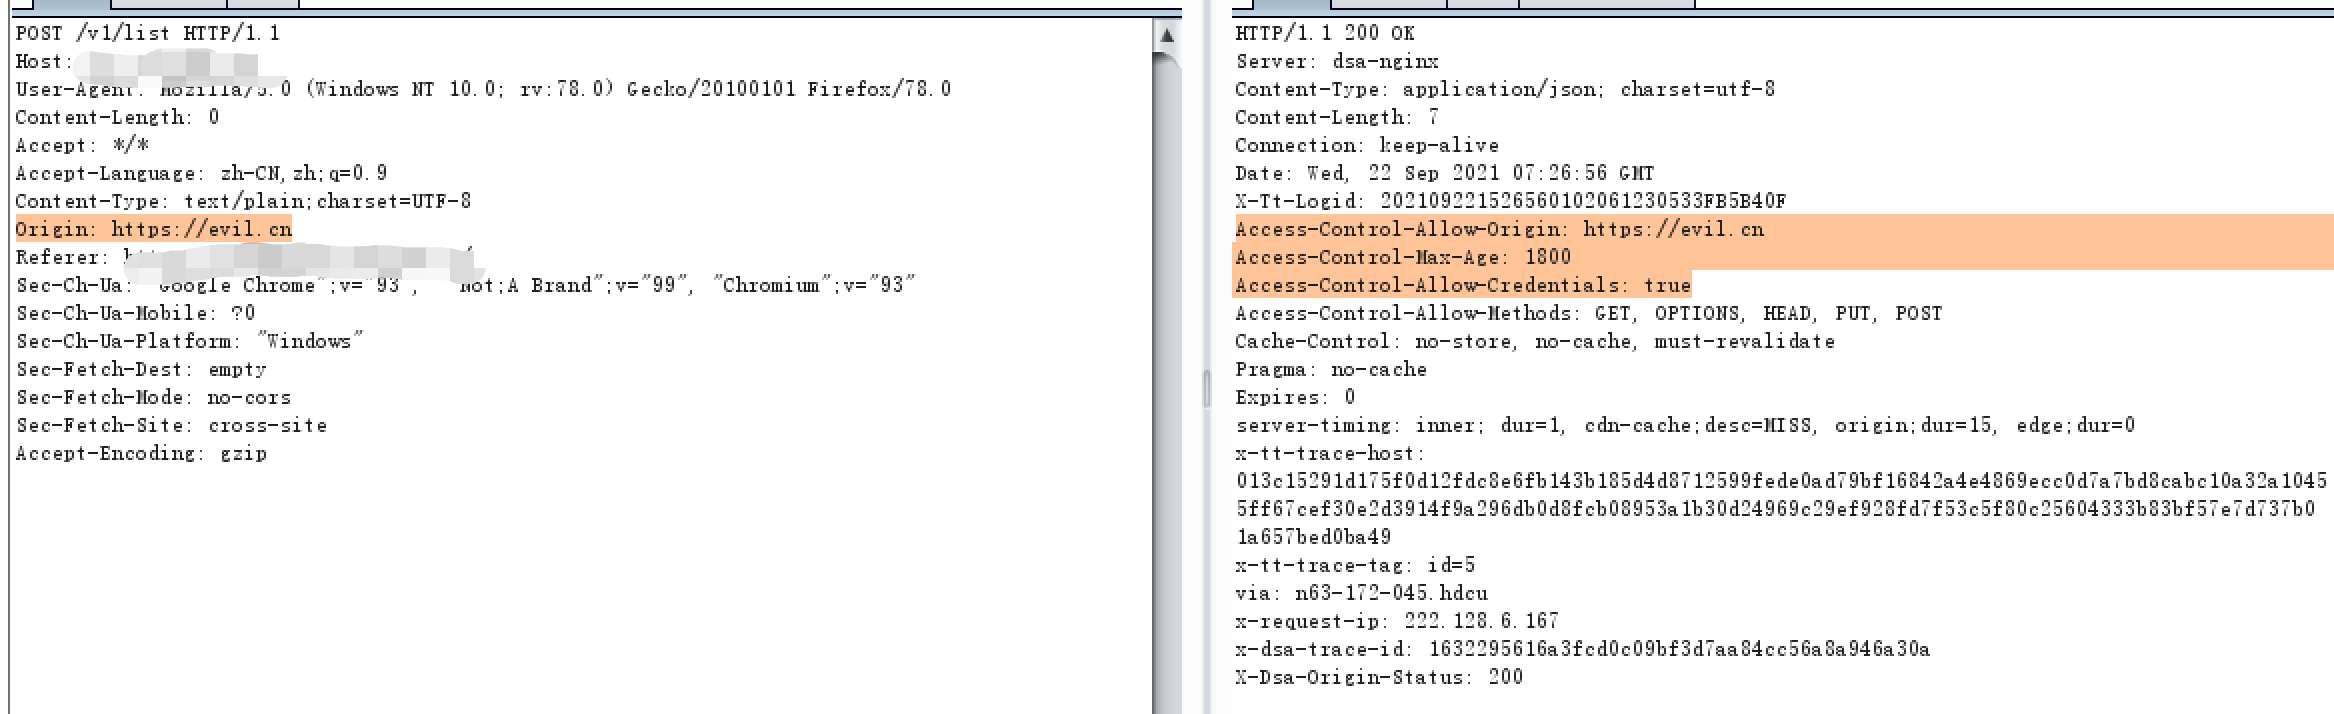
web漏洞挖掘指南-前端跨域漏洞
web漏洞挖掘指南 前端跨域漏洞 一、何为跨域 1.设想一种场景,一个恶意网站上嵌入了一个iframe标签去加载银行的登陆页面,高度和宽度的设置和真实的银行官网一样,当用户访问恶意网站并登录时,...
2022年3月10日 23:37CVE-2021-39316: WordPress DZS Zoomsounds <=6.50 - Local File Inclusion
漏洞标题 CVE-2021-39316: WordPress DZS Zoomsounds <=6.50 - Local File Inclusion 漏洞描述 WordPress Zoomsounds plugin 6.45 and earlier allows arbitrary files, including sensitive...
2021年5月19日 18:51CVE-2010-2918: Joomla! Component Visites 1.1 – MosConfig_absolute_path Remote File Inclusion
漏洞标题 CVE-2010-2918: Joomla! Component Visites 1.1 - MosConfig_absolute_path Remote File Inclusion 漏洞描述 A PHP remote file inclusion vulnerability in core/include/myMailer.cl...
2010年7月19日 18:06CVE-2022-42118: Liferay Portal – Cross-site Scripting
漏洞标题 CVE-2022-42118: Liferay Portal - Cross-site Scripting 漏洞描述 A Cross-site scripting (XSS) vulnerability in the Portal Search module in Liferay Portal 7.1.0 through 7.4.2...
2022年8月16日 02:28CVE-2024-29868: Apache StreamPipes <= 0.93.0 - Use of Cryptographically Weak PRNG in Recovery Token Generation
漏洞标题 CVE-2024-29868: Apache StreamPipes <= 0.93.0 - Use of Cryptographically Weak PRNG in Recovery Token Generation 漏洞描述 Apache StreamPipes from version 0.69.0 through 0...
2024年5月12日 17:19CVE-2022-25488: Atom CMS v2.0 – SQL Injection
漏洞标题 CVE-2022-25488: Atom CMS v2.0 - SQL Injection 漏洞描述 Atom CMS v2.0 was discovered to contain a SQL injection vulnerability via the id parameter in /admin/ajax/avatar.php...
2022年1月31日 15:59CVE-2022-0968: Microweber <1.2.12 - Integer Overflow
漏洞标题 CVE-2022-0968: Microweber <1.2.12 - Integer Overflow 漏洞描述 Microweber before 1.2.12 is susceptible to integer overflow. The application allows large characters to in...
2022年9月9日 22:58CVE-2025-2473 PHPGurukul 访客管理系统 2.0 SQL注入漏洞
漏洞标题 CVE-2025-2473 PHPGurukul 访客管理系统 2.0 SQL注入漏洞 漏洞描述 CVE-2025-2473 PHPGurukul 访客管理系统 2.0 SQL注入漏洞 PoC代码 暂无
2025年9月26日 13:26CVE-2025-49001: Dataease JWT 认证绕过漏洞
漏洞标题 CVE-2025-49001: Dataease JWT 认证绕过漏洞 漏洞描述 CVE-2025-49001 是由于JWT校验机制错误导致攻击者可伪造JWT令牌绕过身份验证流程 fofa: body="/js/index-0.0.0-dataease.js...
2025年1月3日 09:16CVE-2023-35813: Sitecore – Remote Code Execution
漏洞标题 CVE-2023-35813: Sitecore - Remote Code Execution 漏洞描述 Multiple Sitecore products allow remote code execution. This affects Experience Manager, Experience Platform, and...
2023年8月19日 06:03CVE-2025-6205: DELMIA Apriso – Broken Access Control
漏洞标题 CVE-2025-6205: DELMIA Apriso - Broken Access Control 漏洞描述 DELMIA Apriso Release 2020 through Release 2025 contains a broken access control vulnerability caused by miss...
2025年1月13日 18:09
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

