
最新发布第363页

Citrix ADC and Citrix Gateway CVE-2023-3519未授权远程代码执行漏洞
漏洞标题 Citrix ADC and Citrix Gateway CVE-2023-3519未授权远程代码执行漏洞 漏洞描述 Citrix ADC and Citrix Gateway存在远程代码执行漏洞,此漏洞是由于缺乏有效的校验导致的。 PoC代码 暂...
 2023年3月7日 18:42
CVE-2024-45409: GitLab – SAML Authentication Bypass
漏洞标题 CVE-2024-45409: GitLab - SAML Authentication Bypass 漏洞描述 The Ruby SAML library is for implementing the client side of a SAML authorization. Ruby-SAML in <= 12.2 and...
2024年8月12日 04:58CVE-2025-48703: CWP (Control Web Panel) < 0.9.8.1205 - Remote Code Execution
漏洞标题 CVE-2025-48703: CWP (Control Web Panel) < 0.9.8.1205 - Remote Code Execution 漏洞描述 CWP (Control Web Panel) < 0.9.8.1205 contains a remote code execution caused by...
2025年7月27日 17:54CVE-2023-27640: PrestaShop tshirtecommerce – Directory Traversal
漏洞标题 CVE-2023-27640: PrestaShop tshirtecommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年2月1日 12:44CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668)
漏洞标题 CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
2018年7月31日 14:08CVE-2020-2096: Jenkins Gitlab Hook <=1.4.2 - Cross-Site Scripting
漏洞标题 CVE-2020-2096: Jenkins Gitlab Hook <=1.4.2 - Cross-Site Scripting 漏洞描述 Jenkins Gitlab Hook 1.4.2 and earlier does not escape project names in the build_now endpoint...
2020年1月4日 16:10CVE-2019-20504: Dell KACE Systems Management Appliance (K1000) 6.4.120756 – Remote Code Execution
漏洞标题 CVE-2019-20504: Dell KACE Systems Management Appliance (K1000) 6.4.120756 - Remote Code Execution 漏洞描述 service/krashrpt.php in Quest KACE K1000 Systems Management Appl...
2019年5月21日 04:04CVE-2023-28662: WordPress Gift Cards <= 4.3.1 - SQL Injection
漏洞标题 CVE-2023-28662: Wordpress Gift Cards <= 4.3.1 - SQL Injection 漏洞描述 The Gift Cards (Gift Vouchers and Packages) WordPress Plugin, version <= 4.3.1, is affected by...
2023年10月16日 12:34CVE-2013-6281: WordPress Spreadsheet – Cross-Site Scripting
漏洞标题 CVE-2013-6281: WordPress Spreadsheet - Cross-Site Scripting 漏洞描述 WordPress Spreadsheet plugin contains a reflected cross-site scripting vulnerability in /dhtmlxspreads...
2013年10月24日 14:51
红蓝对抗之企业对外根域名资产收集
#原创文章# 前言 上次听了火器的线上分享会议有提到火器的资产关联大概的思路,真的是收获了很多。再夸夸火器,在挖一些项目中的确能省掉很多资产收集的时间。本文主要参考上次会议中提交的一些...
2022年3月10日 23:37CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting
漏洞标题 CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting 漏洞描述 WordPress e-search 1.0 and before contains a reflected cross-site scripting vulnerability via...
2016年4月24日 23:23CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 – Unauthenticated Remote Command Execution
漏洞标题 CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 - Unauthenticated Remote Command Execution 漏洞描述 Zoho ManageEngine ADSelfService Plus version 6113 and prior ...
2021年3月31日 22:18CVE-2022-4306: WordPress Panda Pods Repeater Field <1.5.4 - Cross-Site Scripting
漏洞标题 CVE-2022-4306: WordPress Panda Pods Repeater Field <1.5.4 - Cross-Site Scripting 漏洞描述 WordPress Panda Pods Repeater Field before 1.5.4 contains a cross-site scripti...
2022年8月9日 10:24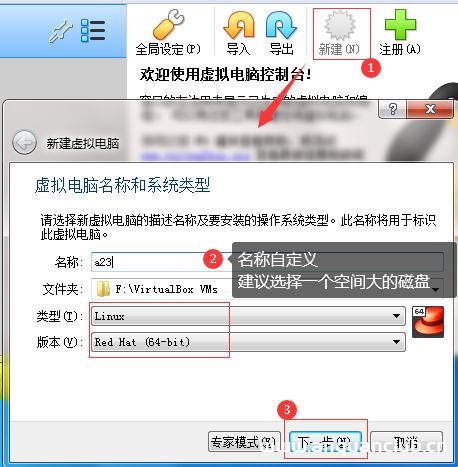
VirtualBox安装CentOS7虚拟机以及增强工具(图文)_VirtualBox
这篇文章主要介绍了VirtualBox安装CentOS7虚拟机以及增强工具,小编觉得挺不错的,现在分享给大家,也给大家做个参考。一起跟随小编过来看看吧 本机电脑系统为:win7 本文以图片为主,含有大量...
2024年3月30日 21:04Apache Tomcat SSI printenv CVE-2019-0221 跨站脚本漏洞
漏洞标题 Apache Tomcat SSI printenv CVE-2019-0221 跨站脚本漏洞 漏洞描述 Apache Tomcat SSI printenv command存在跨站脚本漏洞,此漏洞是由于应用程序对用户输入没有进行充分校验导致的。 P...
2019年4月8日 18:41CVE-2023-47873: WordPress WP Child Theme Generator < 1.1.3 - Arbitrary File Upload
漏洞标题 CVE-2023-47873: WordPress WP Child Theme Generator < 1.1.3 - Arbitrary File Upload 漏洞描述 Unrestricted Upload of File with Dangerous Type vulnerability in WEN Solutio...
2023年8月25日 10:11
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

