
最新发布第364页

CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
 2022年4月30日 13:15
Apache OFBiz webtools/control/xmlrpc 远程代码执行漏洞(CVE-2023-49070)
漏洞标题 Apache OFBiz webtools/control/xmlrpc 远程代码执行漏洞(CVE-2023-49070) 漏洞描述 Apache OFBiz是一个开源的企业资源规划(ERP)系统,提供了多种商业功能和模块。Apache OFBiz 在...
2023年10月2日 21:38
关于Vmware vcenter未授权任意文件上传漏洞(CVE-2021-21972)的问题_VMware
这篇文章主要介绍了Vmware vcenter未授权任意文件上传漏洞(CVE-2021-21972),本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 背景 CVE-2021-21972 ...
2022年9月16日 22:20CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
2022年3月3日 00:24CVE-2022-22963: Spring Cloud Function SPEL 远程命令执行漏洞
漏洞标题 CVE-2022-22963: Spring Cloud Function SPEL 远程命令执行漏洞 漏洞描述 Spring Cloud Function 是基于Spring Boot 的函数计算框架,它抽象出所有传输细节和基础架构,允许开发人员保...
2022年3月21日 23:33CVE-2023-4169: Ruijie RG-EW1200G Router – Password Reset
漏洞标题 CVE-2023-4169: Ruijie RG-EW1200G Router - Password Reset 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 1.0(1)B1P5. It has been declared as critical. Affected by ...
2023年11月11日 09:05CVE-2018-10942: Prestashop AttributeWizardPro Module – Arbitrary File Upload
漏洞标题 CVE-2018-10942: Prestashop AttributeWizardPro Module - Arbitrary File Upload 漏洞描述 In the Attribute Wizard addon 1.6.9 for PrestaShop allows remote attackers to execute...
2018年1月11日 05:10CVE-2023-49103: OwnCloud – Phpinfo Configuration
漏洞标题 CVE-2023-49103: OwnCloud - Phpinfo Configuration 漏洞描述 An issue was discovered in ownCloud owncloud/graphapi 0.2.x before 0.2.1 and 0.3.x before 0.3.1. The graphapi app...
2023年3月2日 09:42CVE-2024-28000: WordPress LiteSpeed Cache – Unauthenticated Privilege Escalation to Admin
漏洞标题 CVE-2024-28000: WordPress LiteSpeed Cache - Unauthenticated Privilege Escalation to Admin 漏洞描述 Incorrect Privilege Assignment vulnerability in LiteSpeed Technologies L...
2024年9月16日 18:51CVE-2023-41538: PHPJabbers PHP Forum Script 3.0 – Cross-Site Scripting
漏洞标题 CVE-2023-41538: PHPJabbers PHP Forum Script 3.0 - Cross-Site Scripting 漏洞描述 PhpJabbers PHP Forum Script 3.0 is vulnerable to Cross Site Scripting (XSS) via the keyword...
2023年8月29日 22:38CVE-2023-48777: WordPress Elementor 3.18.1 – File Upload/Remote Code Execution
漏洞标题 CVE-2023-48777: WordPress Elementor 3.18.1 - File Upload/Remote Code Execution 漏洞描述 The plugin is vulnerable to Remote Code Execution via file upload via the template ...
2023年12月10日 14:07CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年5月8日 06:30CVE-2023-5559: 10Web Booster < 2.24.18 - Unauthenticated Arbitrary Option Deletion
漏洞标题 CVE-2023-5559: 10Web Booster < 2.24.18 - Unauthenticated Arbitrary Option Deletion 漏洞描述 The 10Web Booster WordPress plugin before 2.24.18 does not validate the opti...
2023年2月12日 03:44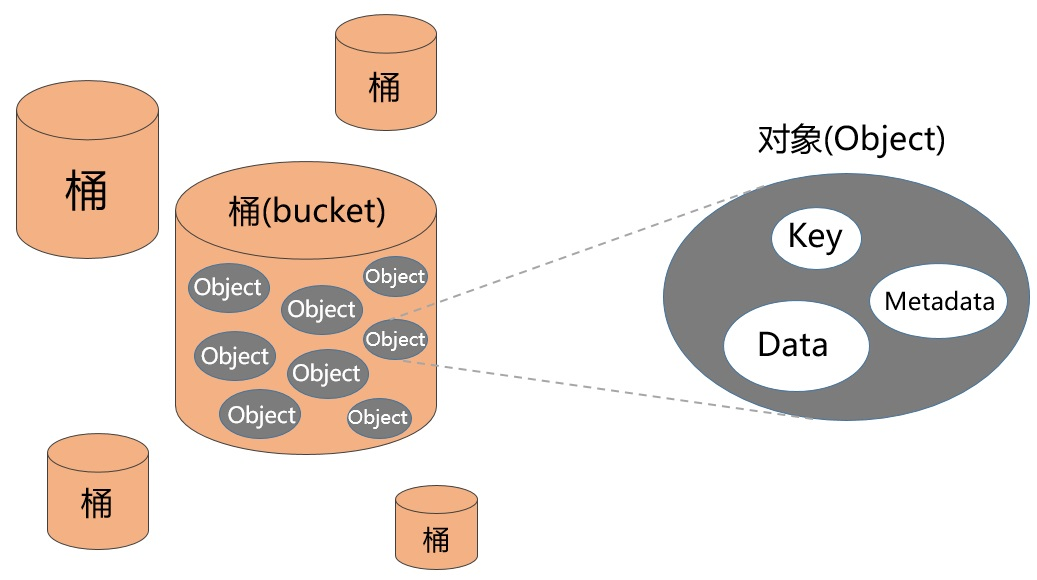
AWS S3 对象存储攻防
0x00 前言 对象存储(Object-Based Storage),也可以叫做面向对象的存储,现在也有不少厂商直接把它叫做云存储。 说到对象存储就不得不提 Amazon,Amazon S3 (Simple Storage Service) 简单存...
2022年3月10日 23:34CVE-2023-6549: Citrix Netscaler ADC & Gateway – Out-Of-Bounds Memory Read
漏洞标题 CVE-2023-6549: Citrix Netscaler ADC & Gateway - Out-Of-Bounds Memory Read 漏洞描述 The vulnerability would enable an attacker to remotely obtain sensitive information ...
2023年2月3日 21:17
万户OA download_ftp.jsp 任意文件下载漏洞
本文转载于公众号:融云攻防实验室,原文地址: 万户OA download_ftp.jsp 任意文件下载漏洞 万户软件网络是业内普遍认可的智慧政务办公专家,OA系统国家行业标准编制组长单位,协同软件国家行业标...
2026年2月13日 12:53
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

