
最新发布第364页

CVE-2019-16332: WordPress API Bearer Auth <20190907 - Cross-Site Scripting
漏洞标题 CVE-2019-16332: WordPress API Bearer Auth <20190907 - Cross-Site Scripting 漏洞描述 WordPress API Bearer Auth plugin before 20190907 contains a cross-site scripting vul...
 2019年9月4日 19:50
第十六期「听火」线上会议沙龙即将袭来,主题「协同模式下的渗透测试」
十五期内容回顾 http://zone.huoxian.cn/d/585 主题: 协同模式下的渗透测试 简介:古人云:“工欲善其事,必先利其器。随着项目协同平台http://coop.huoxian.cn/overview的对外开放,很多小伙...
2022年3月10日 23:32CVE-2024-36991: Splunk Enterprise – Local File Inclusion
漏洞标题 CVE-2024-36991: Splunk Enterprise - Local File Inclusion 漏洞描述 In Splunk Enterprise on Windows versions below 9.2.2, 9.1.5, and 9.0.10, an attacker could perform a path...
2024年7月29日 15:25CVE-2018-12300: Seagate NAS OS 4.3.15.1 – Open Redirect
漏洞标题 CVE-2018-12300: Seagate NAS OS 4.3.15.1 - Open Redirect 漏洞描述 Seagate NAS OS 4.3.15.1 contains an open redirect vulnerability in echo-server.html, which can allow an at...
2018年3月12日 06:04CVE-2023-24657: phpIPAM – 1.6 – Cross-Site Scripting
漏洞标题 CVE-2023-24657: phpIPAM - 1.6 - Cross-Site Scripting 漏洞描述 phpIPAM 1.6 contains a cross-site scripting vulnerability via the closeClass parameter at /subnet-masks/popup...
2023年11月23日 18:23Apache Kylin API未授权访问漏洞(CVE-2020-13937)
漏洞标题 Apache Kylin API未授权访问漏洞(CVE-2020-13937) 漏洞描述 【漏洞对象】Apache Kylin 【涉及版本】Kylin 2.x.x,Kylin <= 3.1.0,Kylin 4.0.0-alpha【漏洞描述】Apache Kylin是一个...
2020年6月11日 08:56CVE-2010-1345: Joomla! Component Cookex Agency CKForms – Local File Inclusion
漏洞标题 CVE-2010-1345: Joomla! Component Cookex Agency CKForms - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Cookex Agency CKForms (com_ckforms) compo...
2010年6月22日 17:14
EasyShell更新日志-V2.8.3已更新【20261018】
程序激活流程参考以下文章,直接点击右侧目录树跳转激活码教程即可 如遇程序启动失败的建议尝试一下命令 该情况主要是使用2.0之前版本,程序加密秘钥不兼容导致的macOS : rm -rf ~/Library/Appl...

 2026年10月18日 20:40
CVE-2020-9054: Zyxel NAS Firmware 5.21- Remote Code Execution
漏洞标题 CVE-2020-9054: Zyxel NAS Firmware 5.21- Remote Code Execution 漏洞描述 Multiple Zyxel network-attached storage (NAS) devices running firmware version 5.21 contain a pre-au...
2020年8月20日 17:55CVE-2010-2122: Joomla! Component simpledownload <=0.9.5 - Arbitrary File Retrieval
漏洞标题 CVE-2010-2122: Joomla! Component simpledownload <=0.9.5 - Arbitrary File Retrieval 漏洞描述 A directory traversal vulnerability in the SimpleDownload (com_simpledownloa...
2010年10月15日 03:59CVE-2022-24223: Atom CMS v2.0 – SQL Injection
漏洞标题 CVE-2022-24223: Atom CMS v2.0 - SQL Injection 漏洞描述 AtomCMS v2.0 was discovered to contain a SQL injection vulnerability via /admin/login.php. PoC代码
2022年1月25日 19:38CVE-2018-7251: Anchor CMS 0.12.3 – Error Log Exposure
漏洞标题 CVE-2018-7251: Anchor CMS 0.12.3 - Error Log Exposure 漏洞描述 Anchor CMS 0.12.3 is susceptible to an error log exposure vulnerability due to an issue in config/error.php....
2018年12月10日 09:47CVE-2021-21351: XStream <1.4.16 - Remote Code Execution
漏洞标题 CVE-2021-21351: XStream <1.4.16 - Remote Code Execution 漏洞描述 XStream before 1.4.16 is susceptible to remote code execution. An attacker can load and execute arbitra...
2021年5月7日 16:46CVE-2024-24329: TotoLink Router setPortForwardRules – Command Injection
漏洞标题 CVE-2024-24329: TotoLink Router setPortForwardRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vuln...
2024年5月14日 17:03CVE-2017-6090: PhpColl 2.5.1 Arbitrary File Upload
漏洞标题 CVE-2017-6090: PhpColl 2.5.1 Arbitrary File Upload 漏洞描述 PhpCollab 2.5.1 and earlier allows remote authenticated users to execute arbitrary code by uploading a file wit...
2017年5月26日 05:10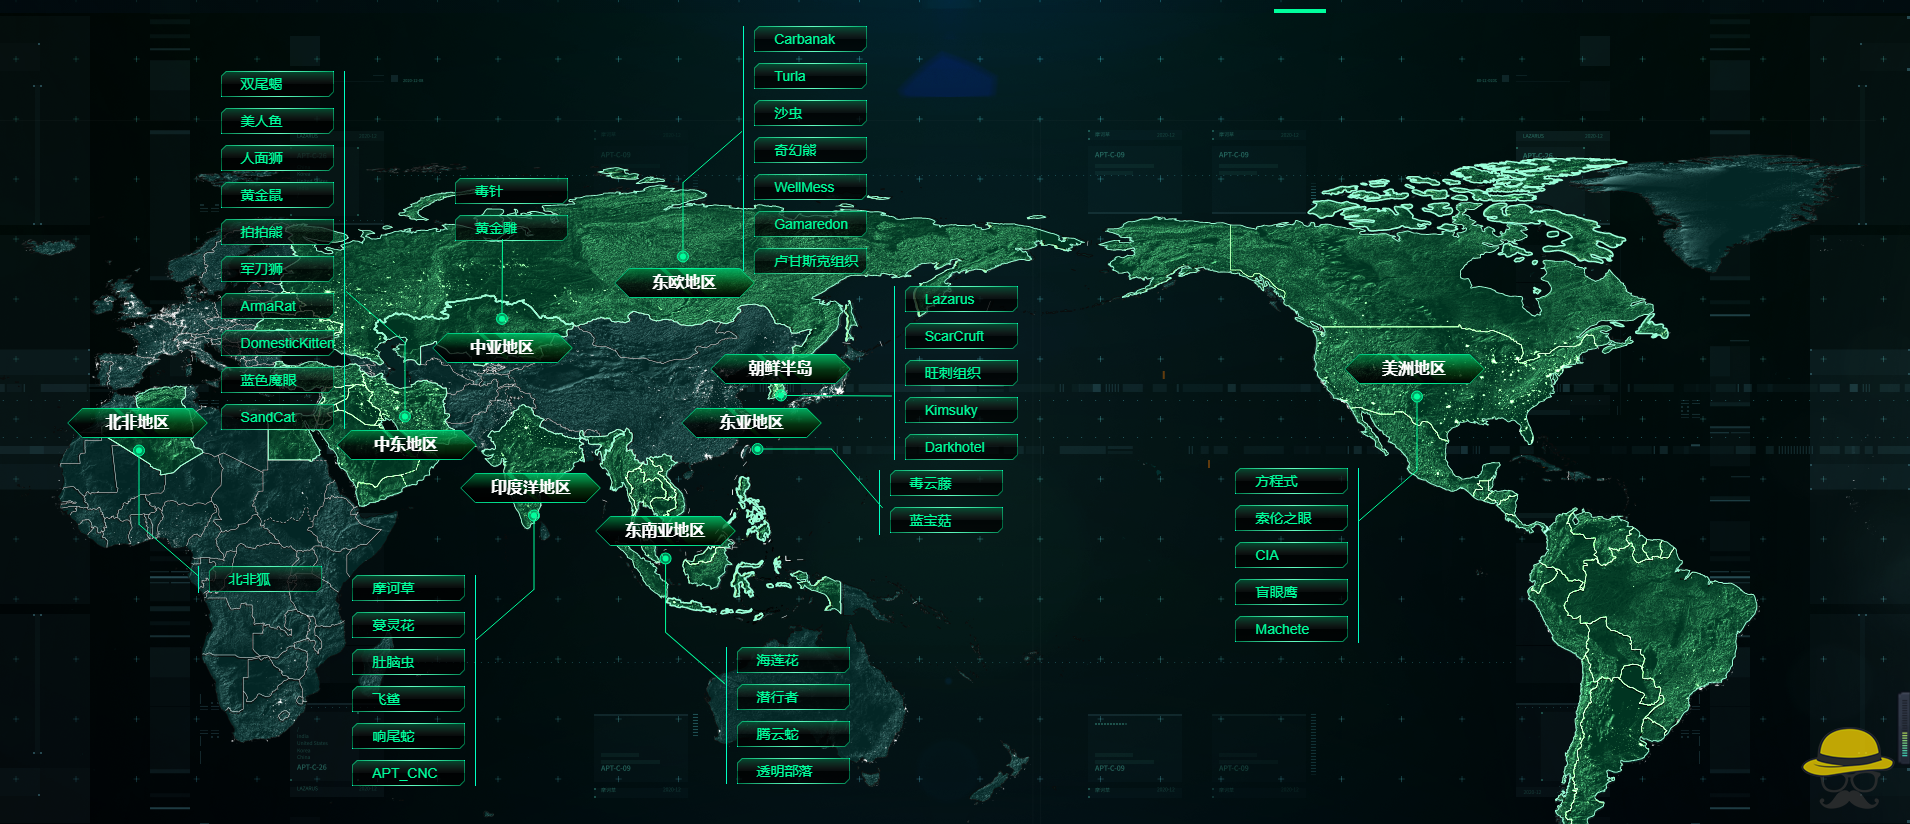
全球APT组织相关威胁情报
情报来源 360威胁情报中心 APT全景雷达 http://apt.360.net/ 安恒威胁情报中心 APT组织分布全景图 http://ti.dbappsecurity.com.cn/apt/map 相关APT组织信息 APT(Advanced Persisten...
2023年12月2日 15:21
2026年10月22日 11:46
2026年10月21日 11:45
2026年10月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53
2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

