
最新发布第36页

CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion 漏洞描述 The HUSKY – Products Filter Professiona...
 2025年6月25日 13:23
CVE-2018-14912: cgit < 1.2.1 - Directory Traversal
漏洞标题 CVE-2018-14912: cgit < 1.2.1 - Directory Traversal 漏洞描述 cGit < 1.2.1 via cgit_clone_objects has a directory traversal vulnerability when `enable-http-clone=1` is...
2018年1月14日 04:33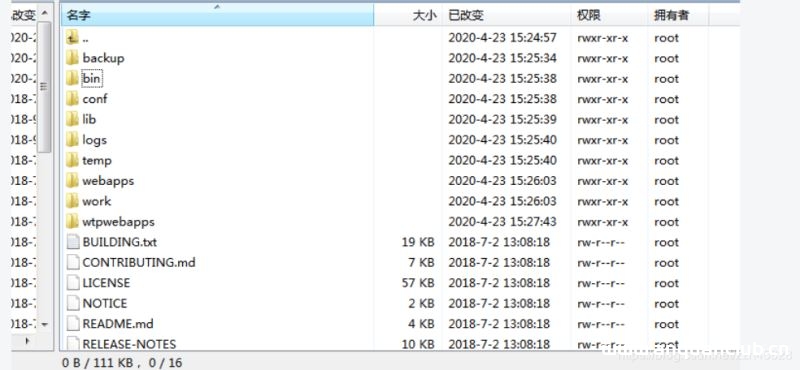
Linux部署Tomcat发布项目过程中各种问题及解决方法_Tomcat
这篇文章主要介绍了解决Linux部署Tomcat发布项目过程中各种问题,本文通过图文实例相结合给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 部署项目到项...
2024年2月3日 21:38CVE-2024-43425: Moodle – Remote Code Execution
漏洞标题 CVE-2024-43425: Moodle - Remote Code Execution 漏洞描述 Attackers with the permission to create or modify questions in Moodle courses are able to craft malicious inputs fo...
2024年9月9日 20:15CVE-2023-32315: Openfire Administration Console – Authentication Bypass
漏洞标题 CVE-2023-32315: Openfire Administration Console - Authentication Bypass 漏洞描述 Openfire is an XMPP server licensed under the Open Source Apache License. Openfire's ...
2023年11月6日 02:57(CVE-2025-54123) Hoverfly 中间件API命令注入漏洞
漏洞标题 (CVE-2025-54123) Hoverfly 中间件API命令注入漏洞 漏洞描述 (CVE-2025-54123) Hoverfly 中间件API命令注入漏洞 PoC代码 暂无
2025年1月4日 10:17CVE-2019-17230: WordPress OneTone theme <= 3.0.6 – Unauthenticated Options Changes
漏洞标题 CVE-2019-17230: WordPress OneTone theme <= 3.0.6 – Unauthenticated Options Changes 漏洞描述 includes/theme-functions.php in the OneTone theme through 3.0.6 for WordPre...
2019年5月21日 08:47CVE-2022-40881: SolarView 6.00 – Remote Command Execution
漏洞标题 CVE-2022-40881: SolarView 6.00 - Remote Command Execution 漏洞描述 SolarView Compact 6.00 is vulnerable to a command injection via network_test.php. PoC代码
2022年2月22日 17:51Adobe Commerce CVE-2024-34102 XML外部实体注入漏洞
漏洞标题 Adobe Commerce CVE-2024-34102 XML外部实体注入漏洞 漏洞描述 Adobe Commerce 存在XML外部实体注入漏洞,此漏洞是由于程序未充分验证用户输入estimate-shipping-methods的数据所导致...
2024年12月6日 05:33
bugbounty技巧聚合20211013
漏洞报告 【Acronis 100刀】www.cyberlynx.lu 子域名劫持漏洞 http://hackerone.com/reports/1256389 【Mail.ru】url跳转组合CRLF注入导致app.doma.uchi.ru上的 XSS http://hackerone.com/repor...
2022年3月10日 23:34CVE-2021-43798: Grafana v8.x – Arbitrary File Read
漏洞标题 CVE-2021-43798: Grafana v8.x - Arbitrary File Read 漏洞描述 Grafana versions 8.0.0-beta1 through 8.3.0 are vulnerable to a local directory traversal, allowing access to lo...
2021年8月17日 22:49CVE-2024-6926: Viral Signup <= 2.1 - SQL Injection
漏洞标题 CVE-2024-6926: Viral Signup <= 2.1 - SQL Injection 漏洞描述 The Viral Signup limited opt-in with viral referral sharing plugin for WordPress is vulnerable to SQL Inject...
2024年2月6日 22:59CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection
漏洞标题 CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection 漏洞描述 The LearnPress WordPress LMS Plugin plugin for WordPress is vulnerable to time-based ...
2024年3月13日 13:48CVE-2024-24329: TotoLink Router setPortForwardRules – Command Injection
漏洞标题 CVE-2024-24329: TotoLink Router setPortForwardRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vuln...
2024年2月9日 03:15CVE-2025-59474: Jenkins Sidepanel – Unauthorized Agent/Queue Exposure
漏洞标题 CVE-2025-59474: Jenkins Sidepanel - Unauthorized Agent/Queue Exposure 漏洞描述 Jenkins 2.527 and earlier, LTS 2.516.2 and earlier does not perform a permission check in th...
2025年11月15日 20:00CVE-2020-27481: Good Layers LMS Plugin <= 2.1.4 - SQL Injection
漏洞标题 CVE-2020-27481: Good Layers LMS Plugin <= 2.1.4 - SQL Injection 漏洞描述 An unauthenticated SQL Injection vulnerability in Good Layers LMS Plugin <= 2.1.4 exists due...
2020年9月11日 15:18
2026年9月16日 11:45
2026年9月15日 11:45
2026年9月14日 11:45
2026年9月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

