
最新发布第370页

CVE-2014-9735: WordPress RevSlider – Remote Code Execution via File Upload
漏洞标题 CVE-2014-9735: WordPress RevSlider - Remote Code Execution via File Upload 漏洞描述 The ThemePunch Slider Revolution (revslider) plugin before 3.0.96 for WordPress and Sho...
 2014年1月18日 05:19
CVE-2017-17043: WordPress Emag Marketplace Connector 1.0 – Cross-Site Scripting
漏洞标题 CVE-2017-17043: WordPress Emag Marketplace Connector 1.0 - Cross-Site Scripting 漏洞描述 WordPress Emag Marketplace Connector plugin 1.0 contains a reflected cross-site sc...
2017年2月13日 01:56CVE-2021-21351: XStream <1.4.16 - Remote Code Execution
漏洞标题 CVE-2021-21351: XStream <1.4.16 - Remote Code Execution 漏洞描述 XStream before 1.4.16 is susceptible to remote code execution. An attacker can load and execute arbitra...
2021年5月7日 16:46CVE-2021-22707: EVlink City < R8 V3.4.0.1 - Authentication Bypass
漏洞标题 CVE-2021-22707: EVlink City < R8 V3.4.0.1 - Authentication Bypass 漏洞描述 A CWE-798: Use of Hard-coded Credentials vulnerability exists in EVlink City (EVC1S22P4 / EVC...
2021年5月30日 10:02CVE-2025-1098: Ingress-Nginx Controller – Configuration Injection via Unsanitized Mirror Annotations
漏洞标题 CVE-2025-1098: Ingress-Nginx Controller - Configuration Injection via Unsanitized Mirror Annotations 漏洞描述 A security issue was discovered in ingress-nginx https-//gith...
2025年12月22日 05:08CVE-2023-3722: Avaya Aura Device Services – OS Command Injection
漏洞标题 CVE-2023-3722: Avaya Aura Device Services - OS Command Injection 漏洞描述 An OS command injection vulnerability was found in the Avaya Aura Device Services Web application...
2023年12月25日 17:33CVE-2020-28188: TerraMaster TOS – Unauthenticated Remote Command Execution
漏洞标题 CVE-2020-28188: TerraMaster TOS - Unauthenticated Remote Command Execution 漏洞描述 TerraMaster TOS <= 4.2.06 is susceptible to a remote code execution vulnerability wh...
2020年8月25日 03:17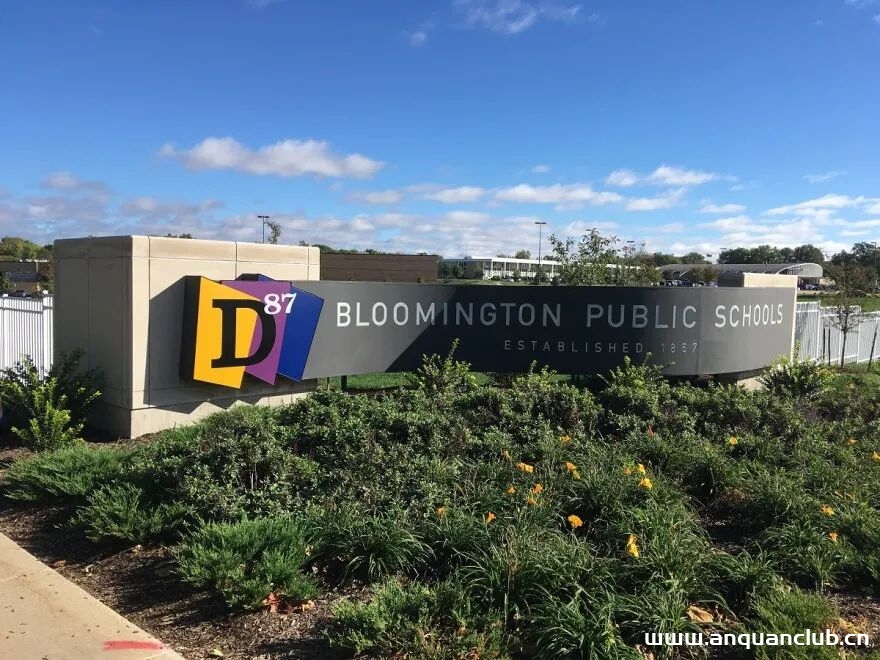
美国学区网络保险费用上涨至去年三倍多
根据伊利诺伊州布卢明顿87学区公布的责任保险费用明细表,其网络保险续保费用从2021年的6661美元跃升至今年的22229美元,增幅约为234%。学区:由州立法机关创设、组织的准市政法人,负责该州公...
2022年3月10日 23:40CVE-2025-2748: Kentico Xperience CMS – Unauthenticated Stored XSS
漏洞标题 CVE-2025-2748: Kentico Xperience CMS - Unauthenticated Stored XSS 漏洞描述 The Kentico Xperience application does not fully validate or filter files uploaded via the multi...
2025年12月19日 23:35CVE-2021-3374: Rstudio Shiny Server <1.5.16 - Local File Inclusion
漏洞标题 CVE-2021-3374: Rstudio Shiny Server <1.5.16 - Local File Inclusion 漏洞描述 Rstudio Shiny Server prior to 1.5.16 is vulnerable to local file inclusion and source code l...
2021年5月26日 07:03Ureport v2.1.7 CVE-2023-24189 XXE漏洞
漏洞标题 Ureport v2.1.7 CVE-2023-24189 XXE漏洞 漏洞描述 Ureport v2.1.7 CVE-2023-24189 XXE漏洞 日期: 2024-02-07 | 影响软件: Ureport v2.1.7 | PoC代码
2023年11月29日 10:05CVE-2024-7954: SPIP Porte Plume Plugin – Remote Code Execution
漏洞标题 CVE-2024-7954: SPIP Porte Plume Plugin - Remote Code Execution 漏洞描述 The porte_plume plugin used by SPIP before 4.30-alpha2, 4.2.13, and 4.1.16 is vulnerable to an arbi...
2024年6月21日 13:58CVE-2023-25346: ChurchCRM 4.5.3 – Cross-Site Scripting
漏洞标题 CVE-2023-25346: ChurchCRM 4.5.3 - Cross-Site Scripting 漏洞描述 A reflected cross-site scripting (XSS) vulnerability in ChurchCRM 4.5.3 allows remote attackers to inject a...
2023年3月12日 23:02CVE-2004-1641: Titan FTP ≤ 3.21 – Heap Overflow via Long Commands
漏洞标题 CVE-2004-1641: Titan FTP ≤ 3.21 - Heap Overflow via Long Commands 漏洞描述 Titan FTP versions ≤ 3.21 contain heap overflow vulnerabilities when processing long FTP comma...
2004年8月17日 15:09Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556)
漏洞标题 Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556) 漏洞描述 在Struts2 WebWork 2.1+ 和 Struts 2 的“altSyntax”功能允许将 OGNL表达式插入到文本字符串中并进行递归处理。这...
2007年2月7日 13:15CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 – SQL Injection
漏洞标题 CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 - SQL Injection 漏洞描述 SQL Injection exists in the PrayerCenter 3.0.2 component for Joomla! via the sessionid paramet...
2018年9月10日 13:53
2026年11月11日 11:45
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

