
最新发布第370页
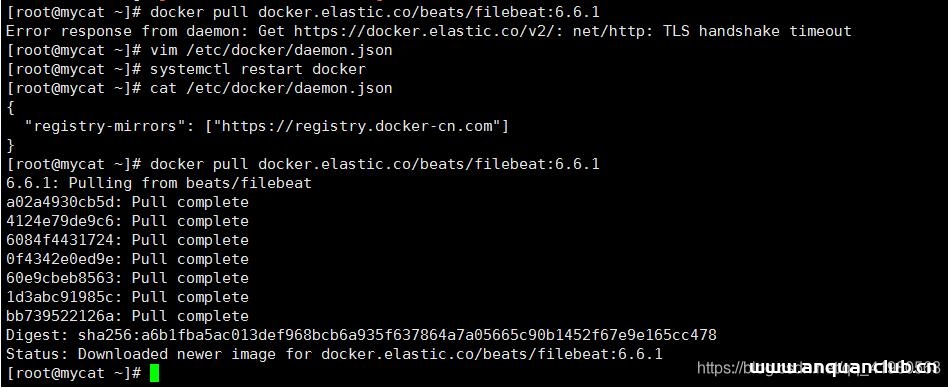
docker pull拉取超时的解决方案_docker
这篇文章主要介绍了docker pull拉取超时的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 最近docker pull镜像的时候非常不稳定,速度慢不说还经常超时失败 Pullin...
 2022年8月17日 21:34

CVE-2022-0785: WordPress Daily Prayer Time <2022.03.01 - SQL Injection
漏洞标题 CVE-2022-0785: WordPress Daily Prayer Time <2022.03.01 - SQL Injection 漏洞描述 WordPress Daily Prayer Time plugin prior to 2022.03.01 contains a SQL injection vulnerab...
2022年12月18日 18:10CVE-2023-21839: Oracle WebLogic Server – Unauthorized Access
漏洞标题 CVE-2023-21839: Oracle WebLogic Server - Unauthorized Access 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Su...
2023年2月5日 13:53CVE-2019-9874: Sitecore Experience Platform – Deserialization of Untrusted Data
漏洞标题 CVE-2019-9874: Sitecore Experience Platform - Deserialization of Untrusted Data 漏洞描述 Sitecore Experience Platform before 8.2 Update-7 and 9.0 before Update-2 is vulner...
2019年12月22日 16:19CVE-2021-37304: Jeecg Boot <= 2.4.5 - Information Disclosure
漏洞标题 CVE-2021-37304: Jeecg Boot <= 2.4.5 - Information Disclosure 漏洞描述 An Insecure Permissions issue in jeecg-boot 2.4.5 allows unauthenticated remote attackers to gain ...
2021年7月21日 13:24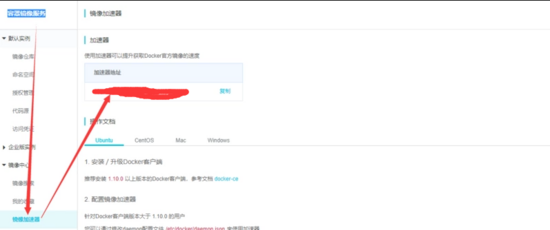
docker在win10家庭版下构建laravel开发环境的教程详解_docker
这篇文章主要介绍了docker在win10家庭版下构建laravel开发环境,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 操作系统: win10 家庭版 安装dock...
2023年11月17日 20:01CVE-2025-34045: WeiPHP 5.0 – Path Traversal
漏洞标题 CVE-2025-34045: WeiPHP 5.0 - Path Traversal 漏洞描述 WeiPHP 5.0 contains a path traversal caused by insufficient input validation of the picUrl parameter in /public/index....
2025年9月27日 14:55CVE-2020-13379: Grafana 3.0.1-7.0.1 – Server-Side Request Forgery
漏洞标题 CVE-2020-13379: Grafana 3.0.1-7.0.1 - Server-Side Request Forgery 漏洞描述 Grafana 3.0.1 through 7.0.1 is susceptible to server-side request forgery via the avatar feature...
2020年2月9日 13:23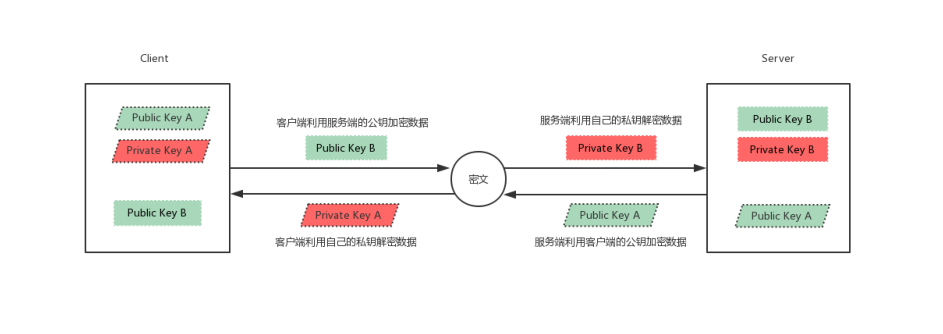
Linux系统中SSH服务基于key认证实践的过程_Linux
这篇文章主要介绍了Linux系统中SSH服务基于key认证实践,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 众所周知ssh是目前较可靠,专为远程登录会话和其他网络服务提...
2024年5月6日 21:05CVE-2022-22242: Juniper Networks Junos OS 错误页面反射 XSS 漏洞
漏洞标题 CVE-2022-22242: Juniper Networks Junos OS 错误页面反射 XSS 漏洞 漏洞描述 CVE-2022-22242它是位于出错页面 (“error.php”) 上的预认证反射型XSS漏洞,可导致远程攻击者嗅探 Junos...
2022年3月9日 20:20CVE-2020-8771: WordPress Time Capsule < 1.21.16 - Authentication Bypass
漏洞标题 CVE-2020-8771: WordPress Time Capsule < 1.21.16 - Authentication Bypass 漏洞描述 WordPress Time Capsule plugin before 1.21.16 for WordPress has an authentication bypass...
2020年4月28日 01:47CVE-2022-34576: WAVLINK WN535 G3 – Improper Access Control
漏洞标题 CVE-2022-34576: WAVLINK WN535 G3 - Improper Access Control 漏洞描述 WAVLINK WN535 G3 M35G3R.V5030.180927 is susceptible to improper access control. A vulnerability in /cgi...
2022年4月28日 22:34
CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion
漏洞标题 CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion 漏洞描述 WordPress MyPixs 0.3 and prior contains a local file inclusion vulnerability. PoC代码
2015年4月25日 12:11CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection
漏洞标题 CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection 漏洞描述 A SQL injection vulnerability in the product_all_one_img and image_product parameters of the...
2022年12月12日 15:44CVE-2016-15042: WordPress Frontend File Manager < 4.0 & N-Media Post Frontend < 1.1 - Arbitrary File Upload
漏洞标题 CVE-2016-15042: WordPress Frontend File Manager < 4.0 & N-Media Post Frontend < 1.1 - Arbitrary File Upload 漏洞描述 The Frontend File Manager plugin (<4.0) a...
2016年3月12日 21:48
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

