
最新发布第383页

CVE-2021-32819: Nodejs Squirrelly – Remote Code Execution
漏洞标题 CVE-2021-32819: Nodejs Squirrelly - Remote Code Execution 漏洞描述 Nodejs Squirrelly is susceptible to remote code execution. Squirrelly is a template engine implemented i...
 2021年1月16日 12:11
CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
2023年10月29日 12:02CVE-2022-29464: WSO2 Management – Arbitrary File Upload & Remote Code Execution
漏洞标题 CVE-2022-29464: WSO2 Management - Arbitrary File Upload & Remote Code Execution 漏洞描述 Certain WSO2 products allow unrestricted file upload with resultant remote cod...
2022年1月28日 23:41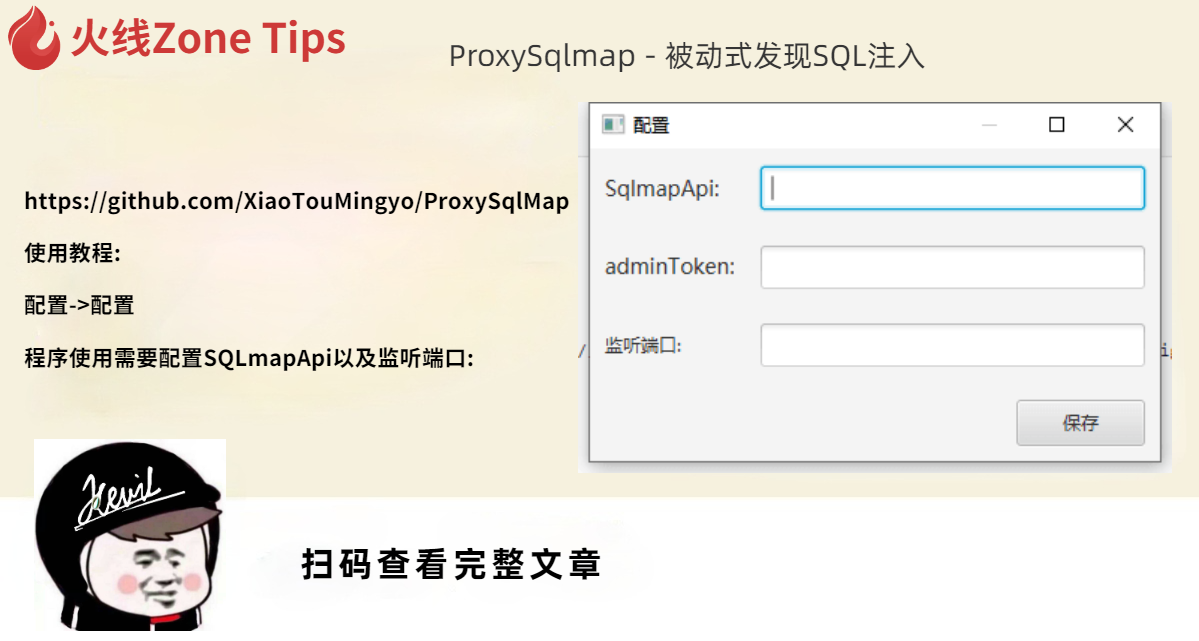
ProxySqlmap – 被动式发现SQL注入
http://github.com/XiaoTouMingyo/ProxySqlMap 使用教程: 配置->配置 程序使用需要配置SQLmapApi以及监听端口: 在SQLMAP中使用命令开开启SQLmapApi: sqlmapapi -s --host=0.0.0.0 --port=889...
2022年3月10日 23:36
docker 查看容器的挂载目录操作_docker
这篇文章主要介绍了docker 查看容器的挂载目录操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 只显示Docker容器挂载目录信息 docker inspect --format '{{.Config.Volu...
2022年8月14日 20:20CVE-2022-39048: ServiceNow – Cross-site Scripting
漏洞标题 CVE-2022-39048: ServiceNow - Cross-site Scripting 漏洞描述 A XSS vulnerability was identified in the ServiceNow UI page assessment_redirect. To exploit this vulnerability,...
2022年7月23日 14:32CVE-2015-3035: TP-LINK – Local File Inclusion
漏洞标题 CVE-2015-3035: TP-LINK - Local File Inclusion 漏洞描述 TP-LINK is susceptible to local file inclusion in these products: Archer C5 (1.2) with firmware before 150317, Arche...
2015年9月2日 12:08CVE-2023-43326: MooSocial 3.1.8 – Cross-Site Scripting
漏洞标题 CVE-2023-43326: MooSocial 3.1.8 - Cross-Site Scripting 漏洞描述 A reflected cross-site scripting (XSS) vulnerability exisits in multiple url of mooSocial v3.1.8 which allo...
2023年5月2日 13:15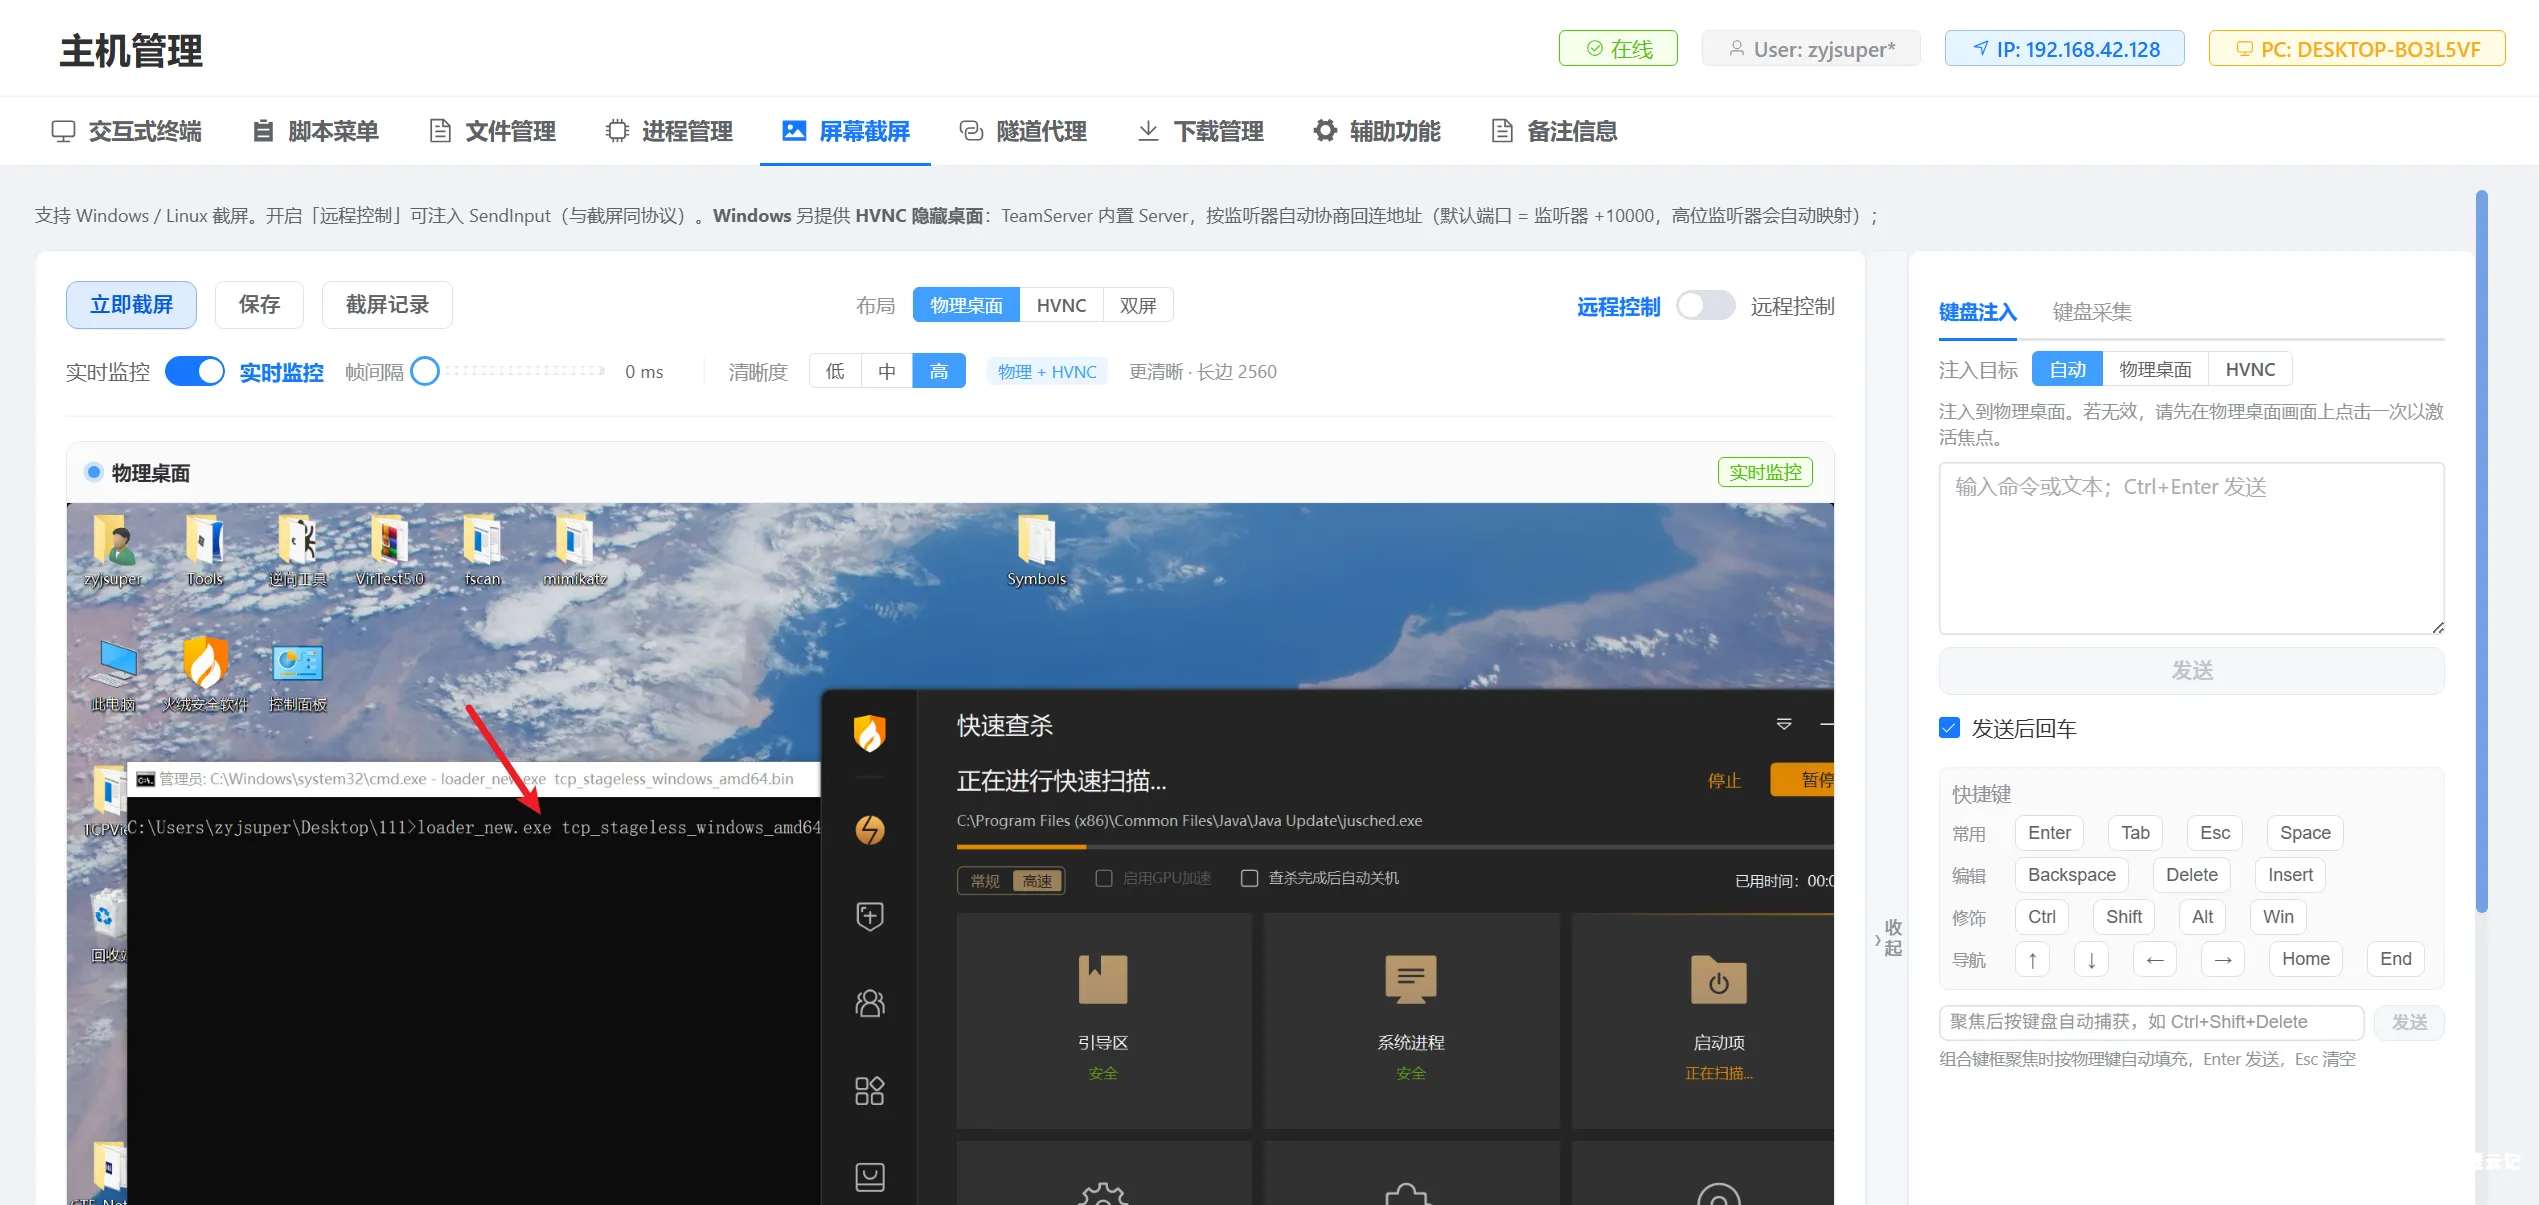
EasyShell&EasyTools 双工具更新|中秋×国庆渗透云记福利抽奖活动
前言 一直在思考为什么其他师傅的公众号排班、文案总是那么优秀,思来想去,还是不知道怎么写。 为了减少内耗,还是继续打磨我那俩小垃圾(EasyShell和EasyTools)吧, AI越来越强大,出现了更...

 2026年9月20日 16:22
CVE-2022-2544: WordPress Ninja Job Board < 1.3.3 - Direct Request
漏洞标题 CVE-2022-2544: WordPress Ninja Job Board < 1.3.3 - Direct Request 漏洞描述 WordPress Ninja Job Board plugin prior to 1.3.3 is susceptible to a direct request vulnerabil...
2022年1月24日 15:16CVE-2024-1561: Gradio 4.3-4.12 – Local File Read
漏洞标题 CVE-2024-1561: Gradio 4.3-4.12 - Local File Read 漏洞描述 Local file read by calling arbitrary methods of Components class between Gradio versions 4.3-4.12 PoC代码
2024年8月14日 22:25CVE-2018-11138: Quest KACE System Management Appliance 8.0.318 – Remote Code Execution
漏洞标题 CVE-2018-11138: Quest KACE System Management Appliance 8.0.318 - Remote Code Execution 漏洞描述 The '/common/download_agent_installer.php' script in the Quest KA...
2018年7月21日 11:31CVE-2020-13700: WordPress acf-to-rest-api <=3.1.0 - Insecure Direct Object Reference
漏洞标题 CVE-2020-13700: WordPress acf-to-rest-api <=3.1.0 - Insecure Direct Object Reference 漏洞描述 WordPress acf-to-rest-ap through 3.1.0 allows an insecure direct object re...
2020年6月10日 20:07CVE-2012-5321: TikiWiki CMS Groupware v8.3 – Open Redirect
漏洞标题 CVE-2012-5321: TikiWiki CMS Groupware v8.3 - Open Redirect 漏洞描述 tiki-featured_link.php in TikiWiki CMS/Groupware 8.3 allows remote attackers to load arbitrary web site...
2012年8月15日 16:05CVE-2023-6989: Shield Security WP Plugin <= 18.5.9 - Local File Inclusion
漏洞标题 CVE-2023-6989: Shield Security WP Plugin <= 18.5.9 - Local File Inclusion 漏洞描述 The Shield Security Smart Bot Blocking & Intrusion Prevention Security plugin for...
2023年12月27日 10:57CVE-2021-30497: Ivanti Avalanche 6.3.2 – Local File Inclusion
漏洞标题 CVE-2021-30497: Ivanti Avalanche 6.3.2 - Local File Inclusion 漏洞描述 Ivanti Avalanche 6.3.2 is vulnerable to local file inclusion because it allows remote unauthenticate...
2021年7月11日 11:09
2026年10月23日 11:45
2026年10月22日 11:46
2026年10月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

