
最新发布第393页

CVE-2021-41291: ECOA Building Automation System – Directory Traversal Content Disclosure
漏洞标题 CVE-2021-41291: ECOA Building Automation System - Directory Traversal Content Disclosure 漏洞描述 The ECOA BAS controller suffers from a directory traversal content disclo...
 2021年4月5日 07:33
CVE-2020-35359: Pure-FTPd 1.0.48 – Denial of Service
漏洞标题 CVE-2020-35359: Pure-FTPd 1.0.48 - Denial of Service 漏洞描述 Pure-FTPd 1.0.48 is vulnerable to Denial of Service via exhaustion of connections due to lack of proper conne...
2020年7月26日 21:26CVE-2021-22205: GitLab CE/EE – Remote Code Execution
漏洞标题 CVE-2021-22205: GitLab CE/EE - Remote Code Execution 漏洞描述 GitLab CE/EE starting from 11.9 does not properly validate image files that were passed to a file parser, res...
2021年11月17日 17:58CVE-2017-5521: Bypassing Authentication on NETGEAR Routers
漏洞标题 CVE-2017-5521: Bypassing Authentication on NETGEAR Routers 漏洞描述 NETGEAR routers before 6.0.10 allow remote attackers to bypass authentication and gain access to the ro...
2017年3月9日 04:46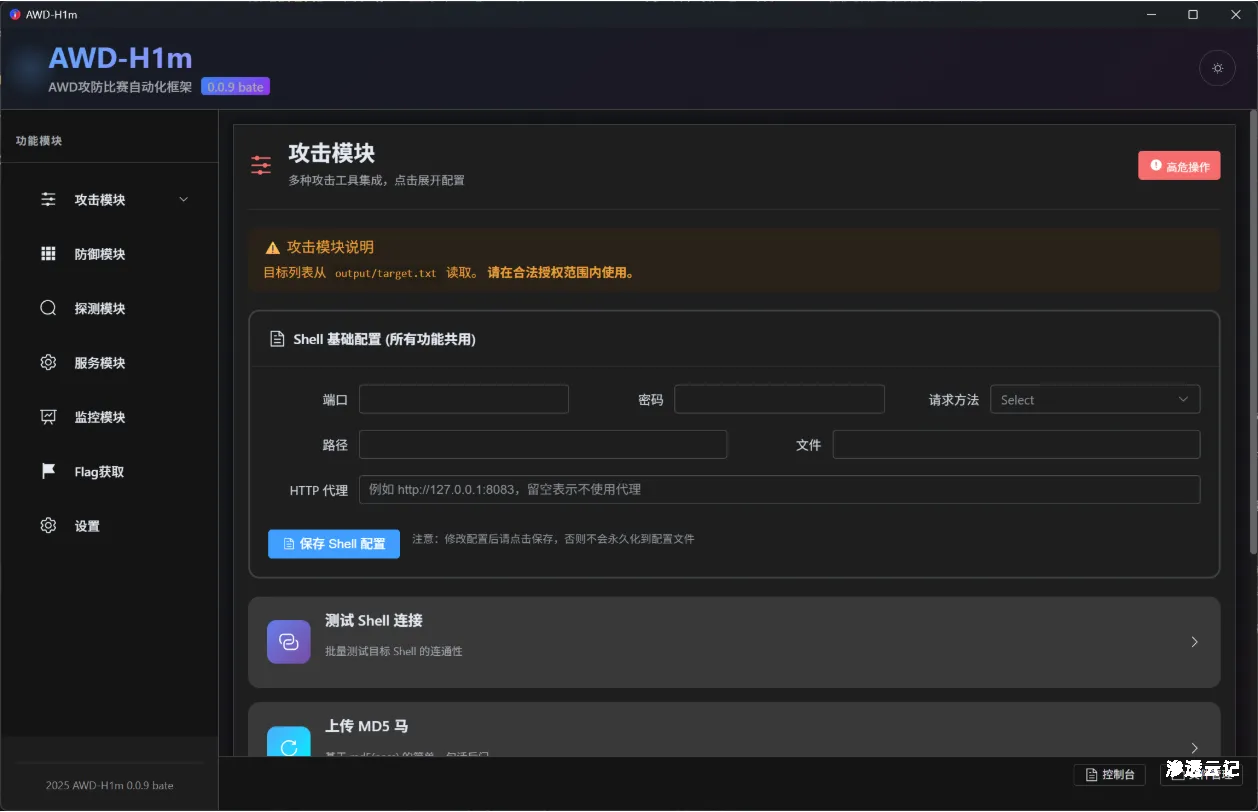
AWD-H1M-PRO -专为 CTF 设计的自动化 AWD 工具
项目介绍 AWD-H1m 是一款专为 CTF AWD (Attack With Defense) 赛制设计的桌面应用程序,帮助参赛选手在有限的比赛时间内高效完成攻击、防御、流量分析与 Flag 提交等核心任务。 在 AWD 竞赛中,...

 2026年3月25日 22:03
CVE-2021-39327: WordPress BulletProof Security 5.1 Information Disclosure
漏洞标题 CVE-2021-39327: WordPress BulletProof Security 5.1 Information Disclosure 漏洞描述 The BulletProof Security WordPress plugin is vulnerable to sensitive information disclos...
2021年4月18日 23:34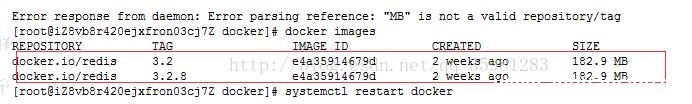
在docker下删除两个id相同的镜像的操作_docker
这篇文章主要介绍了在docker下删除两个id相同的镜像的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 今天建立docker容器的时候由于疏忽,镜像的名字输错了,结果容器...
2023年1月31日 20:08CVE-2017-18487: AdPush < 1.44 - Cross-Site Scripting
漏洞标题 CVE-2017-18487: AdPush < 1.44 - Cross-Site Scripting 漏洞描述 The adsense-plugin (aka Google AdSense) plugin before 1.44 for WordPress has multiple XSS issues. PoC代码
2017年12月12日 12:28CVE-2019-8943: WordPress Core 5.0.0 – Crop-image Shell Upload
漏洞标题 CVE-2019-8943: WordPress Core 5.0.0 - Crop-image Shell Upload 漏洞描述 WordPress through 5.0.3 allows Path Traversal in wp_crop_image(). An attacker (who has privileges to...
2019年2月24日 14:52CVE-2021-26855: Microsoft Exchange Server Remote Code Execution
漏洞标题 CVE-2021-26855: Microsoft Exchange Server Remote Code Execution 漏洞描述 Microsoft Exchange Server Remote Code Execution Vulnerability PoC代码
2021年8月30日 04:02CVE-2017-9506: Atlassian Jira IconURIServlet – Cross-Site Scripting/Server-Side Request Forgery
漏洞标题 CVE-2017-9506: Atlassian Jira IconURIServlet - Cross-Site Scripting/Server-Side Request Forgery 漏洞描述 The Atlassian Jira IconUriServlet of the OAuth Plugin from version...
2017年9月26日 14:25CVE-2023-2256: WordPress Product Addons & Fields for WooCommerce < 32.0.7 - Cross-Site Scripting
漏洞标题 CVE-2023-2256: WordPress Product Addons & Fields for WooCommerce < 32.0.7 - Cross-Site Scripting 漏洞描述 The Product Addons & Fields for WooCommerce WordPress ...
2023年5月20日 04:20CVE-2022-38840: Güralp MAN-EAM-0003 3.2.4 – XML External Entity (XXE)
漏洞标题 CVE-2022-38840: Güralp MAN-EAM-0003 3.2.4 - XML External Entity (XXE) 漏洞描述 cgi-bin/xmlstatus.cgi in Güralp MAN-EAM-0003 3.2.4 is vulnerable to an XML External Entity...
2022年4月22日 03:06CVE-2022-4260: WordPress WP-Ban <1.69.1 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-4260: WordPress WP-Ban <1.69.1 - Stored Cross-Site Scripting 漏洞描述 WordPress WP-Ban plugin before 1.69.1 contains a stored cross-site scripting vulnerabilit...
2022年8月27日 16:09Apache Struts2(S2-012)远程代码执行漏洞(CVE-2013-1965)
漏洞标题 Apache Struts2(S2-012)远程代码执行漏洞(CVE-2013-1965) 漏洞描述 S2-012中,包含特制请求参数的请求可用于将任意 OGNL代码注入属性,然后用作重定向地址的请求参数,这将导致进一步...
2013年9月19日 17:01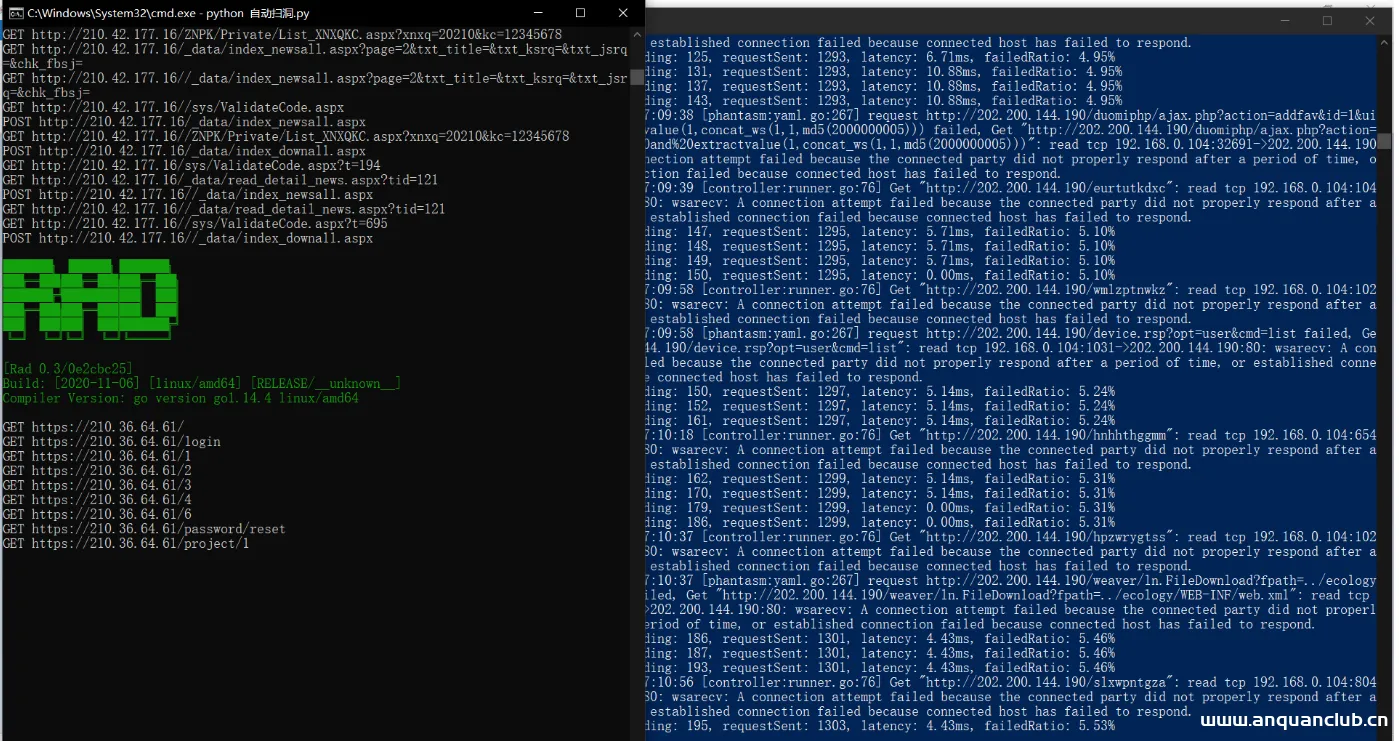
Rad爬虫——一款专为安全扫描而生的浏览器爬虫
rad,全名 Radium,名字来源于放射性元素——镭, 从一个URL开始,辐射到一整个站点空间 一款专为安全扫描而生的浏览器爬虫 下载地址 http://github.com/chaitin/rad/releases 快速使用 在...
2023年1月13日 19:53
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

