
最新发布第394页
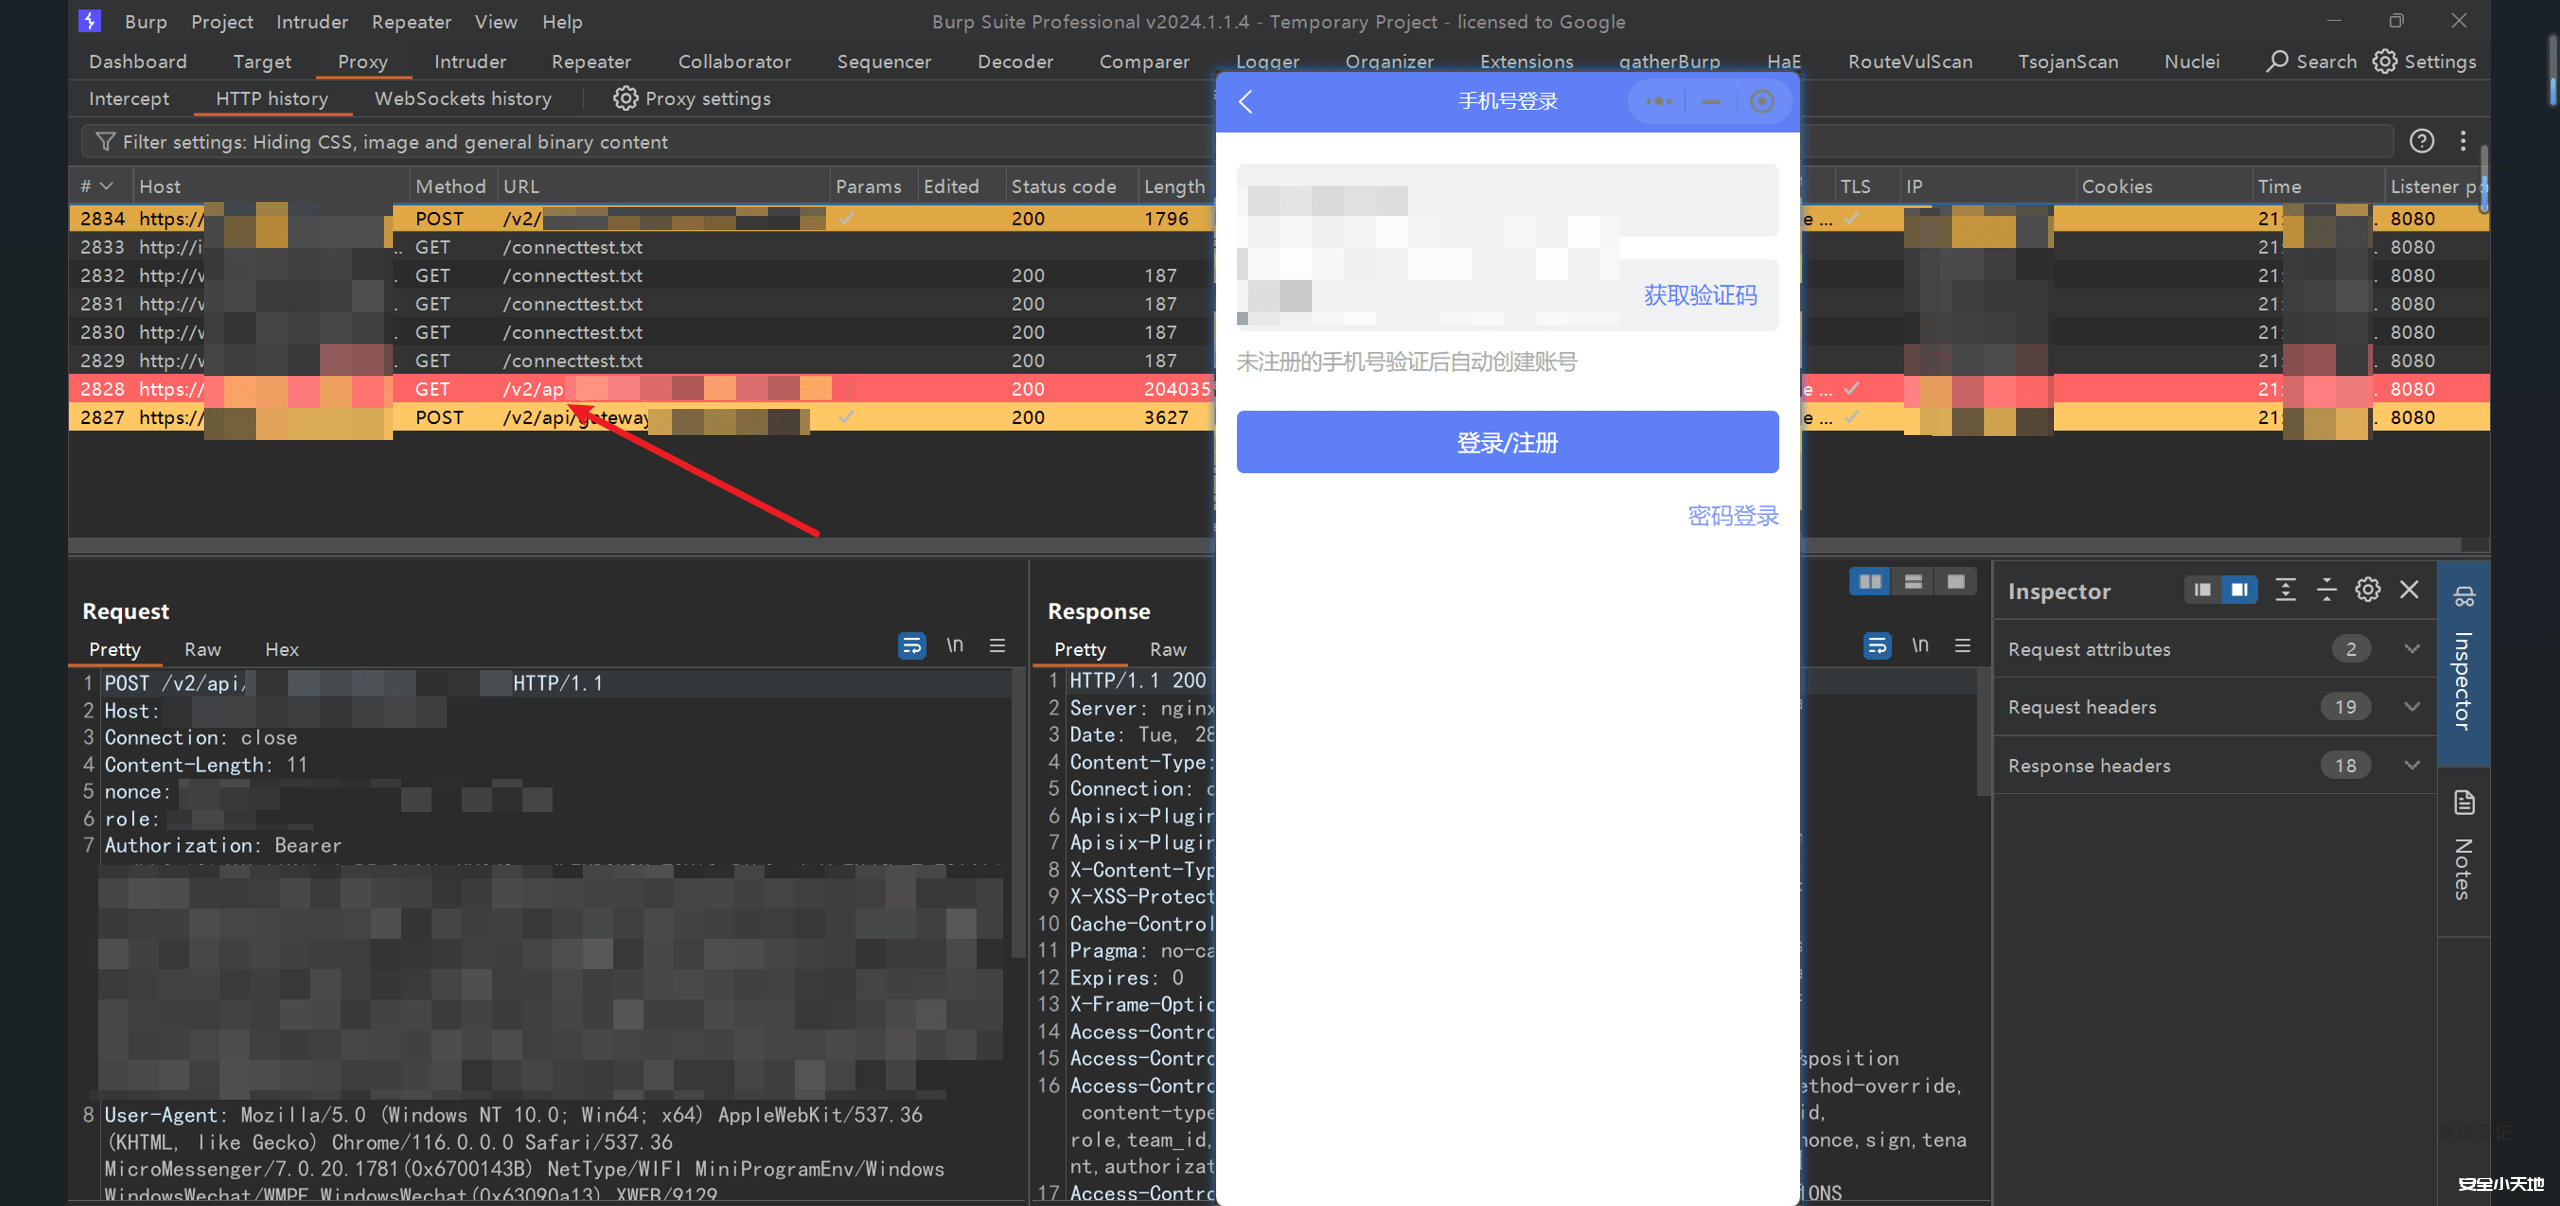
渗透测试中针对微信小程序AppSecret秘钥泄露的利用方式
前言 针对小程序和公众号的渗透测试,咱们都知道只要拿到开发者ID(AppID)和开发者密码(AppSecret),咱们即可结束此次测试。拿到 Appid和Appsecret之后咱们大概率可以直接实现账号接管。 记录一...

 2024年6月30日 13:24

CVE-2021-24435: WordPress Titan Framework plugin <= 1.12.1 - Cross-Site Scripting
漏洞标题 CVE-2021-24435: WordPress Titan Framework plugin <= 1.12.1 - Cross-Site Scripting 漏洞描述 The iframe-font-preview.php file of the titan-framework does not properly esc...
 2021年10月13日 16:24
CVE-2021-21805: Advantech R-SeeNet 2.4.12 – OS Command Injection
漏洞标题 CVE-2021-21805: Advantech R-SeeNet 2.4.12 - OS Command Injection 漏洞描述 Advantech R-SeeNet 2.4.12 is susceptible to remote OS command execution via the ping.php script f...
2021年6月19日 15:21CVE-2022-31798: Nortek Linear eMerge E3-Series – Cross-Site Scripting
漏洞标题 CVE-2022-31798: Nortek Linear eMerge E3-Series - Cross-Site Scripting 漏洞描述 There is a local session fixation vulnerability that, when chained with cross-site scripting...
2022年9月26日 20:44CVE-2023-40779: IceWarp Mail Server Deep Castle 2 v.13.0.1.2 – Open Redirect
漏洞标题 CVE-2023-40779: IceWarp Mail Server Deep Castle 2 v.13.0.1.2 - Open Redirect 漏洞描述 An issue in IceWarp Mail Server Deep Castle 2 v.13.0.1.2 allows a remote attacker to ...
2023年5月12日 22:56
【代码审计】zzzphp V1.6.0 php语言建站系统 任意文件删除、远程代码执行漏洞分析审计
前言 zzzcms系统是一款免费、开源的php语言建站系统,采用类MVC结构,框架简单,简单易学。诞生于2016年,其设计初衷是为了让用户快速、方便地建立自己的网站。该系统采用PHP语言开发,支持多相...
2023年6月3日 17:17CVE-2023-41266: Qlik Sense Enterprise – Path Traversal
漏洞标题 CVE-2023-41266: Qlik Sense Enterprise - Path Traversal 漏洞描述 A path traversal vulnerability found in Qlik Sense Enterprise for Windows for versions May 2023 Patch 3 and...
2023年1月11日 02:08CVE-2020-24186: WordPress wpDiscuz <=7.0.4 - Remote Code Execution
漏洞标题 CVE-2020-24186: WordPress wpDiscuz <=7.0.4 - Remote Code Execution 漏洞描述 WordPress wpDiscuz plugin versions version 7.0 through 7.0.4 are susceptible to remote code ...
2020年8月21日 02:48CVE-2021-34370: Accela Civic Platform <=21.1 - Cross-Site Scripting
漏洞标题 CVE-2021-34370: Accela Civic Platform <=21.1 - Cross-Site Scripting 漏洞描述 Accela Civic Platform through 21.1 contains a cross-site scripting vulnerability via ssoAda...
2021年3月11日 17:55Atlassian Jira 信息泄露(CVE-2019-3401)
漏洞标题 Atlassian Jira 信息泄露(CVE-2019-3401) 漏洞描述 Jira 7.13.3之前版本和8.1.1之前版本8.0.0中的ManageFilters.jspa资源允许远程攻击者通过不正确的授权检查枚举用户名。 PoC代码 暂...
2019年9月2日 12:42CVE-2021-24991: WooCommerce PDF Invoices & Packing Slips WordPress Plugin < 2.10.5 - Cross-Site Scripting
漏洞标题 CVE-2021-24991: WooCommerce PDF Invoices & Packing Slips WordPress Plugin < 2.10.5 - Cross-Site Scripting 漏洞描述 The Wordpress plugin WooCommerce PDF Invoices &am...
2021年7月14日 05:08CVE-2011-5265: Featurific For WordPress 1.6.2 – Cross-Site Scripting
漏洞标题 CVE-2011-5265: Featurific For WordPress 1.6.2 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in cached_image.php in the Featurific For WordPress plug...
2011年2月15日 14:57CVE-2020-12124: WAVLINK WN530H4 live_api.cgi – Command Injection
漏洞标题 CVE-2020-12124: WAVLINK WN530H4 live_api.cgi - Command Injection 漏洞描述 A remote command-line injection vulnerability in the /cgi-bin/live_api.cgi endpoint of the WAVLIN...
2020年8月17日 13:17CVE-2019-10758: mongo-express Remote Code Execution
漏洞标题 CVE-2019-10758: mongo-express Remote Code Execution 漏洞描述 mongo-express before 0.54.0 is vulnerable to remote code execution via endpoints that uses the `toBSON` method...
2019年10月16日 05:00CVE-2025-26793: FREEDOM Administration – Default Login
漏洞标题 CVE-2025-26793: FREEDOM Administration - Default Login 漏洞描述 The Web GUI configuration panel of Hirsch (formerly Identiv and Viscount) Enterphone MESH through 2024 ship...
2025年5月15日 19:13Appspace服务端请求伪造漏洞(CVE-2021-27670)
漏洞标题 Appspace服务端请求伪造漏洞(CVE-2021-27670) 漏洞描述 Appspace 6.2.4存在漏洞,允许通过api/v1/core/proxy/jsonprequest接口来进行服务端请求伪造,危害系统安全。 PoC代码 暂无
2021年9月15日 00:11
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

