
最新发布第39页
黑客在伊朗国营广播电视上呼吁暗杀最高领袖
2022年1月下旬,伊朗伊斯兰共和国广播电视台(IRIB,国营垄断企业,伊朗唯一覆盖全国的广播电视媒体)遭网络攻击,攻击者在该电视台播放反对派领导人的镜头,并呼吁暗杀伊朗现任最高领导人。2月...
 2022年3月10日 23:40

CVE-2024-3300: Delmia Apriso – Pre-Authentication Unsafe .NET Object Deserialization
漏洞标题 CVE-2024-3300: Delmia Apriso - Pre-Authentication Unsafe .NET Object Deserialization 漏洞描述 An unsafe .NET object deserialization vulnerability in DELMIA Apriso Release ...
2024年9月25日 17:57CVE-2022-4306: WordPress Panda Pods Repeater Field <1.5.4 - Cross-Site Scripting
漏洞标题 CVE-2022-4306: WordPress Panda Pods Repeater Field <1.5.4 - Cross-Site Scripting 漏洞描述 WordPress Panda Pods Repeater Field before 1.5.4 contains a cross-site scripti...
2022年2月12日 08:32
docker中使用mysql数据库实现局域网访问_docker
在本篇内容里小编给大家整理了关于docker中使用mysql数据库实现局域网访问相关内容,有需要的朋友们可以学习下。 1.获取mysql镜像 docker pull mysql:5.6 注意:此处之所以获取mysql5.6是因为my...
2024年3月8日 20:40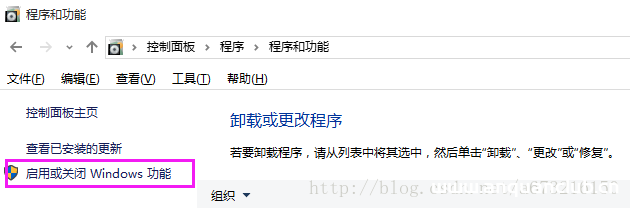
Win10下配置IIS10并支持调试ASP程序的步骤_win服务器
今天临时需要在Win10下配置IIS10并支持调试ASP程序的步骤,不像windows服务器版本比较好找,这个得找到放风,这里九尾大家分享一下需要的朋友可以参考下 微软公司的IIS IIS(Internet Informatio...
2024年2月12日 20:00CVE-2023-40000: LiteSpeed Cache <= 5.7 - Unauthenticated Stored XSS
漏洞标题 CVE-2023-40000: LiteSpeed Cache <= 5.7 - Unauthenticated Stored XSS 漏洞描述 Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting...
2023年7月17日 15:38
泛微OA 多个漏洞介绍
0x02 漏洞描述 本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 泛微OA E-Cology getdata.jsp SQL注入漏洞 本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 泛微OA E-Cology Lo...

 2023年2月10日 14:03
CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload
漏洞标题 CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload 漏洞描述 Arbitrary File Upload vulnerability in WordPress Royal Elementor Addon...
2023年7月21日 14:53CVE-2023-43187: NodeBB XML-RPC Request xmlrpc.php – XML Injection
漏洞标题 CVE-2023-43187: NodeBB XML-RPC Request xmlrpc.php - XML Injection 漏洞描述 A remote code execution (RCE) vulnerability in the xmlrpc.php endpoint of NodeBB Inc NodeBB foru...
2023年8月14日 17:36
极速文件搜索工具 everything
杂谈 今天分享一个提升工作效率的小技巧,使用everything可以提升你的搜索效率,找文件的时候就不用那么头疼了 功能介绍 Everthing可以在闪电般的瞬间从海量的硬盘中找到你需要的文件,速度快到...
2022年5月17日 22:11CVE-2014-3704: Drupal SQL Injection
漏洞标题 CVE-2014-3704: Drupal SQL Injection 漏洞描述 The expandArguments function in the database abstraction API in Drupal core 7.x before 7.32 does not properly construct prepar...
2014年5月20日 18:34CVE-2018-16159: WordPress Gift Voucher <4.1.8 - Blind SQL Injection
漏洞标题 CVE-2018-16159: WordPress Gift Voucher <4.1.8 - Blind SQL Injection 漏洞描述 WordPress Gift Vouchers plugin before 4.1.8 contains a blind SQL injection vulnerability vi...
2018年12月15日 00:44CVE-2023-3847: MooDating 1.2 – Cross-Site scripting
漏洞标题 CVE-2023-3847: MooDating 1.2 - Cross-Site scripting 漏洞描述 A vulnerability classified as problematic was found in mooSocial mooDating 1.2. This vulnerability affects unk...
2023年6月5日 06:00CVE-2022-33965: WordPress Visitor Statistics <=5.7 - SQL Injection
漏洞标题 CVE-2022-33965: WordPress Visitor Statistics <=5.7 - SQL Injection 漏洞描述 WordPress Visitor Statistics plugin through 5.7 contains multiple unauthenticated SQL inject...
2022年4月9日 20:52CVE-2013-7240: WordPress Plugin Advanced Dewplayer 1.2 – Directory Traversal
漏洞标题 CVE-2013-7240: WordPress Plugin Advanced Dewplayer 1.2 - Directory Traversal 漏洞描述 A directory traversal vulnerability in download-file.php in the Advanced Dewplayer pl...
2013年10月27日 16:12CVE-2011-5252: Orchard ‘ReturnUrl’ Parameter URI – Open Redirect
漏洞标题 CVE-2011-5252: Orchard 'ReturnUrl' Parameter URI - Open Redirect 漏洞描述 Open redirect vulnerability in Users/Account/LogOff in Orchard 1.0.x before 1.0.21, 1.1...
2011年8月20日 22:04
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
2026年10月7日 15:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

