
最新发布第406页
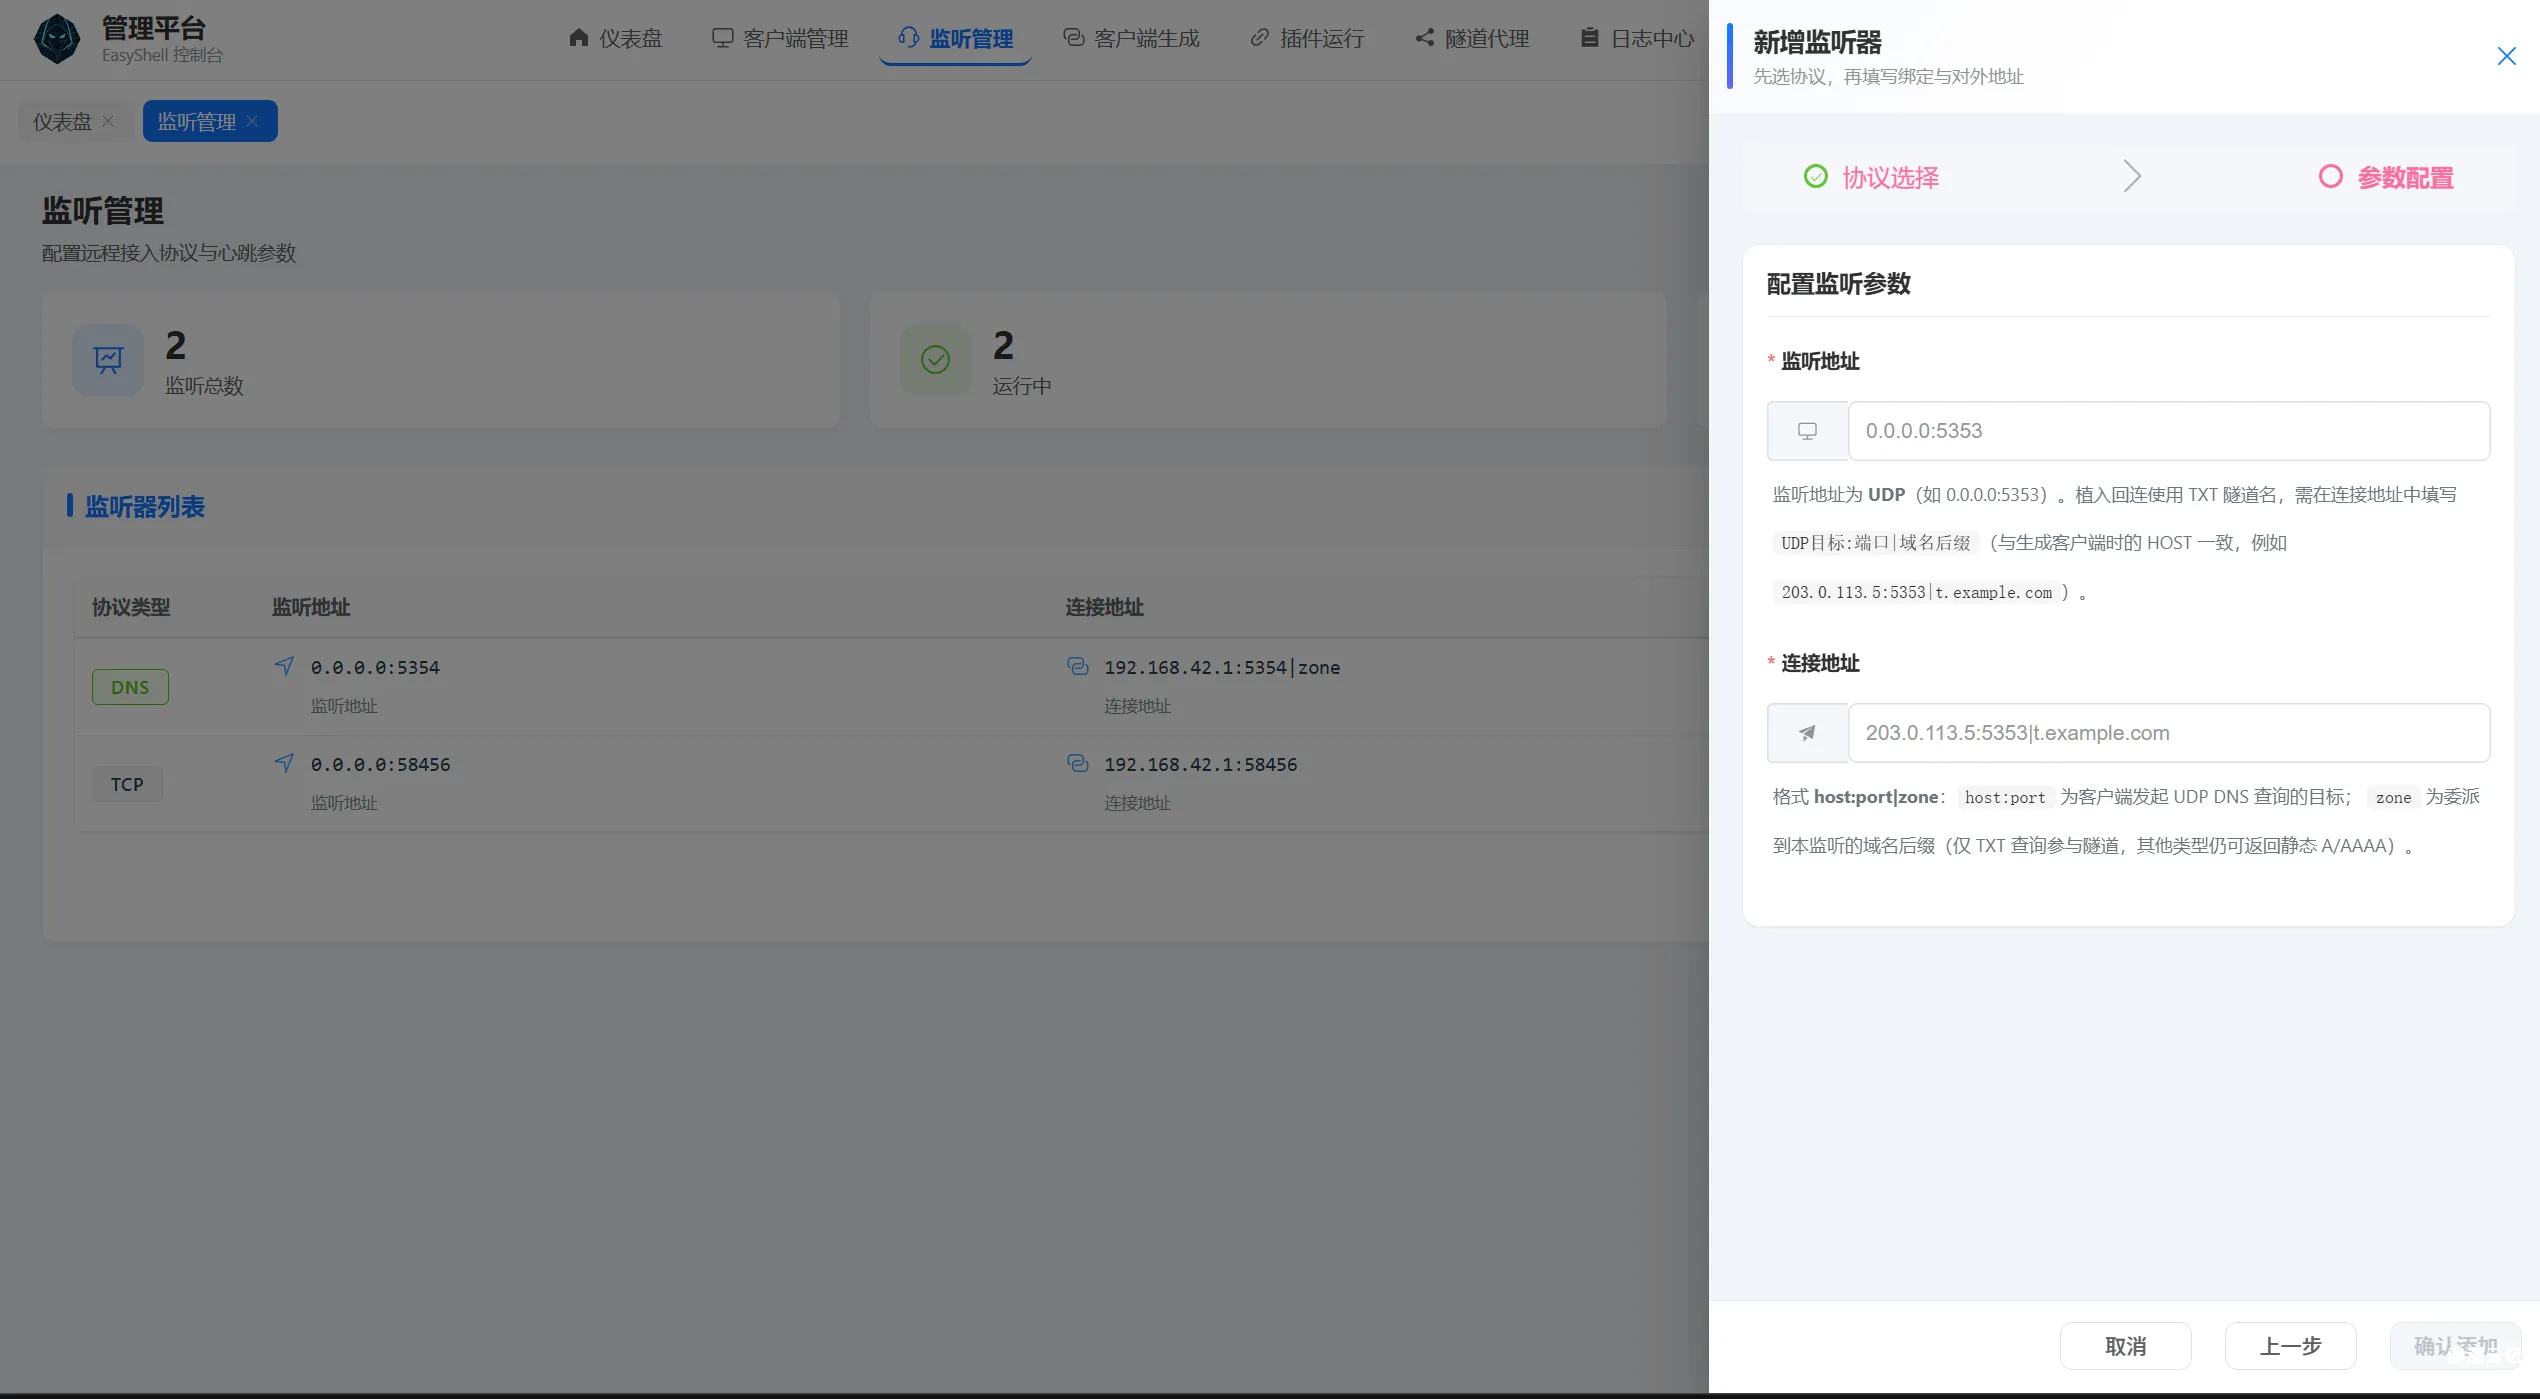
【工具更新】EasyShell v1.7版本更新,修复诸多bug,同时新增诸多新功能
前言 听人劝,吃饱饭,师傅们说啥我加啥,经过一段时间的更新,新版本的EasyShell出来了,修复了诸多bug,同时也新增了诸多功能,在此进行一个更新说明。 新增DNS监听协议,支持DNS协议上线 优...

 2026年5月22日 18:36
疑为俄罗斯背景的黑客组织长期攻击乌克兰关键机构
微软在近日发布的一篇关于ACTINIUM黑客组织的研究报告中表示,在过去的六个月中,微软威胁情报中心MSTIC观察到ACTINIUM针对乌克兰的政府、军事、司法、执法、非政府组织和非营利组织的一系列行...
 2022年3月10日 23:40
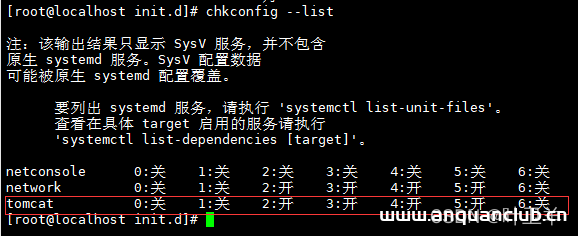
Linux系统设置tomcat开机自启介绍_Linux
大家好,本篇文章主要讲的是Linux系统设置tomcat开机自启介绍,感兴趣的同学赶快来看一看吧,对你有帮助的话记得收藏一下,方便下次浏览 1.进入到 /etc/init.d 目录中: cd /etc/init.d 2.创建 ...
2022年6月15日 08:45
bugbounty技巧聚合20220114
漏洞报告 【 Lark Technologies】[IDOR] 通过reminderId参数修改其他团队的提醒 http://hackerone.com/reports/946323 【Adobe】在配置文件中泄露 github 访问令牌 http://hackerone.com/report...
2022年3月10日 23:38
CVE-2023-44012: mojoPortal v.2.7.0.0 – Cross-Site Scripting
漏洞标题 CVE-2023-44012: mojoPortal v.2.7.0.0 - Cross-Site Scripting 漏洞描述 Cross Site Scripting vulnerability in mojoPortal v.2.7.0.0 allows a remote attacker to execute arbitra...
2023年1月9日 04:04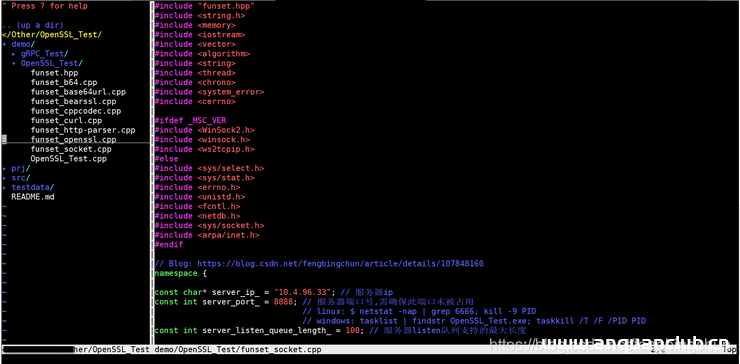
Ubuntu上Vim安装NERDTree插件的详细操作步骤_Linux
这篇文章主要介绍了Ubuntu上Vim安装NERDTree插件操作步骤,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 NERDTree是Vim的文件系统浏览器,使用此...
2023年7月20日 21:16CVE-2010-4769: Joomla! Component Jimtawl 1.0.2 – Local File Inclusion
漏洞标题 CVE-2010-4769: Joomla! Component Jimtawl 1.0.2 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Jimtawl (com_jimtawl) component 1.0.2 Joomla! all...
2010年7月4日 20:25CVE-2021-24875: WordPress eCommerce Product Catalog <3.0.39 - Cross-Site Scripting
漏洞标题 CVE-2021-24875: WordPress eCommerce Product Catalog <3.0.39 - Cross-Site Scripting 漏洞描述 WordPress eCommerce Product Catalog plugin before 3.0.39 contains a cross-si...
2021年5月26日 06:28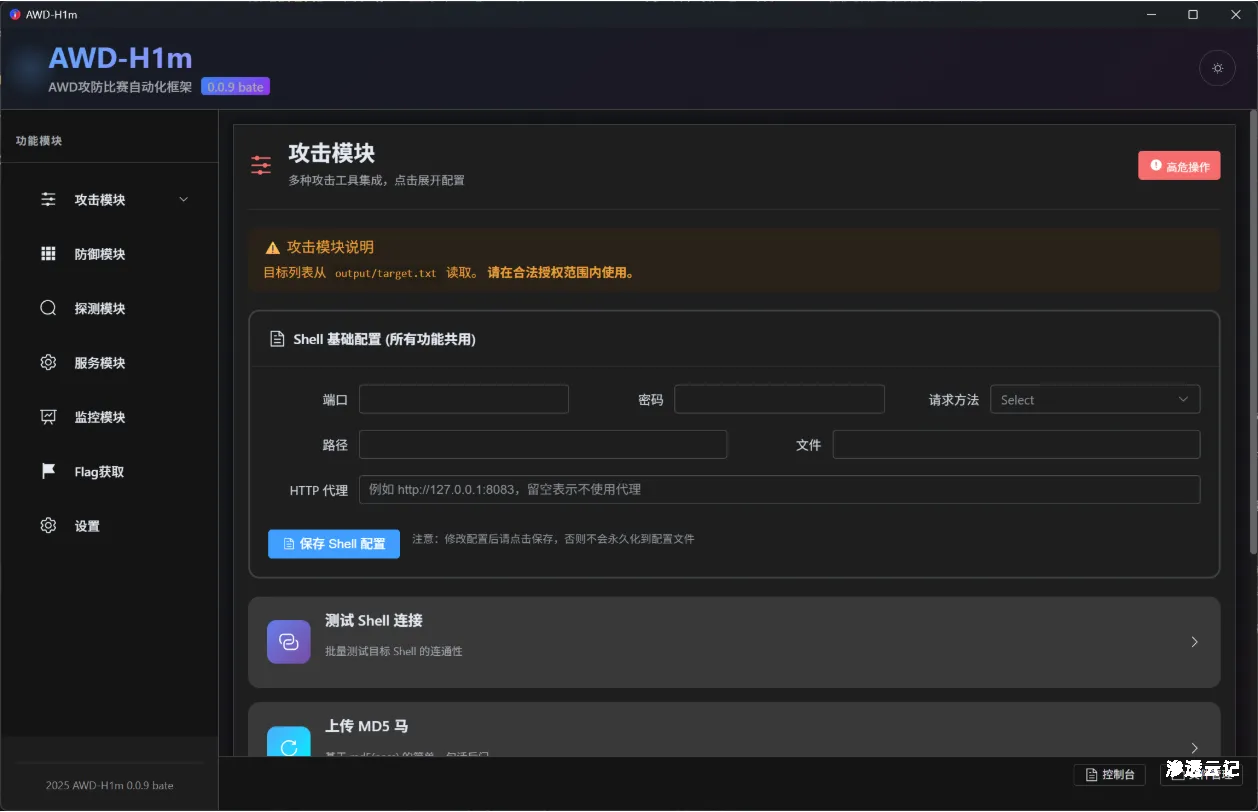
AWD-H1M-PRO -专为 CTF 设计的自动化 AWD 工具
项目介绍 AWD-H1m 是一款专为 CTF AWD (Attack With Defense) 赛制设计的桌面应用程序,帮助参赛选手在有限的比赛时间内高效完成攻击、防御、流量分析与 Flag 提交等核心任务。 在 AWD 竞赛中,...
2026年3月25日 22:03Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776)
漏洞标题 Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776) 漏洞描述 【漏洞对象】Apache Struts 2 【涉及版本】2.3-2.3.34,2.5-2.5.16 【漏洞描述】软件存在输入验证漏洞,远程攻击者可...
2018年1月26日 13:16Ubuntu12.04建立内核树实现过程详解_Linux
这篇文章主要介绍了Ubuntu12.04建立内核树实现过程详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 先查看自己使用的内核版本 lin@lin...
2023年5月19日 20:10CVE-2021-41381: Payara Micro Community 5.2021.6 Directory Traversal
漏洞标题 CVE-2021-41381: Payara Micro Community 5.2021.6 Directory Traversal 漏洞描述 Payara Micro Community 5.2021.6 and below contains a directory traversal vulnerability. PoC代...
2021年6月3日 22:11CVE-2022-41800: F5 BIG-IP Appliance Mode – Command Injection
漏洞标题 CVE-2022-41800: F5 BIG-IP Appliance Mode - Command Injection 漏洞描述 When running in Appliance mode, an authenticated user assigned the Administrator role may bypass Appl...
2022年3月11日 16:58CVE-2023-40753: PHPJabbers Ticket Support Script v3.2 – Cross-Site Scripting
漏洞标题 CVE-2023-40753: PHPJabbers Ticket Support Script v3.2 - Cross-Site Scripting 漏洞描述 There is a Cross Site Scripting (XSS) vulnerability in the message parameter of index...
2023年12月3日 23:57CVE-2022-42475: Fortinet SSL-VPN – Heap-Based Buffer Overflow
漏洞标题 CVE-2022-42475: Fortinet SSL-VPN - Heap-Based Buffer Overflow 漏洞描述 A heap-based buffer overflow vulnerability [CWE-122] in FortiOS SSL-VPN (versions 7.2.0 through 7.2....
2022年4月21日 03:29
nginx网站服务如何配置防盗链(推荐)_nginx
这篇文章主要介绍了nginx网站服务如何配置防盗链,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 一、盗链原理 1.1 网页准备 Web源主机(192.168....
2022年10月17日 21:55
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

