
最新发布第407页

spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+
漏洞标题 spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+ 漏洞描述 A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to rem...
 2022年12月7日 11:57
CVE-2021-43734: kkFileView getCorsFile 任意文件读取漏洞
漏洞标题 CVE-2021-43734: kkFileView getCorsFile 任意文件读取漏洞 漏洞描述 kkFileView getCorsFile 3.6.0 版本以下存在任意文件读取漏洞,攻击者通过漏洞可以获取服务器中的任意文件,获取...
2021年3月1日 11:02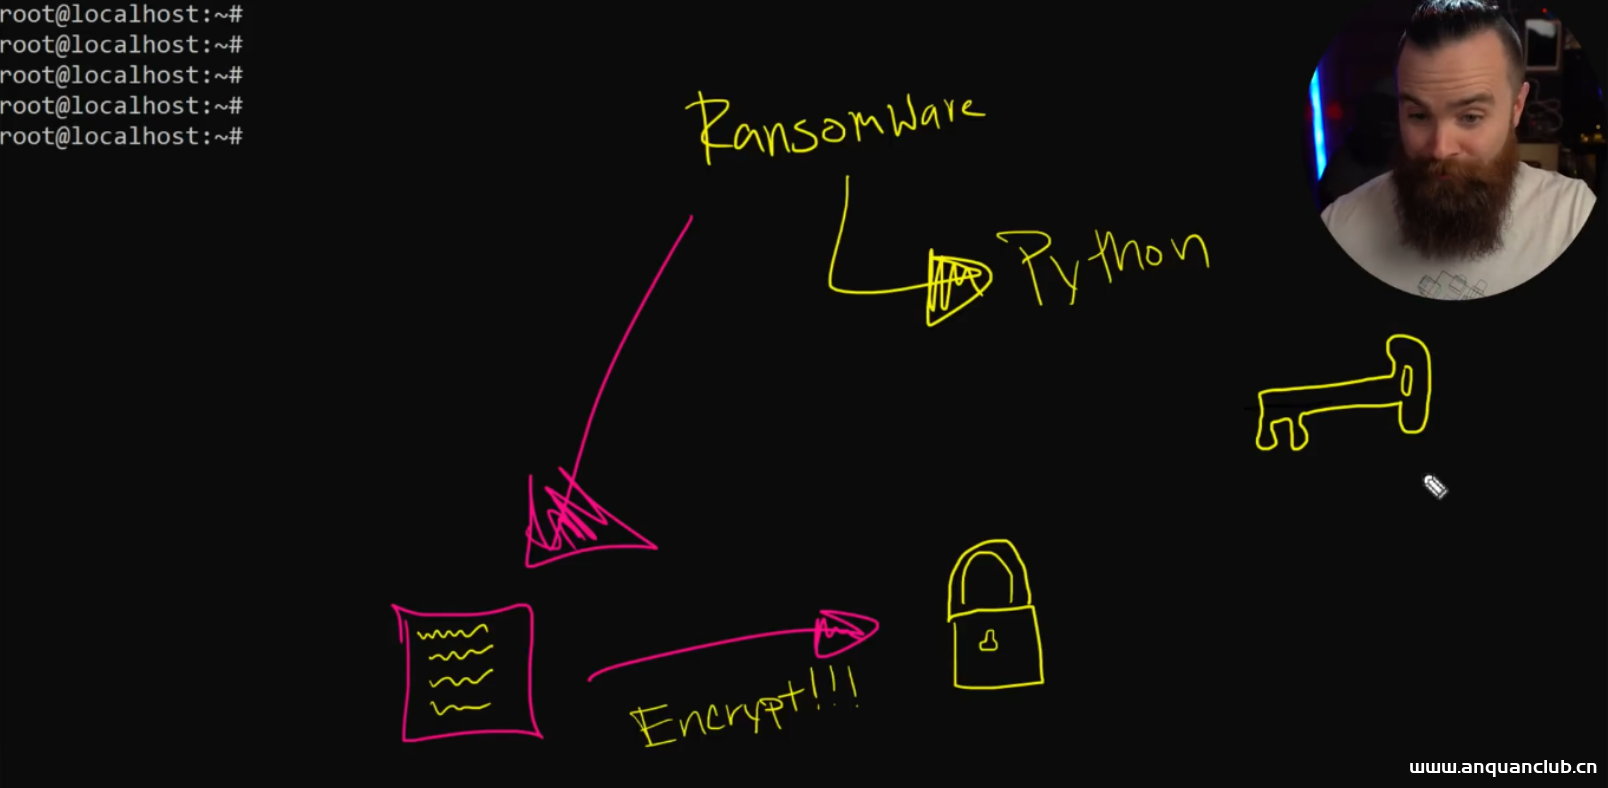
如何使用Python编写一个简单好玩的勒索程序?
相关阅读 图文讲解 原理分析 其实我们要写的脚本本质上就是一个加密程序,将文件内容通过Fernet算法进行加密,然后生成key,后面我们可以通过key在进行解密,这个过程是不是像极了勒索的场面…...

 2023年1月13日 19:56
CVE-2020-11738: WordPress Duplicator 1.3.24 & 1.3.26 – Local File Inclusion
漏洞标题 CVE-2020-11738: WordPress Duplicator 1.3.24 & 1.3.26 - Local File Inclusion 漏洞描述 WordPress Duplicator 1.3.24 & 1.3.26 are vulnerable to local file inclusion vu...
2020年6月15日 04:46CVE-2021-2135: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2021-2135: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Oracle WebLogic Server (12.2.1.3.0, 12.2.1.4.0, 14.1.1.0.0) contains a remote code execution caused ...
2021年1月8日 09:04CVE-2021-46073: Vehicle Service Management System 1.0 – Cross Site Scripting
漏洞标题 CVE-2021-46073: Vehicle Service Management System 1.0 - Cross Site Scripting 漏洞描述 Vehicle Service Management System 1.0 contains a cross-site scripting vulnerability v...
2021年4月22日 08:59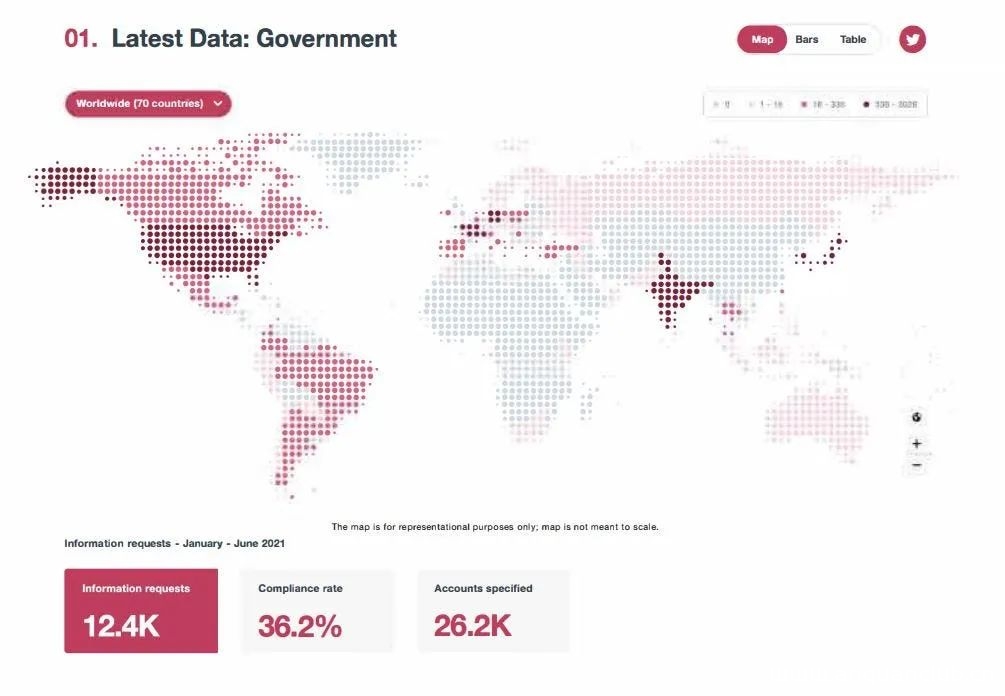
推特透明度报告:美国政府索要的信息最多
1月25日,推特Twitter透明度中心公布了一份透明度报告,以让用户了解世界范围内各国政府向他们提出的要求。 推特认为透明度有利于保护持续受到威胁的开放互联网,并且对于追究公司和政府的...
2022年3月10日 23:40CVE-2019-12989: Citrix SD-WAN and NetScaler SD-WAN – SQL Injection
漏洞标题 CVE-2019-12989: Citrix SD-WAN and NetScaler SD-WAN - SQL Injection 漏洞描述 Citrix SD-WAN 10.2.x before 10.2.3 and NetScaler SD-WAN 10.0.x before 10.0.8 contain an SQL inj...
2019年5月19日 09:10CVE-2022-1724: WordPress Simple Membership <4.1.1 - Cross-Site Scripting
漏洞标题 CVE-2022-1724: WordPress Simple Membership <4.1.1 - Cross-Site Scripting 漏洞描述 WordPress Simple Membership plugin before 4.1.1 contains a reflected cross-site script...
2022年3月15日 05:32CVE-2022-45808: LearnPress Plugin < 4.2.0 - Unauthenticated Time-Based Blind SQLi
漏洞标题 CVE-2022-45808: LearnPress Plugin < 4.2.0 - Unauthenticated Time-Based Blind SQLi 漏洞描述 SQL Injection vulnerability in LearnPress – WordPress LMS Plugin <= 4.1.7...
2022年3月7日 07:02CVE-2010-0982: Joomla! Component com_cartweberp – Local File Inclusion
漏洞标题 CVE-2010-0982: Joomla! Component com_cartweberp - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the CARTwebERP (com_cartweberp) component 1.56.75 fo...
2010年11月4日 15:36CVE-2018-20526: Roxy Fileman 1.4.5 – Unrestricted File Upload
漏洞标题 CVE-2018-20526: Roxy Fileman 1.4.5 - Unrestricted File Upload 漏洞描述 Roxy Fileman 1.4.5 is susceptible to unrestricted file upload via upload.php. An attacker can execut...
2018年4月1日 23:28CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop
漏洞标题 CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when using ...
2005年2月16日 08:14CVE-2018-10942: Prestashop AttributeWizardPro Module – Arbitrary File Upload
漏洞标题 CVE-2018-10942: Prestashop AttributeWizardPro Module - Arbitrary File Upload 漏洞描述 In the Attribute Wizard addon 1.6.9 for PrestaShop allows remote attackers to execute...
2018年6月18日 05:52CVE-2024-9014: pgAdmin 4 – Authentication Bypass
漏洞标题 CVE-2024-9014: pgAdmin 4 - Authentication Bypass 漏洞描述 pgAdmin 4 versions 8.11 and earlier are vulnerable to a security flaw in OAuth2 authentication. This vulnerabilit...
2024年7月24日 12:05CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect
漏洞标题 CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect 漏洞描述 WordPress Event Tickets < 5.2.2 is susceptible to an open redirect vulnerability. The plugin...
2021年12月27日 06:37
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

