
最新发布第415页

CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
 2019年8月15日 14:58
CVE-2022-30525: Zyxel Firewall – OS Command Injection
漏洞标题 CVE-2022-30525: Zyxel Firewall - OS Command Injection 漏洞描述 An OS command injection vulnerability in the CGI program of Zyxel USG FLEX 100(W) firmware versions 5.00 thr...
2022年2月7日 17:47CVE-2021-25003: WordPress WPCargo Track & Trace <6.9.0 - Remote Code Execution
漏洞标题 CVE-2021-25003: WordPress WPCargo Track & Trace <6.9.0 - Remote Code Execution 漏洞描述 WordPress WPCargo Track & Trace plugin before 6.9.0 is susceptible to re...
2021年11月16日 17:33CVE-2021-34427: Eclipse BIRT Viewer – Remote Code Execution
漏洞标题 CVE-2021-34427: Eclipse BIRT Viewer - Remote Code Execution 漏洞描述 Eclipse BIRT versions 4.8.0 and earlier contain a JSP injection caused by query parameters, letting re...
2021年7月8日 03:20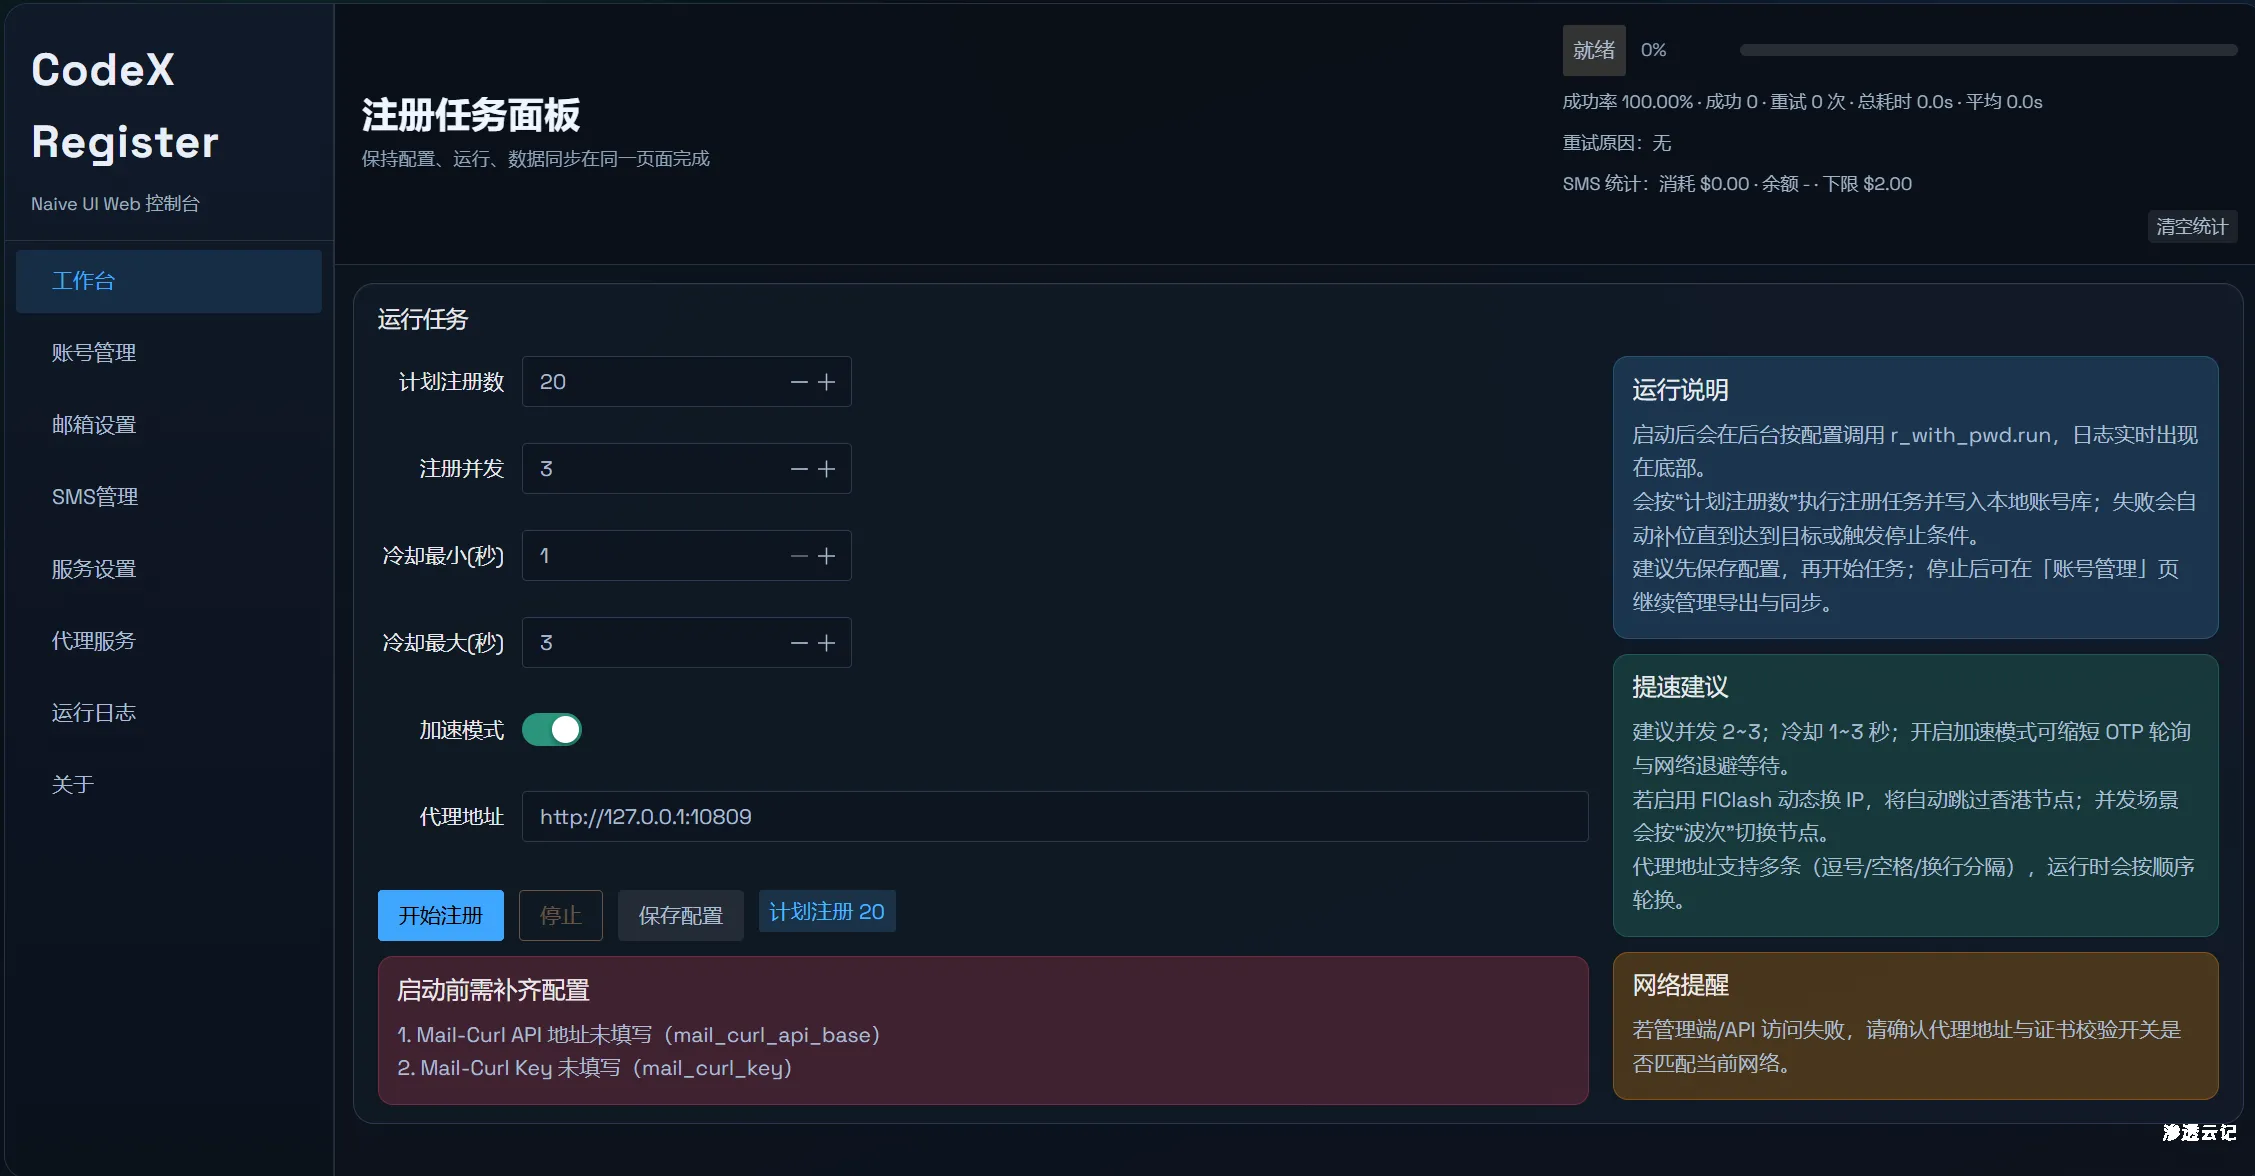
CodeX Register
CodeX Register 是一个本地桌面化控制台,用于统一执行注册流程、邮箱池管理、SMS 接码、代理切换、本地账号库管理、以及云端账号运维。 本项目由 GPT-5.3-Codex 辅助完成。 前端:Vue 3 + Naiv...

 2026年4月1日 22:20
CVE-2018-12300: Seagate NAS OS 4.3.15.1 – Open Redirect
漏洞标题 CVE-2018-12300: Seagate NAS OS 4.3.15.1 - Open Redirect 漏洞描述 Seagate NAS OS 4.3.15.1 contains an open redirect vulnerability in echo-server.html, which can allow an at...
2018年6月23日 12:57
[HCTF 2018]admin – buu刷题笔记
首先爬一遍整个网站,发现有没注册的时候有“login”,'register', 这两个页面,注册一个123用户登录后发现有 'index“,”post“,”logout“,”change password“这四个界面, 根据题目提示的a...
2022年4月17日 16:53CVE-2023-6549: Citrix Netscaler ADC & Gateway – Out-Of-Bounds Memory Read
漏洞标题 CVE-2023-6549: Citrix Netscaler ADC & Gateway - Out-Of-Bounds Memory Read 漏洞描述 The vulnerability would enable an attacker to remotely obtain sensitive information ...
2023年5月15日 10:30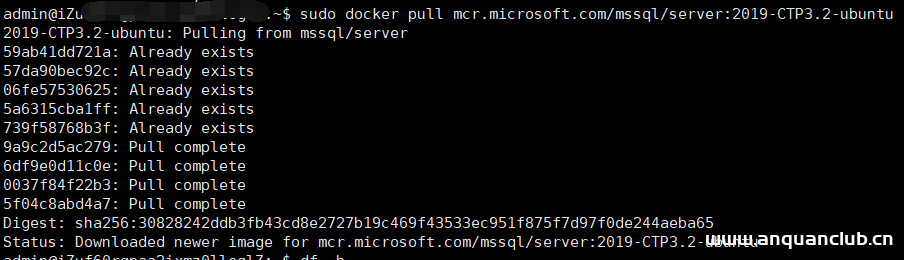
使用Docker运行SQL Server的实现_docker
这篇文章主要介绍了使用Docker运行SQL Server的实现,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 现在.net core...
2023年9月28日 20:20Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759)
漏洞标题 Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759) 漏洞描述 【漏洞描述】 Apache Tomcat JK(mod_jk) 【涉及版本】1.2.0,1.2.4 【漏洞描述】 由于Apache TomcatWeb服务器(...
2018年10月18日 07:45CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass
漏洞标题 CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass 漏洞描述 Kubernetes Dashboard before 1.10.1 allows attackers to bypass authentication and use Dashb...
2018年2月25日 04:28
给敏感信息打上马赛克就安全了吗?
我们在群聊发送图片、平台上传视频的时候,通常会对图片和视频的敏感信息进行处理,最常见的几种方式有马赛克、模糊、涂抹、黑条等,其中马赛克可以说是最为常见的一种。然而我们经常可以看到有...
2022年2月18日 18:20CVE-2021-25063: WordPress Contact Form 7 Skins <=2.5.0 - Cross-Site Scripting
漏洞标题 CVE-2021-25063: WordPress Contact Form 7 Skins <=2.5.0 - Cross-Site Scripting 漏洞描述 WordPress Contact Form 7 Skins plugin 2.5.0 and prior contains a reflected cross-...
2021年8月20日 09:56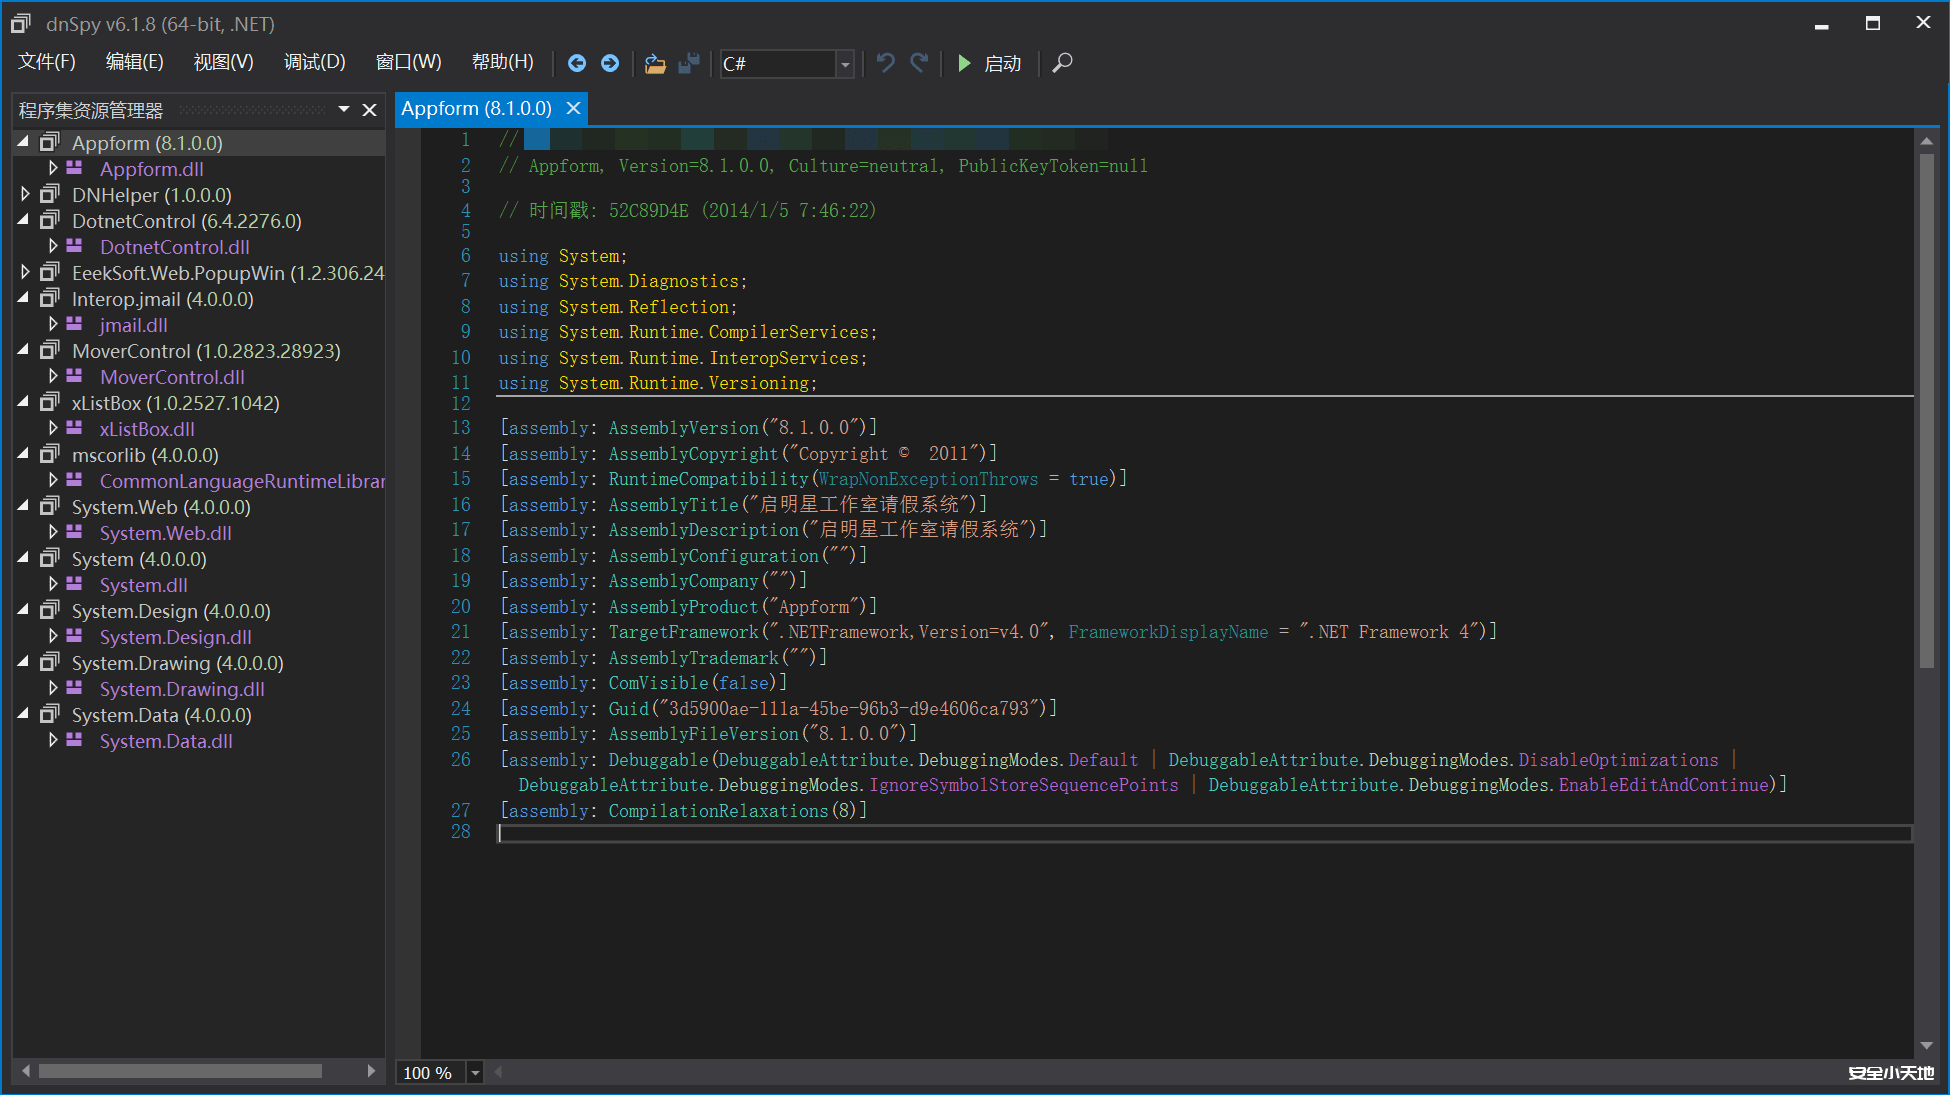
ASP.NET代码审计中常用的DLL反编译工具
前言 在针对ASP.NET开发的程序进行代码审计的时间,asp.net可以用C# ,VB.NET ,Jscript.net等等来开发,但是通常首选都是C#和VB.NET进行开发 审计ASP.NET的时候,首先得弄明白他的结构,他并不...
2024年3月3日 11:28CVE-2020-36728: WordPress Plugin Adning Advertising < 1.5.6 - Arbitrary File Upload
漏洞标题 CVE-2020-36728: WordPress Plugin Adning Advertising < 1.5.6 - Arbitrary File Upload 漏洞描述 The Adning Advertising plugin for WordPress versions below 1.5.6 is vulnera...
2020年2月18日 12:14CVE-2017-9791: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-9791: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.1.x and 2.3.x with the Struts 1 plugin might allow remote code execution via a malici...
2017年3月31日 09:24
2026年9月28日 11:45
2026年9月27日 11:45
2026年9月26日 11:45
2026年9月25日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

