
最新发布第419页

CVE-2019-2725: Oracle WebLogic Remote Code Execution
漏洞标题 CVE-2019-2725: Oracle WebLogic Remote Code Execution 漏洞描述 Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Services...
 2019年4月3日 07:40
CVE-2021-3017: Intelbras WIN 300/WRN 342 – Credentials Disclosure
漏洞标题 CVE-2021-3017: Intelbras WIN 300/WRN 342 - Credentials Disclosure 漏洞描述 Intelbras WIN 300 and WRN 342 devices through 2021-01-04 allows remote attackers to discover cre...
2021年8月3日 16:25CVE-2023-23488: WordPress Paid Memberships Pro <2.9.8 - Blind SQL Injection
漏洞标题 CVE-2023-23488: WordPress Paid Memberships Pro <2.9.8 - Blind SQL Injection 漏洞描述 WordPress Paid Memberships Pro plugin before 2.9.8 contains a blind SQL injection v...
2023年7月5日 06:13CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure 漏洞描述 DataEase, an open source data visualization and analysis tool, has a database configuration ...
2024年9月22日 09:49CVE-2017-9506: Atlassian Jira IconURIServlet – Cross-Site Scripting/Server-Side Request Forgery
漏洞标题 CVE-2017-9506: Atlassian Jira IconURIServlet - Cross-Site Scripting/Server-Side Request Forgery 漏洞描述 The Atlassian Jira IconUriServlet of the OAuth Plugin from version...
2017年6月6日 12:58CVE-2017-3528: Oracle E-Business Suite 12.1.3/12.2.x – Open Redirect
漏洞标题 CVE-2017-3528: Oracle E-Business Suite 12.1.3/12.2.x - Open Redirect 漏洞描述 The Oracle Applications Framework component of Oracle E-Business Suite (subcomponent: Popup w...
2017年12月13日 09:18CVE-2022-1221: WordPress Gwyn’s Imagemap Selector <=0.3.3 - Cross-Site Scripting
漏洞标题 CVE-2022-1221: WordPress Gwyn's Imagemap Selector <=0.3.3 - Cross-Site Scripting 漏洞描述 Wordpress Gwyn's Imagemap Selector plugin 0.3.3 and prior contains a...
2022年7月6日 02:49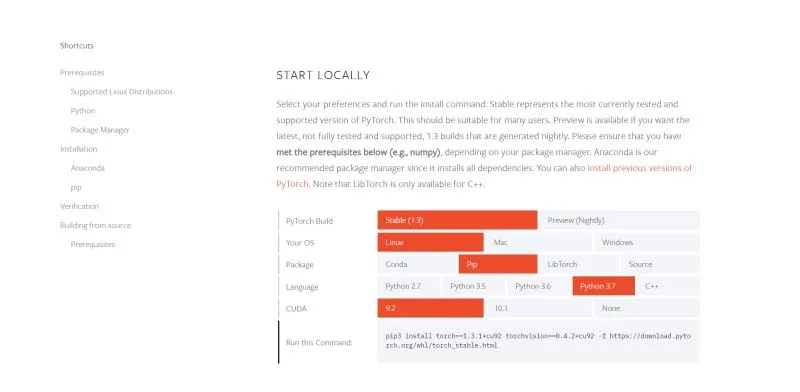
linux或windows环境下pytorch的安装与检查验证(解决runtimeerror问题)_Linux
这篇文章主要介绍了linux或windows环境下pytorch的安装与检查验证(解决runtimeerror问题),需要的朋友可以参考下 1、pytorch官网下载对应安装文件 http://pytorch.org/ 在getstarted处选择对应版...
2026年5月22日 11:45CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal
漏洞标题 CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal 漏洞描述 WordPress Backup Migration plugin versions up to 1.3.6 contain a path traversal and file va...
2023年1月5日 18:28CVE-2019-9881: WPEngine WPGraphQL 0.2.3 – Unauthenticated Comment Posting
漏洞标题 CVE-2019-9881: WPEngine WPGraphQL 0.2.3 - Unauthenticated Comment Posting 漏洞描述 The createComment mutation in the WPGraphQL 0.2.3 plugin for WordPress allows unauthenti...
2019年5月5日 15:55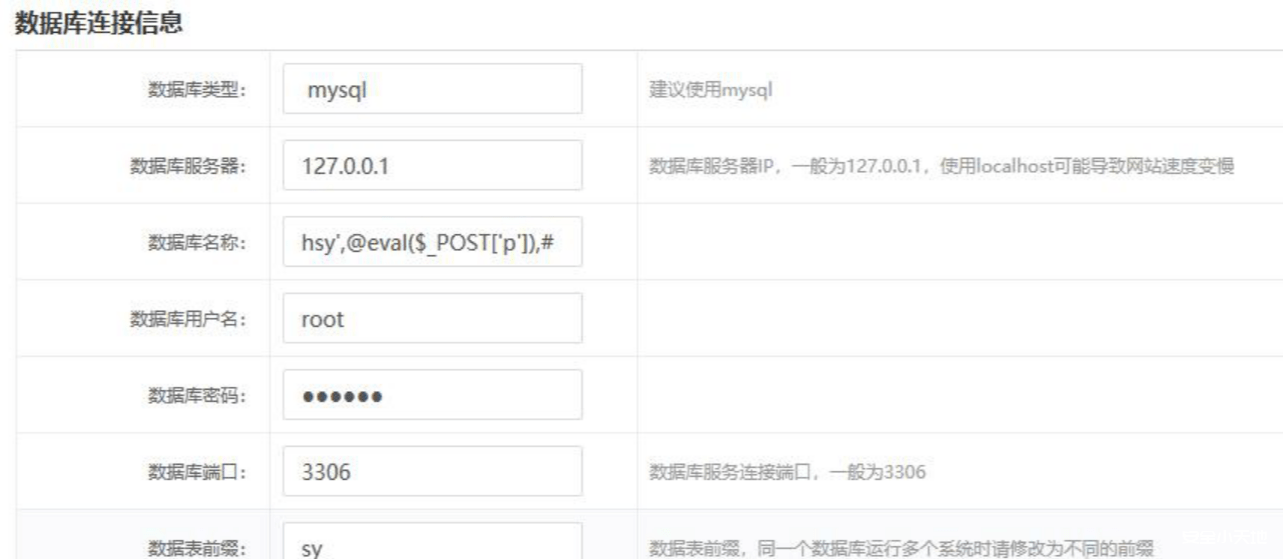
Hsycms2.0代码审计
前言 ThinkPHP 5 免费企业网站管理系统HSYCMS 带前后台是由好生意工作室开发的一款全新的企业站后台管理系统,网址URL全伪静态处理,网址简短,易于优化。 Hsycms 企业管理系统后台是作者...

 2023年6月9日 20:30

总结Linux 6种日志查看方法_Linux
在本篇文章里小编给大家整理的是关于Linux 6种日志查看方法,有需要的朋友们可以学习下。 作为一名后端程序员,和Linux打交道的地方很多,不会看Linux日志,非常容易受到来自同事和面试官的嘲讽...
2024年5月27日 21:37
deepin linux 手动升级内核的方法_Linux
这篇文章主要介绍了deepin linux 手动升级内核的方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 deepin和Ubun...
2026年3月26日 11:45CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit – Broken Access Control
漏洞标题 CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit - Broken Access Control 漏洞描述 The Recover WooCommerc...
2025年3月24日 22:07
[ACTF2020 新生赛]Upload – buu刷题笔记
[ACTF2020 新生赛]Upload 考点 前端后缀名绕过的方式 php可执行文件后缀名的种类主界面 有一个灯泡,提示你上传文件,前端有验证,只能上传 jpg|png|gif 这个时候我们有两种方式绕过前端验证 直...
2022年4月14日 20:02CVE-2023-23491: Quick Event Manager < 9.7.5 - Cross-Site Scripting
漏洞标题 CVE-2023-23491: Quick Event Manager < 9.7.5 - Cross-Site Scripting 漏洞描述 The Quick Event Manager WordPress Plugin, version < 9.7.5, is affected by a reflected cro...
2023年6月16日 12:30
2026年10月23日 11:45
2026年10月22日 11:46
2026年10月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

