
最新发布第421页

CVE-2020-2883: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2020-2883: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). S...
 2020年6月20日 23:10
CVE-2023-4111: PHPJabbers Bus Reservation System 1.1 – Cross-Site Scripting
漏洞标题 CVE-2023-4111: PHPJabbers Bus Reservation System 1.1 - Cross-Site Scripting 漏洞描述 A vulnerability was found in PHP Jabbers Bus Reservation System 1.1 and classified as ...
2023年6月22日 09:45
CVE-2020-11710: Kong API Gateway Unauthorized
漏洞标题 CVE-2020-11710: Kong API Gateway Unauthorized 漏洞描述 An issue was discovered in docker-kong (for Kong) through 2.0.3. The admin API port may be accessible on interfaces ...
2020年4月18日 02:04CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年6月10日 10:05Cisco RV132W RV134W 路由器信息泄露(CVE-2018-0127)
漏洞标题 Cisco RV132W RV134W 路由器信息泄露(CVE-2018-0127) 漏洞描述 Cisco RV132W ADSL2+Wireless-N VPN路由器和Cisco RV134W VDSL2 Wireless ACVPN路由器的web界面中存在漏洞,使得未经验...
2018年11月21日 21:14CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE
漏洞标题 CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE 漏洞描述 On BIG-IP versions 16.0.x before 16.0.1.1, 15.1.x before 15.1.2.1, 14.1.x before 14.1.4, 13.1.x before...
2021年3月6日 07:00
一款免费精品广告横幅在线制作网站
介绍 logo广告横幅在线生成网站源码,玩网必备,上传源码后解压访问即可,修改网站名信息在文件Config.php 内置10余中模板,也可以自己制作,方便简单 演示 源码下载 下载

 2023年1月18日 19:47
CVE-2021-27561: YeaLink DM 3.6.0.20 – Remote Command Injection
漏洞标题 CVE-2021-27561: YeaLink DM 3.6.0.20 - Remote Command Injection 漏洞描述 Yealink Device Management (DM) 3.6.0.20 allows command injection as root via the /sm/api/v1/firewal...
2021年3月7日 08:42CVE-2024-3080: ASUS DSL-AC88U – Authentication Bypass
漏洞标题 CVE-2024-3080: ASUS DSL-AC88U - Authentication Bypass 漏洞描述 A vulnerability in the ASUS DSL-AC88U router permits unauthorized individuals to bypass authentication.When ...
2024年6月20日 16:39CVE-2022-2379: WordPress Easy Student Results <=2.2.8 - Improper Authorization
漏洞标题 CVE-2022-2379: WordPress Easy Student Results <=2.2.8 - Improper Authorization 漏洞描述 WordPress Easy Student Results plugin through 2.2.8 is susceptible to informatio...
2022年9月20日 16:55CVE-2021-39146: XStream 1.4.18 – Arbitrary Code Execution
漏洞标题 CVE-2021-39146: XStream 1.4.18 - Arbitrary Code Execution 漏洞描述 XStream 1.4.18 is susceptible to remote code execution. An attacker can execute commands of the host by ...
2021年6月24日 02:00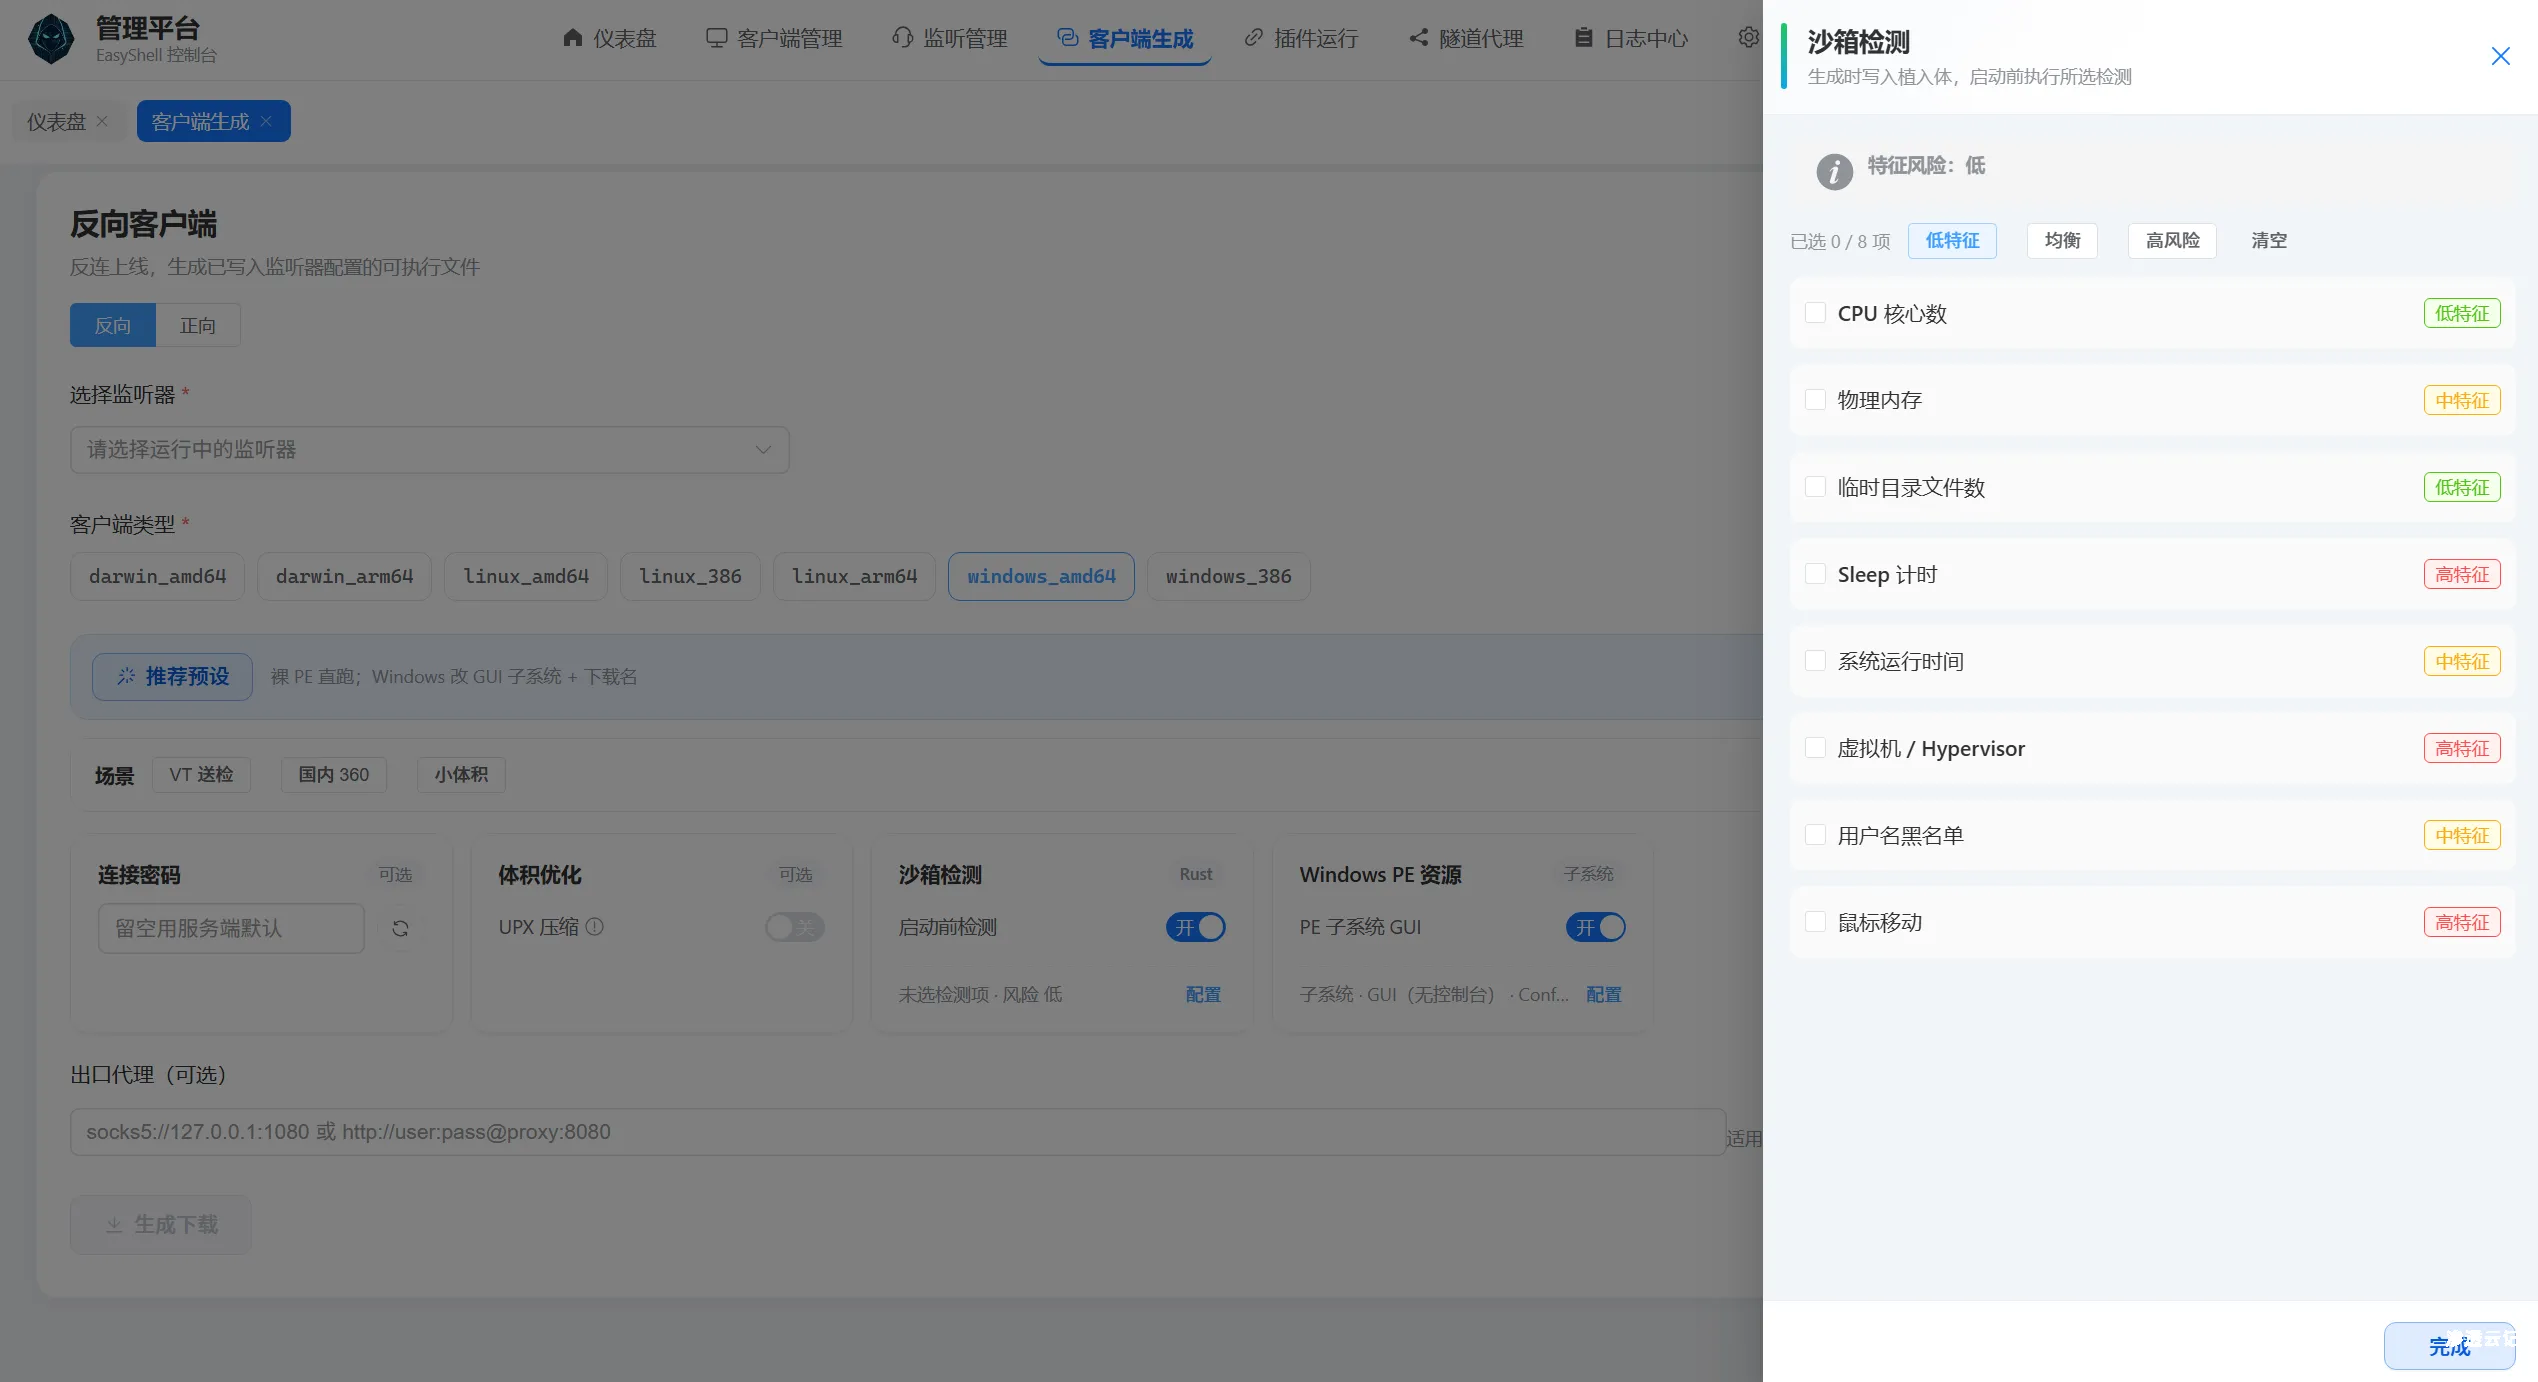
【工具更新】EasyShell v1.8版本更新,重构客户端,减小体积的同时增强免杀效果
前言 经过仔细思考,还是使用rust将客户端进行完整重构了一般,现在构建文件由原来的go(win)的10m压缩至2m,upx压缩之后只有700kb,虽然比不上完全由c/c#实现的客户端吧,但是也还是可以接受...
2026年5月29日 22:08CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年3月14日 09:20CVE-2024-51228: TOTOLINK CX-A3002RU – Remote Code Execution
漏洞标题 CVE-2024-51228: TOTOLINK CX-A3002RU - Remote Code Execution 漏洞描述 An issue in TOTOLINK-CX-A3002RU V1.0.4-B20171106.1512 and TOTOLINK-CX-N150RT V2.1.6-B20171121.1002 and...
2024年10月9日 23:37CVE-2021-3122: NCR Command Center Agent 16.3 – Remote Command Execution
漏洞标题 CVE-2021-3122: NCR Command Center Agent 16.3 - Remote Command Execution 漏洞描述 CMCAgent in NCR Command Center Agent 16.3 on Aloha POS/BOH servers permits the submission ...
2021年6月17日 16:46
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

