
最新发布第426页

CVE-2022-2187: WordPress Contact Form 7 Captcha <0.1.2 - Cross-Site Scripting
漏洞标题 CVE-2022-2187: WordPress Contact Form 7 Captcha <0.1.2 - Cross-Site Scripting 漏洞描述 WordPress Contact Form 7 Captcha plugin before 0.1.2 contains a reflected cross-s...
 2022年9月15日 20:02
CVE-2020-35847: Agentejo Cockpit <0.11.2 - NoSQL Injection
漏洞标题 CVE-2020-35847: Agentejo Cockpit <0.11.2 - NoSQL Injection 漏洞描述 Agentejo Cockpit before 0.11.2 allows NoSQL injection via the Controller/Auth.php resetpassword func...
2020年8月1日 03:07CVE-2024-7029: AVTECH IP Camera – Command Injection
漏洞标题 CVE-2024-7029: AVTECH IP Camera - Command Injection 漏洞描述 The endpoint `/cgi-bin/supervisor/Factory.cgi` is vulnerable to command injection via the `action` parameter, ...
2024年7月11日 16:06CVE-2024-51228: TOTOLINK CX-A3002RU – Remote Code Execution
漏洞标题 CVE-2024-51228: TOTOLINK CX-A3002RU - Remote Code Execution 漏洞描述 An issue in TOTOLINK-CX-A3002RU V1.0.4-B20171106.1512 and TOTOLINK-CX-N150RT V2.1.6-B20171121.1002 and...
2024年10月26日 05:09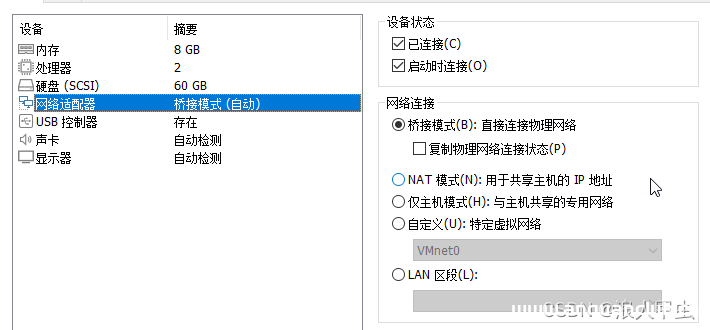
自建FTP和SFTP服务器过程介绍_Linux
大家好,本篇文章主要讲的是自建FTP和SFTP服务器过程介绍,感兴趣的同学赶快来看一看吧,对你有帮助的话记得收藏一下,方便下次浏览 FTP、SFTP作为文件传输协议,使用广泛。为进行相关的功能开...
2022年6月15日 08:45CVE-2022-42475: Fortinet SSL-VPN – Heap-Based Buffer Overflow
漏洞标题 CVE-2022-42475: Fortinet SSL-VPN - Heap-Based Buffer Overflow 漏洞描述 A heap-based buffer overflow vulnerability [CWE-122] in FortiOS SSL-VPN (versions 7.2.0 through 7.2....
2022年9月26日 01:23CVE-2021-3223: Node RED Dashboard – Directory Traversal
漏洞标题 CVE-2021-3223: Node RED Dashboard - Directory Traversal 漏洞描述 Node-RED-Dashboard before 2.26.2 allows ui_base/js/..%2f directory traversal to read files. PoC代码
2021年7月14日 13:11CVE-2021-25099: WordPress GiveWP <2.17.3 - Cross-Site Scripting
漏洞标题 CVE-2021-25099: WordPress GiveWP <2.17.3 - Cross-Site Scripting 漏洞描述 WordPress GiveWP plugin before 2.17.3 contains a cross-site scripting vulnerability. The plugin...
2021年8月30日 16:08
西方最大轮胎制造商普利司通遭勒索软件攻击,攻击者自称无政治立场
普利司通是世界最知名的轮胎制造商之一,在美洲拥有50多家生产工厂和55000名员工。近日,该公司确认遭到Lockbit勒索软件攻击,重要数据遭窃。Lockbit勒索软件团伙威胁普利司通在2022年3月15日23...
2022年3月16日 09:16CVE-2022-0826: WordPress WP Video Gallery <=1.7.1 - SQL Injection
漏洞标题 CVE-2022-0826: WordPress WP Video Gallery <=1.7.1 - SQL Injection 漏洞描述 WordPress WP Video Gallery plugin through 1.7.1 contains a SQL injection vulnerability. The p...
2022年10月27日 12:42CVE-2024-54763: ipTIME A2004 – Unauthorized Access
漏洞标题 CVE-2024-54763: ipTIME A2004 - Unauthorized Access 漏洞描述 An access control issue in the component /login/hostinfo.cgi of ipTIME A2004 v12.17.0 allows attackers to obtai...
2024年5月25日 15:23
BUUCTF:[BUUCTF 2018]Online Tool – buu刷题笔记
打开可以看见是代码审计,我们看看代码 <?php if (isset($_SERVER['HTTP_X_FORWARDED_FOR'])) { $_SERVER['REMOTE_ADDR'] = $_SERVER['HTTP_X_FORWARDED_FOR']; } if(!isset($_GET['host']))...

 2022年6月2日 17:42
CVE-2020-19283: Jeesns 1.4.2 – Cross-Site Scripting
漏洞标题 CVE-2020-19283: Jeesns 1.4.2 - Cross-Site Scripting 漏洞描述 Jeesns 1.4.2 is vulnerable to reflected cross-site scripting in the /newVersion component and allows attackers...
2020年8月26日 13:37CVE-2021-24970: WordPress All-In-One Video Gallery <2.5.0 - Local File Inclusion
漏洞标题 CVE-2021-24970: WordPress All-In-One Video Gallery <2.5.0 - Local File Inclusion 漏洞描述 WordPress All-in-One Video Gallery plugin before 2.5.0 is susceptible to local...
2021年5月4日 06:53CVE-2025-32815: NetMRI < 7.6.1 - Authentication Bypass via Hardcoded Credentials
漏洞标题 CVE-2025-32815: NetMRI < 7.6.1 - Authentication Bypass via Hardcoded Credentials 漏洞描述 An issue was discovered in Infoblox NETMRI before 7.6.1. Authentication Bypass...
2025年7月16日 20:32CVE-2022-22963: Spring Cloud – Remote Code Execution
漏洞标题 CVE-2022-22963: Spring Cloud - Remote Code Execution 漏洞描述 Spring Cloud Function versions 3.1.6, 3.2.2 and older unsupported versions are susceptible to remote code exe...
2022年7月23日 05:11
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

