
最新发布第429页

CVE-2021-25282: SaltStack Salt Unautherenticated Remote Command Execution
漏洞标题 CVE-2021-25282: SaltStack Salt Unautherenticated Remote Command Execution 漏洞描述 An issue was discovered in through SaltStack Salt before 3002.5. The salt.wheel.pillar_r...
 2021年6月26日 11:29
CVE-2020-29453: Jira Server Pre-Auth – Arbitrary File Retrieval (WEB-INF, META-INF)
漏洞标题 CVE-2020-29453: Jira Server Pre-Auth - Arbitrary File Retrieval (WEB-INF, META-INF) 漏洞描述 The CachingResourceDownloadRewriteRule class in Jira Server and Jira Data Cent...
2020年5月26日 22:38CVE-2023-40931: Nagios XI v5.11.0 – SQL Injection
漏洞标题 CVE-2023-40931: Nagios XI v5.11.0 - SQL Injection 漏洞描述 A SQL injection vulnerability in Nagios XI from version 5.11.0 up to and including 5.11.1 allows authenticated a...
2023年12月12日 11:49CVE-2022-1388: F5 BIG-IP iControl – REST Auth Bypass RCE
漏洞标题 CVE-2022-1388: F5 BIG-IP iControl - REST Auth Bypass RCE 漏洞描述 F5 BIG-IP 16.1.x versions prior to 16.1.2.2, 15.1.x versions prior to 15.1.5.1, 14.1.x versions prior to ...
2022年1月2日 20:28CVE-2024-9487: GitHub Enterprise – SAML Authentication Bypass
漏洞标题 CVE-2024-9487: GitHub Enterprise - SAML Authentication Bypass 漏洞描述 An improper verification of cryptographic signature vulnerability was identified in GitHub Enterpris...
2024年7月14日 18:42CVE-2022-31846: WAVLINK WN535 G3 – Information Disclosure
漏洞标题 CVE-2022-31846: WAVLINK WN535 G3 - Information Disclosure 漏洞描述 WAVLINK WN535 G3 M35G3R.V5030.180927 is susceptible to information disclosure in the live_mfg.shtml page...
2022年10月12日 09:15CVE-2024-6555: WP Popups – Information Disclosure
漏洞标题 CVE-2024-6555: WP Popups - Information Disclosure 漏洞描述 WP Popups - WordPress Popup builder plugin for WordPress contains a full path disclosure caused by using mobiled...
2024年6月3日 18:46
再分享6个可无限激活阿里云盘邀请码,不信你不能激活阿里云盘_云其它
这篇文章主要分享6个可无限激活的阿里云盘邀请码,不信你不能激活阿里云盘,需要的朋友可以参考下 阿里云盘距离上次更新已过去不少时间了,据网友反应已经有部分前期参加“个人种子”活动的用户...
2023年1月31日 20:05CVE-2022-2488: Wavlink WN535K2/WN535K3 – OS Command Injection
漏洞标题 CVE-2022-2488: Wavlink WN535K2/WN535K3 - OS Command Injection 漏洞描述 Wavlink WN535K2 and WN535K3 routers are susceptible to OS command injection in /cgi-bin/touchlist_sy...
2022年12月27日 08:45CVE-2023-33405: BlogEngine CMS – Open Redirect
漏洞标题 CVE-2023-33405: BlogEngine CMS - Open Redirect 漏洞描述 Blogengine.net 3.3.8.0 and earlier is vulnerable to Open Redirect PoC代码
2023年1月16日 10:23Citrix System SDWAN WAN-OP 权限绕过漏洞(CVE-2020-8193)
漏洞标题 Citrix System SDWAN WAN-OP 权限绕过漏洞(CVE-2020-8193) 漏洞描述 Citrix Systems Citrix System SDWAN WAN-OP是美国思杰系统(Citrix Systems)公司的一款SD-WAN(虚拟软件定义的...
2020年6月18日 15:22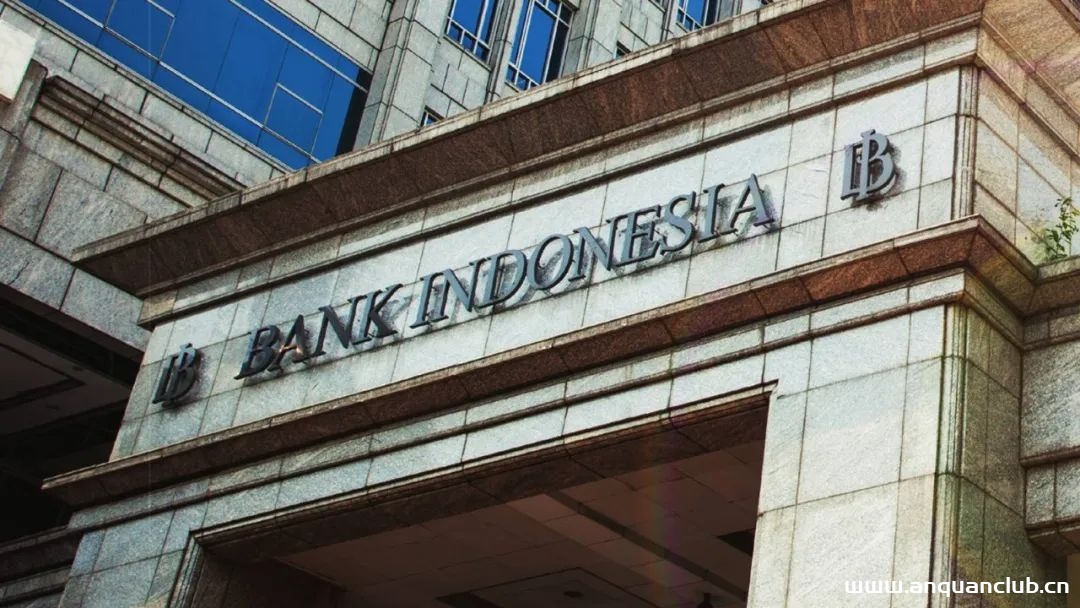
印尼央行确认遭受勒索软件攻击
1月20日,印度尼西亚共和国中央银行——印度尼西亚银行(BANK INDONESIA)通信部执行主任Erwin Haryono证实,银行于上个月遭受了勒索软件攻击。中央银行有着管理货币部门、维持支付系统和金融系...
2022年3月10日 23:34CVE-2017-9506: Atlassian Jira IconURIServlet – Cross-Site Scripting/Server-Side Request Forgery
漏洞标题 CVE-2017-9506: Atlassian Jira IconURIServlet - Cross-Site Scripting/Server-Side Request Forgery 漏洞描述 The Atlassian Jira IconUriServlet of the OAuth Plugin from version...
2017年9月26日 14:25CVE-2010-3426: Joomla! Component Jphone 1.0 Alpha 3 – Local File Inclusion
漏洞标题 CVE-2010-3426: Joomla! Component Jphone 1.0 Alpha 3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in jphone.php in the JPhone (com_jphone) component ...
2010年1月9日 12:41CVE-2019-6802: Pypiserver <1.2.5 - Carriage Return Line Feed Injection
漏洞标题 CVE-2019-6802: Pypiserver <1.2.5 - Carriage Return Line Feed Injection 漏洞描述 Pypiserver through 1.2.5 and below is susceptible to carriage return line feed injection...
2019年6月29日 04:58CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
2024年6月26日 14:35
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

