
最新发布第429页

CVE-2021-31755: Tenda Router AC11 – Remote Command Injection
漏洞标题 CVE-2021-31755: Tenda Router AC11 - Remote Command Injection 漏洞描述 Tenda Router AC11 is susceptible to remote command injection vulnerabilities in the web-based managem...
 2021年3月20日 18:13
CVE-2021-33221: CommScope Ruckus IoT Controller – Information Disclosure
漏洞标题 CVE-2021-33221: CommScope Ruckus IoT Controller - Information Disclosure 漏洞描述 CommScope Ruckus IoT Controller is susceptible to information disclosure vulnerabilities ...
2021年7月12日 01:52CVE-2021-38146: Wipro Holmes Orchestrator 20.4.1 – Arbitrary File Download
漏洞标题 CVE-2021-38146: Wipro Holmes Orchestrator 20.4.1 - Arbitrary File Download 漏洞描述 The File Download API in Wipro Holmes Orchestrator 20.4.1 (20.4.1_02_11_2020) allows re...
2021年1月12日 19:09CVE-2022-1574: WordPress HTML2WP <=1.0.0 - Arbitrary File Upload
漏洞标题 CVE-2022-1574: WordPress HTML2WP <=1.0.0 - Arbitrary File Upload 漏洞描述 WordPress HTML2WP plugin through 1.0.0 contains an arbitrary file upload vulnerability. The pl...
2022年12月16日 16:10CVE-2025-31324: SAP NetWeaver Visual Composer Metadata Uploader – Deserialization
漏洞标题 CVE-2025-31324: SAP NetWeaver Visual Composer Metadata Uploader - Deserialization 漏洞描述 SAP NetWeaver Visual Composer Metadata Uploader is not protected with a proper a...
2025年5月31日 20:10CVE-2019-11886: Yellow Pencil Visual Theme Customizer < 7.2.1 - Privilege Escalation
漏洞标题 CVE-2019-11886: Yellow Pencil Visual Theme Customizer < 7.2.1 - Privilege Escalation 漏洞描述 The WaspThemes Visual CSS Style Editor (aka yellow-pencil-visual-theme-cus...
2019年10月24日 06:19CVE-2020-17453: WSO2 Carbon Management Console <=5.10 - Cross-Site Scripting
漏洞标题 CVE-2020-17453: WSO2 Carbon Management Console <=5.10 - Cross-Site Scripting 漏洞描述 WSO2 Management Console through 5.10 is susceptible to reflected cross-site script...
2020年10月7日 06:00CVE-2021-21801: Advantech R-SeeNet – Cross-Site Scripting
漏洞标题 CVE-2021-21801: Advantech R-SeeNet - Cross-Site Scripting 漏洞描述 Advantech R-SeeNet contains a cross-site scripting vulnerability in the device_graph_page.php script via...
2021年7月21日 07:29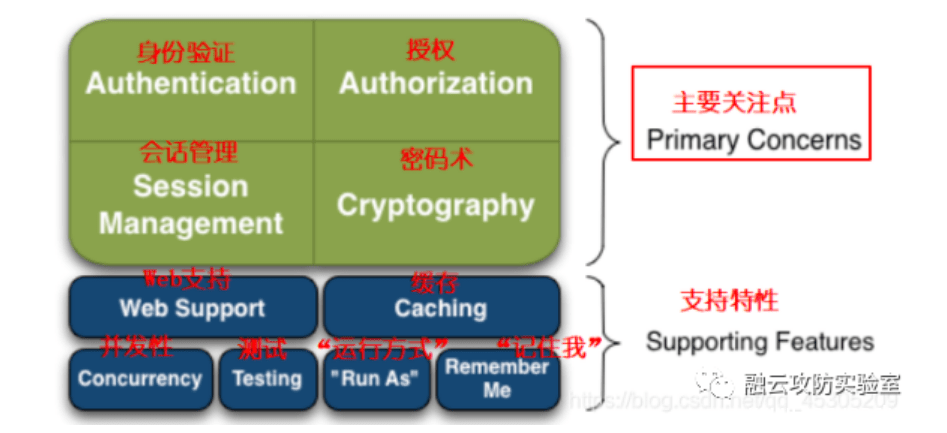
CVE-2016-4437 Shiro1.2.4反序列化漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 CVE-2016-4437 Shiro1.2.4反序列化漏洞 ApacheShiro是一款开源安全框架,提供身份验证、授权、密码学和会话管理。Shiro框架直观、易用...
2023年2月13日 13:51CVE-2024-7339: TVT DVR Sensitive Device – Information Disclosure
漏洞标题 CVE-2024-7339: TVT DVR Sensitive Device - Information Disclosure 漏洞描述 A vulnerability has been found in TVT DVR TD-2104TS-CL, DVR TD-2108TS-HP, Provision-ISR DVR SH-40...
2024年6月26日 20:52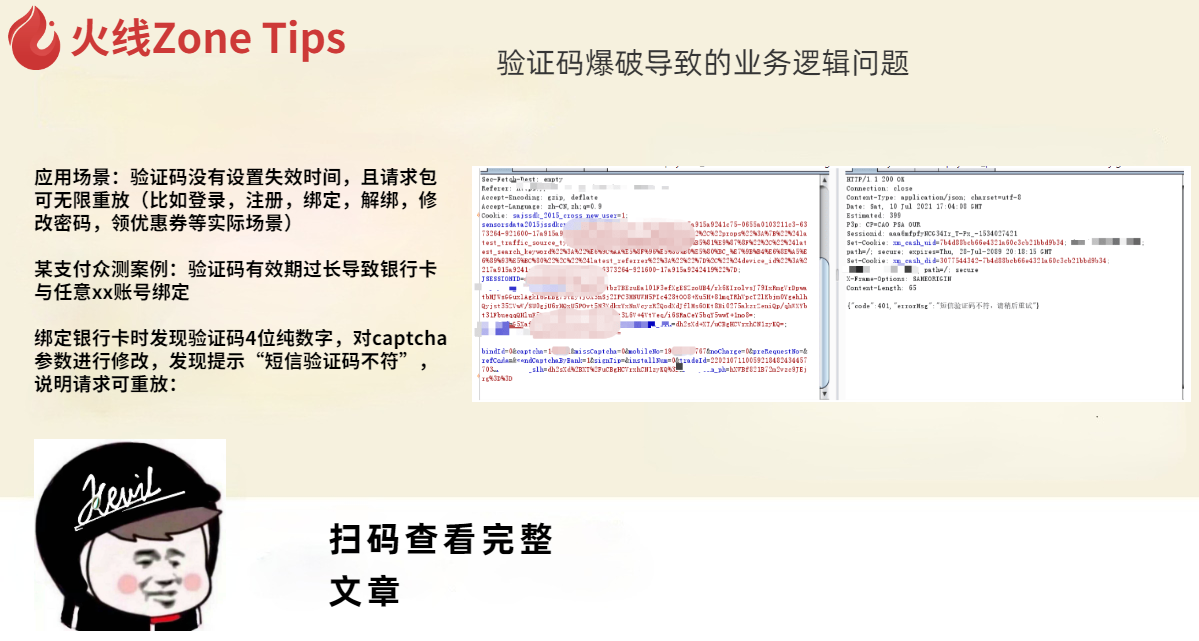
验证码爆破导致的业务逻辑问题
应用场景:验证码没有设置失效时间,且请求包可无限重放(比如登录,注册,绑定,解绑,修改密码,领优惠券等实际场景) 某支付众测案例:验证码有效期过长导致银行卡与任意xx账号绑定 绑定银行...
2022年3月10日 23:37
src中遇到的未授权挖掘分享
1.扫描子域名直接访问成功的未授权(spring、swagger-ui、rocketMQ、telescope等等) 2.在登陆页面,通过查看js文件查找api接口拼接路径成功的未授权 3.Shiro在每个接口前加上分号 /;/绕过拼接路...
2022年3月10日 23:34CVE-2023-27624: WordPress Redirect After Login <= 0.1.9 - Admin Stored XSS
漏洞标题 CVE-2023-27624: WordPress Redirect After Login <= 0.1.9 - Admin Stored XSS 漏洞描述 Marcelotorres Redirect After Login plugin <= 0.1.9 contains a stored cross-site s...
2023年5月4日 06:38CVE-2017-18557: Google Maps by BestWebSoft < 1.3.6 - Cross-Site Scripting
漏洞标题 CVE-2017-18557: Google Maps by BestWebSoft < 1.3.6 - Cross-Site Scripting 漏洞描述 The bws-google-maps plugin before 1.3.6 for WordPress has multiple XSS issues. PoC代...
2017年11月6日 14:55CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS
漏洞标题 CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS 漏洞描述 FileZilla Server versions prior to 0.9.31 contain a buffer overflow vulnerability relate...
2009年10月11日 03:07CVE-2022-41840: Welcart eCommerce <= 2.7.7 - Unauth Directory Traversal
漏洞标题 CVE-2022-41840: Welcart eCommerce <= 2.7.7 - Unauth Directory Traversal 漏洞描述 Unauth. Directory Traversal vulnerability in Welcart eCommerce plugin <= 2.7.7 on Wo...
2022年9月23日 14:47
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

