
最新发布第434页

CVE-2022-43769: Hitachi Pentaho Business Analytics Server – Remote Code Execution
漏洞标题 CVE-2022-43769: Hitachi Pentaho Business Analytics Server - Remote Code Execution 漏洞描述 Hitachi Pentaho Business Analytics Server prior to versions 9.4.0.1 and 9.3.0.2,...
 2022年2月3日 02:54
最新AWVS14.8.220606174破解版,支持windows
更新支持 新增漏洞检测 新的漏洞检测Confluence 服务器和数据中心中的未经身份验证的远程代码执行漏洞( CVE-2022-26134 ) 提供版本 Windows 工具下载 AWVS14.8.220606174下载 提取码...

 2026年3月15日 12:27
CVE-2020-14750: Oracle WebLogic Server – Remote Command Execution
漏洞标题 CVE-2020-14750: Oracle WebLogic Server - Remote Command Execution 漏洞描述 Oracle WebLogic Server 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0 is suscepti...
2020年10月5日 18:04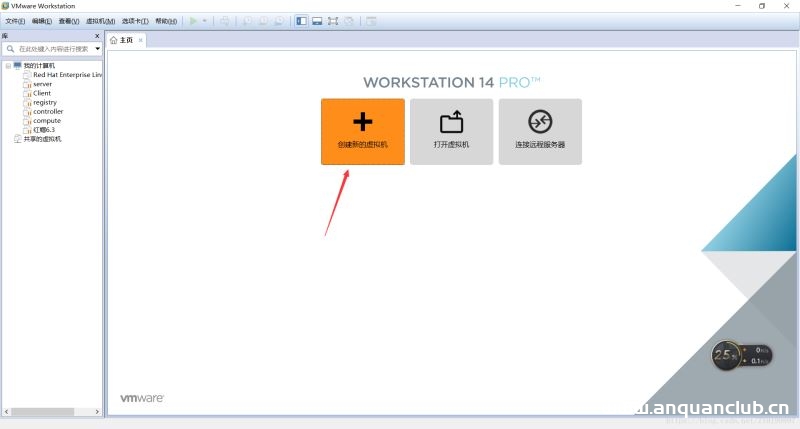
从零开始安装VMwareTools的详细步骤(图文教程)_VMware
这篇文章主要介绍了从零开始安装VMwareTools的详细步骤,小编觉得挺不错的,现在分享给大家,也给大家做个参考。一起跟随小编过来看看吧 VMware Tools是VMware虚拟机中自带的一种工具,相当于Vi...
2024年4月11日 20:49CVE-2022-0783: Multiple Shipping Address Woocommerce < 2.0 - SQL Injection
漏洞标题 CVE-2022-0783: Multiple Shipping Address Woocommerce < 2.0 - SQL Injection 漏洞描述 The Multiple Shipping Address Woocommerce plugin before 2.0 does not properly saniti...
2022年8月31日 20:36CVE-2025-32970: XWiki WYSIWYG API – Open Redirect
漏洞标题 CVE-2025-32970: XWiki WYSIWYG API - Open Redirect 漏洞描述 A vulnerability in XWiki's WYSIWYG API allows an attacker to redirect users to arbitrary external URLs thro...
2025年8月8日 16:53CVE-2024-2862: LG LED Assistant – Unauthenticated Password Reset
漏洞标题 CVE-2024-2862: LG LED Assistant - Unauthenticated Password Reset 漏洞描述 The /api/changePw endpoint in LG LED Assistant allows unauthenticated password resets when reques...
2024年9月17日 01:56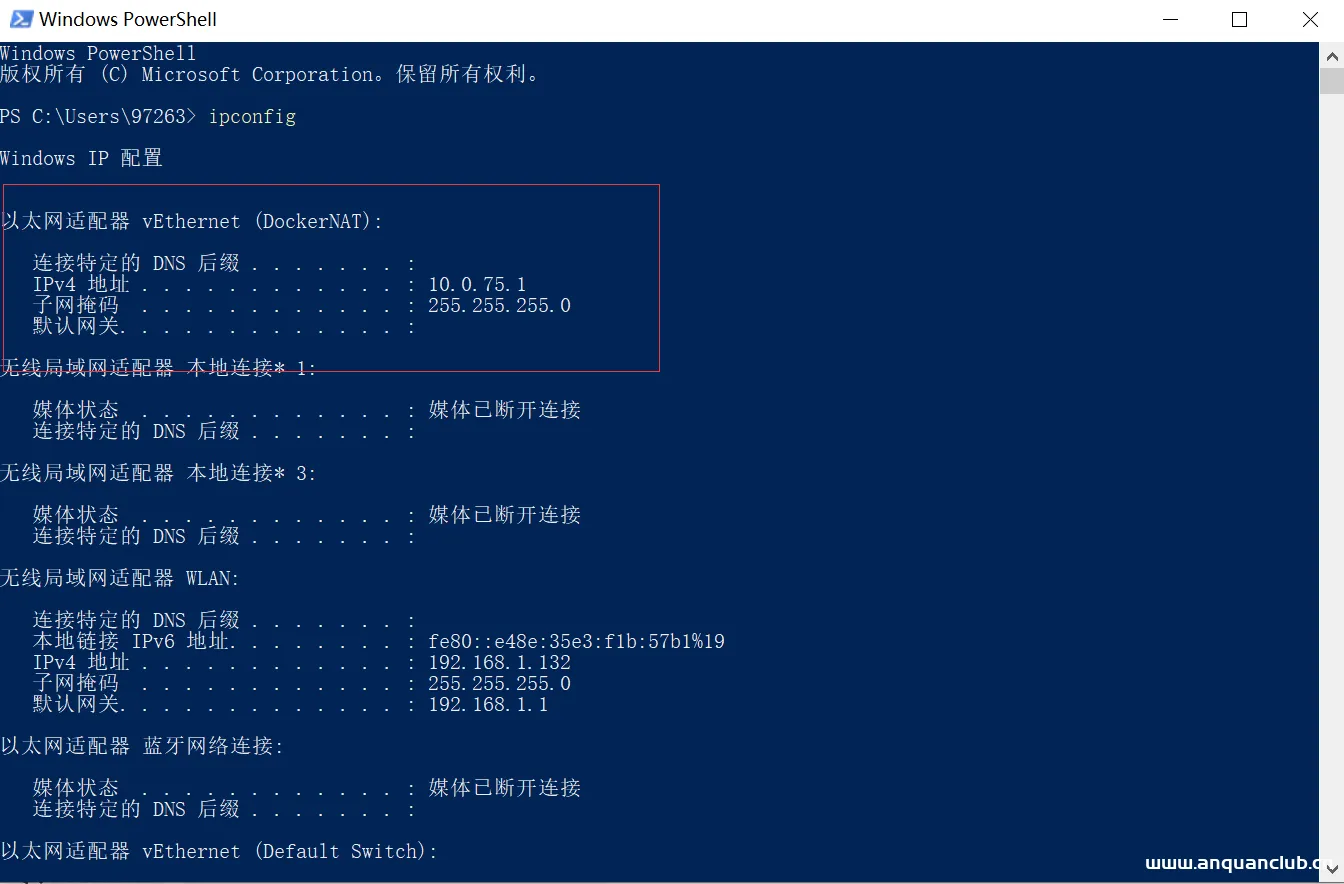
docker for windows 容器内网通过独立IP直接访问的方法_docker
这篇文章主要介绍了docker for windows 容器内网通过独立IP直接访问的方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学...
2026年3月1日 15:46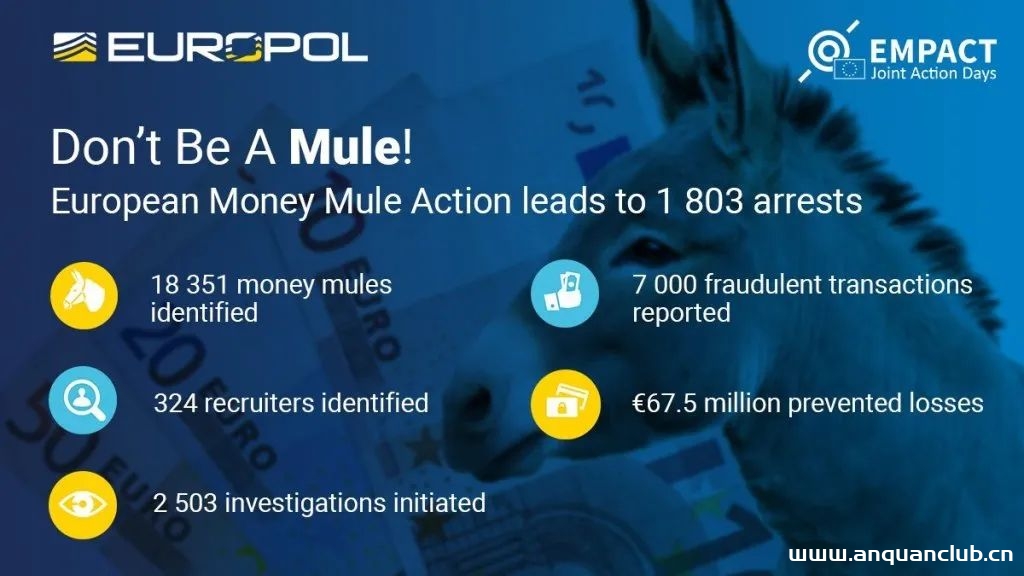
近两万钱骡,欧洲第七次联合打击洗钱行动落幕
12月1日,一项有着400家金融机构支持、名为EMMA 7(The European Money Mule Action)的欧洲多国联合行动落下帷幕。从9月15日起至11月30日,该行动取得了如下成果:识别18351名“钱骡“;识别32...
2022年3月10日 23:38CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection
漏洞标题 CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection 漏洞描述 Perfect Survey WordPress plugin before 1.5.2 does not validate and escape the question_id GET p...
2021年3月12日 09:26CVE-2018-1000600: Jenkins GitHub Plugin <=1.29.1 - Server-Side Request Forgery
漏洞标题 CVE-2018-1000600: Jenkins GitHub Plugin <=1.29.1 - Server-Side Request Forgery 漏洞描述 Jenkins GitHub Plugin 1.29.1 and earlier is susceptible to server-side request f...
2018年4月27日 08:25CVE-2015-4074: Joomla! Helpdesk Pro plugin <1.4.0 - Local File Inclusion
漏洞标题 CVE-2015-4074: Joomla! Helpdesk Pro plugin <1.4.0 - Local File Inclusion 漏洞描述 Directory traversal vulnerability in the Helpdesk Pro plugin before 1.4.0 for Joomla! ...
2015年3月14日 05:21CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059
漏洞标题 CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059 漏洞描述 Apache Struts 2.0.0 to 2.5.20 forced double OGNL evaluation when evaluated on raw user inp...
2019年1月17日 20:52CVE-2024-24565: CrateDB数据库任意文件读取漏洞
漏洞标题 CVE-2024-24565: CrateDB数据库任意文件读取漏洞 漏洞描述 CrateDB is a distributed SQL database that makes it simple to store and analyze massive amounts of data in real-time...
2024年2月17日 05:39CVE-2018-10823: D-Link Routers – Remote Command Injection
漏洞标题 CVE-2018-10823: D-Link Routers - Remote Command Injection 漏洞描述 D-Link DWR-116 through 1.06, DWR-512 through 2.02, DWR-712 through 2.02, DWR-912 through 2.02, DWR-921 t...
2018年11月20日 03:42Aiohttp CVE-2024-23334 目录遍历漏洞
漏洞标题 Aiohttp CVE-2024-23334 目录遍历漏洞 漏洞描述 Aiohttp 是一款开源的用于 asyncio 和 Python 的异步 HTTP 客户端/服务器框架。Aiohttp 存在目录遍历漏洞,此漏洞是由于应用程序读取文...
2024年1月12日 23:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

