
最新发布第440页

CVE-2017-9833: BOA Web Server 0.94.14 – Arbitrary File Access
漏洞标题 CVE-2017-9833: BOA Web Server 0.94.14 - Arbitrary File Access 漏洞描述 BOA Web Server 0.94.14 is susceptible to arbitrary file access. The server allows the injection of &...
 2017年3月17日 17:19
CVE-2024-51978: Brother Printers – Authentication Bypass via Default Admin Password
漏洞标题 CVE-2024-51978: Brother Printers – Authentication Bypass via Default Admin Password 漏洞描述 By leaking a target device's serial number, a remote attacker can genera...
2024年8月14日 08:49CVE-2019-9632: ESAFENET CDG – Arbitrary File Download
漏洞标题 CVE-2019-9632: ESAFENET CDG - Arbitrary File Download 漏洞描述 ESAFENET CDG V3 and V5 has an arbitrary file download vulnerability via the fileName parameter in download.j...
2019年1月30日 13:10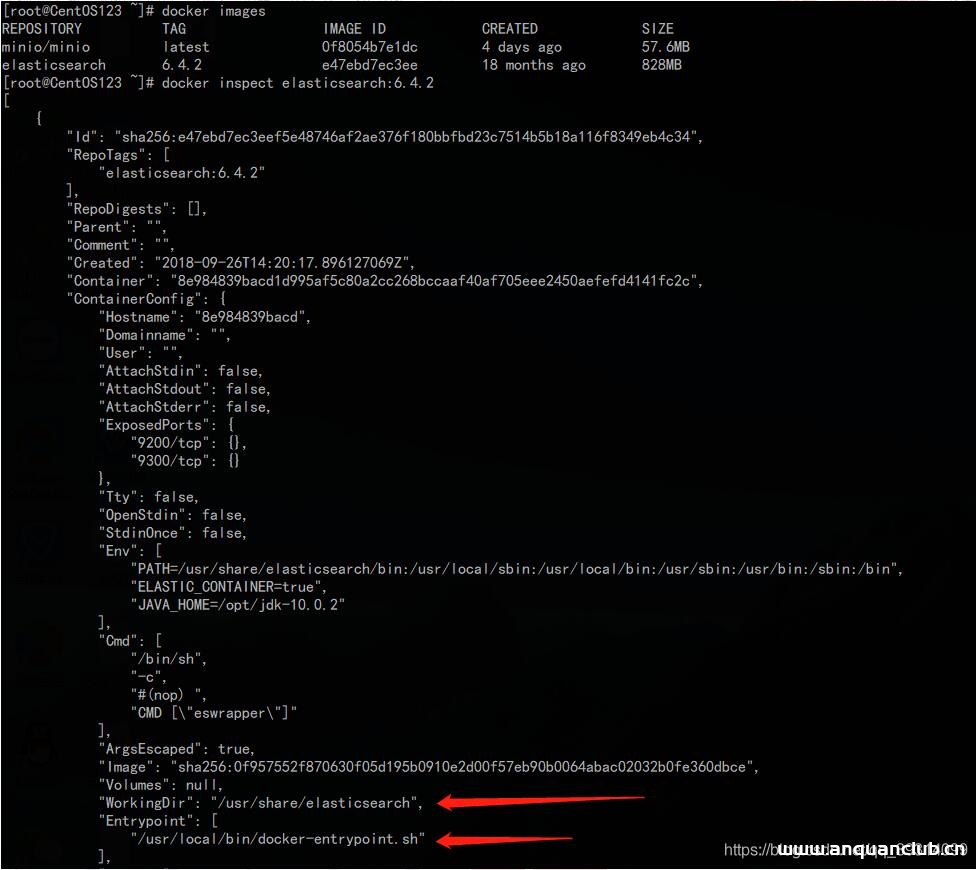
docker 启动elasticsearch镜像,挂载目录后报错的解决_docker
这篇文章主要介绍了docker 启动 elasticsearch镜像,挂载目录后报错的解决,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 从docker hub下载了一个es的镜像,版本为6.4.2,详...
2023年1月29日 21:12CVE-2022-45362: WordPress Paytm Payment Gateway <=2.7.0 - Server-Side Request Forgery
漏洞标题 CVE-2022-45362: WordPress Paytm Payment Gateway <=2.7.0 - Server-Side Request Forgery 漏洞描述 WordPress Paytm Payment Gateway plugin through 2.7.0 contains a server-si...
2022年1月5日 08:07CVE-2024-32738: CyberPower – SQL Injection
漏洞标题 CVE-2024-32738: CyberPower - SQL Injection 漏洞描述 A sql injection vulnerability exists in CyberPower PowerPanel Enterprise prior to v2.8.3. PoC代码
2024年6月24日 19:10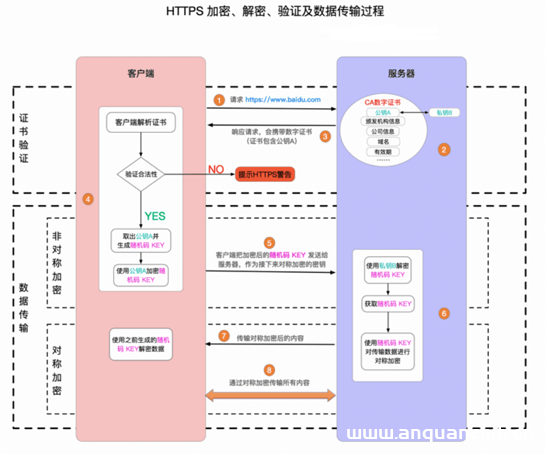
基于Nginx实现HTTPS网站设置的步骤_nginx
本文主要介绍了Nginx实现HTTPS网站设置的步骤,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录前言:加密算法:一、HTTPS 简介二、Nginx 实现 HTTPS ...
2022年6月17日 10:00CVE-2016-1000137: WordPress Hero Maps Pro 2.1.0 – Cross-Site Scripting
漏洞标题 CVE-2016-1000137: WordPress Hero Maps Pro 2.1.0 - Cross-Site Scripting 漏洞描述 WordPress Hero Maps Pro 2.1.0 contains a reflected cross-site scripting vulnerability which...
2016年5月23日 15:47CVE-2021-24295: Spam protection, AntiSpam, FireWall by CleanTalk < 5.153.4 - Unauthenticated Blind SQL Injection
漏洞标题 CVE-2021-24295: Spam protection, AntiSpam, FireWall by CleanTalk < 5.153.4 - Unauthenticated Blind SQL Injection 漏洞描述 It was possible to exploit an Unauthenticated ...
2021年6月13日 15:21
CentOS 8.1下搭建LEMP(Linux+Nginx+MySQL+PHP)环境(教程详解)_Linux
LEMP是一个软件堆栈,包含一组免费的开源工具,这些工具用于为高流量和动态网站提供动力。 这篇文章给大家介绍如何在CentOS 8 Linux发行版上安装LEMP服务器,本文通过实例代码给大家介绍的非常...
2024年4月4日 20:16
【分享】你真的了解二维码吗?
今天我们来聊一聊如今与我们日常生活联系非常密切的一样东西——我们出行,就餐,购物,几乎是每天都可能会用到。没错,就是二维码。 曾几何时,谁能料到,一个小小的黑白码竟有如此广泛的用途...

 2022年5月2日 15:22
CVE-2024-45488: SafeGuard for Privileged Passwords < 7.5.2 - Authentication Bypass
漏洞标题 CVE-2024-45488: SafeGuard for Privileged Passwords < 7.5.2 - Authentication Bypass 漏洞描述 One Identity Safeguard for Privileged Passwords before 7.5.2 allows unauthor...
2024年2月4日 17:20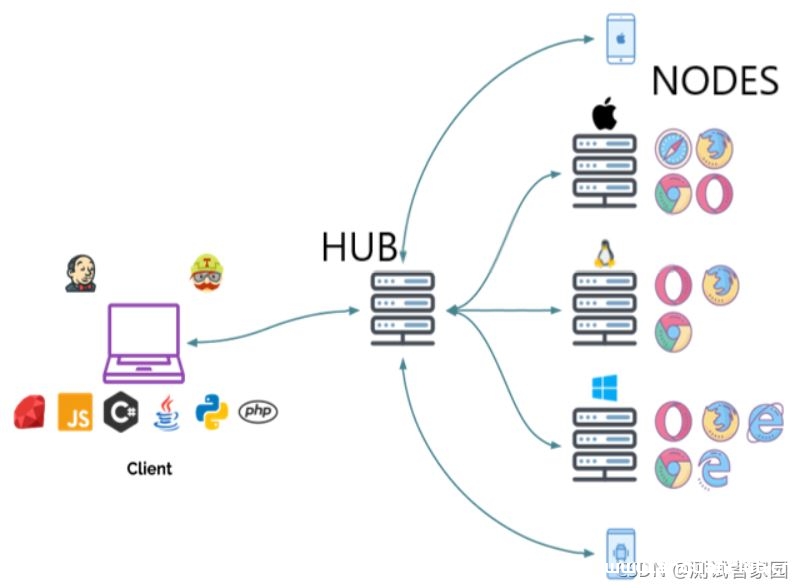
基于Docker+Selenium Grid的测试技术应用示例代码_docker
Selenium Grid允许我们在多台计算机上并行运行测试,并集中管理不同的浏览器版本和浏览器配置。这篇文章给大家介绍基于Docker+Selenium Grid的测试技术应用示例代码,需要的朋友参考下吧 Seleni...
2022年6月15日 22:43CVE-2024-50623: Cleo Synchronization 任意文件读取
漏洞标题 CVE-2024-50623: Cleo Synchronization 任意文件读取 漏洞描述 Cleo Synchronization 存在任意文件读取漏洞,攻击者可通过构造恶意请求获取服务器上的任意文件内容。 fofa: server=&qu...
2024年9月10日 04:00
bugbounty技巧聚合20220126
漏洞报告 【Imgur】密码无长度 http://hackerone.com/reports/1411363 【Mail.ru 】子域接管 http://hackerone.com/reports/1348504 【Lark Technologies】能够使用 Lark 的 Compose Email 功能...
2022年3月10日 23:39CVE-2019-2725: Oracle WebLogic Remote Code Execution
漏洞标题 CVE-2019-2725: Oracle WebLogic Remote Code Execution 漏洞描述 Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Services...
2019年11月29日 17:44
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

