
最新发布第441页
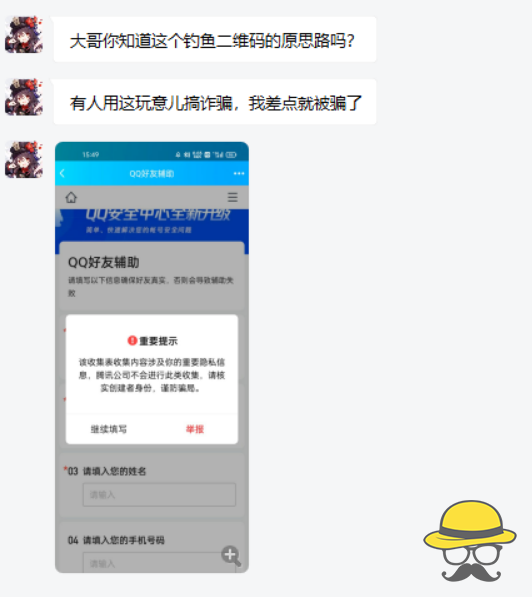
【骗局揭秘】QQ好友辅助验证导致的账户泄露 请谨防上当受骗!
杂谈 今天下午收到热心网友的求助 这不是腾讯文档吗?现在的人钓鱼手段简直太邪恶了……用腾讯自家的产品在QQ上钓鱼,就很离谱啊! 在线体验 下面的页面是仿真页面,请勿输入自己的密码,请勿花...

 2022年2月22日 19:57

CVE-2022-3933: WordPress Essential Real Estate <3.9.6 - Authenticated Cross-Site Scripting
漏洞标题 CVE-2022-3933: WordPress Essential Real Estate <3.9.6 - Authenticated Cross-Site Scripting 漏洞描述 WordPress Essential Real Estate plugin before 3.9.6 contains an auth...
 2022年9月17日 14:31
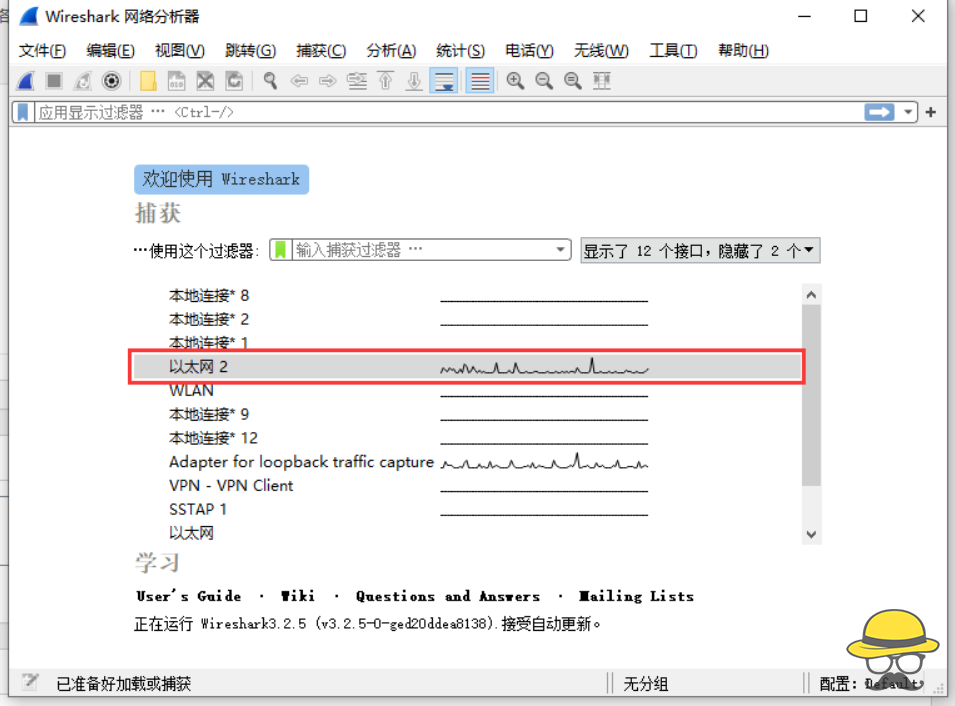
使用Wireshark抓包获取QQ好友的IP地址
介绍 很多人喜欢在互联网上装逼、口嗨,很多骗子在互联网上各种嚣张,通过这个教程可以很好的治一治这些人,本教程教大家如何通过Wireshark获取QQ好友的IP地址。 声明 本教程仅用于教育目的,请...
2022年4月1日 18:36CVE-2024-46938: Sitecore Experience Platform <= 10.4 - Arbitrary File Read
漏洞标题 CVE-2024-46938: Sitecore Experience Platform <= 10.4 - Arbitrary File Read 漏洞描述 An issue was discovered in Sitecore Experience Platform (XP), Experience Manager (XM...
2024年7月4日 09:10CVE-2025-49132: Pterodactyl Panel – Remote Code Execution
漏洞标题 CVE-2025-49132: Pterodactyl Panel - Remote Code Execution 漏洞描述 Pterodactyl is a free, open-source game server management panel. Using the /locales/locale.json with the...
2025年10月2日 00:11CVE-2024-0352: Likeshop userFormImage 文件上传漏洞
漏洞标题 CVE-2024-0352: Likeshop userFormImage 文件上传漏洞 漏洞描述 Likeshop up to 2.5.7.20210311 存在一处安全漏洞,被分类为严重级别。该漏洞影响 HTTP POST 请求处理组件的 file serv...
2024年11月11日 04:13CVE-2018-11138: Quest KACE System Management Appliance 8.0.318 – Remote Code Execution
漏洞标题 CVE-2018-11138: Quest KACE System Management Appliance 8.0.318 - Remote Code Execution 漏洞描述 The '/common/download_agent_installer.php' script in the Quest KA...
2018年3月12日 23:25CVE-2021-27909: Mautic <3.3.4 - Cross-Site Scripting
漏洞标题 CVE-2021-27909: Mautic <3.3.4 - Cross-Site Scripting 漏洞描述 Mautic before 3.3.4 contains a cross-site scripting vulnerability on the password reset page in the bundle...
2021年8月30日 02:18CVE-2024-27954: WordPress Automatic Plugin <3.92.1 - Arbitrary File Download and SSRF
漏洞标题 CVE-2024-27954: WordPress Automatic Plugin <3.92.1 - Arbitrary File Download and SSRF 漏洞描述 WordPress Automatic plugin <3.92.1 is vulnerable to unauthenticated Ar...
2024年4月25日 10:41CVE-2024-25852: Linksys RE7000 – Command Injection
漏洞标题 CVE-2024-25852: Linksys RE7000 - Command Injection 漏洞描述 Linksys RE7000 v2.0.9, v2.0.11, and v2.0.15 have a command execution vulnerability in the "AccessControlLi...
2024年1月26日 19:26CVE-2021-3287: Zoho ManageEngine OpManager < 12.5.329 - Remote Code Execution
漏洞标题 CVE-2021-3287: Zoho ManageEngine OpManager < 12.5.329 - Remote Code Execution 漏洞描述 Zoho ManageEngine OpManager before 12.5.329 contains a remote code execution caus...
2021年2月16日 13:11CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
2012年6月29日 03:29CVE-2024-8181: Flowise <= 1.8.2 Authentication Bypass
漏洞标题 CVE-2024-8181: Flowise <= 1.8.2 Authentication Bypass 漏洞描述 An Authentication Bypass vulnerability exists in Flowise version 1.8.2. This could allow a remote, unauth...
2024年8月6日 17:18CVE-2024-55416: DevDojo Voyager <=1.8.0 - Cross-Site Scripting
漏洞标题 CVE-2024-55416: DevDojo Voyager <=1.8.0 - Cross-Site Scripting 漏洞描述 DevDojo Voyager through version 1.8.0 is vulnerable to reflected XSS via /admin/compass. By mani...
2024年5月11日 01:05CVE-2021-24991: WooCommerce PDF Invoices & Packing Slips WordPress Plugin < 2.10.5 - Cross-Site Scripting
漏洞标题 CVE-2021-24991: WooCommerce PDF Invoices & Packing Slips WordPress Plugin < 2.10.5 - Cross-Site Scripting 漏洞描述 The Wordpress plugin WooCommerce PDF Invoices &am...
2021年9月15日 14:12CVE-2016-1555: NETGEAR WNAP320 Access Point Firmware – Remote Command Injection
漏洞标题 CVE-2016-1555: NETGEAR WNAP320 Access Point Firmware - Remote Command Injection 漏洞描述 NETGEAR WNAP320 Access Point Firmware version 2.0.3 could allow an unauthenticated...
2016年11月13日 04:11
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

