
最新发布第455页

(CVE-2023-3765) MLflow 绝对路径遍历漏洞
漏洞标题 (CVE-2023-3765) MLflow 绝对路径遍历漏洞 漏洞描述 (CVE-2023-3765) MLflow 绝对路径遍历漏洞 PoC代码 暂无
 2023年1月11日 20:19
-Struts2-045 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-Struts2-045 远程命令执行漏洞 Struts是Apache软件基金会(ASF)赞助的一个开源项目。它最初是Jakarta项目中的一个子项目,并在2004年3...

 2023年2月5日 12:56
CVE-2023-40753: PHPJabbers Ticket Support Script v3.2 – Cross-Site Scripting
漏洞标题 CVE-2023-40753: PHPJabbers Ticket Support Script v3.2 - Cross-Site Scripting 漏洞描述 There is a Cross Site Scripting (XSS) vulnerability in the message parameter of index...
2023年12月13日 17:50CVE-2024-41810: Twisted – Open Redirect & XSS
漏洞标题 CVE-2024-41810: Twisted - Open Redirect & XSS 漏洞描述 Twisted is an event-based framework for internet applications, supporting Python 3.6+. The Twisted web framework...
2024年1月5日 12:26CVE-2017-7615: MantisBT <=2.30 - Arbitrary Password Reset/Admin Access
漏洞标题 CVE-2017-7615: MantisBT <=2.30 - Arbitrary Password Reset/Admin Access 漏洞描述 MantisBT through 2.3.0 allows arbitrary password reset and unauthenticated admin access ...
2017年6月9日 00:36CVE-2016-8735: Apache Tomcat – Remote Code Execution via JMX Ports
漏洞标题 CVE-2016-8735: Apache Tomcat - Remote Code Execution via JMX Ports 漏洞描述 Apache Tomcat versions before 6.0.48, 7.x before 7.0.73, 8.x before 8.0.39, 8.5.x before 8.5.7,...
2016年3月17日 00:34CVE-2020-16846: SaltStack Shell Injection
漏洞标题 CVE-2020-16846: SaltStack Shell Injection 漏洞描述 An issue was discovered in SaltStack Salt through 3002. Sending crafted web requests to the Salt API, with the SSH clien...
2020年4月19日 12:56CVE-2025-55182: React Server Components – Remote Code Execution
漏洞标题 CVE-2025-55182: React Server Components - Remote Code Execution 漏洞描述 React Server Components 19.0.0, 19.1.0, 19.1.1, and 19.2.0 including react-server-dom-parcel, reac...
2025年1月28日 08:54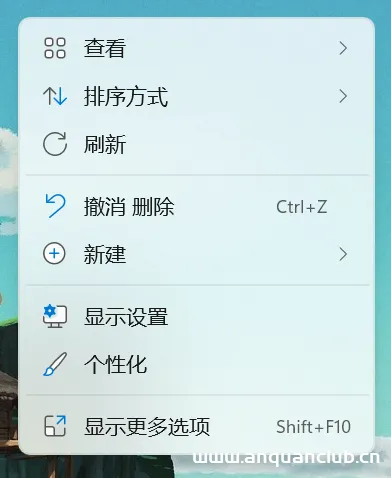
Win11桌面右键菜单栏怎么回到Win10的样子(直接命令执行便可完成,简单快捷)
很多小伙伴在用Win11的时候都有因为它的右键菜单栏所苦恼吧。 每次在解压一个文件的时候都要多点击一下 “显示更多选项” 才可以出现完整的菜单栏, 在我的电脑文件夹当中也需要点击 “显示更多...
2022年8月17日 12:15CVE-2023-1454: Jeecg Boot QuerySql sql injection
漏洞标题 CVE-2023-1454: Jeecg Boot QuerySql sql injection 漏洞描述 JeecgBoot是一款基于BPM的低代码平台!前后端分离架构 SpringBoot 2.x,SpringCloud,Ant Design&Vue,Mybatis-plus...
2023年6月9日 09:55CVE-2018-16283: WordPress Plugin Wechat Broadcast 1.2.0 – Local File Inclusion
漏洞标题 CVE-2018-16283: WordPress Plugin Wechat Broadcast 1.2.0 - Local File Inclusion 漏洞描述 WordPress Wechat Broadcast plugin 1.2.0 and earlier allows Directory Traversal via ...
2018年4月25日 22:26CVE-2025-51586: PrestaShop – Information Disclosure
漏洞标题 CVE-2025-51586: PrestaShop - Information Disclosure 漏洞描述 User enumeration vulnerability in the AdminLogin controller in PrestaShop 1.7 through 8.2.2 allows remote atta...
2025年12月20日 04:11CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export
漏洞标题 CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export 漏洞描述 includes/options.php in the motors-car-dealership-clas...
2019年8月19日 11:11CVE-2021-42887: TOTOLINK EX1200T 4.1.2cu.5215 – Authentication Bypass
漏洞标题 CVE-2021-42887: TOTOLINK EX1200T 4.1.2cu.5215 - Authentication Bypass 漏洞描述 TOTOLINK EX1200T 4.1.2cu.5215 is susceptible to authentication bypass. An attacker can bypas...
2021年10月7日 12:50(CVE-2010-1603) Joomla! ZiMB Core组件目录遍历漏洞
漏洞标题 (CVE-2010-1603) Joomla! ZiMB Core组件目录遍历漏洞 漏洞描述 (CVE-2010-1603) Joomla! ZiMB Core组件目录遍历漏洞 PoC代码 暂无
2010年8月6日 04:55
[GXYCTF2019]BabySQli
进入题目一个登录框 对登录框做了一些常规的sql注入和fuzz发现都无果。然后在等级登录后跳转的search.php页面查看源代码发现一段编码。 MMZFM422K5HDASKDN5TVU3SKOZRFGQRRMMZFM6KJJBSG6WSYJJWES...
2022年4月21日 21:53
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

