
最新发布第466页

CVE-2023-3277: MStore API <= 4.10.7 - Unauthorized Account Access and Privilege Escalation
漏洞标题 CVE-2023-3277: MStore API <= 4.10.7 - Unauthorized Account Access and Privilege Escalation 漏洞描述 The MStore API plugin for WordPress is vulnerable to Unauthorized Ac...
 2023年11月7日 19:42
CVE-2021-24212: WooCommerce Help Scout – Arbitrary File Upload
漏洞标题 CVE-2021-24212: WooCommerce Help Scout - Arbitrary File Upload 漏洞描述 WooCommerce Help Scout plugin before version 2.9.1 contains an unrestricted file upload vulnerabili...
2021年3月11日 00:24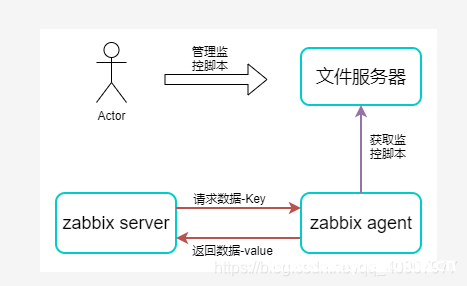
Zabbix 动态执行监控采集脚本的实现原理_zabbix
这篇文章主要介绍了Zabbix 动态执行监控采集脚本的实现原理,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 在使用Zabbix自定义脚本采集监控数据...
2022年9月16日 22:20
如何使用docker对容器资源进行限制_docker
这篇文章主要介绍了如何使用docker对容器资源进行限制,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 问题窥探 在服务器当中,假设iis服务部署多...
2022年8月26日 20:13CVE-2023-20888: VMware Aria Operations for Networks – Remote Code Execution
漏洞标题 CVE-2023-20888: VMware Aria Operations for Networks - Remote Code Execution 漏洞描述 Aria Operations for Networks contains an authenticated deserialization vulnerability. ...
2023年5月12日 17:12CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
2022年12月4日 02:57CVE-2024-10708: System Dashboard < 2.8.15 - Admin+ Path Traversal
漏洞标题 CVE-2024-10708: System Dashboard < 2.8.15 - Admin+ Path Traversal 漏洞描述 The System Dashboard WordPress plugin before 2.8.15 does not validate user input used in a pa...
2024年1月23日 12:03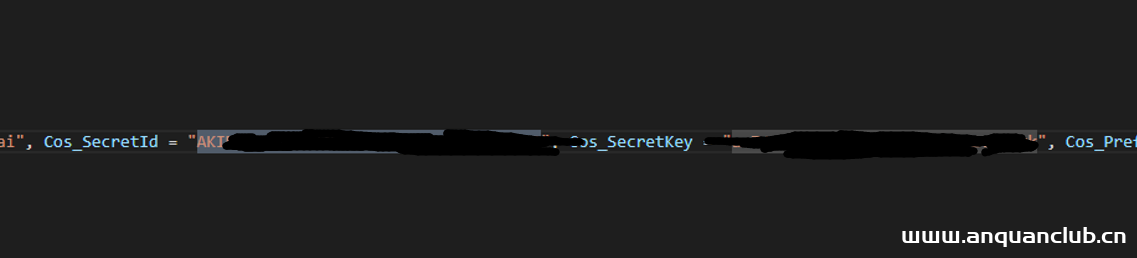
某鹅一次AK /SK 泄露导致拿下存储桶
第一次写文章师傅们 轻喷~ 起因 大二学生上课摸鱼,然后正常在测一些东西,emm 偶然在前端发现 发现了 AK 等字样~ 心里窃喜 洞要来了 ? !! 直接用现成的工具 就好 然后进一步利用的话 可以做...
2022年3月10日 23:37CVE-2024-7029: AVTECH IP Camera – Command Injection
漏洞标题 CVE-2024-7029: AVTECH IP Camera - Command Injection 漏洞描述 The endpoint `/cgi-bin/supervisor/Factory.cgi` is vulnerable to command injection via the `action` parameter, ...
2024年7月11日 16:06CVE-2023-0876: WordPress Meta SEO <= 4.5.2 - Open Redirect
漏洞标题 CVE-2023-0876: WordPress Meta SEO <= 4.5.2 - Open Redirect 漏洞描述 The WP Meta SEO WordPress plugin before 4.5.3 did not authorize several AJAX actions, which allowed ...
2023年12月15日 20:13CVE-2025-64446: FortiWeb – Authentication Bypass
漏洞标题 CVE-2025-64446: FortiWeb - Authentication Bypass 漏洞描述 A relative path traversal vulnerability in Fortinet FortiWeb 8.0.0 through 8.0.1, FortiWeb 7.6.0 through 7.6.4, F...
2025年7月24日 07:23
工具理解小结(面试火线被拒后的发奋图强)
面试官直接问我子域名收集工具原理,我寻思会用就行啊,结果我想了半天也没整明白,然后去把工具扒出来挨个瞅了瞅,这边给大家介绍一下: 一、首先了解一下为什么要收集子域名 在挖洞之前肯定要...
2022年3月10日 23:34CVE-2022-0952: WordPress Sitemap by click5 <1.0.36 - Missing Authorization
漏洞标题 CVE-2022-0952: WordPress Sitemap by click5 <1.0.36 - Missing Authorization 漏洞描述 WordPress Sitemap by click5 plugin before 1.0.36 is susceptible to missing authoriza...
2022年12月24日 08:56CVE-2025-27505: GeoServer – Missing Authorization on REST API Index
漏洞标题 CVE-2025-27505: GeoServer - Missing Authorization on REST API Index 漏洞描述 GeoServer contains a missing authorization vulnerability that allows unauthorized access to th...
2025年8月11日 23:09CVE-2020-36510: WordPress 15Zine <3.3.0 - Cross-Site Scripting
漏洞标题 CVE-2020-36510: WordPress 15Zine <3.3.0 - Cross-Site Scripting 漏洞描述 WordPress 15Zine before 3.3.0 is vulnerable to reflected cross-site scripting because the theme ...
2020年10月27日 20:02CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
2022年9月22日 17:04
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

