
最新发布第472页

CVE-2025-41646: RevPi Webstatus <= v2.4.5 - Authentication Bypass
漏洞标题 CVE-2025-41646: RevPi Webstatus <= v2.4.5 - Authentication Bypass 漏洞描述 An unauthorized remote attacker can bypass the authentication of the affected software packag...
 2025年5月27日 11:43
CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure
漏洞标题 CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure 漏洞描述 WordPress WPS Hide Login plugin before 1.9.1 is susceptible to incorrect authorization...
2021年4月29日 09:20CVE-2021-21803: Advantech R-SeeNet – Cross-Site Scripting
漏洞标题 CVE-2021-21803: Advantech R-SeeNet - Cross-Site Scripting 漏洞描述 Advantech R-SeeNet is vulnerable to cross-site scripting via the device_graph_page.php script via the is...
2021年2月28日 00:05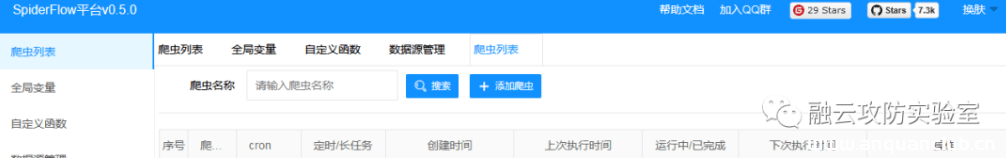
SpiderFlow save 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 SpiderFlow save 远程命令执行漏洞 spider-flow 是一个爬虫平台,以图形化方式定义爬虫流程,无需代码即可实现一个爬虫 。spider-flow...
2026年2月13日 12:53CVE-2022-32195: Open edX <2022-06-06 - Cross-Site Scripting
漏洞标题 CVE-2022-32195: Open edX <2022-06-06 - Cross-Site Scripting 漏洞描述 Open edX before 2022-06-06 contains a reflected cross-site scripting vulnerability via the 'ne...
2022年12月20日 15:16CVE-2022-32409: Portal do Software Publico Brasileiro i3geo 7.0.5 – Local File Inclusion
漏洞标题 CVE-2022-32409: Portal do Software Publico Brasileiro i3geo 7.0.5 - Local File Inclusion 漏洞描述 Portal do Software Publico Brasileiro i3geo 7.0.5 is vulnerable to local ...
2022年4月21日 03:48CVE-2010-1532: Joomla! Component PowerMail Pro 1.5.3 – Local File Inclusion
漏洞标题 CVE-2010-1532: Joomla! Component PowerMail Pro 1.5.3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the givesight PowerMail Pro (com_powermail) com...
2010年3月27日 12:31CVE-2022-40734: UniSharp aka Laravel Filemanager v2.5.1 – Directory Traversal
漏洞标题 CVE-2022-40734: UniSharp aka Laravel Filemanager v2.5.1 - Directory Traversal 漏洞描述 UniSharp laravel-filemanager (aka Laravel Filemanager) through 2.5.1 allows download...
2022年11月27日 00:07CVE-2009-2015: Joomla! MooFAQ 1.0 – Local File Inclusion
漏洞标题 CVE-2009-2015: Joomla! MooFAQ 1.0 - Local File Inclusion 漏洞描述 Joomla! Ideal MooFAQ 1.0 via com_moofaq allows remote attackers to read arbitrary files via a .. (dot dot...
2009年7月23日 20:43
防护措施 – 关键信息基础设施安全保护 – hvv面试题
什么是安全加固 为什么要做安全加固 法律法规利益保护安全检查自身安全 安全加固划分 安全加固准备阶段 基本要素准备 确定安全加固的范围;确定安全加固的时间进度;确定安全加固的人力资源与沟...

 2022年6月30日 18:12
spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+
漏洞标题 spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+ 漏洞描述 A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to rem...
2022年4月4日 14:52CVE-2023-2518: WordPress Easy Forms for Mailchimp Plugin < 6.8.9 - Cross-Site Scripting
漏洞标题 CVE-2023-2518: WordPress Easy Forms for Mailchimp Plugin < 6.8.9 - Cross-Site Scripting 漏洞描述 The Easy Forms for Mailchimp plugin before version 6.8.9 contains a ref...
2023年7月27日 02:32CVE-2015-4127: WordPress Church Admin <0.810 - Cross-Site Scripting
漏洞标题 CVE-2015-4127: WordPress Church Admin <0.810 - Cross-Site Scripting 漏洞描述 WordPress Church Admin plugin before 0.810 allows remote attackers to inject arbitrary web ...
2015年2月11日 00:30CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect
漏洞标题 CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect 漏洞描述 WordPress Event Tickets < 5.2.2 is susceptible to an open redirect vulnerability. The plugin...
2021年9月21日 17:04CVE-2024-6753: Social Auto Poster <= 5.3.14 - Stored Cross-Site Scripting
漏洞标题 CVE-2024-6753: Social Auto Poster <= 5.3.14 - Stored Cross-Site Scripting 漏洞描述 Social Auto Poster plugin for WordPress versions up to 5.3.14 contains a stored cross...
2024年12月24日 05:40CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion
漏洞标题 CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion 漏洞描述 WordPress MyPixs 0.3 and prior contains a local file inclusion vulnerability. PoC代码
2015年6月22日 19:13
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

