
最新发布第47页

CVE-2022-0948: WordPress Order Listener for WooCommerce <3.2.2 - SQL Injection
漏洞标题 CVE-2022-0948: WordPress Order Listener for WooCommerce <3.2.2 - SQL Injection 漏洞描述 WordPress Order Listener for WooCommerce plugin before 3.2.2 contains a SQL inje...
 2022年1月3日 20:13

Dockerfile 中 VOLUME 与 docker -v 的区别说明_docker
这篇文章主要介绍了Dockerfile 中 VOLUME 与 docker -v 的区别说明,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 Dockerfile 中的 VOLUME 挂载与 docker -v 命令挂载,两...
2022年7月18日 21:24CVE-2021-34621: WordPress ProfilePress 3.0.0-3.1.3 – Admin User Creation Weakness
漏洞标题 CVE-2021-34621: WordPress ProfilePress 3.0.0-3.1.3 - Admin User Creation Weakness 漏洞描述 ProfilePress WordPress plugin is susceptible to a vulnerability in the user regi...
2021年8月17日 05:58
Nginx解决前端访问资源跨域问题的方法详解_nginx
这篇文章主要给大家介绍了关于Nginx解决前端访问资源跨域问题的相关资料,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习...
2022年10月24日 21:10CVE-2018-10942: Prestashop AttributeWizardPro Module – Arbitrary File Upload
漏洞标题 CVE-2018-10942: Prestashop AttributeWizardPro Module - Arbitrary File Upload 漏洞描述 In the Attribute Wizard addon 1.6.9 for PrestaShop allows remote attackers to execute...
2018年9月10日 02:05CVE-2025-9196: Trinity Audio <= 5.21.0 - Information Exposure
漏洞标题 CVE-2025-9196: Trinity Audio <= 5.21.0 - Information Exposure 漏洞描述 The Trinity Audio Text to Speech AI audio player to convert content into audio plugin for WordPre...
2025年8月20日 05:07CVE-2023-36347: POS Codekop v2.0 – Broken Authentication
漏洞标题 CVE-2023-36347: POS Codekop v2.0 - Broken Authentication 漏洞描述 A broken authentication mechanism in the endpoint excel.php of POS Codekop v2.0 allows unauthenticated at...
2023年6月29日 00:06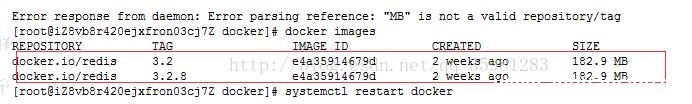
在docker下删除两个id相同的镜像的操作_docker
这篇文章主要介绍了在docker下删除两个id相同的镜像的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 今天建立docker容器的时候由于疏忽,镜像的名字输错了,结果容器...
2023年1月31日 20:08CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection
漏洞标题 CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection 漏洞描述 The LearnPress WordPress LMS Plugin plugin for WordPress is vulnerable to time-based ...
2024年3月26日 19:24CVE-2020-12800: WordPress Contact Form 7 <1.3.3.3 - Remote Code Execution
漏洞标题 CVE-2020-12800: WordPress Contact Form 7 <1.3.3.3 - Remote Code Execution 漏洞描述 WordPress Contact Form 7 before 1.3.3.3 allows unrestricted file upload and remote co...
2020年7月28日 06:39渗透痕迹清理方法的简单总结
1、为什么要做痕迹清理 在渗透完成之后,为了减少被发现和追溯的概率,攻击者有必要清除自己的攻击痕迹,本文分别对windows和linux上清理痕迹的方式做一个总结。 2、windows 情况一: 可以远程...

 2023年4月17日 19:41
CVE-2017-5487: WordPress<4.7.1 Exist Username Enumeration
漏洞标题 CVE-2017-5487: Wordpress<4.7.1 Exist Username Enumeration 漏洞描述 WordPress (是一种使用PHP语言开发的博客平台)WordPress 在4.7.0版本之后将REST API插件集成到默认功能之...
2017年11月6日 19:07CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass
漏洞标题 CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass 漏洞描述 Stacks Mobile App Builder WordPress plugin ≤ 5.2.3 suffers from an authent...
2024年1月19日 22:16CVE-2017-8229: Amcrest IP Camera Web Management – Data Exposure
漏洞标题 CVE-2017-8229: Amcrest IP Camera Web Management - Data Exposure 漏洞描述 Amcrest IPM-721S V2.420.AC00.16.R.20160909 devices allow an unauthenticated attacker to download t...
2017年5月3日 15:15CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection
漏洞标题 CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection 漏洞描述 WordPress Pricing Deals for WooCommerce plugin through 2.0.2.02 contains a SQ...
2022年12月4日 03:20CVE-2023-28432: MinIO Cluster Deployment – Information Disclosure
漏洞标题 CVE-2023-28432: MinIO Cluster Deployment - Information Disclosure 漏洞描述 MinIO is susceptible to information disclosure. In a cluster deployment starting with RELEASE.20...
2023年1月21日 14:14
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
2026年10月27日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

