
最新发布第493页

CVE-2010-1472: Joomla! Component Horoscope 1.5.0 – Local File Inclusion
漏洞标题 CVE-2010-1472: Joomla! Component Horoscope 1.5.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Daily Horoscope (com_horoscope) component 1.5.0...
 2010年3月7日 04:22
CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 – Remote Code Execution (XXE)
漏洞标题 CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 - Remote Code Execution (XXE) 漏洞描述 The JIRA Workflow Designer Plugin in Atlassian JIRA...
2017年8月8日 10:18CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass
漏洞标题 CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass 漏洞描述 Kubernetes Dashboard before 1.10.1 allows attackers to bypass authentication and use Dashb...
2018年2月1日 12:08Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518)
漏洞标题 Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518) 漏洞描述 Atlassian Confluence是一款企业知识管理与协作软件。该漏洞存在于Atlassian Confluence...
2023年5月28日 18:58CVE-2021-39320: WordPress Under Construction <1.19 - Cross-Site Scripting
漏洞标题 CVE-2021-39320: WordPress Under Construction <1.19 - Cross-Site Scripting 漏洞描述 WordPress Under Construction plugin before 1.19 contains a cross-site scripting vulne...
2021年8月8日 17:59CVE-2010-2050: Joomla! Component MS Comment 0.8.0b – Local File Inclusion
漏洞标题 CVE-2010-2050: Joomla! Component MS Comment 0.8.0b - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Moron Solutions MS Comment (com_mscomment) co...
2010年6月2日 16:42CVE-2019-7609: Kibana Timelion – Arbitrary Code Execution
漏洞标题 CVE-2019-7609: Kibana Timelion - Arbitrary Code Execution 漏洞描述 Kibana versions before 5.6.15 and 6.6.1 contain an arbitrary code execution flaw in the Timelion visuali...
2019年11月4日 19:20CVE-2023-42442: JumpServer > 3.6.4 – Information Disclosure
漏洞标题 CVE-2023-42442: JumpServer > 3.6.4 - Information Disclosure 漏洞描述 JumpServer is an open source bastion host and a professional operation and maintenance security aud...
2023年12月1日 03:46CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass
漏洞标题 CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass 漏洞描述 Stacks Mobile App Builder WordPress plugin ≤ 5.2.3 suffers from an authent...
2024年1月19日 22:16CVE-2018-11138: Quest KACE System Management Appliance 8.0.318 – Remote Code Execution
漏洞标题 CVE-2018-11138: Quest KACE System Management Appliance 8.0.318 - Remote Code Execution 漏洞描述 The '/common/download_agent_installer.php' script in the Quest KA...
2018年1月20日 18:42CVE-2022-1916: WordPress Active Products Tables for WooCommerce <1.0.5 - Cross-Site Scripting
漏洞标题 CVE-2022-1916: WordPress Active Products Tables for WooCommerce <1.0.5 - Cross-Site Scripting 漏洞描述 WordPress Active Products Tables for WooCommerce plugin prior to ...
2022年3月21日 22:41CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
2023年1月5日 03:21CVE-2018-19877: Adiscon LogAnalyzer <4.1.7 - Cross-Site Scripting
漏洞标题 CVE-2018-19877: Adiscon LogAnalyzer <4.1.7 - Cross-Site Scripting 漏洞描述 Adiscon LogAnalyzer before 4.1.7 contains a cross-site scripting vulnerability in the 'r...
2018年2月16日 00:46CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 – SQL Injection
漏洞标题 CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 - SQL Injection 漏洞描述 WordPress Easy Digital Downloads plugin 3.1.0.2 and 3.1.0.3 contains a SQL inject...
2023年12月29日 15:53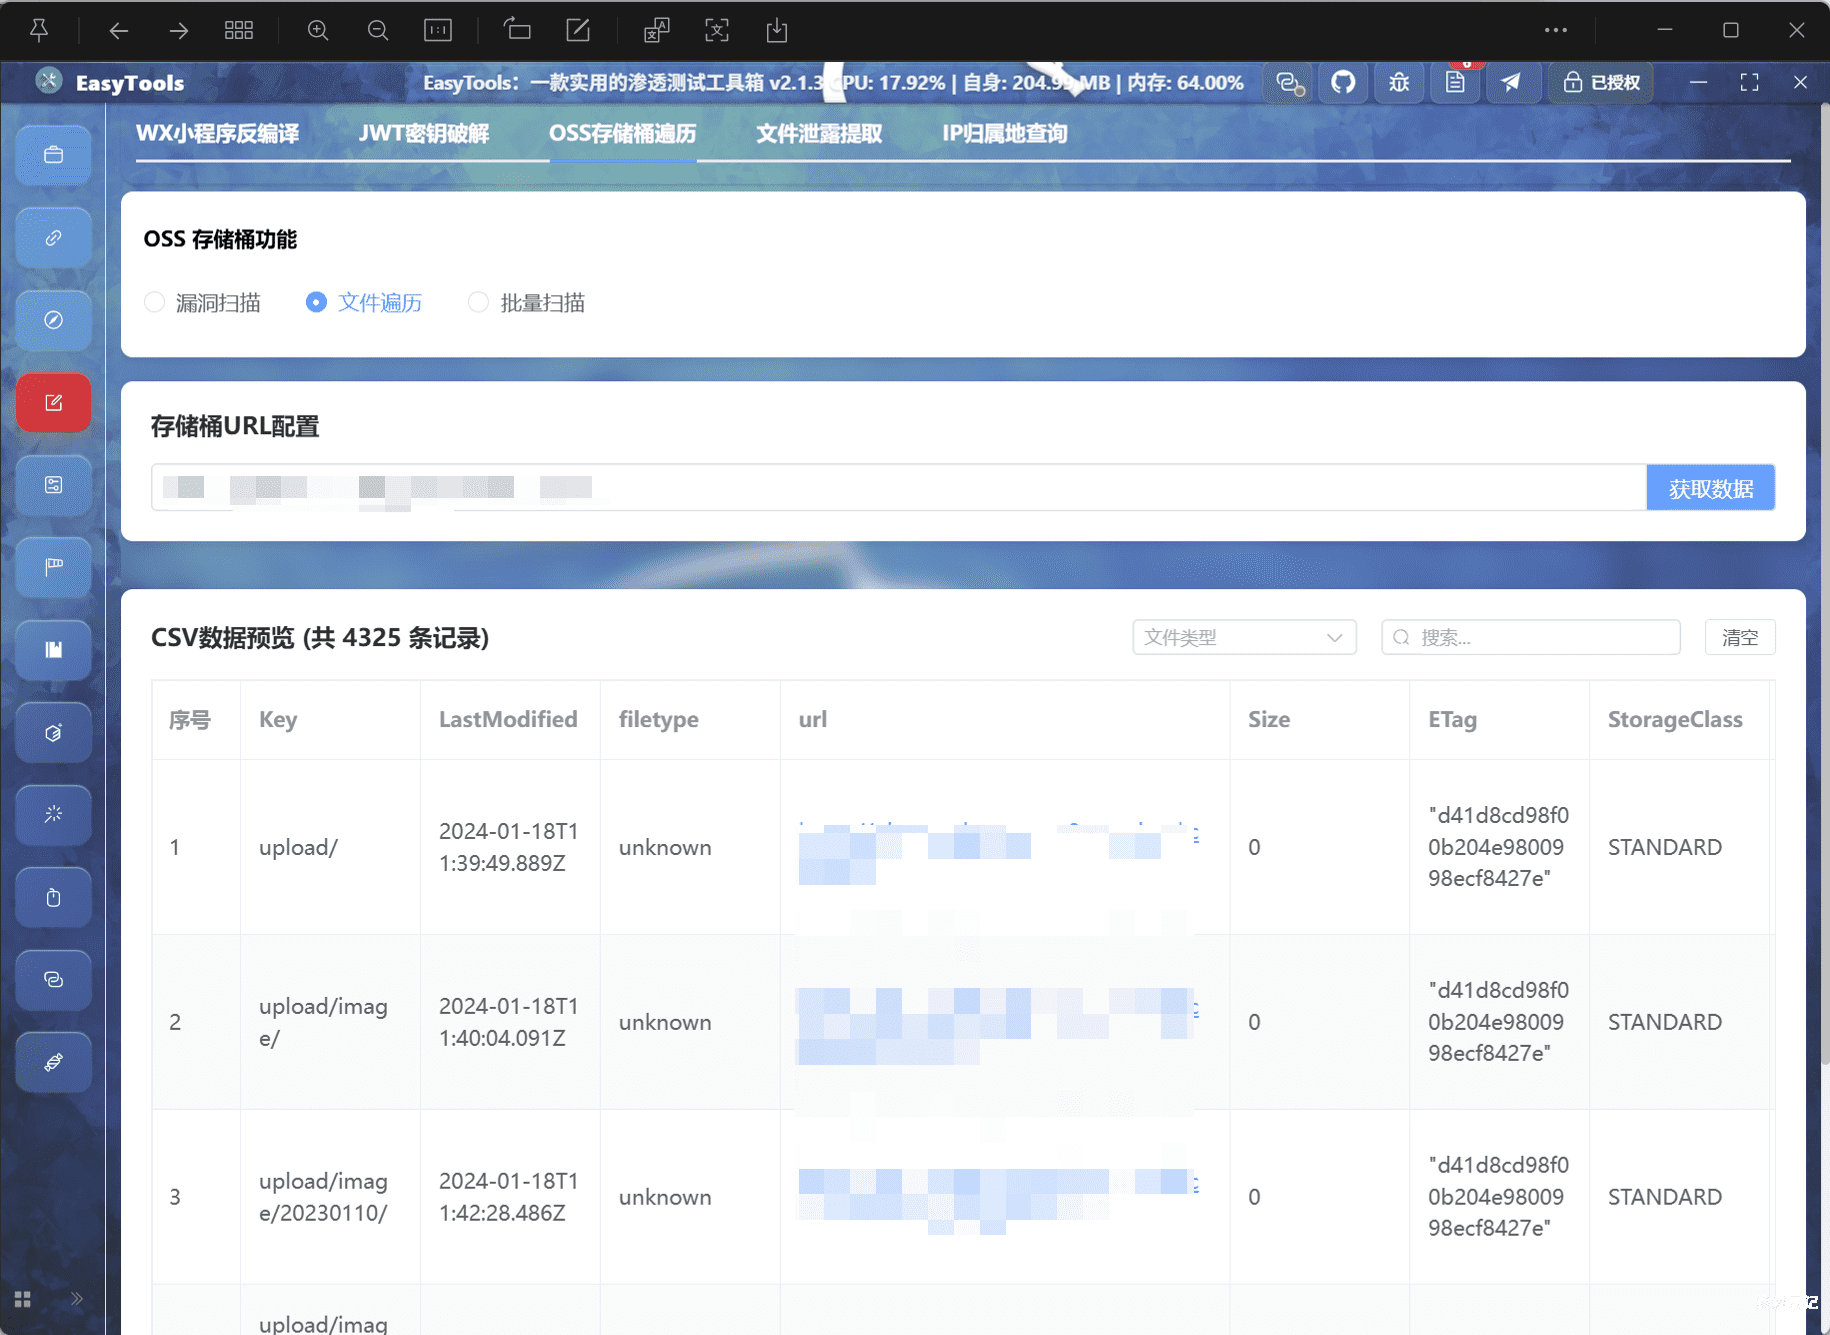
EasyTools渗透测试工具箱V2.1.4更新(优化资源桶遍历功能,支持kkfileview预览,新增空间测绘、AI版域名收集功能等诸多功能)
前言 各位看官老爷们,很久没有更新了,新的一年了在此汇报一下更新进度: 优化资源桶遍历功能,支持kkfileview预览; 重构渗透测试模块,调用httpx提高性能与准确度; 新增AI底座,方便后续功能...

 2026年3月1日 15:46
CVE-2021-24849: WCFM WooCommerce Multivendor Marketplace < 3.4.12 - SQL Injection
漏洞标题 CVE-2021-24849: WCFM WooCommerce Multivendor Marketplace < 3.4.12 - SQL Injection 漏洞描述 The wcfm_ajax_controller AJAX action of the WCFM Marketplace WordPress plugin...
2021年11月24日 23:19
2026年9月24日 11:46
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

