
最新发布第497页

CVE-2022-1946: WordPress Gallery <2.0.0 - Cross-Site Scripting
漏洞标题 CVE-2022-1946: WordPress Gallery <2.0.0 - Cross-Site Scripting 漏洞描述 WordPress Gallery plugin before 2.0.0 contains a reflected cross-site scripting vulnerability. I...
 2022年12月11日 01:17
CVE-2023-37462: XWiki Platform – Remote Code Execution
漏洞标题 CVE-2023-37462: XWiki Platform - Remote Code Execution 漏洞描述 XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Im...
2023年2月13日 12:27(CVE-2020-4429) IBM Data Risk Manager 2.0.1-2.0.6 默认密码漏洞
漏洞标题 (CVE-2020-4429) IBM Data Risk Manager 2.0.1-2.0.6 默认密码漏洞 漏洞描述 (CVE-2020-4429) IBM Data Risk Manager 2.0.1-2.0.6 默认密码漏洞 PoC代码 暂无
2020年2月27日 23:09CVE-2023-1177: MLflow get-artifact 任意文件读取漏洞
漏洞标题 CVE-2023-1177: MLflow get-artifact 任意文件读取漏洞 漏洞描述 使用 MLflow 模型注册表托管 MLflow 开源项目的用户 mlflow server或者 mlflow ui使用早于 MLflow 2.2.1 的 MLflow 版...
2023年10月1日 10:01CVE-2023-5222: Viessmann Vitogate 300 – Hardcoded Password
漏洞标题 CVE-2023-5222: Viessmann Vitogate 300 - Hardcoded Password 漏洞描述 A critical vulnerability in Viessmann Vitogate 300 up to 2.1.3.0 allows attackers to authenticate using...
2023年5月26日 06:43CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting
漏洞标题 CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting 漏洞描述 WordPress Social Warfare plugin before 3.5.3 contains a cross-site scripting vulnerabilit...
2019年8月9日 06:27Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518)
漏洞标题 Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518) 漏洞描述 Atlassian Confluence是一款企业知识管理与协作软件。该漏洞存在于Atlassian Confluence...
2023年8月29日 11:47copyparty 低于1.8.2 版本存在任意文件读取漏洞(CVE-2023-37474)
漏洞标题 copyparty 低于1.8.2 版本存在任意文件读取漏洞(CVE-2023-37474) 漏洞描述 Copyparty是一个便携式文件服务器,copyparty 低于1.8.2 版本存在任意文件读取漏洞 PoC代码 暂无
2023年3月26日 11:28CVE-2021-38314: WordPress Redux Framework <=4.2.11 - Information Disclosure
漏洞标题 CVE-2021-38314: WordPress Redux Framework <=4.2.11 - Information Disclosure 漏洞描述 WordPress Redux Framework plugin through 4.2.11 is susceptible to information discl...
2021年11月29日 14:38CVE-2018-8823: PrestaShop Responsive Mega Menu Module – Remote Code Execution
漏洞标题 CVE-2018-8823: PrestaShop Responsive Mega Menu Module - Remote Code Execution 漏洞描述 The 'Responsive Mega Menu' module for PrestaShop is prone to a remote code...
2018年4月4日 05:13CVE-2017-17736: Kentico – Installer Privilege Escalation
漏洞标题 CVE-2017-17736: Kentico - Installer Privilege Escalation 漏洞描述 Kentico 9.0 before 9.0.51 and 10.0 before 10.0.48 are susceptible to a privilege escalation attack. An at...
2017年3月8日 09:52CVE-2015-6477: Nordex NC2 – Cross-Site Scripting
漏洞标题 CVE-2015-6477: Nordex NC2 - Cross-Site Scripting 漏洞描述 Nordex NC2 contains a cross-site scripting vulnerability which allows an attacker to execute arbitrary script cod...
2015年7月21日 17:19CVE-2016-10940: WordPress zm-gallery plugin 1.0 SQL Injection
漏洞标题 CVE-2016-10940: WordPress zm-gallery plugin 1.0 SQL Injection 漏洞描述 zm-gallery plugin 1.0 for WordPress is susceptible to SQL injection via the order parameter. PoC代码
2016年10月28日 09:15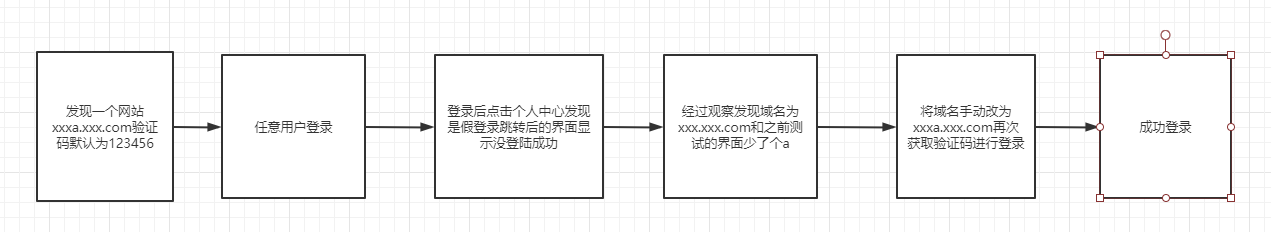
一次奇葩的任意用户登录
在安全小天地测试某src时发现一个界面,域名为xxxa.xxx.com,是一个登录界面,发现该界面支持使用手机号登录以及注册功能,测试后发现该网站使用的短信验证码为123456 因此用脚趾头都能想出来的...
2022年3月10日 23:36CVE-2022-28290: WordPress Country Selector <1.6.6 - Cross-Site Scripting
漏洞标题 CVE-2022-28290: WordPress Country Selector <1.6.6 - Cross-Site Scripting 漏洞描述 WordPress Country Selector plugin prior to 1.6.6 contains a cross-site scripting vulne...
2022年8月3日 05:48
微议管理系统后台文件上传漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 微议管理系统后台文件上传漏洞 微议管理系统存在后台文件上传漏洞,攻击者可以通过上传木马执行任意命令,获取服务器管理权限。 fofa:...
2026年2月13日 12:53
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

