
最新发布第49页

CVE-2014-3704: Drupal SQL Injection
漏洞标题 CVE-2014-3704: Drupal SQL Injection 漏洞描述 The expandArguments function in the database abstraction API in Drupal core 7.x before 7.32 does not properly construct prepar...
 2014年11月25日 21:40
CVE-2023-32563: Ivanti Avalanche – Remote Code Execution
漏洞标题 CVE-2023-32563: Ivanti Avalanche - Remote Code Execution 漏洞描述 An unauthenticated attacker could achieve the code execution through a RemoteControl server. PoC代码
2023年7月23日 12:21CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE
漏洞标题 CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE 漏洞描述 On BIG-IP versions 16.0.x before 16.0.1.1, 15.1.x before 15.1.2.1, 14.1.x before 14.1.4, 13.1.x before...
2021年4月9日 18:16CVE-2022-29349: kkFileView 4.0.0 – Cross-Site Scripting
漏洞标题 CVE-2022-29349: kkFileView 4.0.0 - Cross-Site Scripting 漏洞描述 kkFileView 4.0.0 contains multiple cross-site scripting vulnerabilities via the urls and currentUrl parame...
2022年12月22日 01:23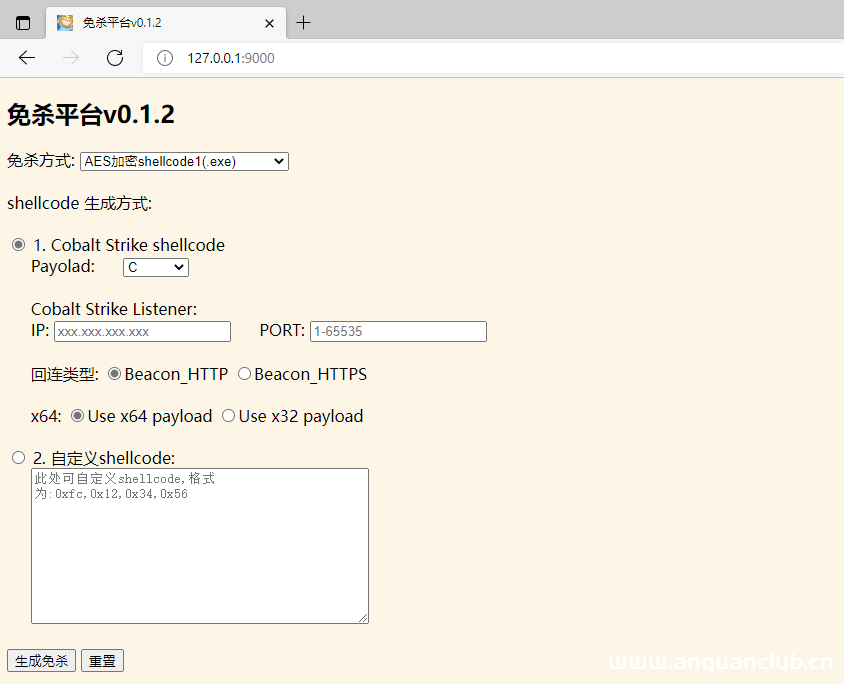
免杀基础教学
0x00 前言: 最近闲来无事搞了一个免杀平台玩儿玩儿,用于生成免杀Cobalt Strike木马和免杀加载一些其它shellcode(如msf、自定义等),这里就和大家分享一下免杀思路。 通过本篇文章你将学会: 杀...
2022年3月10日 23:36CVE-2023-6000: WordPress Popup Builder <= 4.2.3 - Unauthenticated Stored XSS
漏洞标题 CVE-2023-6000: WordPress Popup Builder <= 4.2.3 - Unauthenticated Stored XSS 漏洞描述 The Popup Builder WordPress plugin before 4.2.3 does not prevent simple visitors f...
2023年3月26日 16:42CVE-2021-34429: Eclipse Jetty – Information Disclosure
漏洞标题 CVE-2021-34429: Eclipse Jetty - Information Disclosure 漏洞描述 Eclipse Jetty 9.4.37-9.4.42, 10.0.1-10.0.5 and 11.0.1-11.0.5 are susceptible to improper authorization. URI...
2021年1月29日 22:55CVE-2023-6875: WordPress POST SMTP Mailer <= 2.8.7 - Authorization Bypass
漏洞标题 CVE-2023-6875: WordPress POST SMTP Mailer <= 2.8.7 - Authorization Bypass 漏洞描述 The POST SMTP Mailer – Email log, Delivery Failure Notifications and Best Mail SMTP ...
2023年4月11日 06:27CVE-2021-24926: WordPress Domain Check <1.0.17 - Cross-Site Scripting
漏洞标题 CVE-2021-24926: WordPress Domain Check <1.0.17 - Cross-Site Scripting 漏洞描述 WordPress Domain Check plugin before 1.0.17 contains a reflected cross-site scripting vul...
2021年8月5日 01:29CVE-2009-1496: Joomla! Cmimarketplace 0.1 – Local File Inclusion
漏洞标题 CVE-2009-1496: Joomla! Cmimarketplace 0.1 - Local File Inclusion 漏洞描述 Joomla! Cmimarketplace 0.1 is susceptible to local file inclusion because com_cmimarketplace allo...
2009年7月1日 02:01CVE-2017-17731: DedeCMS 5.7 – SQL Injection
漏洞标题 CVE-2017-17731: DedeCMS 5.7 - SQL Injection 漏洞描述 DedeCMS through 5.7 has SQL Injection via the $_FILES superglobal to plus/recommend.php. PoC代码
2017年12月30日 05:36CVE-2021-45046-DAST: Apache Log4j2 – Remote Code Injection
漏洞标题 CVE-2021-45046-DAST: Apache Log4j2 - Remote Code Injection 漏洞描述 Apache Log4j2 Thread Context Lookup Pattern is vulnerable to remote code execution in certain non-defau...
2021年9月20日 15:29Apache OFBiz CVE-2024-36104 鉴权绕过漏洞
漏洞标题 Apache OFBiz CVE-2024-36104 鉴权绕过漏洞 漏洞描述 Apache OFBiz 存在鉴权绕过漏洞,此漏洞是由于ProgramExport未充分验证用户输入的数据所导致的。 PoC代码 暂无
2024年3月22日 20:46CVE-2022-31101: Prestashop Blockwishlist 2.1.0 SQL Injection
漏洞标题 CVE-2022-31101: Prestashop Blockwishlist 2.1.0 SQL Injection 漏洞描述 Prestashop Blockwishlist module version 2.1.0 suffers from a remote authenticated SQL injection vulne...
2022年8月21日 08:55CVE-2021-42192: KONGA 0.14.9 – Privilege Escalation
漏洞标题 CVE-2021-42192: KONGA 0.14.9 - Privilege Escalation 漏洞描述 KONGA 0.14.9 allows attackers to set higher privilege users to full administration access. The attack vector i...
2021年6月6日 04:02CVE-2024-2876: WordPress Email Subscribers by Icegram Express – SQL Injection
漏洞标题 CVE-2024-2876: Wordpress Email Subscribers by Icegram Express - SQL Injection 漏洞描述 The Email Subscribers by Icegram Express - Email Marketing, Newsletters, Automation ...
2024年9月17日 01:21
2026年10月31日 11:45
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

