
最新发布第4页

CVE-2023-44012: mojoPortal v.2.7.0.0 – Cross-Site Scripting
漏洞标题 CVE-2023-44012: mojoPortal v.2.7.0.0 - Cross-Site Scripting 漏洞描述 Cross Site Scripting vulnerability in mojoPortal v.2.7.0.0 allows a remote attacker to execute arbitra...
 2023年10月6日 20:59
CVE-2024-22319: IBM Operational Decision Manager – JNDI Injection
漏洞标题 CVE-2024-22319: IBM Operational Decision Manager - JNDI Injection 漏洞描述 IBM Operational Decision Manager 8.10.3, 8.10.4, 8.10.5.1, 8.11, 8.11.0.1, and 8.12.0.1 is susce...
2024年8月15日 13:52CVE-2020-15227: Nette Framework – Remote Code Execution
漏洞标题 CVE-2020-15227: Nette Framework - Remote Code Execution 漏洞描述 Nette Framework versions before 2.0.19, 2.1.13, 2.2.10, 2.3.14, 2.4.16, and 3.0.6 are vulnerable to a code...
2020年4月23日 07:13CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
2024年7月24日 07:57CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
2019年12月5日 03:31CVE-2020-11529: Grav < 1.7 - Open Redirect
漏洞标题 CVE-2020-11529: Grav < 1.7 - Open Redirect 漏洞描述 Grav before 1.7 has an open redirect vulnerability via common/Grav.php. This is partially fixed in 1.6.23 and still ...
2020年11月25日 15:36CVE-2019-14470: WordPress UserPro 4.9.32 – Cross-Site Scripting
漏洞标题 CVE-2019-14470: WordPress UserPro 4.9.32 - Cross-Site Scripting 漏洞描述 WordPress UserPro 4.9.32 is vulnerable to reflected cross-site scripting because the Instagram PHP...
2019年5月6日 16:43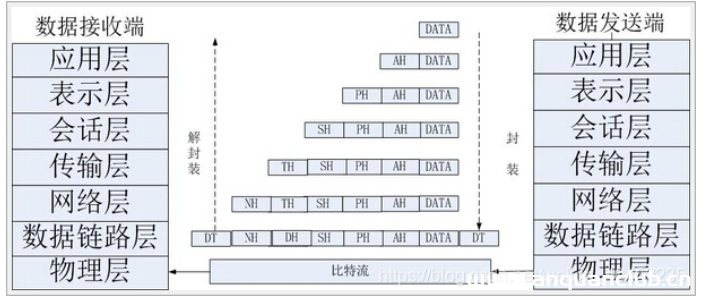
一文教你怎么搞定流量包(二)
前言 承接第一篇CTF流量分析,中间涉及部分知识内容,顺便自己再熟悉一遍,常规CTF或者说工控流量分析用到的工具wireshark之外似乎不怎涉及,,, 协议 TCP协议 TCP(Transmission Control Proto...
2022年3月10日 23:39CVE-2022-0735: GitLab CE/EE – Information Disclosure
漏洞标题 CVE-2022-0735: GitLab CE/EE - Information Disclosure 漏洞描述 GitLab CE/EE is susceptible to information disclosure. An attacker can access runner registration tokens usin...
2022年3月21日 10:39CVE-2018-16836: Rubedo CMS <=3.4.0 - Directory Traversal
漏洞标题 CVE-2018-16836: Rubedo CMS <=3.4.0 - Directory Traversal 漏洞描述 Rubedo CMS through 3.4.0 contains a directory traversal vulnerability in the theme component, allowing...
2018年7月2日 16:07CVE-2025-30220: GeoServer WFS – XXE Processing Vulnerability
漏洞标题 CVE-2025-30220: GeoServer WFS - XXE Processing Vulnerability 漏洞描述 GeoServer Web Feature Service (WFS) is vulnerable to an XML External Entity (XXE) processing attack d...
2025年8月16日 12:14CVE-2025-34026: Versa Concerto Actuator Endpoint – Authentication Bypass
漏洞标题 CVE-2025-34026: Versa Concerto Actuator Endpoint - Authentication Bypass 漏洞描述 An authentication bypass vulnerability affected the Spring Boot Actuator endpoints in Ver...
2025年11月15日 21:02Artica Pandora FMS未授权访问(CVE-2020-8497)
漏洞标题 Artica Pandora FMS未授权访问(CVE-2020-8497) 漏洞描述 Artica Pandora FMS是西班牙Artica公司的一套监控系统,在 Artica Pandora FMS 到 7.42中,未经身份验证的攻击者可以读取聊天...
2020年2月4日 09:41
x-ui面板爬虫爬取及登陆分享
前言 最近无意间翻到了以前的一些文章,其中这个x-ui面板还蛮有意思的 首先他有固定特征,按脚本一键安装之后,默认端口就是54321,默认账号:admin,默认密码:admin 虽然后台都有地方修改,但...

 2024年6月6日 14:27
CVE-2025-61757: Oracle Identity Manager REST WebServices – Authentication Bypass
漏洞标题 CVE-2025-61757: Oracle Identity Manager REST WebServices - Authentication Bypass 漏洞描述 Vulnerability in the Identity Manager product of Oracle Fusion Middleware (compon...
2025年9月8日 05:17CVE-2023-6389: WordPress Toolbar <= 2.2.6 - Open Redirect
漏洞标题 CVE-2023-6389: WordPress Toolbar <= 2.2.6 - Open Redirect 漏洞描述 The plugin redirects to any URL via the "wptbto" parameter. This makes it possible for unau...
2023年5月24日 00:34
2026年10月13日 11:45
2026年10月12日 11:45
2026年10月11日 11:45
2026年10月10日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

