
最新发布第500页

CVE-2015-7245: D-Link DVG-N5402SP – Local File Inclusion
漏洞标题 CVE-2015-7245: D-Link DVG-N5402SP - Local File Inclusion 漏洞描述 D-Link DVG-N5402SP is susceptible to local file inclusion in products with firmware W1000CN-00, W1000CN-0...
 2015年12月12日 09:50
Apache RocketMQ CVE-2023-37582 远程代码执行漏洞
漏洞标题 Apache RocketMQ CVE-2023-37582 远程代码执行漏洞 漏洞描述 Apache RocketMQ CVE-2023-37582 远程 PoC代码 暂无
2023年5月24日 23:28CVE-2015-3337: Elasticsearch – Local File Inclusion
漏洞标题 CVE-2015-3337: Elasticsearch - Local File Inclusion 漏洞描述 Elasticsearch before 1.4.5 and 1.5.x before 1.5.2 allows remote attackers to read arbitrary files via unspecif...
2015年9月3日 07:53
PDF解析器html/XSS 实现SSRF
上次安全小天地审核整理SSRF的时候找我沟通,聊到了PDF的SSRF,当时答应了找找之前的存档写个文档。遂写下改小菜文。大佬们勿喷。(文章写于去年,随便记录的文章,可能存在逻辑或者图片的丢失...
2022年3月10日 23:37CVE-2020-16846: SaltStack Shell Injection
漏洞标题 CVE-2020-16846: SaltStack Shell Injection 漏洞描述 An issue was discovered in SaltStack Salt through 3002. Sending crafted web requests to the Salt API, with the SSH clien...
2020年11月5日 13:18CVE-2024-37728: OfficeWeb365 Indexs Interface – Arbitrary File Read
漏洞标题 CVE-2024-37728: OfficeWeb365 Indexs Interface - Arbitrary File Read 漏洞描述 There is any file reading in the officeWeb365 Indexs interface. PoC代码
2024年3月4日 21:57Certain WSO2 CVE-2022-29464远程代码执行漏洞
漏洞标题 Certain WSO2 CVE-2022-29464远程代码执行漏洞 漏洞描述 Certain WSO2存在远程代码执行漏洞,此漏洞是缺乏校验导致的。 PoC代码 暂无
2022年3月5日 20:55CVE-2024-3469: GP Premium <= 2.4.0 - Cross-Site Scripting
漏洞标题 CVE-2024-3469: GP Premium <= 2.4.0 - Cross-Site Scripting 漏洞描述 The GP Premium plugin for WordPress up to 2.4.0 is vulnerable to reflected XSS via the 'message&...
2024年1月1日 19:34Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776)
漏洞标题 Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776) 漏洞描述 【漏洞对象】Apache Struts 2 【涉及版本】2.3-2.3.34,2.5-2.5.16 【漏洞描述】软件存在输入验证漏洞,远程攻击者可...
2018年12月22日 04:47CVE-2021-45092: Thinfinity Iframe Injection
漏洞标题 CVE-2021-45092: Thinfinity Iframe Injection 漏洞描述 A vulnerability exists in Thinfinity VirtualUI in a function located in /lab.html reachable which by default could all...
2021年7月29日 00:49Atlassian Jira XSS(CVE-2018-20824)
漏洞标题 Atlassian Jira XSS(CVE-2018-20824) 漏洞描述 Jira7.13.1版本之前的WallboardServlet资源允许远程攻击者通过cyclePeriod参数中的跨站点脚本漏洞注入任意HTML或JavaScript。 PoC代码 ...
2018年2月9日 20:22CVE-2021-4449: ZoomSounds Plugin – Unauthenticated Arbitrary File Upload
漏洞标题 CVE-2021-4449: ZoomSounds Plugin - Unauthenticated Arbitrary File Upload 漏洞描述 ZoomSounds plugin for WordPress contains a file upload vulnerability in savepng.php PoC代...
2021年12月13日 02:50CVE-2009-1558: Cisco Linksys WVC54GCA 1.00R22/1.00R24 – Local File Inclusion
漏洞标题 CVE-2009-1558: Cisco Linksys WVC54GCA 1.00R22/1.00R24 - Local File Inclusion 漏洞描述 Cisco Linksys WVC54GCA 1.00R22/1.00R24 is susceptible to local file inclusion in adm/...
2009年5月5日 09:22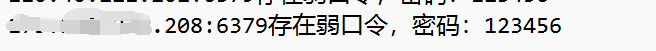
【实战】redis未授权实现ssh登录
0x01 漏洞描述 Redis 默认情况下,会绑定在 0.0.0.0:6379,如果没有进行采用相关的策略,比如添加防火墙规则避免其他非信任来源 ip 访问等,这样将会将 Redis 服务暴露到公网上,如果在没...

 2023年4月13日 08:15
CVE-2023-30013: TOTOLink – Unauthenticated Command Injection
漏洞标题 CVE-2023-30013: TOTOLink - Unauthenticated Command Injection 漏洞描述 TOTOLINK X5000R V9.1.0u.6118_B20201102 and V9.1.0u.6369_B20230113 contain a command insertion vulnera...
2023年11月2日 21:41CVE-2021-24997: WordPress Guppy <=1.1 - Information Disclosure
漏洞标题 CVE-2021-24997: WordPress Guppy <=1.1 - Information Disclosure 漏洞描述 WordPress Guppy plugin through 1.1 is susceptible to an API disclosure vulnerability. This can a...
2021年6月9日 19:17
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

