
最新发布第507页

CVE-2017-17762: Episerver 7 – Blind XML External Entity Injection
漏洞标题 CVE-2017-17762: Episerver 7 - Blind XML External Entity Injection 漏洞描述 Episerver 7 patch 4 and earlier contains an XML external entity (XXE) caused by processing craft...
 2017年5月2日 02:03
CVE-2014-4536: Infusionsoft Gravity Forms Add-on < 1.5.7 - Cross-Site Scripting
漏洞标题 CVE-2014-4536: Infusionsoft Gravity Forms Add-on < 1.5.7 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in tests/notAuto_test_ContactServ...
2014年3月28日 02:34CVE-2025-49001: Dataease JWT 认证绕过漏洞
漏洞标题 CVE-2025-49001: Dataease JWT 认证绕过漏洞 漏洞描述 CVE-2025-49001 是由于JWT校验机制错误导致攻击者可伪造JWT令牌绕过身份验证流程 fofa: body="/js/index-0.0.0-dataease.js...
2025年9月7日 10:26CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
2024年6月1日 21:54
Sapido 多款路由器 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 Sapido 多款路由器 远程命令执行漏洞 SAPIDO傻多,追求台湾制造的严谨品质,发展智慧型网路产品,让使用者以最小的花费满足多样的需求...
2026年2月13日 12:53Atlassian Jira未授权访问 (CVE-2020-14179)
漏洞标题 Atlassian Jira未授权访问 (CVE-2020-14179) 漏洞描述 该漏洞源于Jira Server and DataCenter允许远程、未经身份验证的攻击者通过/secure/QueryComponent!Default中的一个信息泄露漏洞...
2020年4月2日 13:06CVE-2021-3654: Nova noVNC – Open Redirect
漏洞标题 CVE-2021-3654: Nova noVNC - Open Redirect 漏洞描述 Nova noVNC contains an open redirect vulnerability. An attacker can redirect a user to a malicious site and possibly obt...
2021年3月17日 06:39CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
漏洞标题 CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover 漏洞描述 The Motors theme for WordPress is vulnerable to pri...
2025年3月22日 18:47CVE-2022-0786: WordPress KiviCare <2.3.9 - SQL Injection
漏洞标题 CVE-2022-0786: WordPress KiviCare <2.3.9 - SQL Injection 漏洞描述 WordPress KiviCare plugin before 2.3.9 contains a SQL injection vulnerability. The plugin does not san...
2022年12月15日 19:09CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
2021年6月2日 15:48CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting
漏洞标题 CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting 漏洞描述 WordPress Social Warfare plugin before 3.5.3 contains a cross-site scripting vulnerabilit...
2019年4月7日 13:05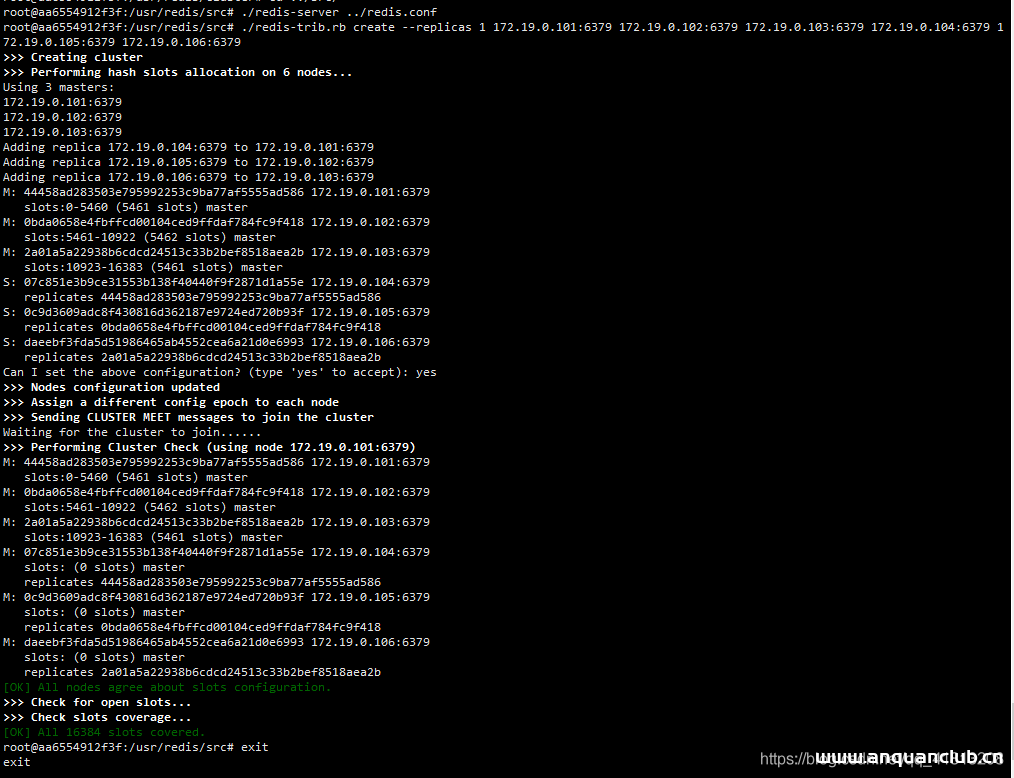
基于docker搭建redis集群的方法_docker
这篇文章主要介绍了基于docker搭建redis集群的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 下载redis镜像 docker pull yyyyttttwwww/redi...
2022年11月20日 20:17CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure 漏洞描述 DataEase, an open source data visualization and analysis tool, has a database configuration ...
2024年9月29日 18:27CVE-2024-22207: Fastify Swagger-UI – Information Disclosure
漏洞标题 CVE-2024-22207: Fastify Swagger-UI - Information Disclosure 漏洞描述 fastify-swagger-ui is a Fastify plugin for serving Swagger UI. Prior to 2.1.0, the default configurati...
2024年3月11日 21:45CVE-2023-43261: Milesight Routers – Information Disclosure
漏洞标题 CVE-2023-43261: Milesight Routers - Information Disclosure 漏洞描述 A critical security vulnerability has been identified in Milesight Industrial Cellular Routers, comprom...
2023年2月7日 04:27CVE-2022-1952: WordPress eaSYNC Booking <1.1.16 - Arbitrary File Upload
漏洞标题 CVE-2022-1952: WordPress eaSYNC Booking <1.1.16 - Arbitrary File Upload 漏洞描述 WordPress eaSync Booking plugin bundle for hotel, restaurant and car rental before 1.1....
2022年7月14日 06:09
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

