
最新发布第509页

CVE-2020-10199: Nexus Repository before 3.21.2 allows JavaEL Injection
漏洞标题 CVE-2020-10199: Nexus Repository before 3.21.2 allows JavaEL Injection 漏洞描述 漏洞触发需要任意账户权限 body="Nexus Repository Manager" app="Nexus-Reposito...
 2020年2月14日 04:14
CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE
漏洞标题 CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE 漏洞描述 On BIG-IP versions 16.0.x before 16.0.1.1, 15.1.x before 15.1.2.1, 14.1.x before 14.1.4, 13.1.x before...
2021年6月28日 04:00Atlassian Confluence OGNL注入漏洞(CVE-2022-26134)
漏洞标题 Atlassian Confluence OGNL注入漏洞(CVE-2022-26134) 漏洞描述 Atlassian Confluence OGNL注入漏洞(CVE-2022-26134) PoC代码 暂无
2022年5月30日 08:59
EasyShell更新日志-V2.8.3已更新【20261018】
程序激活流程参考以下文章,直接点击右侧目录树跳转激活码教程即可 如遇程序启动失败的建议尝试一下命令 该情况主要是使用2.0之前版本,程序加密秘钥不兼容导致的macOS : rm -rf ~/Library/Appl...

 2026年10月18日 20:40
CVE-2023-45852: Viessmann Vitogate 300 – Remote Code Execution
漏洞标题 CVE-2023-45852: Viessmann Vitogate 300 - Remote Code Execution 漏洞描述 In Vitogate 300 2.1.3.0, /cgi-bin/vitogate.cgi allows an unauthenticated attacker to bypass authent...
2023年12月13日 21:10Apache Superset Cookie 权限绕过漏洞(CVE-2023-27524)
漏洞标题 Apache Superset Cookie 权限绕过漏洞(CVE-2023-27524) 漏洞描述 Apache Superset 是一个开源的现代数据探索和可视化平台。Apache Superset Cookie 存在权限绕过漏洞,攻击者可通过...
2023年8月22日 03:22CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 – SQL Injection
漏洞标题 CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 - SQL Injection 漏洞描述 PrestaShop leocustomajax 1.0 and 1.0.0 are vulnerable to SQL Injection via modules/leocus...
2023年5月7日 08:48CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected)
漏洞标题 CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected) 漏洞描述 The WordPress Qwizcards plugin before version 3.95 does not sanitise and escape th...
2025年8月14日 21:51CVE-2010-1469: Joomla! Component JProject Manager 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1469: Joomla! Component JProject Manager 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Ternaria Informatica JProject Manager (com...
2010年1月17日 03:50CVE-2024-21683: Atlassian Confluence Data Center and Server – Remote Code Execution
漏洞标题 CVE-2024-21683: Atlassian Confluence Data Center and Server - Remote Code Execution 漏洞描述 Detects a Remote Code Execution vulnerability in Confluence Data Center and Se...
2024年5月22日 05:50Apache OFBiz CVE-2024-38856 未授权代码执行漏洞
漏洞标题 Apache OFBiz CVE-2024-38856 未授权代码执行漏洞 漏洞描述 Apache OFBiz存在未授权代码执行漏洞,该漏洞是由于ProgramExport接口对用户的权限校验不当导致的。 PoC代码 暂无
2024年9月27日 22:26
bugbounty技巧聚合20210924
漏洞报告 【$250】通过包含多个 unicode 字符(0x0e 和 0x0f)的消息对 Android 的 LINE 客户端进行 DoS http://hackerone.com/reports/1058383 【$500】MacOS 版本的 Facebook Messenger 包含...
2022年3月10日 23:39CVE-2025-53364: Parse Server – GraphQL Schema Information Disclosure
漏洞标题 CVE-2025-53364: Parse Server - GraphQL Schema Information Disclosure 漏洞描述 The Parse Server GraphQL API previously allowed public access to the GraphQL schema without r...
2025年6月12日 07:35CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
2012年3月17日 03:09CVE-2022-28219: Zoho ManageEngine ADAudit Plus <7600 - XML Entity Injection/Remote Code Execution
漏洞标题 CVE-2022-28219: Zoho ManageEngine ADAudit Plus <7600 - XML Entity Injection/Remote Code Execution 漏洞描述 Zoho ManageEngine ADAudit Plus before version 7060 is vulnera...
2022年1月4日 08:07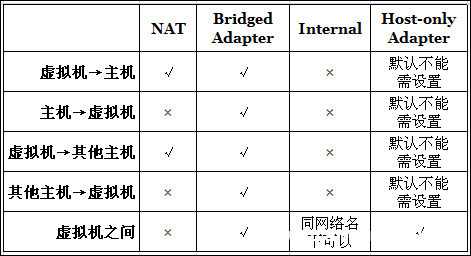
virtualbox centos7 nat+host-only方式联网踩坑总结_VirtualBox
最近公司需要配置服务器,要求centos虚拟机可以yum install、docker拉互联网镜像,因此需要访问互联网。那么本文就介绍一下virtualbox centos7 nat+host-only方式联网踩坑总结,感兴趣的可以了...
2022年6月15日 08:45
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53
2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

