
最新发布第510页

CVE-2023-34362: MOVEit Transfer – Remote Code Execution
漏洞标题 CVE-2023-34362: MOVEit Transfer - Remote Code Execution 漏洞描述 In Progress MOVEit Transfer before 2021.0.6 (13.0.6), 2021.1.4 (13.1.4), 2022.0.4 (14.0.4), 2022.1.5 (14.1...
 2023年4月2日 05:41
CVE-2023-49105: OwnCloud – WebDAV API Authentication Bypass
漏洞标题 CVE-2023-49105: OwnCloud - WebDAV API Authentication Bypass 漏洞描述 An issue was discovered in ownCloud owncloud/core before 10.13.1. An attacker can access, modify, or d...
2023年8月25日 18:42CVE-2020-35984: Rukovoditel <= 2.7.2 - Cross Site Scripting
漏洞标题 CVE-2020-35984: Rukovoditel <= 2.7.2 - Cross Site Scripting 漏洞描述 A stored cross site scripting (XSS) vulnerability in the 'Users Alerts' feature of Rukovo...
2020年5月1日 08:06CVE-2023-40749: PHPJabbers Food Delivery Script v3.0 – SQL Injection
漏洞标题 CVE-2023-40749: PHPJabbers Food Delivery Script v3.0 - SQL Injection 漏洞描述 PHPJabbers Food Delivery Script v3.0 is vulnerable to SQL Injection in the "column"...
2023年2月28日 01:21CVE-2023-38950: ZKTeco BioTime v8.5.5 – Path Traversal
漏洞标题 CVE-2023-38950: ZKTeco BioTime v8.5.5 - Path Traversal 漏洞描述 A path traversal vulnerability in the iclock API of ZKTeco BioTime v8.5.5 allows unauthenticated attackers ...
2023年12月13日 17:56CVE-2025-2075: Uncanny Automator <= 6.3.0.2 - Missing Authorization to Authenticated (Subscriber+) Privilege Escalation
漏洞标题 CVE-2025-2075: Uncanny Automator <= 6.3.0.2 - Missing Authorization to Authenticated (Subscriber+) Privilege Escalation 漏洞描述 The Uncanny Automator - Easy Automation...
2025年4月8日 13:20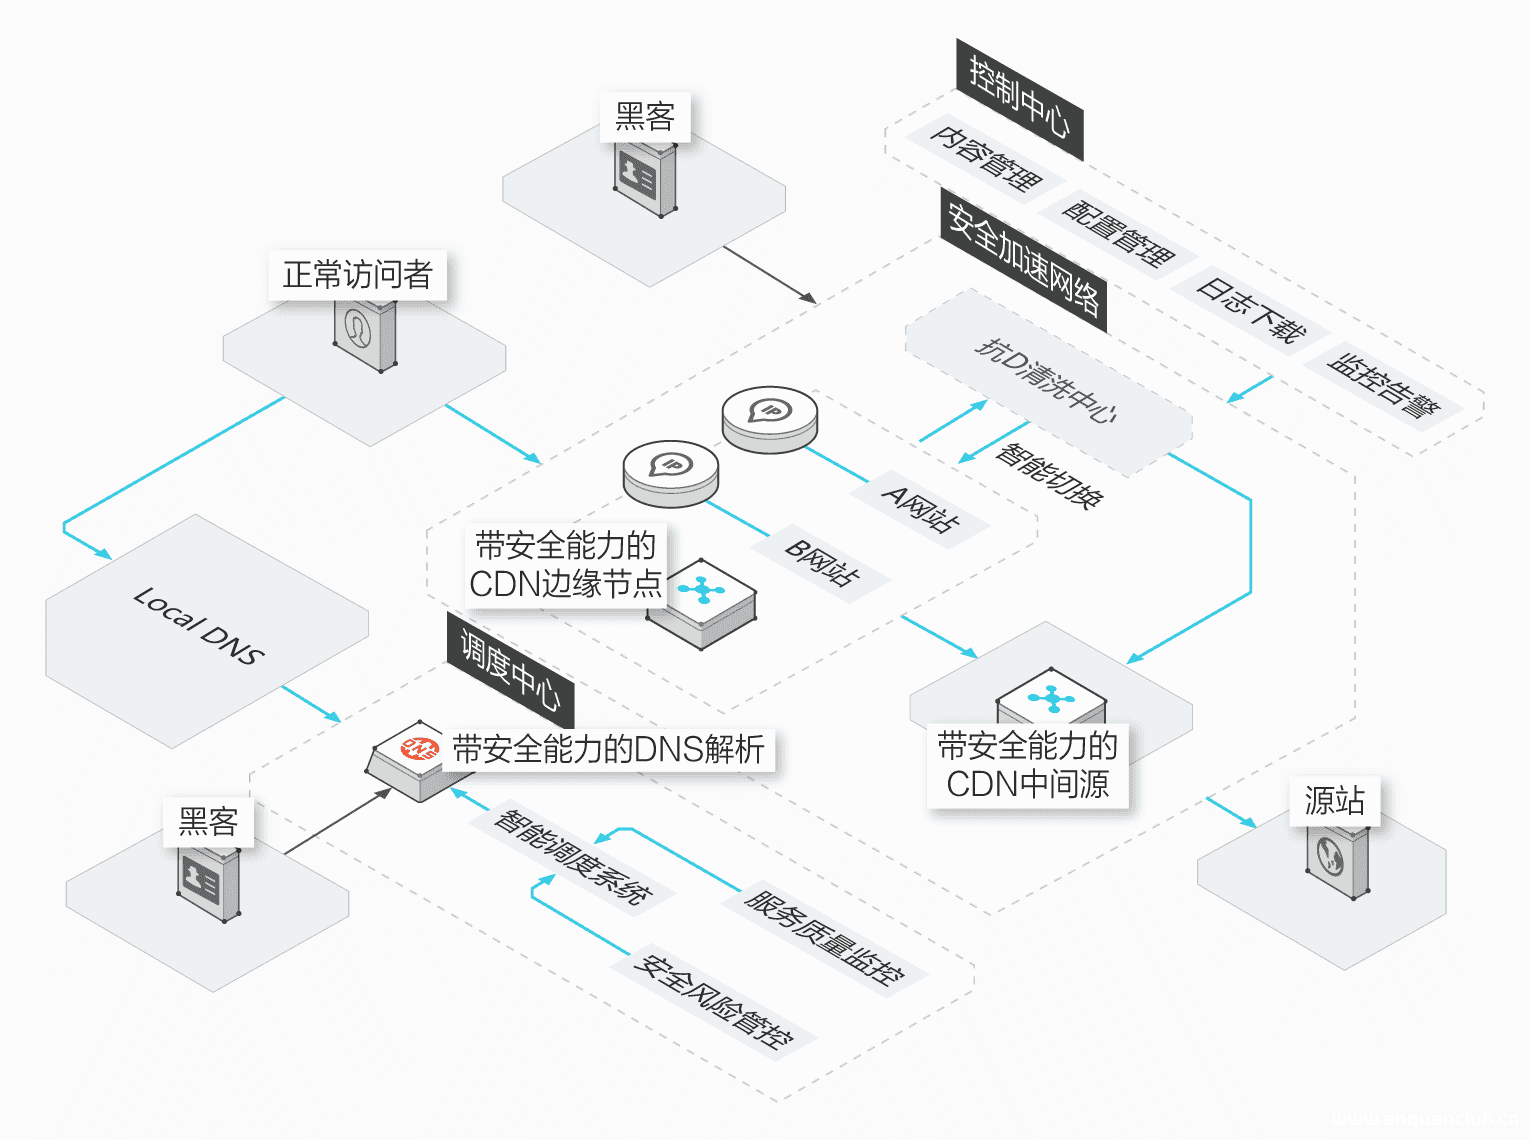
网站加速之CDN、SCDN、DCDN区别在哪?如何选择?_服务器其它
阿里云CDN(内容分发网络)是用户比较熟悉的,那么什么是SCDN?SCDN和CDN有什么区别? 1、CDN 是网站中最常用的加速功能。通过分布式服务器布局,把网站业务内容缓存到各地的云服务器中,供访客...
2024年6月7日 20:30CVE-2023-2272: Tiempo.com <= 0.1.2 - Cross-Site Scripting
漏洞标题 CVE-2023-2272: Tiempo.com <= 0.1.2 - Cross-Site Scripting 漏洞描述 Tiempo.com before 0.1.2 is susceptible to cross-site scripting via the page parameter due to insuffic...
2023年1月30日 19:03CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion 漏洞描述 The HUSKY – Products Filter Professiona...
2025年9月13日 11:54CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
2022年8月25日 09:51CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload
漏洞标题 CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload 漏洞描述 Arbitrary File Upload vulnerability in WordPress Royal Elementor Addon...
2023年7月21日 14:53CVE-2021-21402: Jellyfin prior to 10.7.0 Unauthenticated Arbitrary File Read
漏洞标题 CVE-2021-21402: Jellyfin prior to 10.7.0 Unauthenticated Arbitrary File Read 漏洞描述 Jellyfin is a Free Software Media System. In Jellyfin before version 10.7.1, with cer...
2021年12月15日 10:53CVE-2022-33965: WordPress Visitor Statistics <=5.7 - SQL Injection
漏洞标题 CVE-2022-33965: WordPress Visitor Statistics <=5.7 - SQL Injection 漏洞描述 WordPress Visitor Statistics plugin through 5.7 contains multiple unauthenticated SQL inject...
2022年3月16日 21:13
bugbounty技巧聚合20211129
漏洞报告 【MCUboot】private keys exposed on the GitHub repository http://hackerone.com/reports/1234531 【XVIDEOS】CSRF on delete friend requests - Not protected with CSRF Token htt...
2022年3月10日 23:38CVE-2025-6934: The Opal Estate Pro – Property Management <= 1.7.5 - Unauthenticated Privilege Escalation
漏洞标题 CVE-2025-6934: The Opal Estate Pro – Property Management <= 1.7.5 - Unauthenticated Privilege Escalation 漏洞描述 The Opal Estate Pro plugin (≤ 1.7.5) is vulnerable t...
2025年6月2日 11:57CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion 漏洞描述 The News & Blog Designer Pack WordPre...
2023年8月30日 18:12
2026年9月30日 11:45
2026年9月29日 11:45
2026年9月28日 11:45
2026年9月27日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

