
最新发布第511页

CVE-2021-24862: WordPress RegistrationMagic <5.0.1.6 - Authenticated SQL Injection
漏洞标题 CVE-2021-24862: WordPress RegistrationMagic <5.0.1.6 - Authenticated SQL Injection 漏洞描述 WordPress RegistrationMagic plugin before 5.0.1.6 contains an authenticated ...
 2021年7月7日 10:30
CVE-2017-14135: OpenDreambox 2.0.0 – Remote Code Execution
漏洞标题 CVE-2017-14135: OpenDreambox 2.0.0 - Remote Code Execution 漏洞描述 OpenDreambox 2.0.0 is susceptible to remote code execution via the webadmin plugin. Remote attackers ca...
2017年4月5日 00:04
bugbounty技巧聚合20211110
漏洞报告 【Internet Bug Bounty 4,000 USD】Path traversal and file disclosure vulnerability in Apache HTTP Server 2.4.49 http://hackerone.com/reports/1394916 【Rockset】Failure to I...
2022年3月10日 23:33CVE-2024-32238: H3C ER8300G2-X – Password Disclosure
漏洞标题 CVE-2024-32238: H3C ER8300G2-X - Password Disclosure 漏洞描述 H3C ER8300G2-X is vulnerable to Incorrect Access Control. The password for the router's management syste...
2024年3月27日 22:15CVE-2016-1000137: WordPress Hero Maps Pro 2.1.0 – Cross-Site Scripting
漏洞标题 CVE-2016-1000137: WordPress Hero Maps Pro 2.1.0 - Cross-Site Scripting 漏洞描述 WordPress Hero Maps Pro 2.1.0 contains a reflected cross-site scripting vulnerability which...
2016年4月6日 12:56CVE-2023-29923: PowerJob <=4.3.2 - Unauthenticated Access
漏洞标题 CVE-2023-29923: PowerJob <=4.3.2 - Unauthenticated Access 漏洞描述 PowerJob V4.3.1 is vulnerable to Insecure Permissions. via the list job interface. PoC代码
2023年4月23日 18:30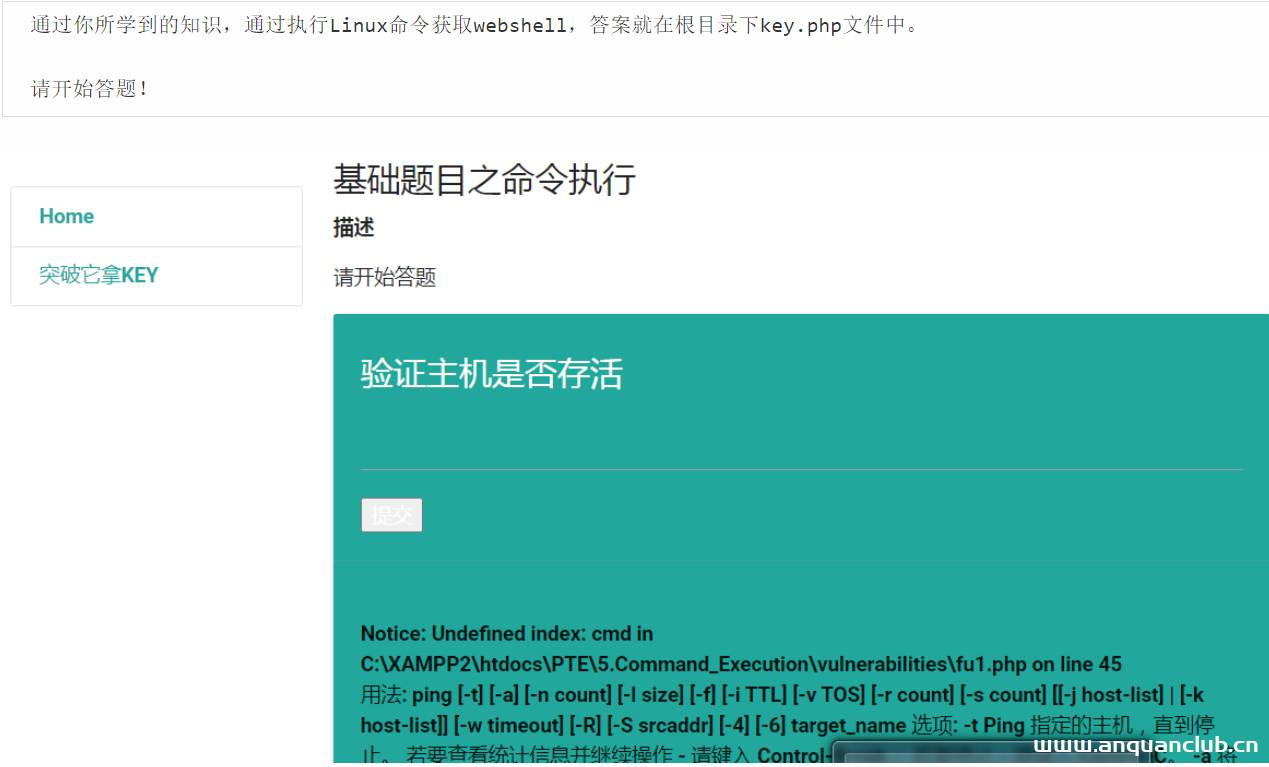
CISP-PTE认证中遇到的CTF题目及WP(一)
0x01 前言 本来想着先补充一文教你xxxxxx(三)的,这到过年了项目还是有点多,报告都没写完,还是先放这篇文章吧,,,,,,CISP-PTE中的题目,毕竟网上的资料比较少,因为考这个贵呀,,大家...
2022年3月10日 23:33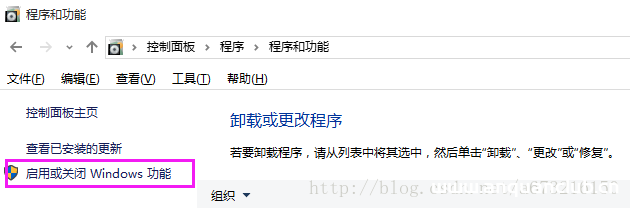
Win10下配置IIS10并支持调试ASP程序的步骤_win服务器
今天临时需要在Win10下配置IIS10并支持调试ASP程序的步骤,不像windows服务器版本比较好找,这个得找到放风,这里九尾大家分享一下需要的朋友可以参考下 微软公司的IIS IIS(Internet Informatio...
2024年2月12日 20:00Centos7的Firewalld防火墙基础命令详解_Linux
这篇文章主要介绍了Centos7的Firewalld防火墙基础命令详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 一、Lin...
2026年8月12日 11:45CVE-2007-4556: OpenSymphony XWork/Apache Struts2 – Remote Code Execution S2-001
漏洞标题 CVE-2007-4556: OpenSymphony XWork/Apache Struts2 - Remote Code Execution S2-001 漏洞描述 Apache Struts support in OpenSymphony XWork before 1.2.3, and 2.x before 2.0.4, as...
2007年5月6日 22:27CVE-2021-24442: WordPress Polls Widget < 1.5.3 - SQL Injection
漏洞标题 CVE-2021-24442: Wordpress Polls Widget < 1.5.3 - SQL Injection 漏洞描述 The Poll, Survey, Questionnaire and Voting system WordPress plugin before 1.5.3 did not sanitise...
2021年12月9日 05:10
防护措施 – 关键信息基础设施安全保护 – hvv面试题
什么是安全加固 为什么要做安全加固 法律法规利益保护安全检查自身安全 安全加固划分 安全加固准备阶段 基本要素准备 确定安全加固的范围;确定安全加固的时间进度;确定安全加固的人力资源与沟...

 2022年6月30日 18:12
Docker服务器存储资源池不足的问题解决_docker
这篇文章主要给大家介绍了关于Docker服务器存储资源池不足的问题解决方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习...
2023年2月18日 20:10CVE-2025-34141: ETQ Reliance – Reflected XSS via SQLConverterServlet
漏洞标题 CVE-2025-34141: ETQ Reliance - Reflected XSS via SQLConverterServlet 漏洞描述 A reflected cross-site scripting (XSS) vulnerability exists in ETQ Reliance CG (legacy) platf...
2025年3月3日 01:42CVE-2012-6499: WordPress Plugin Age Verification v0.4 – Open Redirect
漏洞标题 CVE-2012-6499: WordPress Plugin Age Verification v0.4 - Open Redirect 漏洞描述 Open redirect vulnerability in age-verification.php in the Age Verification plugin 0.4 and e...
2012年11月1日 07:58CVE-2022-48323: Sunflower Simple and Personal 1.0.1.43315 – Remote Code Execution
漏洞标题 CVE-2022-48323: Sunflower Simple and Personal 1.0.1.43315 - Remote Code Execution 漏洞描述 Sunlogin Sunflower Simplified (aka Sunflower Simple and Personal) 1.0.1.43315 is...
2022年4月10日 23:44
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

