
最新发布第514页

CVE-2018-19386: SolarWinds Database Performance Analyzer 11.1.457 – Cross-Site Scripting
漏洞标题 CVE-2018-19386: SolarWinds Database Performance Analyzer 11.1.457 - Cross-Site Scripting 漏洞描述 SolarWinds Database Performance Analyzer 11.1.457 contains a reflected cr...
 2018年12月12日 20:45
CVE-2021-39312: WordPress True Ranker <2.2.4 - Local File Inclusion
漏洞标题 CVE-2021-39312: WordPress True Ranker <2.2.4 - Local File Inclusion 漏洞描述 WordPress True Ranker before version 2.2.4 allows sensitive configuration files such as wp-...
2021年8月5日 01:29CVE-2010-1315: Joomla! Component webERPcustomer – Local File Inclusion
漏洞标题 CVE-2010-1315: Joomla! Component webERPcustomer - Local File Inclusion 漏洞描述 A directory traversal vulnerability in weberpcustomer.php in the webERPcustomer (com_weberp...
2010年9月7日 14:18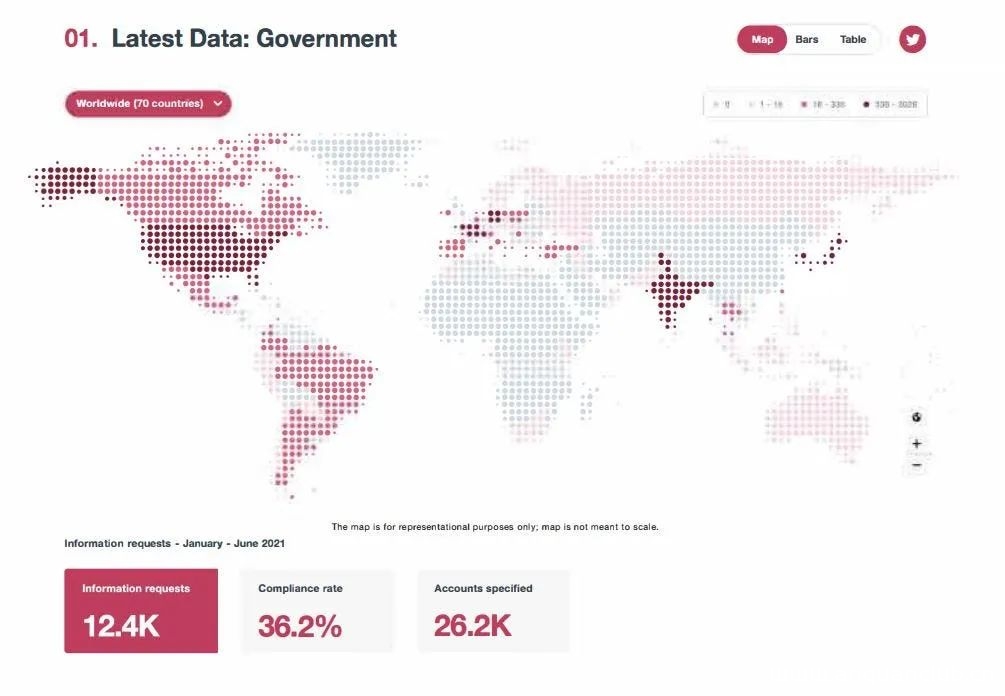
推特透明度报告:美国政府索要的信息最多
1月25日,推特Twitter透明度中心公布了一份透明度报告,以让用户了解世界范围内各国政府向他们提出的要求。 推特认为透明度有利于保护持续受到威胁的开放互联网,并且对于追究公司和政府的...
2022年3月10日 23:40
(2)docker安装教程
前言 通过上一篇文章,我们建议了解了一下,为什么使用容器,接下来我们学习一下docker的安装 安装教程 首先我们进入docker官方安装文档:http://docs.docker.com/ 我们这里选择安装在centos7的...

 2023年2月13日 14:18
CVE-2018-18809: TIBCO JasperReports Library – Directory Traversal
漏洞标题 CVE-2018-18809: TIBCO JasperReports Library - Directory Traversal 漏洞描述 The default server implementation of TIBCO Software Inc.'s TIBCO JasperReports Library, TIB...
2018年1月18日 16:44CVE-2025-56266: Avigilon ACM – Host Header Injection
漏洞标题 CVE-2025-56266: Avigilon ACM - Host Header Injection 漏洞描述 A Host Header Injection vulnerability in Avigilon ACM v7.10.0.20 allows attackers to execute arbitrary code v...
2025年2月22日 12:29CVE-2024-45488: SafeGuard for Privileged Passwords < 7.5.2 - Authentication Bypass
漏洞标题 CVE-2024-45488: SafeGuard for Privileged Passwords < 7.5.2 - Authentication Bypass 漏洞描述 One Identity Safeguard for Privileged Passwords before 7.5.2 allows unauthor...
2024年11月18日 03:01CVE-2016-10134: Zabbix – SQL Injection
漏洞标题 CVE-2016-10134: Zabbix - SQL Injection 漏洞描述 Zabbix before 2.2.14 and 3.0 before 3.0.4 allows remote attackers to execute arbitrary SQL commands via the toggle_ids arra...
2016年12月14日 23:59
bugbounty技巧聚合20210906
漏洞报告 #1145044 Holes in EndpointSlice Validation Enable Host Network Hijack #1095612 Node Validation Admission does not observe all oldObject fields Mail.ru #1241637 information...
2022年3月10日 23:32CVE-2023-27640: PrestaShop tshirtecommerce – Directory Traversal
漏洞标题 CVE-2023-27640: PrestaShop tshirtecommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年2月19日 05:43CVE-2022-0591: Formcraft3 <3.8.28 - Server-Side Request Forgery
漏洞标题 CVE-2022-0591: Formcraft3 <3.8.28 - Server-Side Request Forgery 漏洞描述 Formcraft3 before version 3.8.2 does not validate the URL parameter in the formcraft3_get AJAX ...
2022年11月26日 21:40CVE-2022-0595: WordPress Contact Form 7 <1.3.6.3 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-0595: WordPress Contact Form 7 <1.3.6.3 - Stored Cross-Site Scripting 漏洞描述 WordPress Contact Form 7 before 1.3.6.3 contains an unauthenticated stored cross...
2022年4月13日 22:39Apache RocketMQ CVE-2023-33246 远程代码执行漏洞
漏洞标题 Apache RocketMQ CVE-2023-33246 远程代码执行漏洞 漏洞描述 Apache RocketMQ存在远程代码执行漏洞,此漏洞是由于对权限和用户输入校验不当导致的。 PoC代码 暂无
2023年9月18日 20:09CVE-2010-2033: Joomla! Percha Categories Tree 0.6 – Local File Inclusion
漏洞标题 CVE-2010-2033: Joomla! Percha Categories Tree 0.6 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Percha Fields Attach (com_perchafieldsattach) ...
2010年6月4日 22:27CVE-2018-7490: uWSGI PHP Plugin Directory Traversal
漏洞标题 CVE-2018-7490: uWSGI PHP Plugin Directory Traversal 漏洞描述 uWSGI PHP Plugin Directory Traversal fofa: app="uWSGI" shodan: http.html:"uWSGI" PoC代码
2018年2月14日 00:28
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

