
最新发布第515页

bugbounty技巧聚合20211008
时事热点 上古杂志Phrack更新 ? http://www.phrack.org/issues/70/1.html 实时流媒体视频平台Twitch的敏感数据遭泄露 http://mp.weixin.qq.com/s/Vu5JaUcSwEJx38xsRrTtCQ 下载地址:http://noth...
 2022年3月10日 23:32
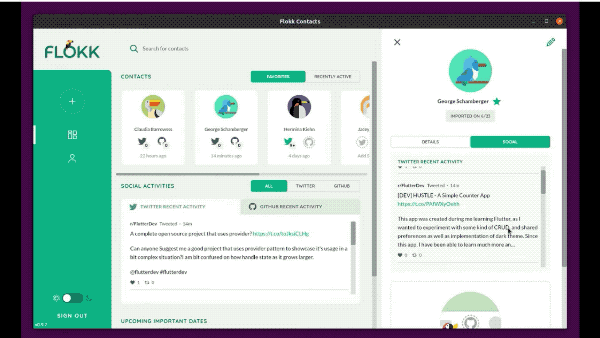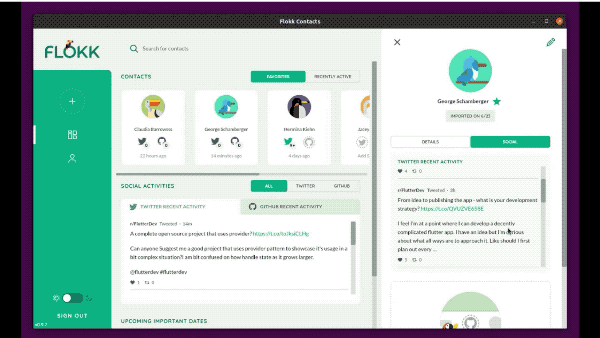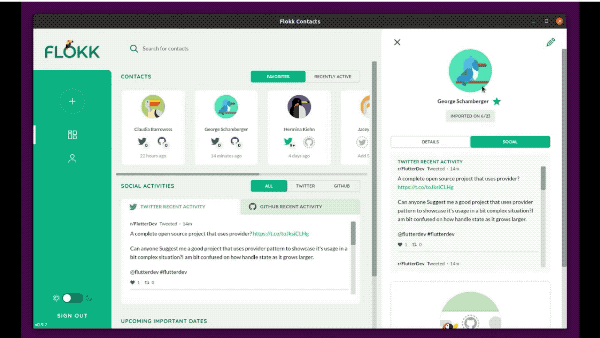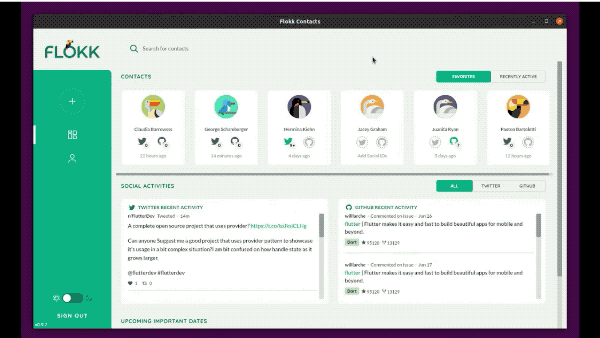
Canonical通过Flutter启用Linux桌面应用程序(推荐)_Linux
这篇文章主要介绍了Canonical通过Flutter启用Linux桌面应用程序,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 Google 对 Flutter 的目标一直是...
2023年10月10日 21:04
如何使用Docker搭建pypi私有仓库_docker
这篇文章主要介绍了如何使用Docker搭建pypi私有仓库,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、搭建 1、准备htpasswd.txt文件 该...
2023年1月2日 21:22
CVE-2020-6308: SAP BusinessObjects Business Intelligence Platform – Blind Server-Side Request Forgery
漏洞标题 CVE-2020-6308: SAP BusinessObjects Business Intelligence Platform - Blind Server-Side Request Forgery 漏洞描述 SAP BusinessObjects Business Intelligence Platform (Web Serv...
2020年12月30日 22:48CVE-2021-24165: WordPress Ninja Forms <3.4.34 - Open Redirect
漏洞标题 CVE-2021-24165: WordPress Ninja Forms <3.4.34 - Open Redirect 漏洞描述 WordPress Ninja Forms plugin before 3.4.34 contains an open redirect vulnerability via the wp_aja...
2021年4月4日 21:31CVE-2023-28121: WooCommerce Payments – Unauthorized Admin Access
漏洞标题 CVE-2023-28121: WooCommerce Payments - Unauthorized Admin Access 漏洞描述 An issue in WooCommerce Payments plugin for WordPress (versions 5.6.1 and lower) allows an unauth...
2023年9月3日 02:34CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
2022年7月28日 03:59CVE-2022-2486: Wavlink WN535K2/WN535K3 – OS Command Injection
漏洞标题 CVE-2022-2486: Wavlink WN535K2/WN535K3 - OS Command Injection 漏洞描述 Wavlink WN535K2 and WN535K3 routers are susceptible to OS command injection in an unknown part of th...
2022年8月22日 00:57aria2 webui 路径遍历漏洞(CVE-2023-39141)
漏洞标题 aria2 webui 路径遍历漏洞(CVE-2023-39141) 漏洞描述 WebUI-Aria2是hamza zia个人开发者的一个应用程序。用于创建与 aria2 交互的界面。 WebUI-Aria24fe2e版本存在路径遍历漏洞,该漏...
2023年3月4日 13:07CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
漏洞标题 CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover 漏洞描述 The Motors theme for WordPress is vulnerable to pri...
2025年3月8日 23:48CVE-2010-1429: Red Hat JBoss Enterprise Application Platform – Sensitive Information Disclosure
漏洞标题 CVE-2010-1429: Red Hat JBoss Enterprise Application Platform - Sensitive Information Disclosure 漏洞描述 Red Hat JBoss Enterprise Application Platform 4.2 before 4.2.0.CP0...
2010年2月27日 01:01CVE-2022-27849: WordPress Simple Ajax Chat <20220116 - Sensitive Information Disclosure vulnerability
漏洞标题 CVE-2022-27849: WordPress Simple Ajax Chat <20220116 - Sensitive Information Disclosure vulnerability 漏洞描述 WordPress Simple Ajax Chat before 20220216 is vulnerable ...
2022年11月1日 08:58CVE-2021-27670: Appspace 6.2.4 – Server-Side Request Forgery
漏洞标题 CVE-2021-27670: Appspace 6.2.4 - Server-Side Request Forgery 漏洞描述 Appspace 6.2.4 allows SSRF via the api/v1/core/proxy/jsonprequest url parameter. PoC代码
2021年4月2日 01:43CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
2012年10月10日 15:26CVE-2024-6646: Netgear-WN604 downloadFile.php – Information Disclosure
漏洞标题 CVE-2024-6646: Netgear-WN604 downloadFile.php - Information Disclosure 漏洞描述 There is an information leakage vulnerability in the downloadFile.php interface of Netgear ...
2024年9月29日 16:47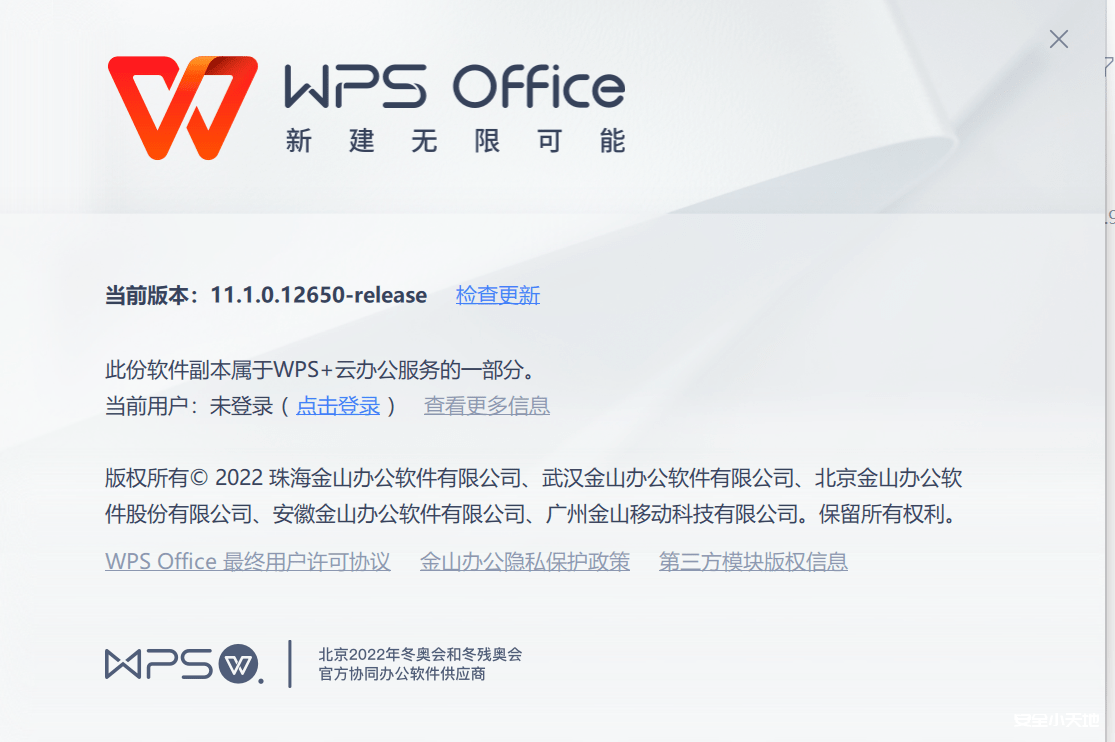
2023最新金山wps恶意文件执行复现,附poc
0x01 漏洞描述 WPS Office for windows的内置浏览界存在逻辑漏洞,攻击者可以利用该漏洞专门构造出恶意文档,受害者打开该文档并点击文档中的URL链接或包舍了超级链接的图片时,...

 2023年8月17日 18:05

2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

