
最新发布第517页

CVE-2019-12725: Zeroshell 3.9.0 – Remote Command Execution
漏洞标题 CVE-2019-12725: Zeroshell 3.9.0 - Remote Command Execution 漏洞描述 Zeroshell 3.9.0 is prone to a remote command execution vulnerability. Specifically, this issue occurs b...
 2019年7月8日 01:25
Nginx的location的常见规则优先级问题_nginx
Nginx是反向代理和负载均衡的首选工具,nginx的location配置有许多细节内容在网上不容易找到资料,或者解释不清。本文对Nginx location规则优先级介绍,需要的朋友参考下吧 目录一、Location / ...
2022年6月15日 09:45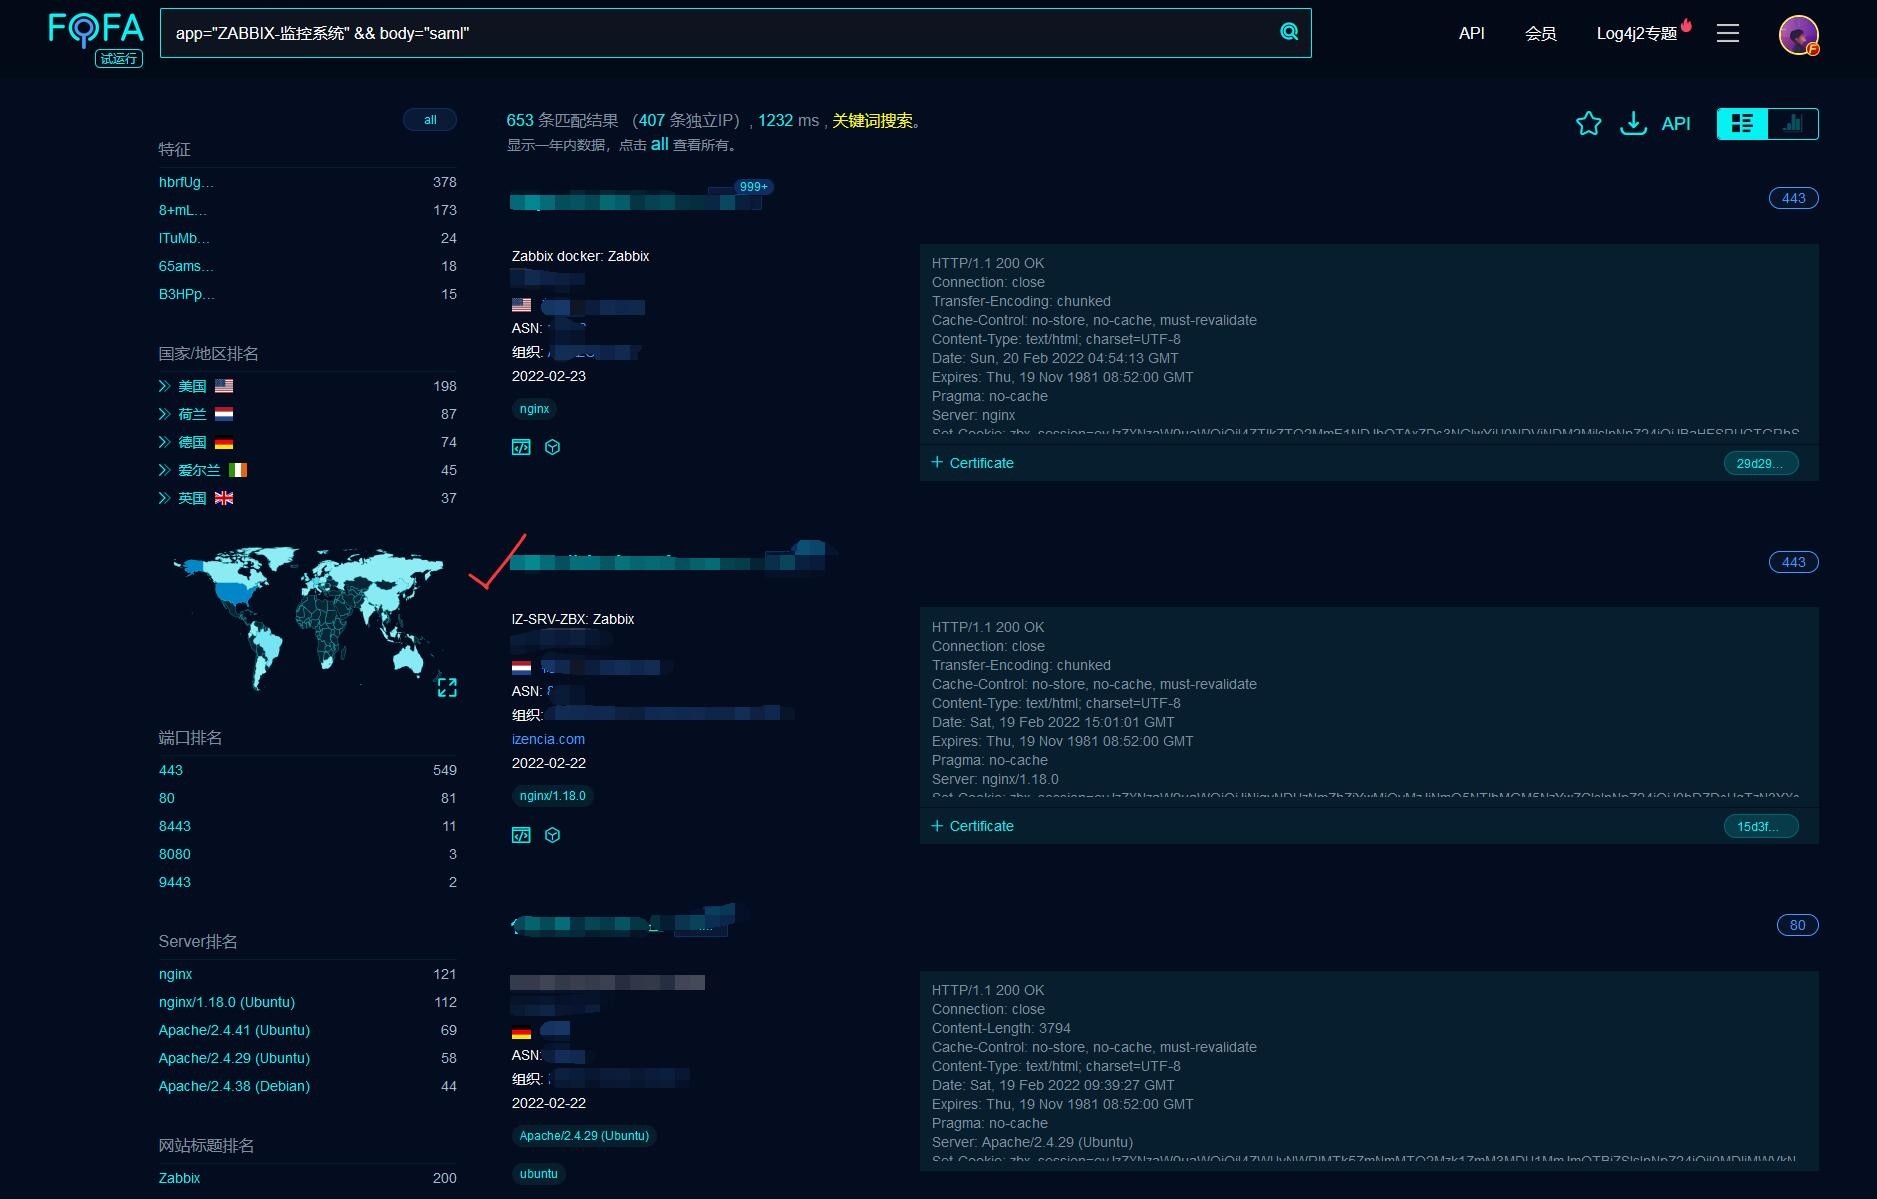
CVE-2022-23131_Zabbix登录绕过漏洞分析及复现
前言 由于传播、利用此文所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,文章作者不为此承担任何责任。 本文章中的漏洞均为公开的漏洞收集,如果文章中的漏洞出现敏感...
2022年3月10日 23:37CVE-2023-22047: Oracle Peoplesoft – Unauthenticated File Read
漏洞标题 CVE-2023-22047: Oracle Peoplesoft - Unauthenticated File Read 漏洞描述 Vulnerability in the PeopleSoft Enterprise PeopleTools product of Oracle PeopleSoft (component- Port...
2023年1月27日 14:12CVE-2018-19127: PHPCMS 2008 – Remote Code Execution via Template Injection
漏洞标题 CVE-2018-19127: PHPCMS 2008 - Remote Code Execution via Template Injection 漏洞描述 PHPCMS 2008 suffers from an unauthenticated RCE via template injection in type.php, whe...
2018年7月30日 04:55Atlassian Jira Confluence xss(CVE-2018-5230)
漏洞标题 Atlassian Jira Confluence xss(CVE-2018-5230) 漏洞描述 版本7.6.6之前的Atlassian JiraConfluence、版本7.7.4之前的版本7.7.0、版本7.8.4之前的7.8.0以及版本7.9.2之前的7.9.0,允许...
2018年12月23日 07:44CVE-2021-27561: YeaLink DM 3.6.0.20 – Remote Command Injection
漏洞标题 CVE-2021-27561: YeaLink DM 3.6.0.20 - Remote Command Injection 漏洞描述 Yealink Device Management (DM) 3.6.0.20 allows command injection as root via the /sm/api/v1/firewal...
2021年3月7日 08:42CVE-2024-8021: Gradio – Open Redirect
漏洞标题 CVE-2024-8021: Gradio - Open Redirect 漏洞描述 Gradio allows an open redirect bypass via URL encoding, enabling attackers to redirect users to malicious sites. This can le...
2024年7月31日 19:26
[HCTF 2018]admin – buu刷题笔记
首先爬一遍整个网站,发现有没注册的时候有“login”,'register', 这两个页面,注册一个123用户登录后发现有 'index“,”post“,”logout“,”change password“这四个界面, 根据题目提示的a...

 2022年4月17日 16:53
Casdoor 1.13.0-SQL注入(CVE-2022-24124)
漏洞标题 Casdoor 1.13.0-SQL注入(CVE-2022-24124) 漏洞描述 Casdoor 是一个基于 OAuth 2.0 / OIDC 的 UI 优先集中认证 / 单点登录 (SSO) 平台。该平台存在sql注入漏洞 PoC代码 暂无
2022年2月24日 21:57CVE-2018-5715: SugarCRM 3.5.1 – Cross-Site Scripting
漏洞标题 CVE-2018-5715: SugarCRM 3.5.1 - Cross-Site Scripting 漏洞描述 SugarCRM 3.5.1 is vulnerable to cross-site scripting via phprint.php and a parameter name in the query string...
2018年4月23日 09:10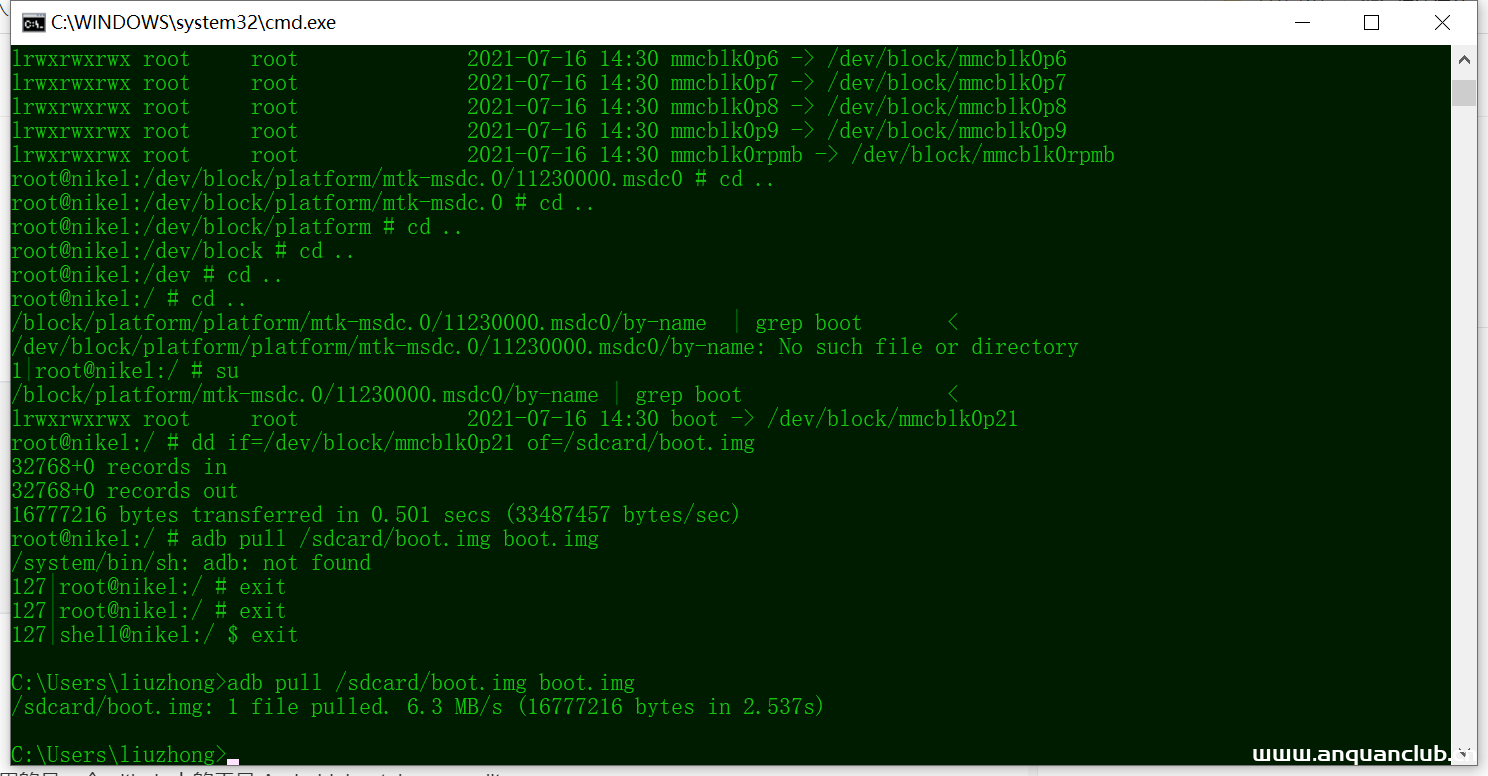
安卓系统修改系统内核绕过TracerPid检测–反防调试
背景: 得到一个Android的CrackMe来考察逆向知识,分析后发现其关键函数位于native so库中,并且在函数开始时启动了线程进行TracerPid检测的反调试,当发现程序被调试时会直接杀死应用。虽然题...
2022年3月10日 23:34CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
2025年6月8日 18:31CVE-2025-58360: GeoServer – XML External Entity Injection
漏洞标题 CVE-2025-58360: GeoServer - XML External Entity Injection 漏洞描述 GeoServer 2.26.0 to 2.26.2 and 2.25.6 contains an XML External Entity (XXE) injection caused by insuffic...
2025年1月19日 21:22CVE-2016-10960: WordPress wSecure Lite < 2.4 - Remote Code Execution
漏洞标题 CVE-2016-10960: WordPress wSecure Lite < 2.4 - Remote Code Execution 漏洞描述 WordPress wsecure plugin before 2.4 is susceptible to remote code execution via shell meta...
2016年9月24日 05:29CVE-2021-3019: ffay lanproxy Directory Traversal
漏洞标题 CVE-2021-3019: ffay lanproxy Directory Traversal 漏洞描述 ffay lanproxy 0.1 is susceptible to a directory traversal vulnerability that could let attackers read /../conf/co...
2021年6月27日 09:25
2026年9月24日 11:46
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

