
最新发布第520页
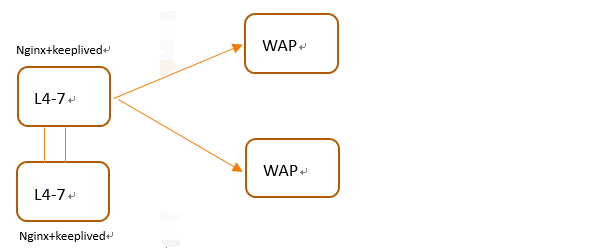
nginx实现动静分离的示例代码_nginx
这篇文章主要介绍了nginx实现动静分离的示例代码,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 一、简单配置ngin...
 2024年7月9日 20:36

CVE-2015-1579: WordPress Slider Revolution – Local File Disclosure
漏洞标题 CVE-2015-1579: WordPress Slider Revolution - Local File Disclosure 漏洞描述 Directory traversal vulnerability in the Elegant Themes Divi theme for WordPress allows remote ...
2015年11月7日 14:53CVE-2015-2067: Magento Server MAGMI – Directory Traversal
漏洞标题 CVE-2015-2067: Magento Server MAGMI - Directory Traversal 漏洞描述 Magento Server MAGMI (aka Magento Mass Importer) contains a directory traversal vulnerability in web/aja...
2015年12月20日 08:32
安恒信息苗春雨:学以致用产教融合,全方位助力网络安全人才体系建设
3月11日,西湖论剑·第五届中国杭州网络安全技能大赛(以下简称“大赛”)决赛在杭州拉开帷幕。作为首届全球数字贸易博览会的亮点单元,本次大赛由杭州市公安局、共青团杭州市委、杭州市学生联...
2022年3月16日 09:15CVE-2014-5368: WordPress Plugin WP Content Source Control – Directory Traversal
漏洞标题 CVE-2014-5368: WordPress Plugin WP Content Source Control - Directory Traversal 漏洞描述 A directory traversal vulnerability in the file_get_contents function in downloadf...
2014年8月23日 13:56CVE-2023-27847: PrestaShop xipblog – SQL Injection
漏洞标题 CVE-2023-27847: PrestaShop xipblog - SQL Injection 漏洞描述 In the blog module (xipblog), an anonymous user can perform SQL injection. Even though the module has been patc...
2023年6月10日 20:47CVE-2010-1306: Joomla! Component Picasa 2.0 – Local File Inclusion
漏洞标题 CVE-2010-1306: Joomla! Component Picasa 2.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Picasa (com_joomlapicasa2) component 2.0 and 2.0.5 f...
2010年9月20日 13:33
使用rpm安装指定版本docker(1.12.6)的详细步骤_docker
为了防止安装高版本的docker引发的错误,需要安装1.12.6版本的docker,下面小编给大家带来了使用rpm安装指定版本的docker(1.12.6)的步骤,感兴趣的朋友一起看看吧 一.原因 如果系统是Centos7.3,...
2022年6月25日 20:34CVE-2019-19824: TOTOLINK Realtek SD Routers – Remote Command Injection
漏洞标题 CVE-2019-19824: TOTOLINK Realtek SD Routers - Remote Command Injection 漏洞描述 TOTOLINK Realtek SDK based routers may allow an authenticated attacker to execute arbitrary...
2019年5月24日 09:24CVE-2022-34048: Wavlink WN-533A8 – Cross-Site Scripting
漏洞标题 CVE-2022-34048: Wavlink WN-533A8 - Cross-Site Scripting 漏洞描述 Wavlink WN-533A8 M33A8.V5030.190716 contains a reflected cross-site scripting vulnerability via the login_...
2022年12月14日 02:13CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
2022年7月8日 00:37CVE-2008-0702: Titan FTP Server 6.03 and 6.0.5.549 – Heap Overflow via Long Commands
漏洞标题 CVE-2008-0702: Titan FTP Server 6.03 and 6.0.5.549 - Heap Overflow via Long Commands 漏洞描述 Titan FTP Server versions 6.03 and 6.05 (builds) contain multiple heap-based ...
2008年12月16日 06:28CVE-2025-5086: Dassault Systèmes DELMIA Apriso (up to 2025) – Insecure Deserialization
漏洞标题 CVE-2025-5086: Dassault Systèmes DELMIA Apriso (up to 2025) - Insecure Deserialization 漏洞描述 A deserialization of untrusted data vulnerability affecting DELMIA Apriso ...
2025年5月19日 05:08CVE-2024-21644: pyLoad Flask Config – Access Control
漏洞标题 CVE-2024-21644: pyLoad Flask Config - Access Control 漏洞描述 pyLoad is the free and open-source Download Manager written in pure Python. Any unauthenticated user can brow...
2024年9月28日 14:26CVE-2012-5913: WordPress Integrator 1.32 – Cross-Site Scripting
漏洞标题 CVE-2012-5913: WordPress Integrator 1.32 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in wp-integrator.php in the WordPress Integrator module 1.32 ...
2012年1月9日 12:20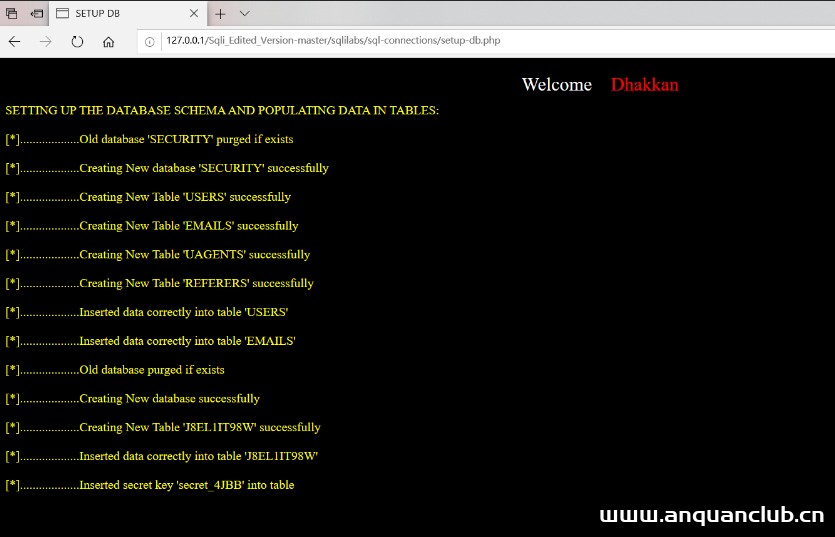
最新版Phpstudy安装sql注入平台(sqli-labs)错误解决方法
网上安装sqli-labs位置及修改的教程有一大堆,但是进入到了浏览器页面,点击Setup/reset Database for labs选项就会报错,虽然网上提供了关于phpstudy 5.x版本和7.x版本的修改办法,但是仍会出...

 2022年3月21日 11:54

2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

