
最新发布第524页

CVE-2022-24990: TerraMaster TOS < 4.2.30 Server Information Disclosure
漏洞标题 CVE-2022-24990: TerraMaster TOS < 4.2.30 Server Information Disclosure 漏洞描述 TerraMaster NAS devices running TOS prior to version 4.2.30 are vulnerable to informatio...
 2022年6月30日 20:16
CVE-2025-4302: Stop User Enumeration WordPress plugin – Authentication Bypass
漏洞标题 CVE-2025-4302: Stop User Enumeration WordPress plugin - Authentication Bypass 漏洞描述 Stop User Enumeration WordPress plugin < 1.7.3 contains an authentication bypass ...
2025年1月15日 18:05CVE-2023-38952: ZKTeco BioTime <= 9.0.1 - Privilege Escalation
漏洞标题 CVE-2023-38952: ZKTeco BioTime <= 9.0.1 - Privilege Escalation 漏洞描述 BioTime default employee credentials (password 123456) allow login. Sessions are not role-valida...
2023年12月22日 19:58CVE-2025-45985: Blink Router – Command Injection
漏洞标题 CVE-2025-45985: Blink Router - Command Injection 漏洞描述 Blink routers BL-WR9000 V2.4.9 , BL-AC2100_AZ3 V1.0.4, BL-X10_AC8 v1.0.5 , BL-LTE300 v1.2.3, BL-F1200_AT1 v1.0.0,...
2025年3月15日 13:51CVE-2020-12054: WordPress Catch Breadcrumb <1.5.4 - Cross-Site Scripting
漏洞标题 CVE-2020-12054: WordPress Catch Breadcrumb <1.5.4 - Cross-Site Scripting 漏洞描述 WordPress Catch Breadcrumb plugin before 1.5.4 contains a reflected cross-site scripti...
2020年3月23日 01:03Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530)
漏洞标题 Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Struts2 会对某些标签属性(比如 id,其他属性有...
2020年5月6日 13:05CVE-2023-48728: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2023-48728: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 A reflected XSS vulnerability exists in the functiongetOpenGraph videoName functionality of WWBN AVideo 11...
2023年10月12日 02:40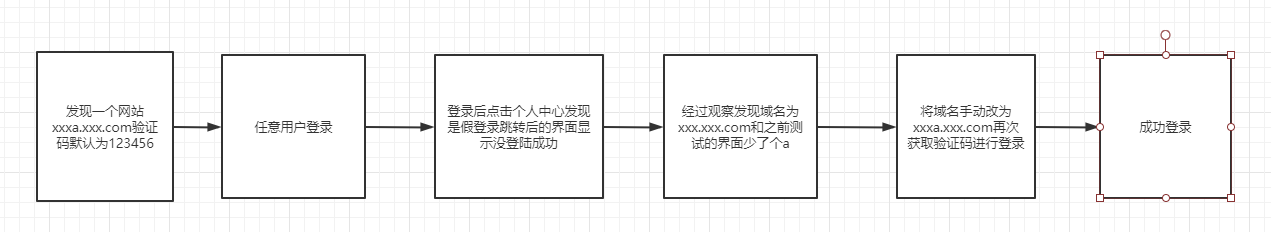
一次奇葩的任意用户登录
在安全小天地测试某src时发现一个界面,域名为xxxa.xxx.com,是一个登录界面,发现该界面支持使用手机号登录以及注册功能,测试后发现该网站使用的短信验证码为123456 因此用脚趾头都能想出来的...
2022年3月10日 23:36
bugbounty技巧聚合20220210
漏洞报告 垂直越权900$ http://hackerone.com/reports/1102652 bucket信息泄露500$ http://hackerone.com/reports/1102546 TikTok XSS 6000$ http://hackerone.com/reports/1452375 挖洞技巧 如...
2022年3月10日 23:30CVE-2023-24657: phpIPAM – 1.6 – Cross-Site Scripting
漏洞标题 CVE-2023-24657: phpIPAM - 1.6 - Cross-Site Scripting 漏洞描述 phpIPAM 1.6 contains a cross-site scripting vulnerability via the closeClass parameter at /subnet-masks/popup...
2023年12月26日 18:32bugbounty技巧聚合20220216
漏洞报告 POST URL跳转? 100$ http://hackerone.com/reports/1358977 爆破使用户无法收到2FA验证码导致无法登录 900$ http://hackerone.com/reports/1406495 挖洞技巧 CVE-2022-22536 EXP http...
2022年3月10日 23:29
Conti内部聊天记录暴露勒索软件团伙工作日常
在办公室或者远程工作,人力资源团队具有严格的招聘流程,还有绩效评估、职业发展和奖金,乍一听像是任何一个普通正规的软件开发团队。但这里要说的不是一家软件公司,而是Conti,最知名的勒索...
2022年3月16日 09:15nginx优化的六点方法_nginx
这篇文章主要介绍了nginx优化的六点方法,有对nginx优化不太熟悉的同学可以参考下 一.优化Nginx并发量 [root@proxy ~]# ab -n 2000 -c 2000 http://192.168.4.5/ Benchmarking 192.168.4.5 (be p...
2022年10月12日 21:35Atlassian Confluence CVE-2023-22527 远程命令执行漏洞
漏洞标题 Atlassian Confluence CVE-2023-22527 远程命令执行漏洞 漏洞描述 Atlassian Confluence存在远程命令执行漏洞,此漏洞是对用户的数据缺乏校验导致的。 PoC代码 暂无
2023年1月1日 13:47CVE-2024-4577: PHP CGI – Argument Injection
漏洞标题 CVE-2024-4577: PHP CGI - Argument Injection 漏洞描述 PHP CGI - Argument Injection (CVE-2024-4577) is a critical argument injection flaw in PHP. PoC代码
2024年6月29日 12:56bugbounty技巧聚合20211021
漏洞报告 【Node.js 250刀】HTTP Request Smuggling due to accepting space before colon http://hackerone.com/reports/1238709 【Nextcloud】RCE on 17 different Docker containers on your...
2022年3月10日 23:30
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

