
最新发布第525页

CVE-2021-24347: WordPress SP Project & Document Manager <4.22 - Authenticated Shell Upload
漏洞标题 CVE-2021-24347: WordPress SP Project & Document Manager <4.22 - Authenticated Shell Upload 漏洞描述 WordPress SP Project & Document Manager plugin before 4.22 i...
 2021年7月8日 21:39
给敏感信息打上马赛克就安全了吗?
我们在群聊发送图片、平台上传视频的时候,通常会对图片和视频的敏感信息进行处理,最常见的几种方式有马赛克、模糊、涂抹、黑条等,其中马赛克可以说是最为常见的一种。然而我们经常可以看到有...

 2022年2月18日 18:20
CVE-2024-21683: Atlassian Confluence Data Center and Server – Remote Code Execution
漏洞标题 CVE-2024-21683: Atlassian Confluence Data Center and Server - Remote Code Execution 漏洞描述 Detects a Remote Code Execution vulnerability in Confluence Data Center and Se...
2024年10月13日 04:23
某src之报错页面导致的大量日志信息泄露
0x01 某天下午在看安全小天地资产时候发现了一个状态码为200,返回包却存在报错信息的报错界面。 由于漏洞已经修复,报错信息已经无,请自行脑补,大概就是报错出了一大堆东西,其中有个参数为...
2022年3月10日 23:36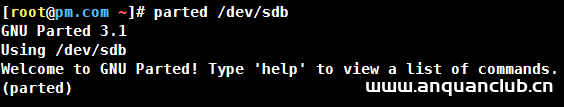
Linux parted磁盘分区实现步骤解析_Linux
这篇文章主要介绍了Linux parted磁盘分区实现步骤解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 相对于fdisk,parted用的比较少,主...
2023年7月12日 21:03
一个脚本让你的app自动吐出密钥信息
### 背景 安全小天地某个私密项目中涉及到一个app的测试,打开一看,证书校验--不让抓包,信息加密-无法篡改,遇到这种情况怎么,正常我这种小菜鸡都是直接放弃了,奈何厂家奖金给的高啊,我还...
2022年3月10日 23:36
nginx 如何实现if嵌套的方法示例_nginx
这篇文章主要介绍了nginx 如何实现if嵌套的方法示例,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 nginx 不支持 ...
2026年8月13日 11:45Apache Solr CVE-2019-0193 DataImportHandler 代码执行漏洞
漏洞标题 Apache Solr CVE-2019-0193 DataImportHandler 代码执行漏洞 漏洞描述 Apache Solr 中存在代码执行漏洞。该漏洞是由于DataImportHandler模块对用户输入的数据验证不足导致的。 PoC代码...
2019年8月9日 14:42CVE-2025-6058: WPBookit <= 1.0.4 - Unauthenticated Arbitrary File Upload
漏洞标题 CVE-2025-6058: WPBookit <= 1.0.4 - Unauthenticated Arbitrary File Upload 漏洞描述 The WPBookit plugin for WordPress is vulnerable to arbitrary file uploads due to missi...
2025年9月29日 02:18CVE-2019-12581: Zyxel ZyWal/USG/UAG Devices – Cross-Site Scripting
漏洞标题 CVE-2019-12581: Zyxel ZyWal/USG/UAG Devices - Cross-Site Scripting 漏洞描述 Zyxel ZyWall, USG, and UAG devices allow remote attackers to inject arbitrary web script or HTM...
2019年1月8日 23:32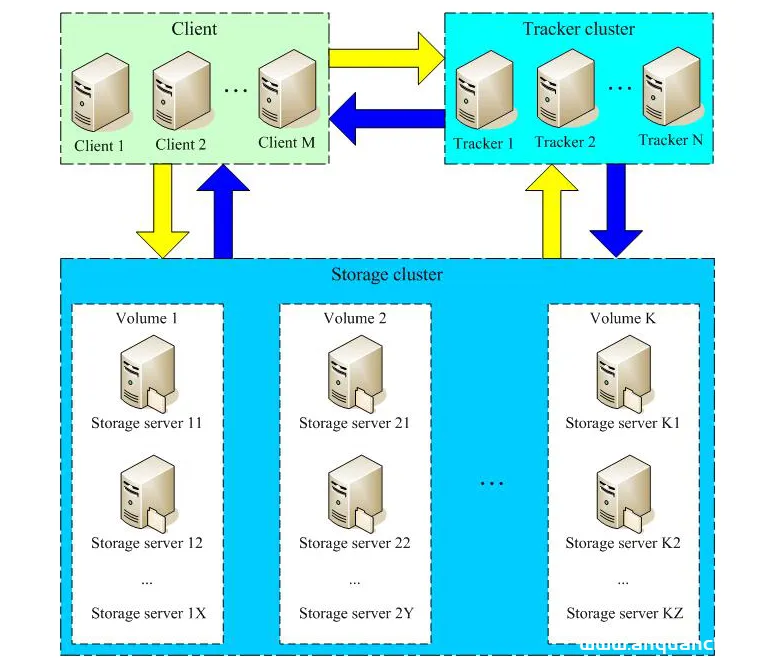
用nginx+FastDFS一步步搭建文件管理系统_服务器其它
FastDFS 是一个开源的高性能分布式文件系统(DFS)。 它的主要功能包括:文件存储,文件同步和文件访问,以及高容量和负载平衡。主要解决了海量数据存储问题,特别适合以中小文件(建议范围:4K...
2023年4月16日 20:56CVE-2013-2287: WordPress Plugin Uploader 1.0.4 – Cross-Site Scripting
漏洞标题 CVE-2013-2287: WordPress Plugin Uploader 1.0.4 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in views/notify.php in the Uploader plugin 1.0...
2013年6月14日 05:37CVE-2020-29453: Jira Server Pre-Auth – Arbitrary File Retrieval (WEB-INF, META-INF)
漏洞标题 CVE-2020-29453: Jira Server Pre-Auth - Arbitrary File Retrieval (WEB-INF, META-INF) 漏洞描述 The CachingResourceDownloadRewriteRule class in Jira Server and Jira Data Cent...
2020年5月26日 22:38
[极客大挑战 2019]PHP
因为每次猫猫都在我键盘上乱跳,所以我有一个良好的备份网站的习惯 不愧是我!!! 这不就是文件扫描,dirb什么的都可以,经过一番测试,备份文件名为www.zip 直接在url后面输入www.zip,可以获...
2023年6月7日 14:53CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
2022年10月18日 03:56CVE-2022-0660: Microweber <1.2.11 - Information Disclosure
漏洞标题 CVE-2022-0660: Microweber <1.2.11 - Information Disclosure 漏洞描述 Microweber before 1.2.11 is susceptible to information disclosure. An error message is generated in ...
2022年2月8日 12:24
2026年10月23日 11:45
2026年10月22日 11:46
2026年10月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

