
最新发布第530页
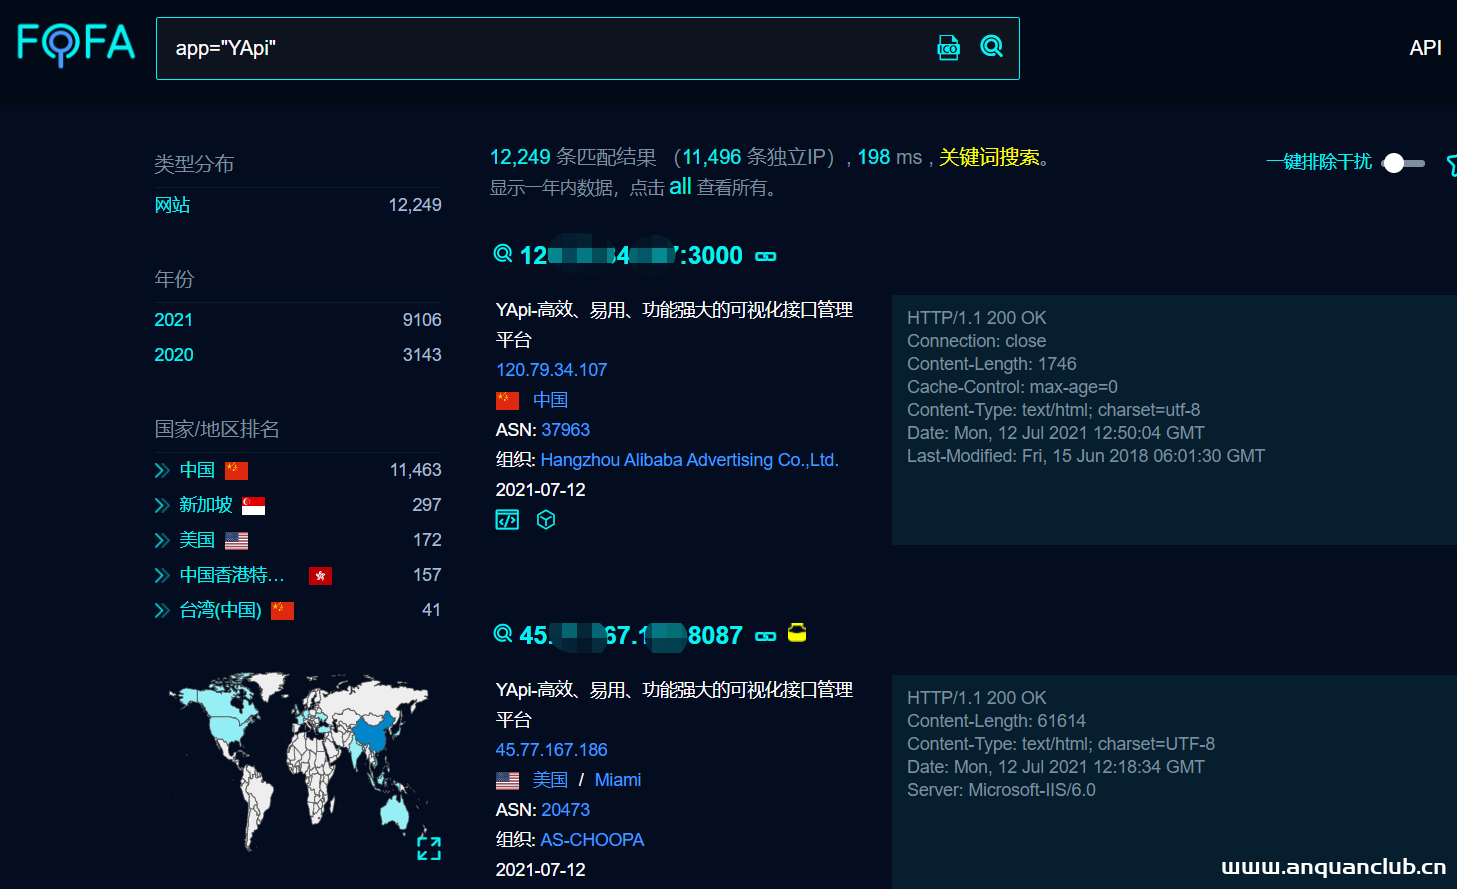
我是如何利用火器捡漏洞的
一、引子 当一个新漏洞被曝光后,如何才能快速在互联网上找到相关资产? 网络空间搜索引擎是一个不错的选择,例如FOFA、shodan等。 举个例子,这几天新爆了一个“Yapi认证用户利用Mock功能远程...
 2022年3月10日 23:36

CVE-2024-10516: Swift Performance Lite < 2.3.7.2 - Local PHP File Inclusion
漏洞标题 CVE-2024-10516: Swift Performance Lite < 2.3.7.2 - Local PHP File Inclusion 漏洞描述 A vulnerability in Swift Performance Lite before version 2.3.7.2 allows unauthentic...
2024年9月6日 23:39CVE-2021-24891: WordPress Elementor Website Builder <3.1.4 - Cross-Site Scripting
漏洞标题 CVE-2021-24891: WordPress Elementor Website Builder <3.1.4 - Cross-Site Scripting 漏洞描述 WordPress Elementor Website Builder plugin before 3.1.4 contains a DOM cross-...
2021年3月31日 12:31BOA Webserver 文件读取(CVE-2017-9833)
漏洞标题 BOA Webserver 文件读取(CVE-2017-9833) 漏洞描述 BOA Webserver 0.94.14rc21 中的 /cgi-bin/wapopen 允许使用 FILECAMERA 变量(由 GET发送)注入“../..”以读取具有 root 权限的文...
2017年11月26日 08:27
CentOS SVN服务器如何管理多个项目_服务器其它
这篇文章主要介绍了CentOS SVN服务器如何管理多个项目,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一 需求 一般来说,公司有多个项目...
2023年2月17日 20:42CVE-2016-10956: WordPress Mail Masta 1.0 – Local File Inclusion
漏洞标题 CVE-2016-10956: WordPress Mail Masta 1.0 - Local File Inclusion 漏洞描述 WordPress Mail Masta 1.0 is susceptible to local file inclusion in count_of_send.php and csvexport...
2016年11月27日 02:28CVE-2022-3578: WordPress ProfileGrid <5.1.1 - Cross-Site Scripting
漏洞标题 CVE-2022-3578: WordPress ProfileGrid <5.1.1 - Cross-Site Scripting 漏洞描述 WordPress ProfileGrid plugin prior to 5.1.1 contains a cross-site scripting vulnerability. T...
2022年8月1日 18:03CVE-2024-2330: NS-ASG Application Security Gateway 6.3 – Sql Injection
漏洞标题 CVE-2024-2330: NS-ASG Application Security Gateway 6.3 - Sql Injection 漏洞描述 A vulnerability was found in Netentsec NS-ASG Application Security Gateway 6.3. It has been...
2024年1月21日 02:49CVE-2025-12480: Triofox – Improper Access Control
漏洞标题 CVE-2025-12480: Triofox - Improper Access Control 漏洞描述 The Gladinet Triofox solution before 12.91.1126.65588 and CentreStack before 12.10.595.65696 allow unauthenticat...
2025年12月4日 07:52bugbounty技巧聚合20220210
漏洞报告 垂直越权900$ http://hackerone.com/reports/1102652 bucket信息泄露500$ http://hackerone.com/reports/1102546 TikTok XSS 6000$ http://hackerone.com/reports/1452375 挖洞技巧 如...
2022年3月10日 23:30CVE-2022-31181: PrestaShop – SQL Injection to Eval Injection
漏洞标题 CVE-2022-31181: PrestaShop - SQL Injection to Eval Injection 漏洞描述 PrestaShop versions from 1.6.0.10 and before 1.7.8.7 contain an SQL injection caused by unsanitized u...
2022年4月4日 06:06CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...
2013年8月9日 15:48CVE-2022-0735: GitLab CE/EE – Information Disclosure
漏洞标题 CVE-2022-0735: GitLab CE/EE - Information Disclosure 漏洞描述 GitLab CE/EE is susceptible to information disclosure. An attacker can access runner registration tokens usin...
2022年3月21日 10:39CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion
漏洞标题 CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion 漏洞描述 STAGIL Navigation for Jira Menu & Themes plugin before 2.0.52 i...
2023年1月22日 05:49CVE-2023-49103: OwnCloud – Phpinfo Configuration
漏洞标题 CVE-2023-49103: OwnCloud - Phpinfo Configuration 漏洞描述 An issue was discovered in ownCloud owncloud/graphapi 0.2.x before 0.2.1 and 0.3.x before 0.3.1. The graphapi app...
2023年6月26日 05:58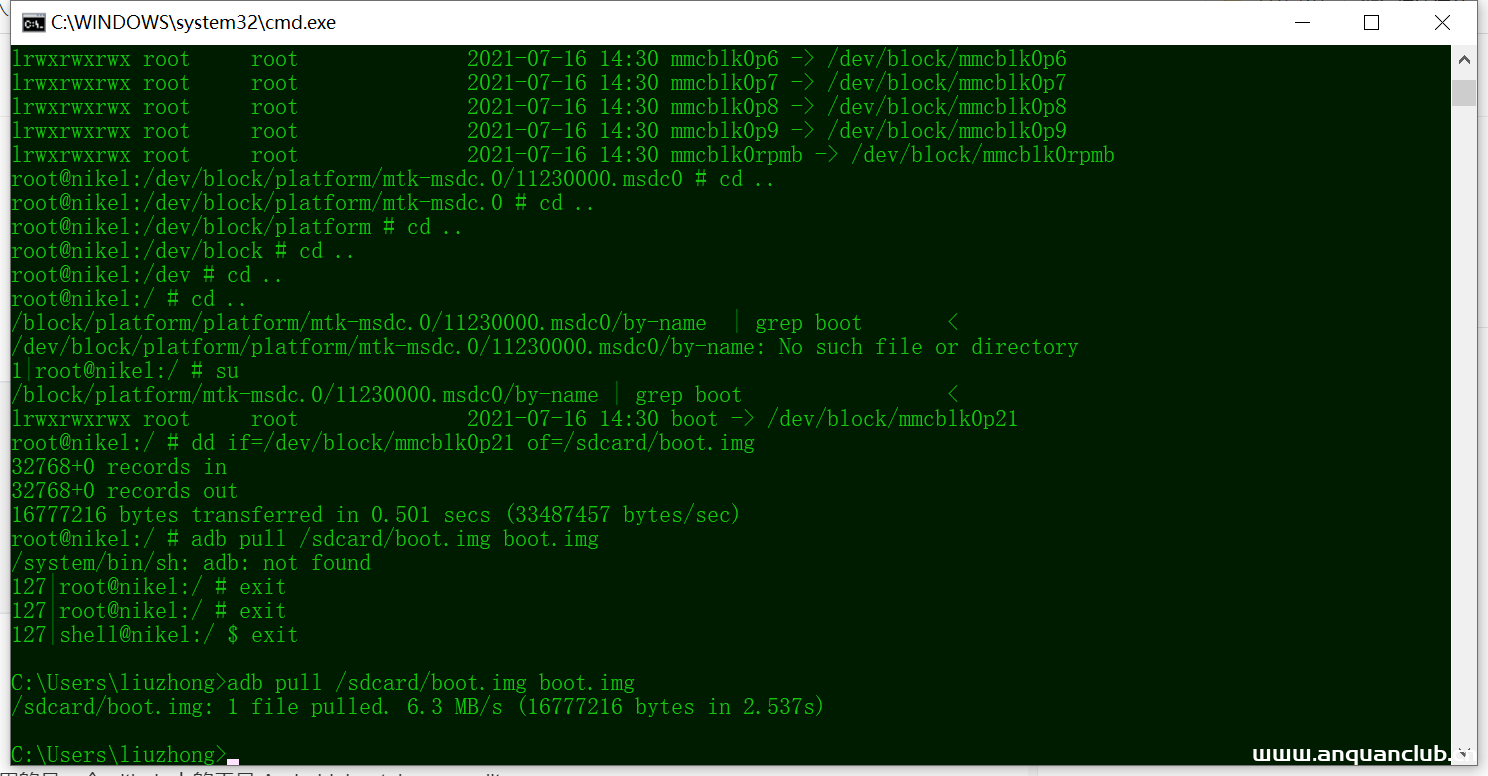
安卓系统修改系统内核绕过TracerPid检测–反防调试
背景: 得到一个Android的CrackMe来考察逆向知识,分析后发现其关键函数位于native so库中,并且在函数开始时启动了线程进行TracerPid检测的反调试,当发现程序被调试时会直接杀死应用。虽然题...
2022年3月10日 23:34
2026年11月17日 11:45
2026年11月16日 11:45
2026年11月15日 11:45
2026年11月14日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

