
最新发布第531页

CVE-2018-1000861: Jenkins – Remote Command Injection
漏洞标题 CVE-2018-1000861: Jenkins - Remote Command Injection 漏洞描述 Jenkins 2.153 and earlier and LTS 2.138.3 and earlier are susceptible to a remote command injection via stapl...
 2018年3月22日 19:03
CVE-2021-24389: WordPress FoodBakery <2.2 - Cross-Site Scripting
漏洞标题 CVE-2021-24389: WordPress FoodBakery <2.2 - Cross-Site Scripting 漏洞描述 WordPress FoodBakery before 2.2 contains an unauthenticated reflected cross-site scripting vul...
2021年4月25日 22:44
CVE-2025-27222: TRUfusion Enterprise <= 7.10.4.0 - Path Traversal
漏洞标题 CVE-2025-27222: TRUfusion Enterprise <= 7.10.4.0 - Path Traversal 漏洞描述 Pre-Auth Path Traversal Allowing to Leak Local server files disclosing sensitive clear-text p...
2025年6月8日 09:44CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
2024年9月28日 07:25CVE-2010-1875: Joomla! Component Property – Local File Inclusion
漏洞标题 CVE-2010-1875: Joomla! Component Property - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Real Estate Property (com_properties) component 3.1.22...
2010年8月31日 01:58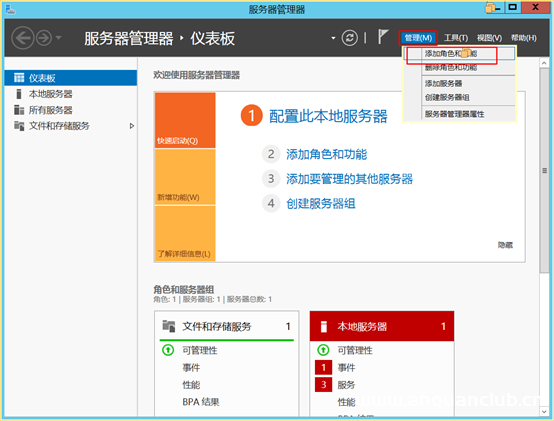
hyper-v简介及安装使用(图文详解)_Hyper-V
这篇文章主要介绍了hyper-v简介及安装使用(图文详解),小编觉得挺不错的,现在分享给大家,也给大家做个参考。一起跟随小编过来看看吧 前言:作为IT界的巨头,微软自己的虚拟化技术,也是微软第...
2024年5月13日 20:03CVE-2023-32563: Ivanti Avalanche – Remote Code Execution
漏洞标题 CVE-2023-32563: Ivanti Avalanche - Remote Code Execution 漏洞描述 An unauthenticated attacker could achieve the code execution through a RemoteControl server. PoC代码
2023年7月23日 12:21CVE-2022-22965: Spring – Remote Code Execution
漏洞标题 CVE-2022-22965: Spring - Remote Code Execution 漏洞描述 Spring MVC and Spring WebFlux applications running on Java Development Kit 9+ are susceptible to remote code execut...
2022年7月27日 23:54
研究人员在Google Play商店发现新的银行木马
移动威胁检测与预防公司ThreatFabric新近发现了一种新的Android银行木马Xenomorph,该木马通过官方Google Play商店分发,目前安装量已超过50000次。该银行木马针对56家欧洲银行,目的是从其客户...
2022年3月10日 23:40CVE-2022-32770: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2022-32770: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 WWBN AVideo 11.6 contains a cross-site scripting vulnerability in the footer alerts functionality via the ...
2022年12月3日 01:06CVE-2010-1540: Joomla! Component com_blog – Directory Traversal
漏洞标题 CVE-2010-1540: Joomla! Component com_blog - Directory Traversal 漏洞描述 A directory traversal vulnerability in index.php in the MyBlog (com_myblog) component 3.0.329 for ...
2010年1月26日 10:24CVE-2010-2037: Joomla! Component Percha Downloads Attach 1.1 – Directory Traversal
漏洞标题 CVE-2010-2037: Joomla! Component Percha Downloads Attach 1.1 - Directory Traversal 漏洞描述 A directory traversal vulnerability in the Percha Downloads Attach (com_perchad...
2010年10月3日 17:46CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
2022年6月2日 11:28CVE-2021-39350: FV Flowplayer Video Player WordPress plugin – Authenticated Cross-Site Scripting
漏洞标题 CVE-2021-39350: FV Flowplayer Video Player WordPress plugin - Authenticated Cross-Site Scripting 漏洞描述 The FV Flowplayer Video Player WordPress plugin is vulnerable to ...
2021年1月31日 18:29CVE-2015-2067: Magento Server MAGMI – Directory Traversal
漏洞标题 CVE-2015-2067: Magento Server MAGMI - Directory Traversal 漏洞描述 Magento Server MAGMI (aka Magento Mass Importer) contains a directory traversal vulnerability in web/aja...
2015年9月4日 15:53
2026年10月22日 11:46
2026年10月21日 11:45
2026年10月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

