
最新发布第532页

CVE-2007-4556: OpenSymphony XWork/Apache Struts2 – Remote Code Execution S2-001
漏洞标题 CVE-2007-4556: OpenSymphony XWork/Apache Struts2 - Remote Code Execution S2-001 漏洞描述 Apache Struts support in OpenSymphony XWork before 1.2.3, and 2.x before 2.0.4, as...
 2007年11月1日 12:14
CVE-2022-29078: Node.js Embedded JavaScript 3.1.6 – Template Injection
漏洞标题 CVE-2022-29078: Node.js Embedded JavaScript 3.1.6 - Template Injection 漏洞描述 Node.js Embedded JavaScript 3.1.6 is susceptible to server-side template injection via sett...
2022年7月12日 05:22Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759)
漏洞标题 Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759) 漏洞描述 【漏洞描述】 Apache Tomcat JK(mod_jk) 【涉及版本】1.2.0,1.2.4 【漏洞描述】 由于Apache TomcatWeb服务器(...
2018年7月23日 09:02CVE-2023-4136: CrafterCMS Engine – Cross-Site Scripting
漏洞标题 CVE-2023-4136: CrafterCMS Engine - Cross-Site Scripting 漏洞描述 CrafterCMS Engine is vulnerable to reflected cross-site scripting (XSS) via the transformerName parameter ...
2023年6月19日 06:02CVE-2022-40879: kkFileView 4.1.0 – Cross-Site Scripting
漏洞标题 CVE-2022-40879: kkFileView 4.1.0 - Cross-Site Scripting 漏洞描述 kkFileView 4.1.0 contains multiple cross-site scripting vulnerabilities via the errorMsg parameter. An att...
2022年9月25日 00:18CVE-2022-3805: Jeg Elementor Kit < 2.5.7 - Unauthenticated Settings Update
漏洞标题 CVE-2022-3805: Jeg Elementor Kit < 2.5.7 - Unauthenticated Settings Update 漏洞描述 The Jeg Elementor Kit plugin for WordPress is vulnerable to authorization bypass in ...
2022年12月22日 12:26CVE-2020-5284: Next.js .next limited path traversal
漏洞标题 CVE-2020-5284: Next.js .next limited path traversal 漏洞描述 前端目录遍历浏览 fofa: "Next.js" PoC代码
2020年5月7日 08:05CVE-2022-2314: WordPress VR Calendar <=2.3.2 - Remote Code Execution
漏洞标题 CVE-2022-2314: WordPress VR Calendar <=2.3.2 - Remote Code Execution 漏洞描述 WordPress VR Calendar plugin through 2.3.2 is susceptible to remote code execution. The pl...
2022年4月4日 11:48CVE-2014-4536: Infusionsoft Gravity Forms Add-on < 1.5.7 - Cross-Site Scripting
漏洞标题 CVE-2014-4536: Infusionsoft Gravity Forms Add-on < 1.5.7 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in tests/notAuto_test_ContactServ...
2014年3月28日 02:34
响应美方要求,俄罗斯捣毁REvil网络犯罪组织
近日,俄罗斯联邦安全局FSB发布新闻稿称,在美国当局的呼吁下,俄罗斯联邦安全局与俄罗斯内务部合作,在莫斯科、圣彼得堡、列宁格勒和利佩茨克地区查明并捣毁了有组织犯罪团伙REvil。REvil是世...
2022年3月10日 23:34CVE-2020-9043: WordPress wpCentral <1.5.1 - Information Disclosure
漏洞标题 CVE-2020-9043: WordPress wpCentral <1.5.1 - Information Disclosure 漏洞描述 WordPress wpCentral plugin before 1.5.1 is susceptible to information disclosure. An attacke...
2020年9月9日 15:34CVE-2025-34143: ETQ Reliance – Authentication Bypass via Trailing Space
漏洞标题 CVE-2025-34143: ETQ Reliance - Authentication Bypass via Trailing Space 漏洞描述 An authentication bypass vulnerability exists in ETQ Reliance on the CG (legacy) platform....
2025年2月21日 16:17CVE-2012-5913: WordPress Integrator 1.32 – Cross-Site Scripting
漏洞标题 CVE-2012-5913: WordPress Integrator 1.32 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in wp-integrator.php in the WordPress Integrator module 1.32 ...
2012年10月24日 07:13CVE-2018-1000861: Jenkins – Remote Command Injection
漏洞标题 CVE-2018-1000861: Jenkins - Remote Command Injection 漏洞描述 Jenkins 2.153 and earlier and LTS 2.138.3 and earlier are susceptible to a remote command injection via stapl...
2018年1月17日 08:21(CVE-2025-48827) vBulletin未认证API方法调用漏洞
漏洞标题 (CVE-2025-48827) vBulletin未认证API方法调用漏洞 漏洞描述 (CVE-2025-48827) vBulletin未认证API方法调用漏洞 PoC代码 暂无
2025年11月4日 18:07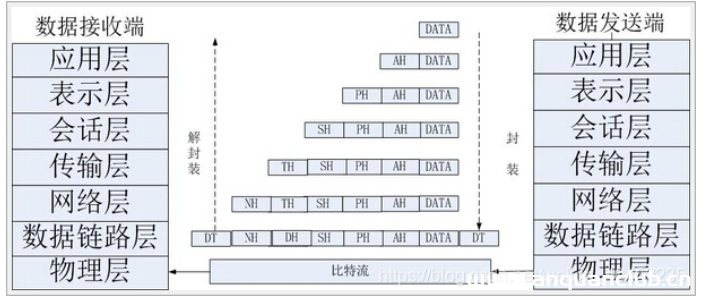
一文教你怎么搞定流量包(二)
前言 承接第一篇CTF流量分析,中间涉及部分知识内容,顺便自己再熟悉一遍,常规CTF或者说工控流量分析用到的工具wireshark之外似乎不怎涉及,,, 协议 TCP协议 TCP(Transmission Control Proto...
2022年3月10日 23:39
2026年9月24日 11:46
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

