
最新发布第533页
俄罗斯拟将苹果、微软等59家撤出俄罗斯的西方企业收归国有
据俄《消息报》,俄罗斯政府正在推进一项计划——将苹果等制裁俄罗斯的西方公司国有化。周四,该计划得到了俄罗斯总统弗拉基米尔·普京的支持,这意味着政府将可要求法院下令对因非商业原因撤出...
 2022年3月16日 09:15

CVE-2022-2314: WordPress VR Calendar <=2.3.2 - Remote Code Execution
漏洞标题 CVE-2022-2314: WordPress VR Calendar <=2.3.2 - Remote Code Execution 漏洞描述 WordPress VR Calendar plugin through 2.3.2 is susceptible to remote code execution. The pl...
2022年3月11日 17:08CVE-2022-41800: F5 BIG-IP Appliance Mode – Command Injection
漏洞标题 CVE-2022-41800: F5 BIG-IP Appliance Mode - Command Injection 漏洞描述 When running in Appliance mode, an authenticated user assigned the Administrator role may bypass Appl...
2022年3月11日 16:58
西湖论剑·第五届中国杭州网络安全技能大赛决赛正式启动
网络空间的竞争,归根结底是人才的竞争。3月11日,西湖论剑·第五届中国杭州网络安全技能大赛决赛在杭州拉开帷幕。作为首届全球数字贸易博览会的亮点单元,本次大赛由杭州市公安局、共青团杭州...
2022年3月16日 09:17CVE-2022-0867: WordPress ARPrice <3.6.1 - SQL Injection
漏洞标题 CVE-2022-0867: WordPress ARPrice <3.6.1 - SQL Injection 漏洞描述 WordPress ARPrice plugin prior to 3.6.1 contains a SQL injection vulnerability. It fails to properly sa...
2022年3月11日 16:11CVE-2022-2383: WordPress Feed Them Social <3.0.1 - Cross-Site Scripting
漏洞标题 CVE-2022-2383: WordPress Feed Them Social <3.0.1 - Cross-Site Scripting 漏洞描述 WordPress Feed Them Social plugin before 3.0.1 contains a reflected cross-site scriptin...
2022年3月11日 10:19CVE-2022-1119: WordPress Simple File List <3.2.8 - Local File Inclusion
漏洞标题 CVE-2022-1119: WordPress Simple File List <3.2.8 - Local File Inclusion 漏洞描述 WordPress Simple File List before 3.2.8 is vulnerable to local file inclusion via the e...
2022年3月11日 00:34
充分利用互联网资源的小tips-续集
挖掘src的时候找到一个资产如下 正常测试弱口令,未授权接口等无果 通过fofa搜索指纹,发现是一个通用的cms 把站点都薅下来,然后尝试弱口令,成功进入后台,顺便发现了一个这个后台的通用默认...
2022年3月10日 23:39
bugbounty技巧聚合20210907
漏洞报告 Google 谷歌漏洞三则 http://apapedulimu.click/story-of-idor-on-google-product/ 挖洞技巧 盲ssrf利用 http://blog.assetnote.io/2021/01/13/blind-ssrf-chains/#confluence 依赖混...
2022年3月10日 23:39bugbounty技巧聚合20210721
H1漏洞报告 Ruby OS Command Injection in '/lib/un.rb -- Utilities to replace common UNIX commands in Makefiles etc' Gitlab [stored XSS in custom emoji](tored XSS in custom emoji) St...
2022年3月10日 23:39bugbounty技巧聚合20211104
漏洞报告 【Flickr 500刀】critical server misconfiguration lead to access to any user sensitive data which include user email and password http://hackerone.com/reports/1365738 【Git...
2022年3月10日 23:39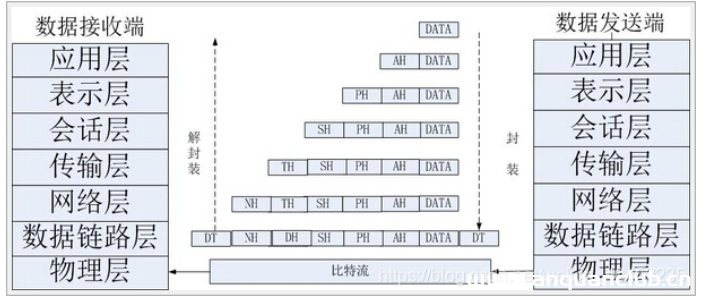
一文教你怎么搞定流量包(二)
前言 承接第一篇CTF流量分析,中间涉及部分知识内容,顺便自己再熟悉一遍,常规CTF或者说工控流量分析用到的工具wireshark之外似乎不怎涉及,,, 协议 TCP协议 TCP(Transmission Control Proto...
2022年3月10日 23:39bugbounty技巧聚合20210811
漏洞报告 HackerOne #1256371 PII data Leakage through hackerone reports #1145563 Tab nabbing in Hackerone inbox. Basecamp #1288898 Password reset link not expiring after changing pa...
2022年4月1日 18:36bugbounty技巧聚合20210901
Affirm [#1312365 Subdomain takeover due to non registered TLD ██████████.█████.██████.com ] #1213580 Open Redirect UPchieve #1166066 No Rate Limit On Reset Pas...
2022年4月1日 18:36bugbounty技巧聚合20211109
漏洞报告 【Shopify 500刀】Senseitive data Related to Shopify Host -> http://shopify.zendesk.com/ http://hackerone.com/reports/1298809 【Shopify 5000刀】Blog posts atom feed of a...
2022年3月10日 23:39每日云安全技术资讯20220228
使用开源的 Kubernetes 漏洞扫描和测试 http://www.conjur.org/blog/tutorial-kubernetes-vulnerability-scanning-testing-with-open-source/ 云原生——容器和应用安全运营实践思考 http://sec...
2022年3月10日 23:39
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

