
最新发布第539页

CVE-2024-21644: pyLoad Flask Config – Access Control
漏洞标题 CVE-2024-21644: pyLoad Flask Config - Access Control 漏洞描述 pyLoad is the free and open-source Download Manager written in pure Python. Any unauthenticated user can brow...
 2024年5月30日 09:54
CVE-2010-0944: Joomla! Component com_jcollection – Directory Traversal
漏洞标题 CVE-2010-0944: Joomla! Component com_jcollection - Directory Traversal 漏洞描述 A directory traversal vulnerability in the JCollection (com_jcollection) component for Joom...
2010年4月4日 18:54CVE-2020-17456: SEOWON INTECH SLC-130 & SLR-120S – Unauthenticated Remote Code Execution
漏洞标题 CVE-2020-17456: SEOWON INTECH SLC-130 & SLR-120S - Unauthenticated Remote Code Execution 漏洞描述 SEOWON INTECH SLC-130 and SLR-120S devices allow remote code executio...
2020年4月4日 09:52
奇安信 网康下一代防火墙 RCE 可直接getshell
网康下一代防火墙(NGFW)是一款可以全面应对应用层威胁的高性能防火墙。通过深入洞察网络流量中的用户、应用和内容,并借助全新的高性能单路径异构并行处理引擎,NGFW能够为用户提供有效的应用层...

 2023年2月5日 14:57
CVE-2017-12542: HPE Integrated Lights-out 4 (ILO4) <2.53 - Authentication Bypass
漏洞标题 CVE-2017-12542: HPE Integrated Lights-out 4 (ILO4) <2.53 - Authentication Bypass 漏洞描述 HPE Integrated Lights-out 4 (iLO 4) prior to 2.53 was found to contain an auth...
2017年9月21日 09:12CVE-2020-9480: Apache Spark – Authentication Bypass
漏洞标题 CVE-2020-9480: Apache Spark - Authentication Bypass 漏洞描述 In Apache Spark 2.4.5 and earlier, a standalone resource manager's master may be configured to require au...
2020年8月11日 04:55CVE-2023-38035: Ivanti Sentry – Authentication Bypass
漏洞标题 CVE-2023-38035: Ivanti Sentry - Authentication Bypass 漏洞描述 A security vulnerability in MICS Admin Portal in Ivanti MobileIron Sentry versions 9.18.0 and below, which m...
2023年5月5日 19:59CVE-2024-48248: NAKIVO Backup and Replication Solution – Unauthenticated Arbitrary File Read
漏洞标题 CVE-2024-48248: NAKIVO Backup and Replication Solution - Unauthenticated Arbitrary File Read 漏洞描述 NAKIVO Backup & Replication is a data protection solution used fo...
2024年2月28日 13:42Apache OFBiz webtools/control/xmlrpc 远程代码执行漏洞(CVE-2023-49070)
漏洞标题 Apache OFBiz webtools/control/xmlrpc 远程代码执行漏洞(CVE-2023-49070) 漏洞描述 Apache OFBiz是一个开源的企业资源规划(ERP)系统,提供了多种商业功能和模块。Apache OFBiz 在...
2023年6月8日 22:53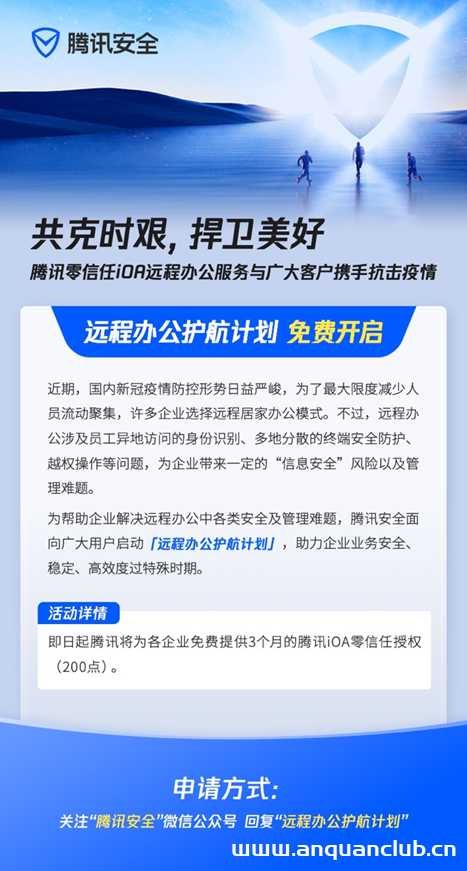
企业远程办公保障难?腾讯安全发布零信任免费计划
近期,国内新冠疫情防控形势日益严峻,为了最大限度减少人员流动聚集,许多企业选择远程居家办公模式。不过,远程办公涉及员工异地访问的身份识别、多地分散的终端安全防护、越权操作等问题,为...
2022年3月17日 08:06CVE-2022-21371: Oracle WebLogic Server Local File Inclusion
漏洞标题 CVE-2022-21371: Oracle WebLogic Server Local File Inclusion 漏洞描述 An easily exploitable local file inclusion vulnerability allows unauthenticated attackers with network...
2022年5月21日 02:59
VMware虚拟机17.5版更新发布 附永久激活KEY
免责声明 安全小天地所发布的文章及工具只限交流学习,安全小天地不承担任何责任!如有侵权,请告知我们立即删除。 新版特性 性能提升:我们对VM虚拟机的性能进行了全面优化,使其在处理大型应...
2023年10月23日 22:51CVE-2021-34621: WordPress ProfilePress 3.0.0-3.1.3 – Admin User Creation Weakness
漏洞标题 CVE-2021-34621: WordPress ProfilePress 3.0.0-3.1.3 - Admin User Creation Weakness 漏洞描述 ProfilePress WordPress plugin is susceptible to a vulnerability in the user regi...
2021年10月5日 13:25CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
2023年8月21日 10:28CVE-2014-9094: WordPress DZS-VideoGallery Plugin Cross-Site Scripting
漏洞标题 CVE-2014-9094: WordPress DZS-VideoGallery Plugin Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in deploy/designer/preview.php in the Digital ...
2014年5月28日 20:19CVE-2020-35713: Belkin Linksys RE6500 <1.0.012.001 - Remote Command Execution
漏洞标题 CVE-2020-35713: Belkin Linksys RE6500 <1.0.012.001 - Remote Command Execution 漏洞描述 Belkin LINKSYS RE6500 devices before 1.0.012.001 allow remote attackers to execut...
2020年8月6日 20:31
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

