
最新发布第553页

CVE-2018-20462: WordPress JSmol2WP <=1.07 - Cross-Site Scripting
漏洞标题 CVE-2018-20462: WordPress JSmol2WP <=1.07 - Cross-Site Scripting 漏洞描述 WordPress JSmol2WP version 1.07 and earlier is vulnerable to cross-site scripting and allows r...
 2018年12月26日 01:49
CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta – Arbitrary File Upload
漏洞标题 CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta - Arbitrary File Upload 漏洞描述 Unrestricted file upload vulnerability in includes/up...
2015年6月30日 16:56Adobe ColdFusion CVE-2023-38203不安全的反序列化漏洞
漏洞标题 Adobe ColdFusion CVE-2023-38203不安全的反序列化漏洞 漏洞描述 Adobe ColdFusion CVE-2023-38203不安全的反序列化漏洞 日期: 2024-02-07 | 影响软件: Adobe ColdFusion | PoC代码 暂...
2023年4月12日 01:13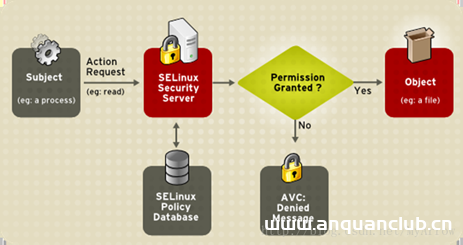
SELINUX工作原理详解_Linux
这篇文章主要介绍了SELINUX工作原理详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 1. 简介 SELinux带给Linux...
2024年6月3日 21:07
穿透静态检测:EDR对抗技术的分层实现
穿透静态检测:EDR对抗技术的分层实现作者:1571199704841171https://xz.aliyun.com/news/91978文章转载自 先知社区 穿透静态检测:EDR 对抗技术的分层拆解 本文仅用于安全研究与防御对抗学习。...

 2026年4月24日 16:49
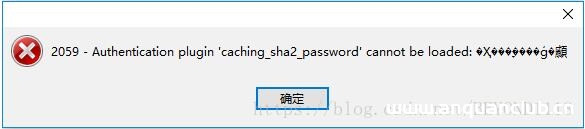
连接docker里面的mysql失败解决方法_docker
这篇文章主要介绍了连接docker里面的mysql失败解决方法,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 场景:在虚拟机的docker容器中安装latest版本的mysql之后,在宿主机...
2023年1月11日 21:06CVE-2022-0594: WordPress Shareaholic <9.7.6 - Information Disclosure
漏洞标题 CVE-2022-0594: WordPress Shareaholic <9.7.6 - Information Disclosure 漏洞描述 WordPress Shareaholic plugin prior to 9.7.6 is susceptible to information disclosure. The ...
2022年8月26日 19:44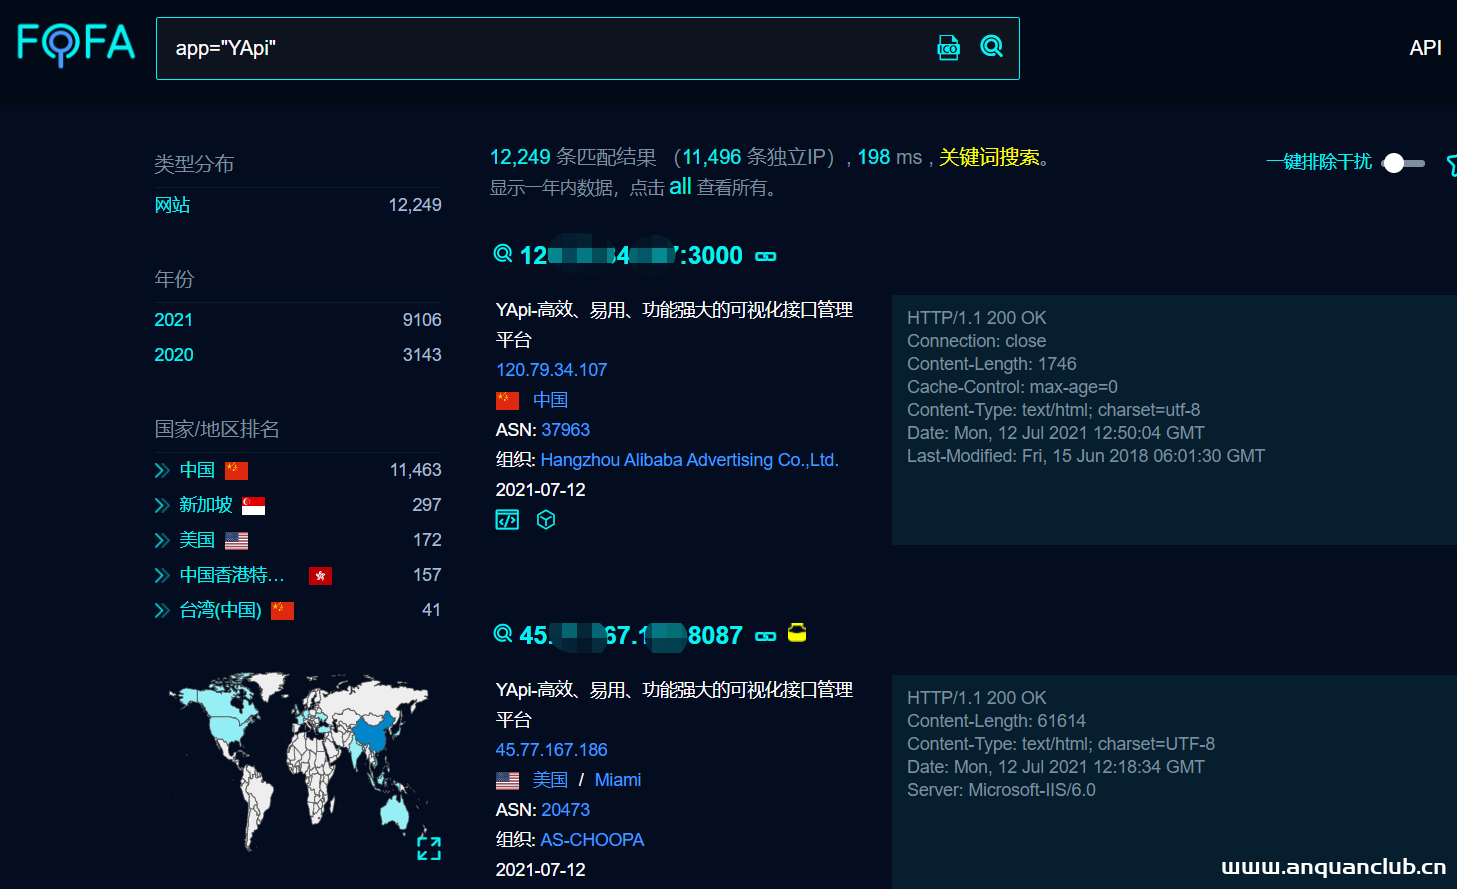
我是如何利用火器捡漏洞的
一、引子 当一个新漏洞被曝光后,如何才能快速在互联网上找到相关资产? 网络空间搜索引擎是一个不错的选择,例如FOFA、shodan等。 举个例子,这几天新爆了一个“Yapi认证用户利用Mock功能远程...
2022年3月10日 23:36ActiveMQ 消息代理系统 fileserver 文件上传漏洞(CVE-2016-3088)
漏洞标题 ActiveMQ 消息代理系统 fileserver 文件上传漏洞(CVE-2016-3088) 漏洞描述 Apache ActiveMQ® 是最流行的开源、多协议、基于 Java 的消息代理。Apache ActiveMQ 5.x 5.14.0 之前的文...
2016年1月10日 05:49CVE-2016-10033: WordPress PHPMailer < 5.2.18 - Remote Code Execution
漏洞标题 CVE-2016-10033: WordPress PHPMailer < 5.2.18 - Remote Code Execution 漏洞描述 WordPress PHPMailer before 5.2.18 might allow remote attackers to pass extra parameters to...
2016年4月25日 00:59CVE-2023-52251: Kafka UI 0.7.1 Command Injection
漏洞标题 CVE-2023-52251: Kafka UI 0.7.1 Command Injection 漏洞描述 An issue discovered in provectus kafka-ui 0.4.0 through 0.7.1 allows remote attackers to execute arbitrary code v...
2023年5月15日 07:17CVE-2021-44228: Apache Log4j2 Remote Code Injection
漏洞标题 CVE-2021-44228: Apache Log4j2 Remote Code Injection 漏洞描述 Apache Log4j2 <=2.14.1 JNDI features used in configuration, log messages, and parameters do not protect aga...
2021年9月19日 20:30CVE-2024-27954: WordPress Automatic Plugin <3.92.1 - Arbitrary File Download and SSRF
漏洞标题 CVE-2024-27954: WordPress Automatic Plugin <3.92.1 - Arbitrary File Download and SSRF 漏洞描述 WordPress Automatic plugin <3.92.1 is vulnerable to unauthenticated Ar...
2024年8月27日 22:18CVE-2018-16059: WirelessHART Fieldgate SWG70 3.0 – Local File Inclusion
漏洞标题 CVE-2018-16059: WirelessHART Fieldgate SWG70 3.0 - Local File Inclusion 漏洞描述 WirelessHART Fieldgate SWG70 3.0 is vulnerable to local file inclusion via the fcgi-bin/wg...
2018年6月3日 22:59
年仅16岁,攻击微软、三星、英伟达的幕后主使浮出水面
Lapsus$是一个近来异常活跃的黑客组织,主要事迹有窃取并泄露英伟达、三星、微软、Okta等科技巨头的源代码和专有数据,此外受害者还有游戏开发商育碧Ubisoft,电信公司Vodafone和电子商务巨头Me...
2022年3月27日 14:55CVE-2017-18529: PromoBar by BestWebSoft < 1.1.1 - Cross-Site Scripting
漏洞标题 CVE-2017-18529: PromoBar by BestWebSoft < 1.1.1 - Cross-Site Scripting 漏洞描述 The promobar plugin before 1.1.1 for WordPress has multiple XSS issues. PoC代码
2017年12月16日 00:33
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

