
最新发布第554页

CVE-2021-25075: WordPress Duplicate Page or Post <1.5.1 - Cross-Site Scripting
漏洞标题 CVE-2021-25075: WordPress Duplicate Page or Post <1.5.1 - Cross-Site Scripting 漏洞描述 WordPress Duplicate Page or Post plugin before 1.5.1 contains a stored cross-sit...
 2021年4月1日 11:54
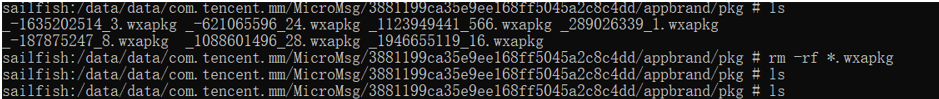
小程序反编译代码审计出奇迹
前言 数据加密或者是业务加签是我们在进行数据包重放或者是修改数据时,不得不遇到的痛点。总体来说对于数据解密或者业务加签破解的难度是:app>web>wxapp。因为api接口都是相同的,因此...
2022年3月10日 23:30CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected)
漏洞标题 CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected) 漏洞描述 The WordPress Qwizcards plugin before version 3.95 does not sanitise and escape th...
2025年8月14日 21:51Anyscale Ray CVE-2023-48022 远程代码执行漏洞
漏洞标题 Anyscale Ray CVE-2023-48022 远程代码执行漏洞 漏洞描述 Anyscale Ray 是一个开源的分布式计算框架,可以轻松扩展 AI 和 Python 工作。该框架中存在远程代码执行漏洞,此漏洞是程序对...
2023年7月19日 00:01CVE-2019-7275: Optergy Proton/Enterprise Building Management System – Open Redirect
漏洞标题 CVE-2019-7275: Optergy Proton/Enterprise Building Management System - Open Redirect 漏洞描述 Optergy Proton/Enterprise Building Management System contains an open redirect...
2019年7月19日 15:43CVE-2023-0968: WordPress Watu Quiz <3.3.9.1 - Cross-Site Scripting
漏洞标题 CVE-2023-0968: WordPress Watu Quiz <3.3.9.1 - Cross-Site Scripting 漏洞描述 WordPress Watu Quiz plugin before 3.3.9.1 is susceptible to cross-site scripting. The plugin...
2023年11月19日 14:34CVE-2024-24763: JumpServer < 3.10.0 - Open Redirect
漏洞标题 CVE-2024-24763: JumpServer < 3.10.0 - Open Redirect 漏洞描述 JumpServer is an open source bastion host and an operation and maintenance security audit system. Prior to ...
2024年9月10日 06:45CVE-2017-18496: Htaccess by BestWebSoft < 1.7.6 - Cross-Site Scripting
漏洞标题 CVE-2017-18496: Htaccess by BestWebSoft < 1.7.6 - Cross-Site Scripting 漏洞描述 The htaccess plugin before 1.7.6 for WordPress has multiple XSS issues. PoC代码
2017年7月9日 22:26CVE-2022-0228: Popup Builder < 4.0.7 - SQL Injection
漏洞标题 CVE-2022-0228: Popup Builder < 4.0.7 - SQL Injection 漏洞描述 The Popup Builder WordPress plugin before 4.0.7 does not validate and properly escape the orderby and orde...
2022年8月7日 00:21CVE-2025-55190: ArgoCD Project API Token Repository Credentials Exposure
漏洞标题 CVE-2025-55190: ArgoCD Project API Token Repository Credentials Exposure 漏洞描述 Argo CD API tokens with project-level permissions are able to retrieve sensitive reposito...
2025年5月13日 15:55CVE-2024-45309: OneDev.io < 11.0.9 - Arbitrary File Read
漏洞标题 CVE-2024-45309: OneDev.io < 11.0.9 - Arbitrary File Read 漏洞描述 Files on the host computer can be accessed by directory traversal. PoC代码
2024年10月20日 16:43CVE-2022-34048: Wavlink WN-533A8 – Cross-Site Scripting
漏洞标题 CVE-2022-34048: Wavlink WN-533A8 - Cross-Site Scripting 漏洞描述 Wavlink WN-533A8 M33A8.V5030.190716 contains a reflected cross-site scripting vulnerability via the login_...
2022年4月21日 10:54CVE-2025-5777: Citrix NetScaler Memory Disclosure – CitrixBleed 2
漏洞标题 CVE-2025-5777: Citrix NetScaler Memory Disclosure - CitrixBleed 2 漏洞描述 Insufficient input validation leading to memory overread on the NetScaler Management Interface N...
2025年2月12日 15:42CVE-2021-3654: Nova noVNC – Open Redirect
漏洞标题 CVE-2021-3654: Nova noVNC - Open Redirect 漏洞描述 Nova noVNC contains an open redirect vulnerability. An attacker can redirect a user to a malicious site and possibly obt...
2021年4月25日 06:18CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
2012年7月29日 11:11
简单的细节处越权漏洞
在挖(捡)src的过程中,遇到一个视频制作教学类的站点,尝试一波信息收集后没什么太大收获,就开始尝试对网站的功能处进行测试,用自己的账号登录后挨个查看网站内容的时候,发现一个模块无权...
2022年3月10日 23:32
2026年10月24日 11:45
2026年10月23日 11:45
2026年10月22日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

