
最新发布第558页

CVE-2021-27748: IBM WebSphere HCL Digital Experience – Server-Side Request Forgery
漏洞标题 CVE-2021-27748: IBM WebSphere HCL Digital Experience - Server-Side Request Forgery 漏洞描述 IBM WebSphere HCL Digital Experience is vulnerable to server-side request forge...
 2021年10月2日 11:06
CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
2022年6月12日 01:13CVE-2024-22729: Netis MW5360 V1.0.1.3031 – Command Injection
漏洞标题 CVE-2024-22729: Netis MW5360 V1.0.1.3031 - Command Injection 漏洞描述 NETIS SYSTEMS MW5360 V1.0.1.3031 was discovered to contain a command injection vulnerability via the ...
2024年6月24日 07:20CVE-2021-45046-DAST: Apache Log4j2 – Remote Code Injection
漏洞标题 CVE-2021-45046-DAST: Apache Log4j2 - Remote Code Injection 漏洞描述 Apache Log4j2 Thread Context Lookup Pattern is vulnerable to remote code execution in certain non-defau...
2021年4月30日 19:59CVE-2019-9874: Sitecore Experience Platform – Deserialization of Untrusted Data
漏洞标题 CVE-2019-9874: Sitecore Experience Platform - Deserialization of Untrusted Data 漏洞描述 Sitecore Experience Platform before 8.2 Update-7 and 9.0 before Update-2 is vulner...
2019年7月19日 14:18CVE-2020-2103: Jenkins <=2.218 - Information Disclosure
漏洞标题 CVE-2020-2103: Jenkins <=2.218 - Information Disclosure 漏洞描述 Jenkins through 2.218, LTS 2.204.1 and earlier, is susceptible to information disclosure. An attacker c...
2020年4月9日 03:41CVE-2024-9474: PAN-OS Management Web Interface – Command Injection
漏洞标题 CVE-2024-9474: PAN-OS Management Web Interface - Command Injection 漏洞描述 A privilege escalation vulnerability in Palo Alto Networks PAN-OS software allows a PAN-OS admi...
2024年3月13日 10:22CVE-2019-17232: WordPress Ultimate FAQs <= 1.8.24 – Unauthenticated Options Import and Export
漏洞标题 CVE-2019-17232: WordPress Ultimate FAQs <= 1.8.24 – Unauthenticated Options Import and Export 漏洞描述 Functions/EWD_UFAQ_Import.php in the ultimate-faqs plugin throug...
2019年9月10日 07:45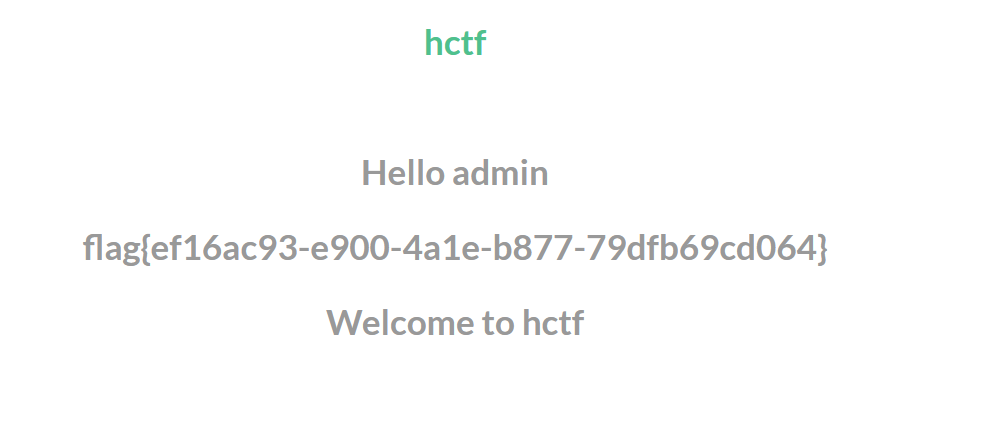
[HCTF 2018]admin – buu刷题笔记
首先爬一遍整个网站,发现有没注册的时候有“login”,'register', 这两个页面,注册一个123用户登录后发现有 'index“,”post“,”logout“,”change password“这四个界面, 根据题目提示的a...

 2022年4月17日 16:53
CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection
漏洞标题 CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection 漏洞描述 Improper Neutralization of Special Elements used in an SQL Command ('SQL Injecti...
2024年6月13日 22:14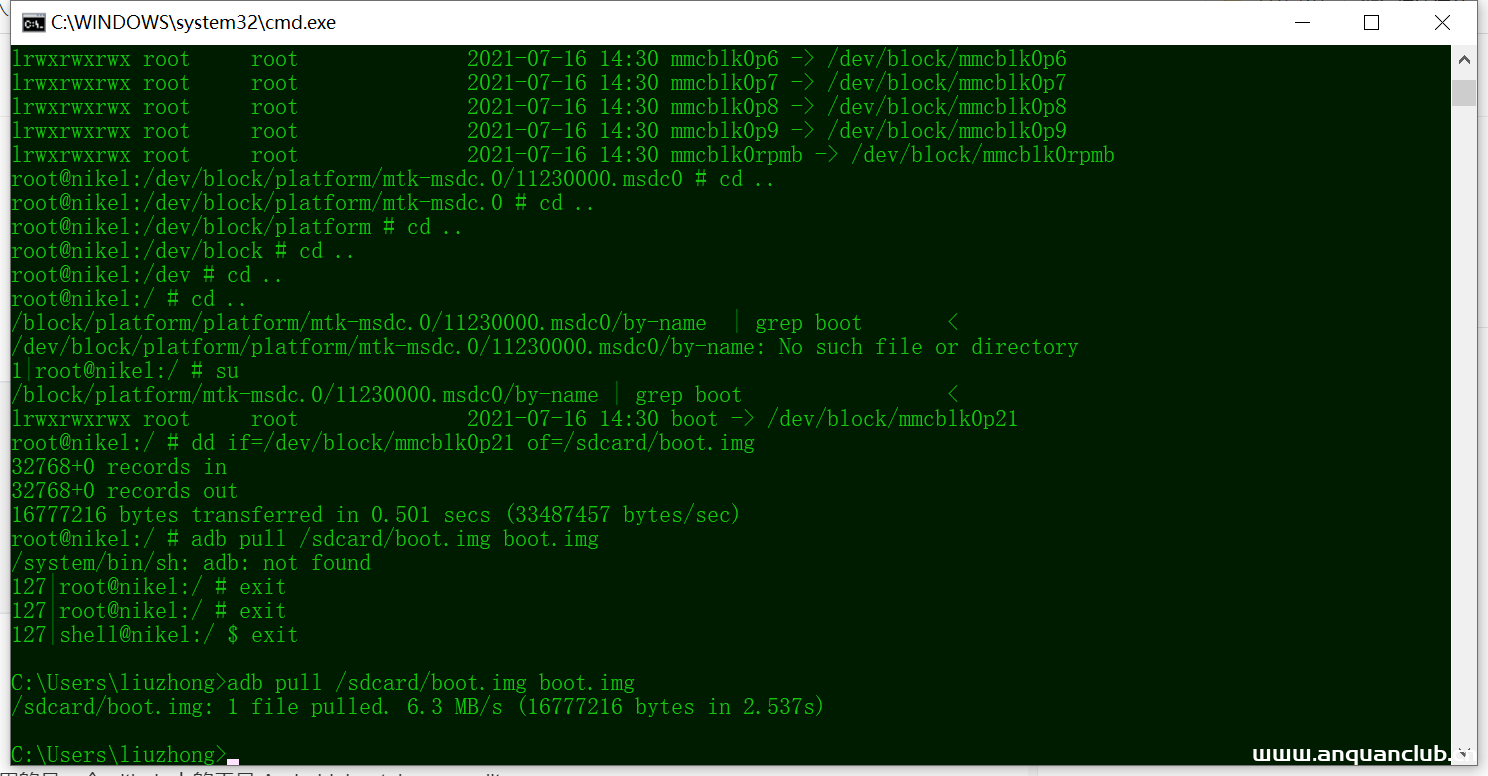
安卓系统修改系统内核绕过TracerPid检测–反防调试
背景: 得到一个Android的CrackMe来考察逆向知识,分析后发现其关键函数位于native so库中,并且在函数开始时启动了线程进行TracerPid检测的反调试,当发现程序被调试时会直接杀死应用。虽然题...
2022年3月10日 23:34CVE-2024-34257: TOTOLINK EX1800T TOTOLINK EX1800T – Command Injection
漏洞标题 CVE-2024-34257: TOTOLINK EX1800T TOTOLINK EX1800T - Command Injection 漏洞描述 TOTOLINK EX1800T V9.1.0cu.2112_B20220316 has a vulnerability in the apcliEncrypType paramete...
2024年2月12日 23:09CVE-2022-34093: Software Publico Brasileiro i3geo v7.0.5 – Cross-Site Scripting
漏洞标题 CVE-2022-34093: Software Publico Brasileiro i3geo v7.0.5 - Cross-Site Scripting 漏洞描述 Portal do Software Publico Brasileiro i3geo v7.0.5 was discovered to contain a cro...
2022年10月16日 10:37CVE-2017-9791: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-9791: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.1.x and 2.3.x with the Struts 1 plugin might allow remote code execution via a malici...
2017年2月17日 01:08CVE-2020-1943: Apache OFBiz <=16.11.07 - Cross-Site Scripting
漏洞标题 CVE-2020-1943: Apache OFBiz <=16.11.07 - Cross-Site Scripting 漏洞描述 Apache OFBiz 16.11.01 to 16.11.07 is vulnerable to cross-site scripting because data sent with co...
2020年1月5日 11:05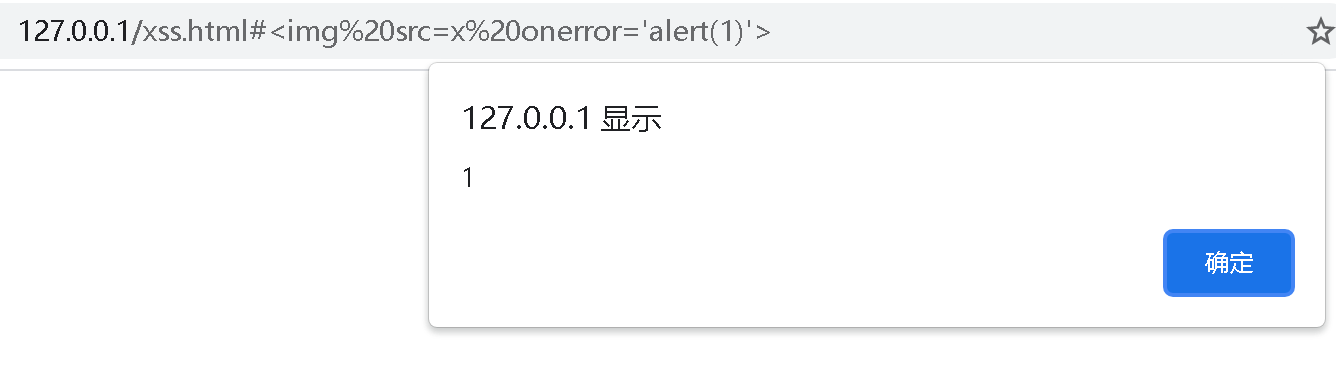
web漏洞挖掘指南 -XSS跨站脚本攻击
web漏洞挖掘指南 XSS跨站脚本攻击 一、漏洞原理 1. 跨站脚本英文全称(Cross Site Scripting跨站脚本),为了不和css层叠样式表(英文全称:Cascading Style Sheets)混淆,因此将跨站脚本缩写为X...
2022年3月10日 23:35
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

